
 #1
Security papers, research projects, technical references, and reproducible material for defensive or authorized analysis.
Kitploit 추천

 googlesky/cve-2026-118383
Proof-of-concept for CVE-2026-118383, an unauthenticated MongoDB use-after-free in replication catch-up, with wire-protocol exploit scripts, a gdb…
 project-oak/oak
분산 시스템에서 데이터에 대한 의미 있는 제어.
 irsdl/webhacklist
Independent web hacking research archive: official Top 10 nominees and winners since 2006, plus additional discoveries, preserved articles and…
 cveproject/cvelistv5
공식 CVE 목록의 CVE JSON 5 형식 캐시
 circl/ail-framework
AIL 프레임워크 - 분석 정보 유출 프레임워크. 프로젝트가 https://github.com/ail-project 로 이동되었습니다.
 tamarin-prover/tamarin-prover
다중집합 재작성과 제약 해결을 사용하여 비밀성, 인증 및 동등성 속성을 증명하는 보안 프로토콜용 기호 검증 도구입니다.
 yosyshq/nextpnr
nextpnr 휴대용 FPGA 배치 및 배선 도구
 asgeirtj/system_prompts_leaks
Curated collection of extracted system prompts from major AI chatbots including Claude, ChatGPT, Gemini, Grok, and Copilot. Updated regularly with…
 nomi-sec/poc-in-github
📡 PoC auto collect from GitHub. ⚠️ Be careful Malware.
 rubysec/ruby-advisory-db
커뮤니티에서 유지 관리하는 Ruby 젬 및 런타임용 보안 권고 데이터베이스로, 패치된 버전이 포함된 구조화된 CVE/GHSA 데이터를 제공하여 취약점 추적 및 감사 통합을 지원합니다.
 z3prover/z3
자동 정리 증명, 제약 조건 해결 및 프로그램 검증을 위한 고성능 SMT 해결사. 형식적 분석을 위한 여러 이론 및 언어 바인딩을 지원합니다.
 ut-dacs/anycast-census
Longitudinal anycast census system that probes IPv4/IPv6 prefixes via ICMP, TCP, and DNS to detect anycast deployments and geolocate PoPs, publishing…
 securewithumer/exploit-index
Zero-API aggregator indexing 150k+ CVE exploits and PoCs from Exploit-DB, Nuclei, Metasploit, and CISA KEV, with EPSS/CVSS risk scoring for threat…
 securewithumer/cve-2026-pocs
Exploit-Index : The Ultimate CVE Proof of Concept (PoC) & Exploit Database. A zero-API, high-performance aggregator for 0days, vulnerabilities, and…
 huhusmang/awesome-llms-for-vulnerability-detection
커뮤니티에서 가장 포괄적이고 지속적으로 업데이트되는 대규모 언어 모델(LLM) 기반 소프트웨어 취약점 탐지 연구 인덱스 — 함수 수준, 저장소 수준, 에이전트 기반, 스마트 계약 탐지에 이르는 논문과 데이터셋, 벤치마크, 설문 조사를 포함합니다.
 b2r2-org/b2r2
B2R2 is a fully managed binary analysis framework written in F#. It provides a rich set of algorithms, functions, and tools for reverse engineering,…
 tencent/ai-infra-guard
Agent Scan, Skills Scan, MCP 스캔, AI 인프라 스캔 및 LLM 탈옥(jailbreak) 평가를 통해 AI 생태계를 보호하는 풀스택 AI 레드팀 플랫폼
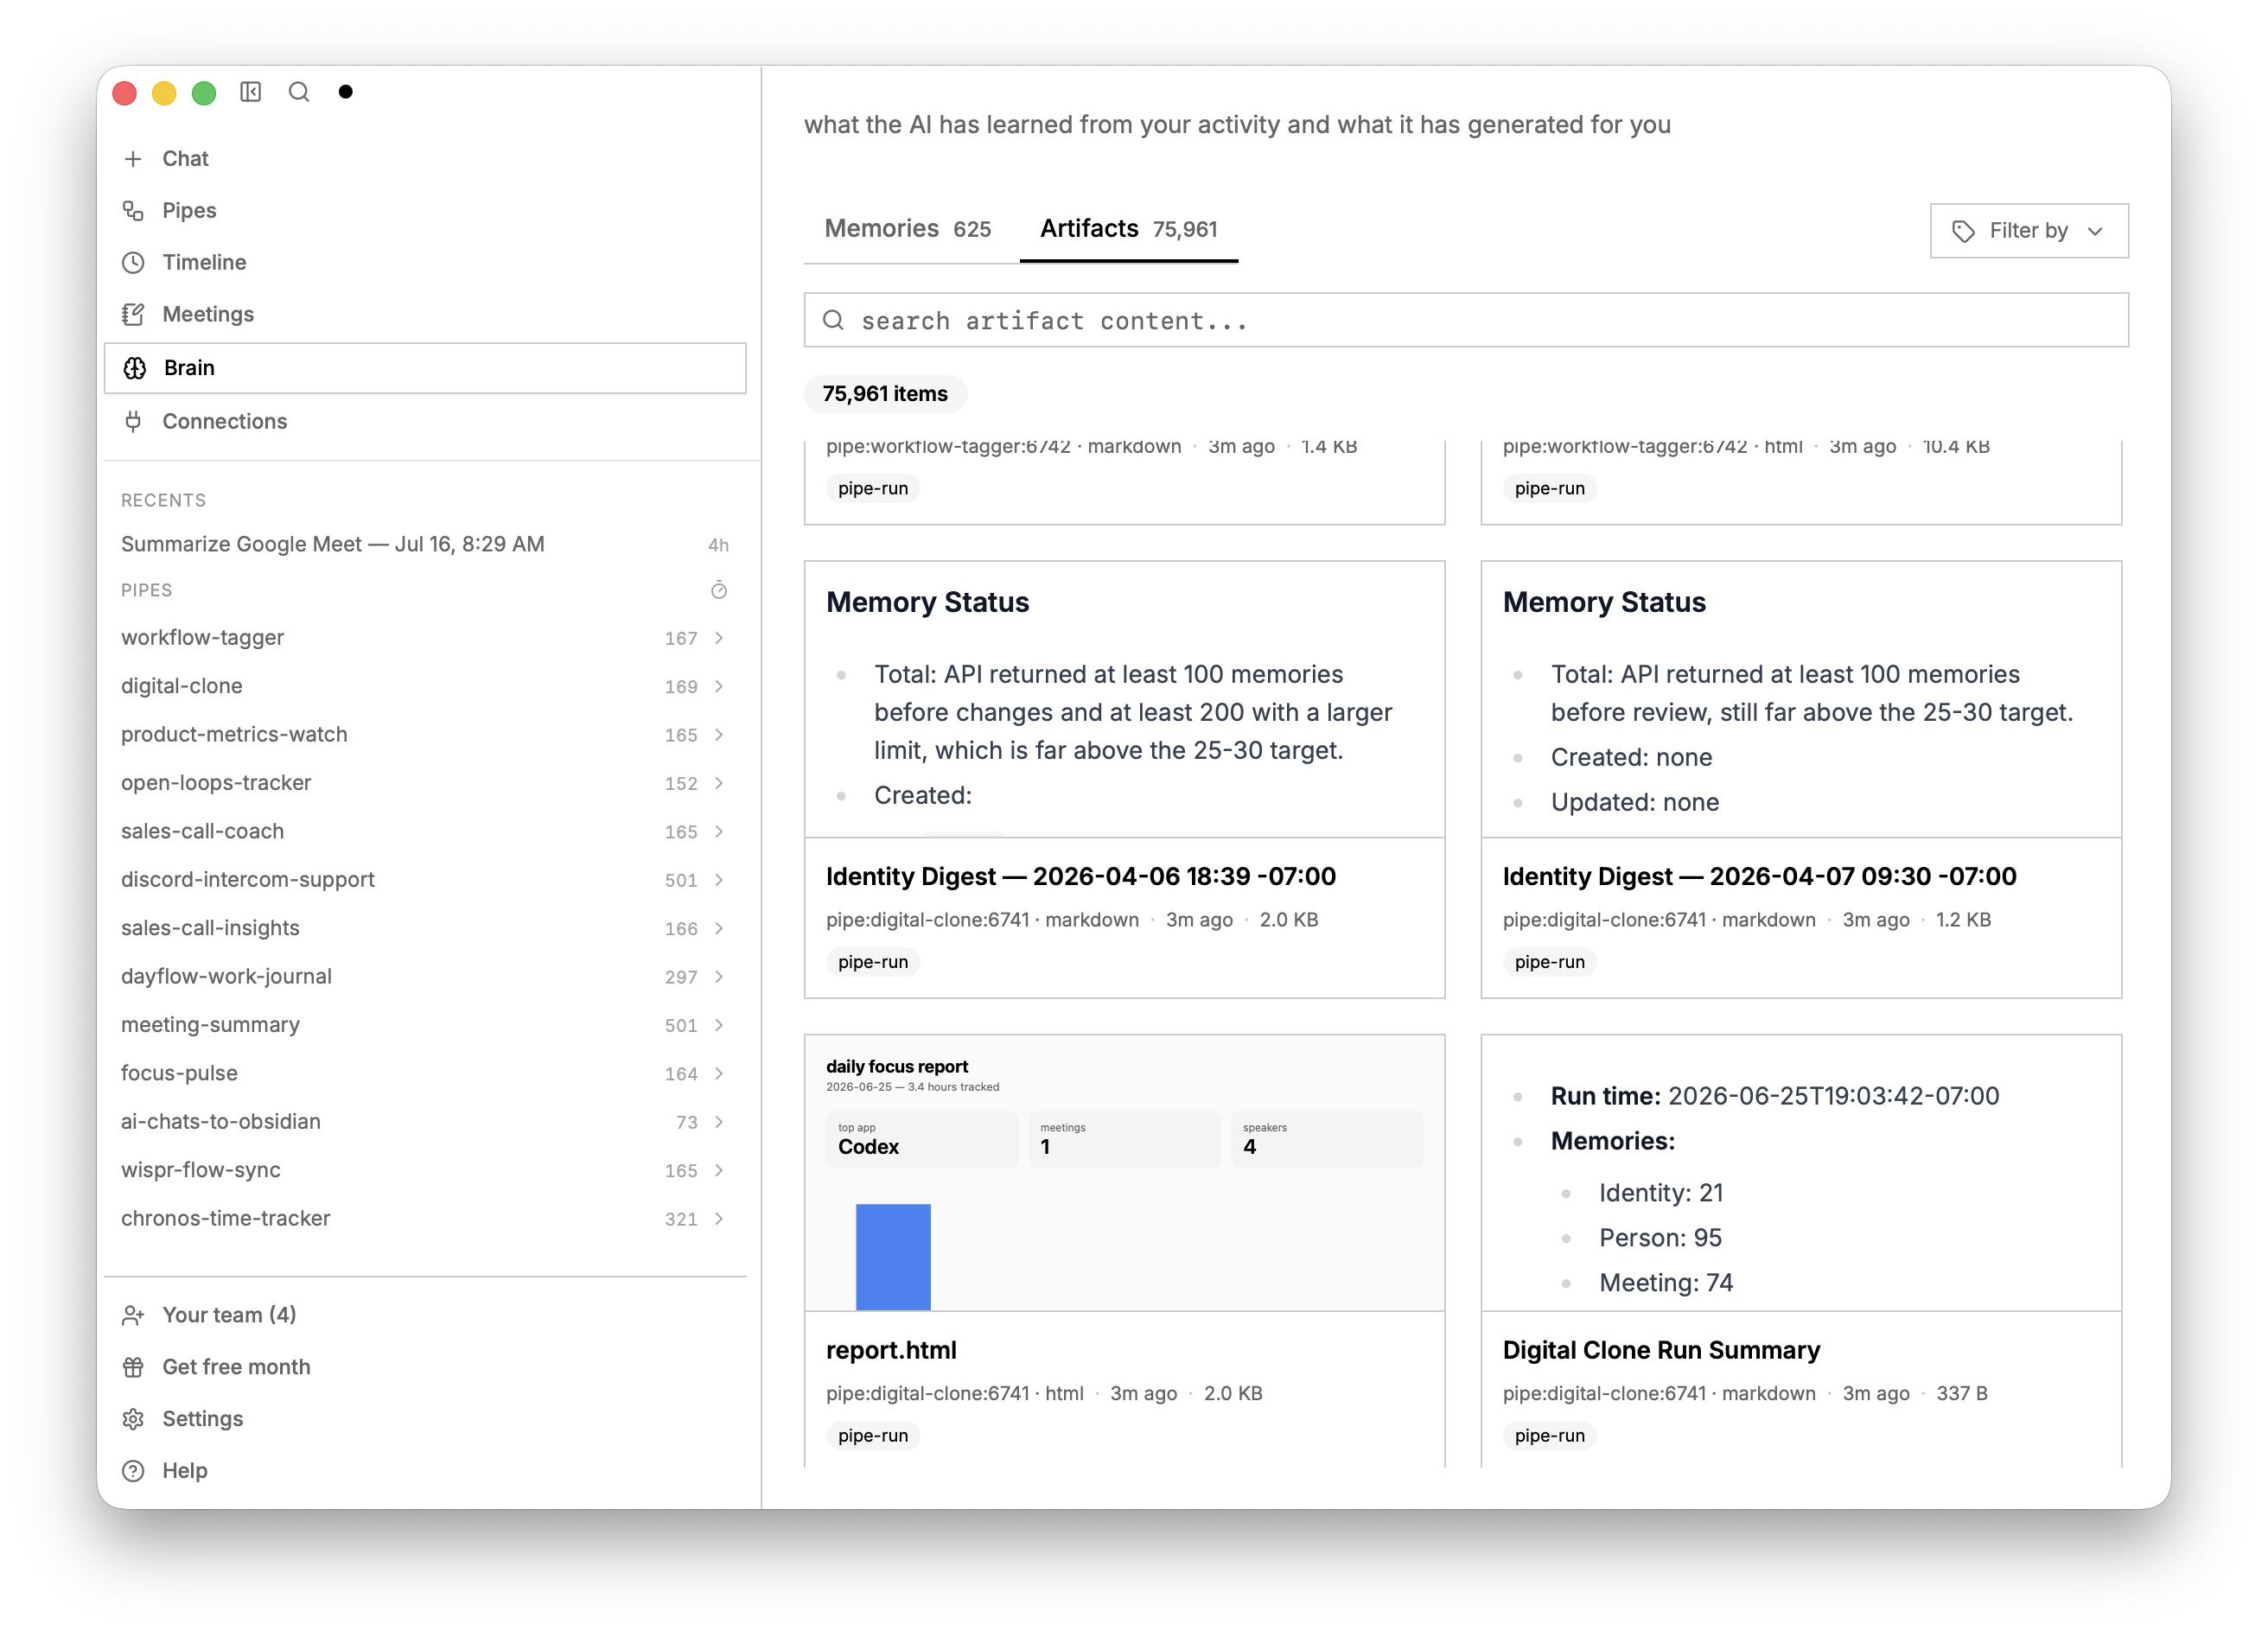 screenpipe/screenpipe
로컬 우선 방식의 연속 화면 및 오디오 레코더로, AI 기반 검색, 전사, 자동화 기능을 제공합니다. 사용자가 보고, 말하고, 하는 모든 것을 캡처한 뒤 플러그인과 MCP 서버를 통해 검색 가능하고 실행 가능하게 만듭니다.








