
Skip to content
KitploitKITPLOIT
도구익스플로잇블로그
Log in
제출
도구익스플로잇블로그
제출

해킹, 침투 테스트 및 사이버 보안 도구를 당신의 보안 무기고에!

Kitploit은 해킹, 사이버 보안 및 침투 테스트 도구 디렉토리입니다. 최신 프로젝트 업데이트를 발견하여 취약점을 찾고, 시스템을 분석하고, 테스트를 자동화하고, 보안을 강화하세요.

피드문의개인정보© 2026 Kitploit

도구 디렉토리

카테고리

모든 카테고리 보기
Loading categories
카테고리

Papers & Research

Security papers, research projects, technical references, and reproducible material for defensive or authorized analysis.

Kitploit 추천

추천 도구

10 선택됨
security-research preview#1

security-research

GitHubgoogle/security-research
4.6k3일 전
0days-in-the-wild preview#2

0days-in-the-wild

GitHubgoogleprojectzero/0days-in-the-wild
1.0k3개월 전
MSRC-Security-Research preview#3

MSRC-Security-Research

GitHubmicrosoft/msrc-security-research
1.4k2년 전
publications preview#4

publications

GitHubtrailofbits/publications
1.9k7일 전
papers-we-love preview#5

papers-we-love

GitHubpapers-we-love/papers-we-love
111.7k23일 전
criticality_score preview#6

criticality_score

GitHubossf/criticality_score
1.5k2개월 전
attack-stix-data preview#7

attack-stix-data

GitHubmitre-attack/attack-stix-data
72515일 전
Security-101 preview#8

Security-101

GitHubmicrosoft/security-101
6.8k2개월 전
h4cker preview#9

h4cker

GitHubthe-art-of-hacking/h4cker
28.9k3일 전
offensive-ai-compilation preview#10

offensive-ai-compilation

GitHubjiep/offensive-ai-compilation
1.4k19일 전
최신관련성인기최근 업데이트
2354 결과
quantum-security-project preview

quantum-security-project

GitHubowasp/quantum-security-project

벤더 중립적인 OWASP 프로젝트로, 양자 시대의 보안 위험을 매핑하여 Top 10 위험 목록, 완화 지침, 포스트퀀텀 암호화 마이그레이션 및 양자 플랫폼 보안을 위한 위협 모델을 제공합니다.

threat-feeds-aggregatorsvulnerability-analysiscryptography+8
582개월 전
SBOM-VEX-Taint-Analysis preview

SBOM-VEX-Taint-Analysis

GitHubowasp/sbom-vex-taint-analysis

Automated SBOM-to-VEX pipeline using a secure multi-agent AI system to analyze CVEs, reason about exploitability, and generate signed CycloneDX VEX…
vulnerability-analysissupply-chain-securitypapers-research+3
24일 전
CVE-2024-22641 preview

CVE-2024-22641

GitHubzunak/cve-2024-22641

CVE-2024-22641에 대한 개념 증명: TCPDF <=6.7.4에서 조작된 SVG 파일에 의해 트리거되는 ReDoS 취약점으로, 정규 표현식 역추적 한도 소진을 시연합니다.

vulnerability-analysisexploitationweb-security+3
12년 전
CVE-2024-21532-PoC-ggit preview

CVE-2024-21532-PoC-ggit

GitHublirantal/cve-2024-21532-poc-ggit

CVE-2024-21532에 대한 개념 증명 익스플로잇으로, ggit npm 패키지의 fetchTags API에 존재하는 명령 주입 취약점을 통해 안전하지 않은 exec() 사용을 입증합니다.

vulnerability-analysisexploitationweb-application-exploitation+2
5개월 전
CVE-2026-63030-Wp2Shell preview

CVE-2026-63030-Wp2Shell

GitHubghostinexile/cve-2026-63030-wp2shell

워드프레스 REST API SQLi to RCE PoC (CVE-2026-63030 및 CVE-2026-60137)
vulnerability-scannerscode-analysisexploitation+3
44개월 전
CVE-2024-10930 preview

CVE-2024-10930

GitHubsahil3276/cve-2024-10930

CVE-2024-10930 공개
privilege-escalationvulnerability-analysisexploitation+3
1년 전
cve-2024-1086-writeup preview

cve-2024-1086-writeup

GitHubluisbuilds-data/cve-2024-1086-writeup

CVE-2024-1086에 대한 근본 원인 분석 및 개념 증명 익스플로잇, 힙 스프레이를 통해 임의 메모리 쓰기를 위한 Linux 커널 netfilter 이중 해제 취약점.

vulnerability-analysisexploitationpapers-research+2
5개월 전
CVE-2024-1086 preview

CVE-2024-1086

GitHubnotselwyn/cve-2024-1086

CVE-2024-1086에 대한 범용 로컬 권한 상승 PoC 익스플로잇으로, Debian, Ubuntu, KernelCTF를 포함한 v5.14~v6.6 사이의 대부분의 Linux 커널에서 작동합니다. KernelCTF 이미지에서 성공률은 99.4%입니다.
privilege-escalationvulnerability-analysisexploitation+4
2.5k2년 전
cve-2024-0519-rca-research preview

cve-2024-0519-rca-research

GitHubinsaida/cve-2024-0519-rca-research

CVE-2024-0519 근본 원인 분석
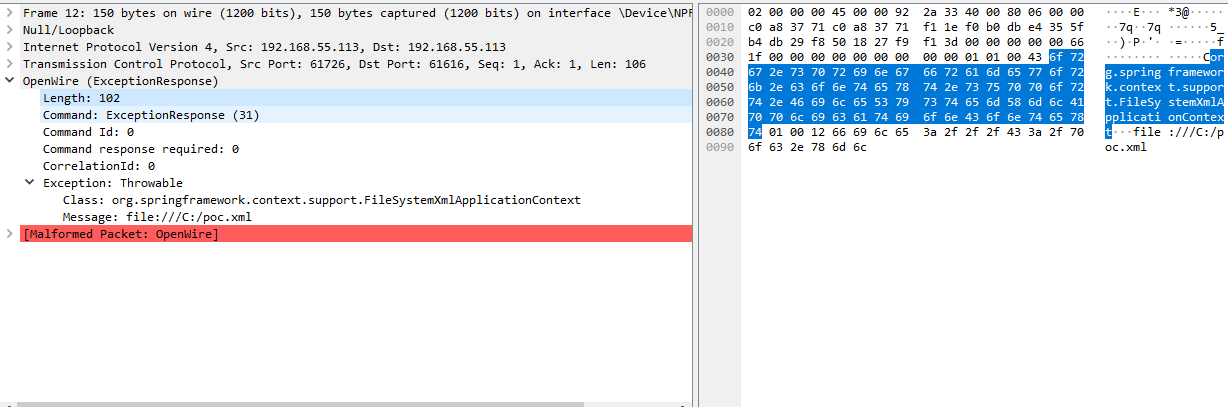
vulnerability-analysisexploitationpapers-research+2
6개월 전
CVE-2023-46604 preview

CVE-2023-46604

GitHubskrkcb2/cve-2023-46604

CVE-2023-46604에 대한 심층 기술 분석, Apache ActiveMQ의 OpenWire 프로토콜에 존재하는 RCE 취약점으로, 패킷 구조 분석 및 익스플로잇 메커니즘을 포함합니다.

vulnerability-analysisexploitationpapers-research+2
11년 전
CVE-2023-49964 preview

CVE-2023-49964

GitHubmbadanoiu/cve-2023-49964

CVE-2023-49964: Alfresco의 FreeMarker 서버 사이드 템플릿 인젝션

vulnerability-analysisexploitationweb-application-exploitation+3
72년 전
CVE-2023-46442_POC preview

CVE-2023-46442_POC

GitHubjacklosingheart/cve-2023-46442_poc

Soot에서 발견된 CVE-2023-46442 서비스 거부 취약점의 PoC

vulnerability-analysisexploitationbinary-analysis+2
1년 전
CVE-2023-46404 preview

CVE-2023-46404

GitHubwindecks/cve-2023-46404

CVE-2023-46404에 대한 PoC 및 Writeup.
vulnerability-analysiscode-analysisexploitation+3
33년 전
physical-bitcoin-attacks preview

physical-bitcoin-attacks

GitHubjlopp/physical-bitcoin-attacks

비트코인 / 암호화폐 자산 보유 주체에 대한 현실 공간에서 발생한 알려진 공격 목록

osintcryptographythreat-intelligence+3
8895일 전
Detection-Rules preview

Detection-Rules

GitHubmanishrawat21/detection-rules

이 저장소는 APT29 시뮬레이션 중 관찰된 적대자 행동에 대한 검증된 탐지 규칙을 포함합니다. 각 규칙은 실제 공격 데이터로 테스트되었으며, Splunk SPL로 변환되었고, 오탐(false positive)에 대해 검증되었습니다.

vulnerability-analysisintrusion-detectionpapers-research+4
42개월 전
CVE-2025-70994 preview

CVE-2025-70994

GitHubktauchathuranga/cve-2025-70994

수동 RF 신호 분석기 for EV1527 고정 코드 프로토콜, Yadea T5 무선 키리스 엔트리 시스템에서 CVE-2025-70994 재전송 취약점을 시연합니다. ESP8266/CC1101용 PoC 코드 포함.

embedded-systems-securityvulnerability-analysisexploitation+5
16개월 전
CVE-2021-3156 preview

CVE-2021-3156

GitHubph4ntonn/cve-2021-3156

CVE-2021-3156

privilege-escalationvulnerability-analysisexploitation+3
35년 전
CVE-2023-38831-WinRAR-Vulnerability-Analysis preview

CVE-2023-38831-WinRAR-Vulnerability-Analysis

GitHubolowostandard1/cve-2023-38831-winrar-vulnerability-analysis

이 프로젝트는 특수하게 제작된 아카이브 파일을 통해 공격자가 악성 코드를 실행할 수 있게 하는 WinRAR의 심각한 취약점인 CVE-2023-38831에 초점을 맞춘 사이버 보안 연구 및 분석 프로젝트입니다. 이 프로젝트는 교육 및 방어적 보안 목적으로만 통제된…


vulnerability-analysisexploitationmalware-analysis+3
16개월 전
이전1…868788…100다음








