
 #1
Tools for blue team, defensive security, and threat protection.
Kitploit 추천

 9pings/fad-checker
Buildless dependency auditor that scans 10 ecosystems offline, reporting CVEs prioritized by CISA KEV and EPSS, EOL packages, licenses, committed…
 g4bri-3l3/idwolf
Read-only Active Directory & Microsoft Entra ID hygiene auditor in pure PowerShell. Collect once, analyze offline: deterministic findings, attack…
 azure/azure-sentinel
클라우드 네이티브 SIEM으로, 전체 엔터프라이즈를 위한 지능형 보안 분석 기능을 제공합니다.
 beenuar/aisoc
Self-hostable AI SOC that fuses security alerts, auto-triages via agentic AI, runs MITRE ATT&CK investigations, and logs every agent decision in a…
 anthropics/oss-scanner
등록된 오픈소스 저장소를 격리된 오프라인 VM에서 빌드하고 보안 취약점을 스캔하여 재현기와 제안된 패치와 함께 결과를 이메일로 전송하는 서비스입니다.
 bekkaze/abusebox
Self-hosted mail server monitoring: checks 24 DNS blacklists, AbuseIPDB reputation, SSL and domain expiry, SPF/DKIM/DMARC grades and uptime, with…
 shuffle/shuffle
Open-source security orchestration, automation, and response (SOAR) platform with a visual workflow editor, prebuilt security app integrations, and…
 mc493/linux-kernel-zero-day-mitigation-zero-downtime-kernel-defense-
Linux 커널 제로데이 무중단 방어 사례 연구. 자동화된 CLI 및 이중 증인 공증 프레임워크는 mc493/kshield를 참조하십시오.
 agentrust-io/cmcp
cMCP: 기밀 MCP 게이트웨이. MCP 도구 호출에 대한 하드웨어 증명 기반 정책 적용.
 hotcakex/harden-windows-security
# Windows 보안 강화 도구 공식적으로 지원되는 Microsoft 방법과 적절한 설명을 사용하여 Windows를 안전하고 보안적으로 강화합니다 | 항상 최신 상태를 유지하며 최신 Windows 빌드와 호환됩니다 | 개인, 기업, 정부 및 군사 보안 수준을 위한…
 matijamiki/ranwhat
Audit log and secret scanner for AI coding agents: see what Claude Code, Codex, Gemini CLI and 27 more ran on your machine, and find API keys leaked…
 xalgorix/xalgorix
Open-source AI penetration testing agent that exploit-verifies every finding. Autonomous 22-phase pentests of web apps & APIs with CVSS-scored PDF…

 daveyd347/secrets-scanner
소스 코드와 git 이력에서 유출된 API 키, 토큰, 개인 키를 탐지하는 의존성 없는 시크릿 스캐너로, 마스킹된 출력과 바로 사용 가능한 GitLab CI 작업을 제공합니다.
 qubesos/qubes-core-admin
Python 관리 API를 통해 Qubes OS 도메인의 핵심 수명 주기를 관리하며, Xen을 사용한 안전한 컴파트먼트화를 처리하고 자동화를 위한 이벤트 시스템을 제공합니다.
 cisagov/kev-data
CISA의 알려진 악용 취약점(KEV) 카탈로그를 JSON 스키마와 함께 CSV 및 JSON으로 미러링하여 KEV 업데이트에 대한 프로그래밍 방식 접근과 커밋 기록 추적을 가능하게 합니다.
 nzymeorg/nzyme
WiFi, Bluetooth 및 이더넷 위협 탐지.
 lolbas-project/lolbas
기본 제공 바이너리 및 스크립트 활용 - (LOLBins and LOLScripts)
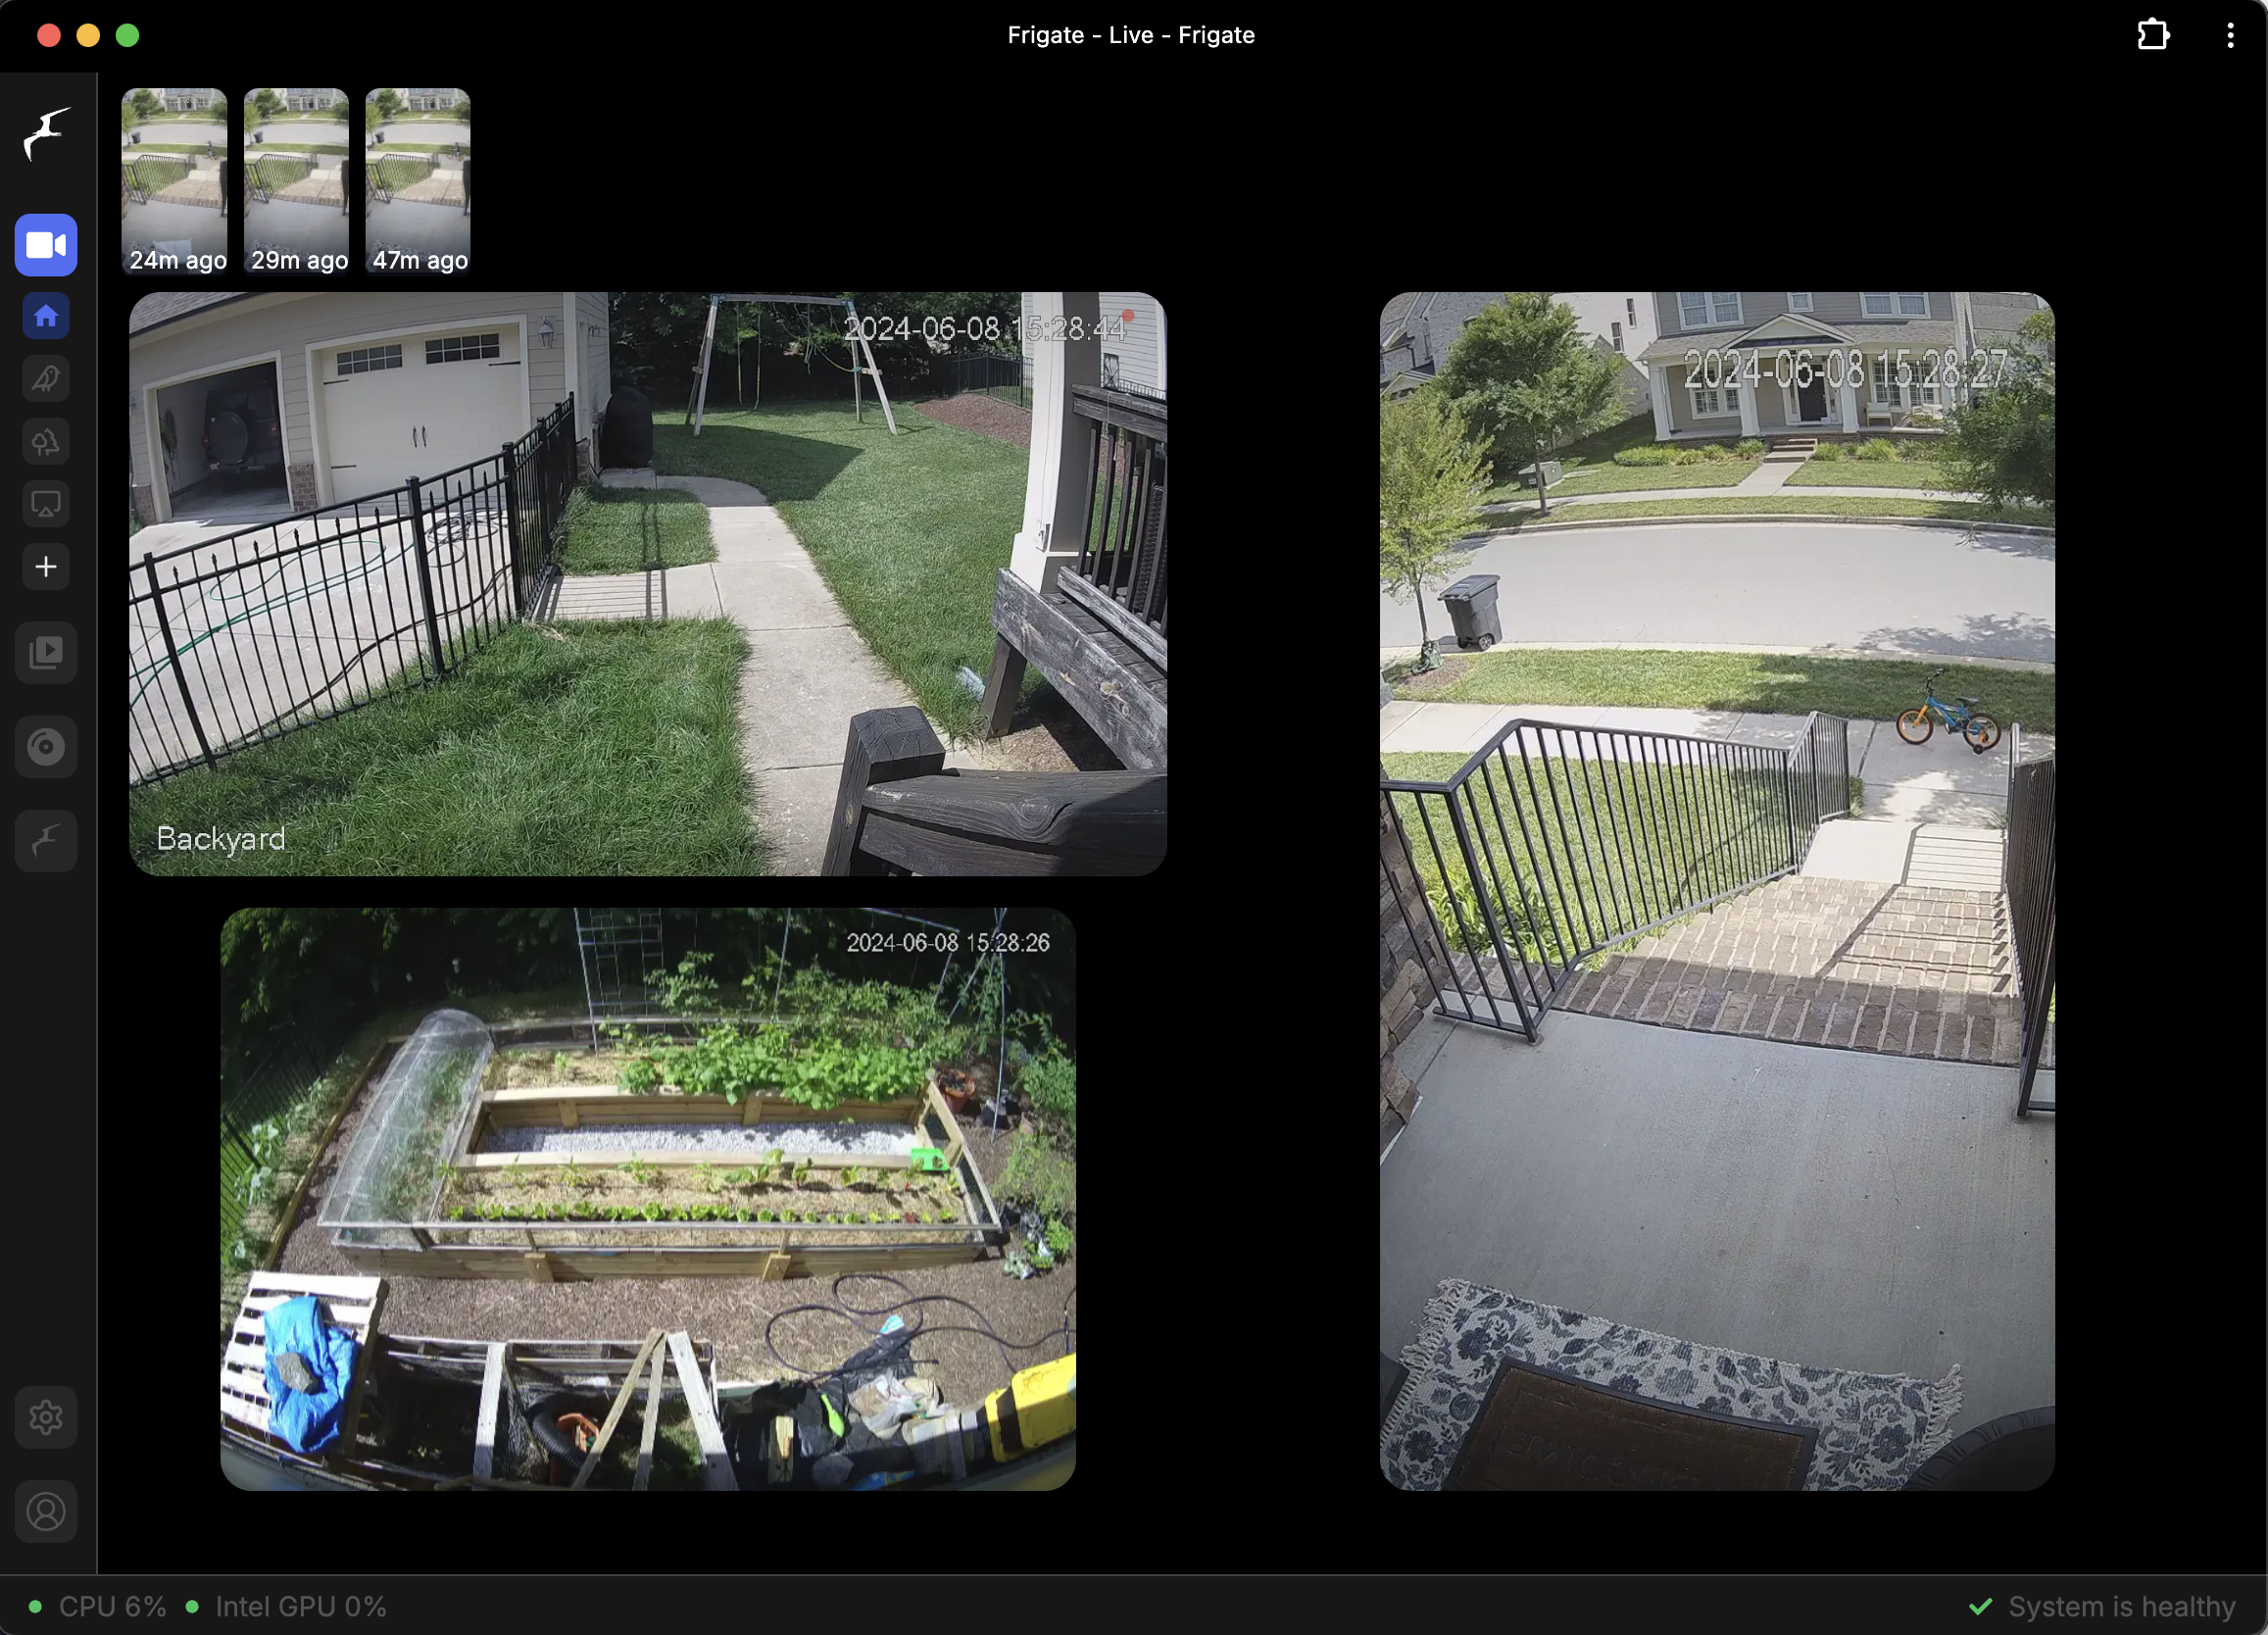 blakeblackshear/frigate
IP 카메라를 위한 실시간 로컬 객체 탐지 기능을 갖춘 NVR








