
Skip to content
KitploitKITPLOIT
도구익스플로잇블로그
Log in
제출
도구익스플로잇블로그
제출

해킹, 침투 테스트 및 사이버 보안 도구를 당신의 보안 무기고에!

Kitploit은 해킹, 사이버 보안 및 침투 테스트 도구 디렉토리입니다. 최신 프로젝트 업데이트를 발견하여 취약점을 찾고, 시스템을 분석하고, 테스트를 자동화하고, 보안을 강화하세요.

피드문의개인정보© 2026 Kitploit

도구 디렉토리

카테고리

모든 카테고리 보기
Loading categories
카테고리

CTF

Capture The Flag platforms, challenge creation, solving tools, and competitive cybersecurity frameworks.

Kitploit 추천
추천 도구

10 선택됨
pwntools preview#1

pwntools

GitHubgallopsled/pwntools
13.6k2일 전
pwndbg preview#2

pwndbg

GitHubpwndbg/pwndbg
10.8k1일 전
gef preview#3

gef

GitHubhugsy/gef
8.3k2개월 전
RsaCtfTool preview#4

RsaCtfTool

GitHubrsactftool/rsactftool
7.1k12일 전
CyberChef preview#5

CyberChef

GitHubgchq/cyberchef
35.6k16시간 12분 전
Ciphey preview#6

Ciphey

GitHubbee-san/ciphey
21.6k9시간 57분 전
how2heap preview#7

how2heap

GitHubshellphish/how2heap
8.8k5개월 전
ROPgadget preview#8

ROPgadget

GitHubjonathansalwan/ropgadget
4.5k4개월 전
Ropper preview#9

Ropper

GitHubsashs/ropper
2.1k2개월 전
zsteg preview#10

zsteg

GitHubzed-0xff/zsteg
1.6k9개월 전
최신관련성인기최근 업데이트
1090 결과
CVE-2026-44578-next-js-ssrf preview

CVE-2026-44578-next-js-ssrf

GitHubisaca0315/cve-2026-44578-next-js-ssrf

이 실험실은 괜찮을 수도 있고 아닐 수도 있지만, 테스트 중이며 작동해야 합니다. AI에게 물어보세요 하하하

vulnerability-analysisexploitationweb-application-exploitation+4
1개월 전
CVE-2026-41651 preview

CVE-2026-41651

GitHubgbuyssens/cve-2026-41651

PackageKit의 TOCTOU 경쟁 조건을 통한 로컬 권한 상승.
privilege-escalationvulnerability-analysisexploitation+2
3개월 전
cve-2024-4577-lab preview

cve-2024-4577-lab

GitHubkhwajasaad267-coder/cve-2024-4577-lab

# Docker 기반 CTF 랩: CVE-2024-4577 PHP-CGI 인자 주입을 통한 RCE 실증 RCE로 이어지는 CVE-2024-4577 PHP-CGI 인자 주입을 시연하는 Docker 기반 CTF 랩입니다. 취약한 PHP 5.4.1 CGI, 익스플로잇…
vulnerability-analysisexploitationweb-application-exploitation+4
2개월 전
CVE-2026-60004-gitea-0day preview

CVE-2026-60004-gitea-0day

GitHubsachinart/cve-2026-60004-gitea-0day

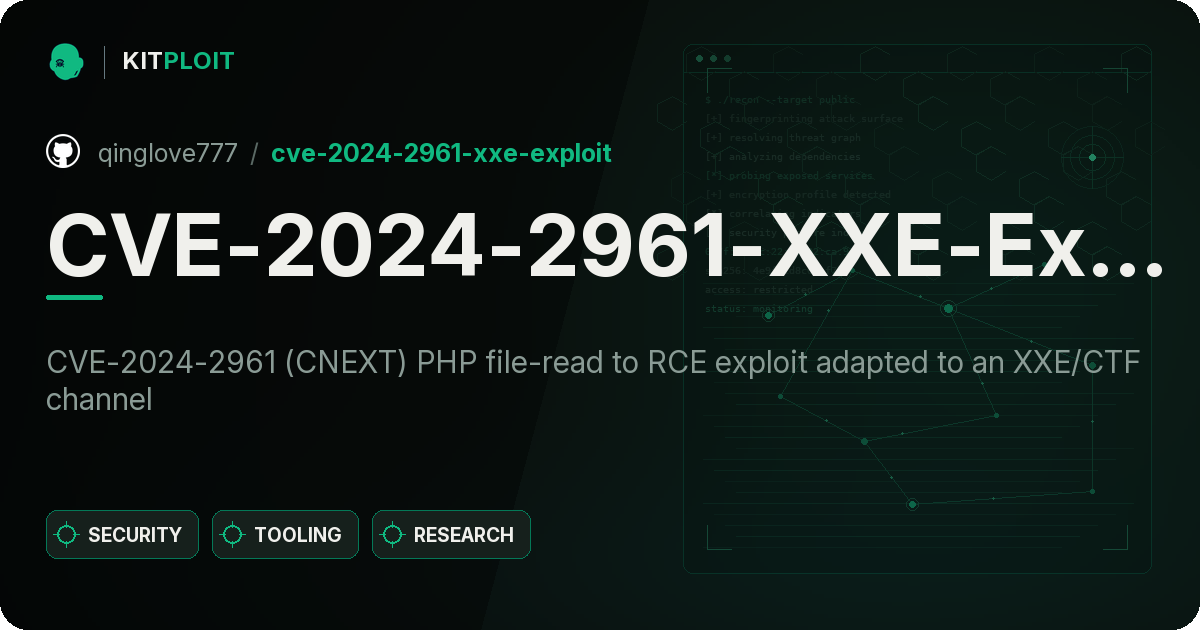
CVE-2026-60004 — Gitea <= 1.27.0 사전 인증 RCE

exploitationweb-application-exploitationpost-exploitation+3
3개월 전
CVE-2026-30225-OliveTin-RCE preview

CVE-2026-30225-OliveTin-RCE

GitHubhackerking24/cve-2026-30225-olivetin-rce

OliveTin의 인증되지 않은 RCE(CVE-2026-30225)에 대한 개념 증명 익스플로잇으로, 안전하지 않은 게스트 기본 설정과 검증되지 않은 인수 유형을 악용하여 취약한 인스턴스에서 루트 셸을 획득합니다.

privilege-escalationvulnerability-analysisexploitation+5
1개월 전
CVE-2023-33733-Exploit-PoC preview

CVE-2023-33733-Exploit-PoC

GitHubl41kaa/cve-2023-33733-exploit-poc

CVE-2023-33733을 대상으로 하는 웹 애플리케이션용 Python 익스플로잇 스크립트. 침투 테스트 및 CTF 환경을 위해 인증, 세션 추출 및 리버스 셸 전달을 자동화합니다.
payload-generationvulnerability-analysisexploitation+3
32년 전
CVE-2024-2961-XXE-Exploit preview

CVE-2024-2961-XXE-Exploit

GitHubqinglove777/cve-2024-2961-xxe-exploit

CVE-2024-2961(CNEXT) PHP 파일 읽기에서 RCE로 이어지는 익스플로잇을 XXE/CTF 채널에 맞게 변형한 도구
vulnerability-analysisexploitationweb-application-exploitation+3
1개월 전
CVE-2026-29782-OpenSTAManager-RCE preview

CVE-2026-29782-OpenSTAManager-RCE

GitHubhackerking24/cve-2026-29782-openstamanager-rce

CVE-2026-29782에 대한 개념 증명 익스플로잇으로, OpenSTAManager에서 SQL 인젝션과 PHP 객체 인젝션을 연쇄적으로 활용하여 원격 코드 실행을 달성합니다. 웹셸 배포 및 리버스 셸 옵션을 포함합니다.

vulnerability-analysisexploitationweb-application-exploitation+2
1개월 전
CVE-2025-4138_tarfile_filter_bypass preview

CVE-2025-4138_tarfile_filter_bypass

GitHubthefizzyfish/cve-2025-4138_tarfile_filter_bypass

CVE-2025-4138 - Python 추출 디렉터리 외부에 임의 파일 쓰기
payload-generationvulnerability-analysisexploitation+3
38개월 전
CVE-2026-39987 preview

CVE-2026-39987

GitHubalreadyclosed/cve-2026-39987

CVE-2026-39987 marimo 0.20.4 PoC
exploitationweb-application-exploitationctf+2
3개월 전
CVE-2018-6789 preview

CVE-2018-6789

GitHubberaphin/cve-2018-6789

Exim의 base64 디코딩에서 발생하는 힙 버퍼 오버플로우인 CVE-2018-6789용 익스플로잇으로, 청크 오버랩과 ACL 문자열 조작을 통해 원격 코드 실행을 달성합니다.
vulnerability-analysisexploitationctf+3
36년 전
CVE-2023-20938-poc preview

CVE-2023-20938-poc

GitHubbyt3quester/cve-2023-20938-poc

로컬 권한 상승 PoC for CVE-2023-20938, Android binder의 use-after-free 취약점으로, 취약한 테스트 빌드에서 root 권한을 획득하고 SELinux를 비활성화합니다.
android-securityprivilege-escalationexploitation+3
14개월 전
CVE-2026-9198 preview

CVE-2026-9198

GitHubywh-jfellus/cve-2026-9198

CVE-2026-9198에 대한 개념 증명 - IBM Langflow 자동 로그인 우회를 통한 인증 없는 RCE

vulnerability-analysisexploitationweb-application-exploitation+4
3개월 전
CVE-2025-32432 preview

CVE-2025-32432

GitHubcd-ratel/cve-2025-32432

CVE-2025-32432에 대한 동작 PoC - Yii2 PhpManager 가젯 + nginx access.log 포이즈닝을 통한 Craft CMS <= 5.6.16 비인증 RCE
vulnerability-analysisexploitationweb-application-exploitation+4
25개월 전
CVE-2023-25690_lab preview

CVE-2023-25690_lab

GitHubgiordy0424/cve-2023-25690_lab

HTTP Request Smuggling 실습: Apache 2.4.55 CRLF injection

vulnerability-analysisweb-application-exploitationctf+3
2개월 전
CVE-2024-27198_Lab preview

CVE-2024-27198_Lab

GitHubcmpnn-romain/cve-2024-27198_lab

CVE-2024-27198 실습 환경
vulnerability-analysisexploitationweb-application-exploitation+8
1개월 전
CVE-2025-29927-PoC preview

CVE-2025-29927-PoC

GitHubritinify/cve-2025-29927-poc

CVE-2025-29927에 대한 개념 증명 익스플로잇으로, Next.js 미들웨어 권한 부여 우회 취약점입니다. 취약한 대상 실습 환경과, 조작된 x-middleware-subrequest 헤더를 전송하여 우회를 검증하는 Python 스크립트가 포함되어 있습니다.
exploitationweb-application-exploitationctf+3
2개월 전
CVE-2022-25765 preview

CVE-2022-25765

GitHubinnocentx0/cve-2022-25765

Python용 CVE-2022-25765 개념 증명(PoC) — pdfkit의 명령 주입 취약점으로, 조작된 PDF 생성을 통해 원격 코드 실행을 가능하게 합니다.

vulnerability-analysisexploitationweb-application-exploitation+4
2개월 전
이전1…293031…61다음







