#1
Tools focused on penetration testing, reversing, and securing Android apps and the Android OS.
Kitploit 추천

 radareorg/radare2
UNIX-like reverse engineering framework and command-line toolset
 permissionlesstech/bitchat-android
블루투스 메시 네트워크를 통한 분산형, 암호화된 P2P 메시징 앱. 인터넷, 서버, 전화번호가 필요 없습니다. X25519 + AES-256-GCM 암호화, IRC 스타일 명령어, iOS와의 크로스 플랫폼 호환성을 제공합니다.
 sarabpal-dev/ionstack-s22u
CVE-2026-43499 full exploit chain for Samsung Galaxy S22 Ultra (Android 5.10 kernel)
 florentineprinzessinzusachsen/badbox-h713-projector
Allwinner H713 Android 프로젝터의 BadBox 악성코드 분석 및 제거 가이드: ADB 접근, 감염 증거, 펌웨어 백업, 드로퍼 제거, 검증.
 amd2g2zz/kunglao-agent
The reverse-engineering expert agent: plans its own analysis path, derives every fact from raw evidence, and converges under mechanical verification…
 qingle009/opace6-cve-2026-64560
OnePlus Ace 6 임시 루트 도구 (CVE-2026-64560) - bootidParent 주소를 수정한 기기 검증 포트
 alirezaparsi/copg
Advanced per-app device / CPU / GPU spoofer for rooted Android — device profiles, per-app CPU models, prop & Android-ID spoofing, all driven by a…
 bmax121/kernelpatch
Linux 커널 이미지만으로 Linux 커널 패치 및 후킹.
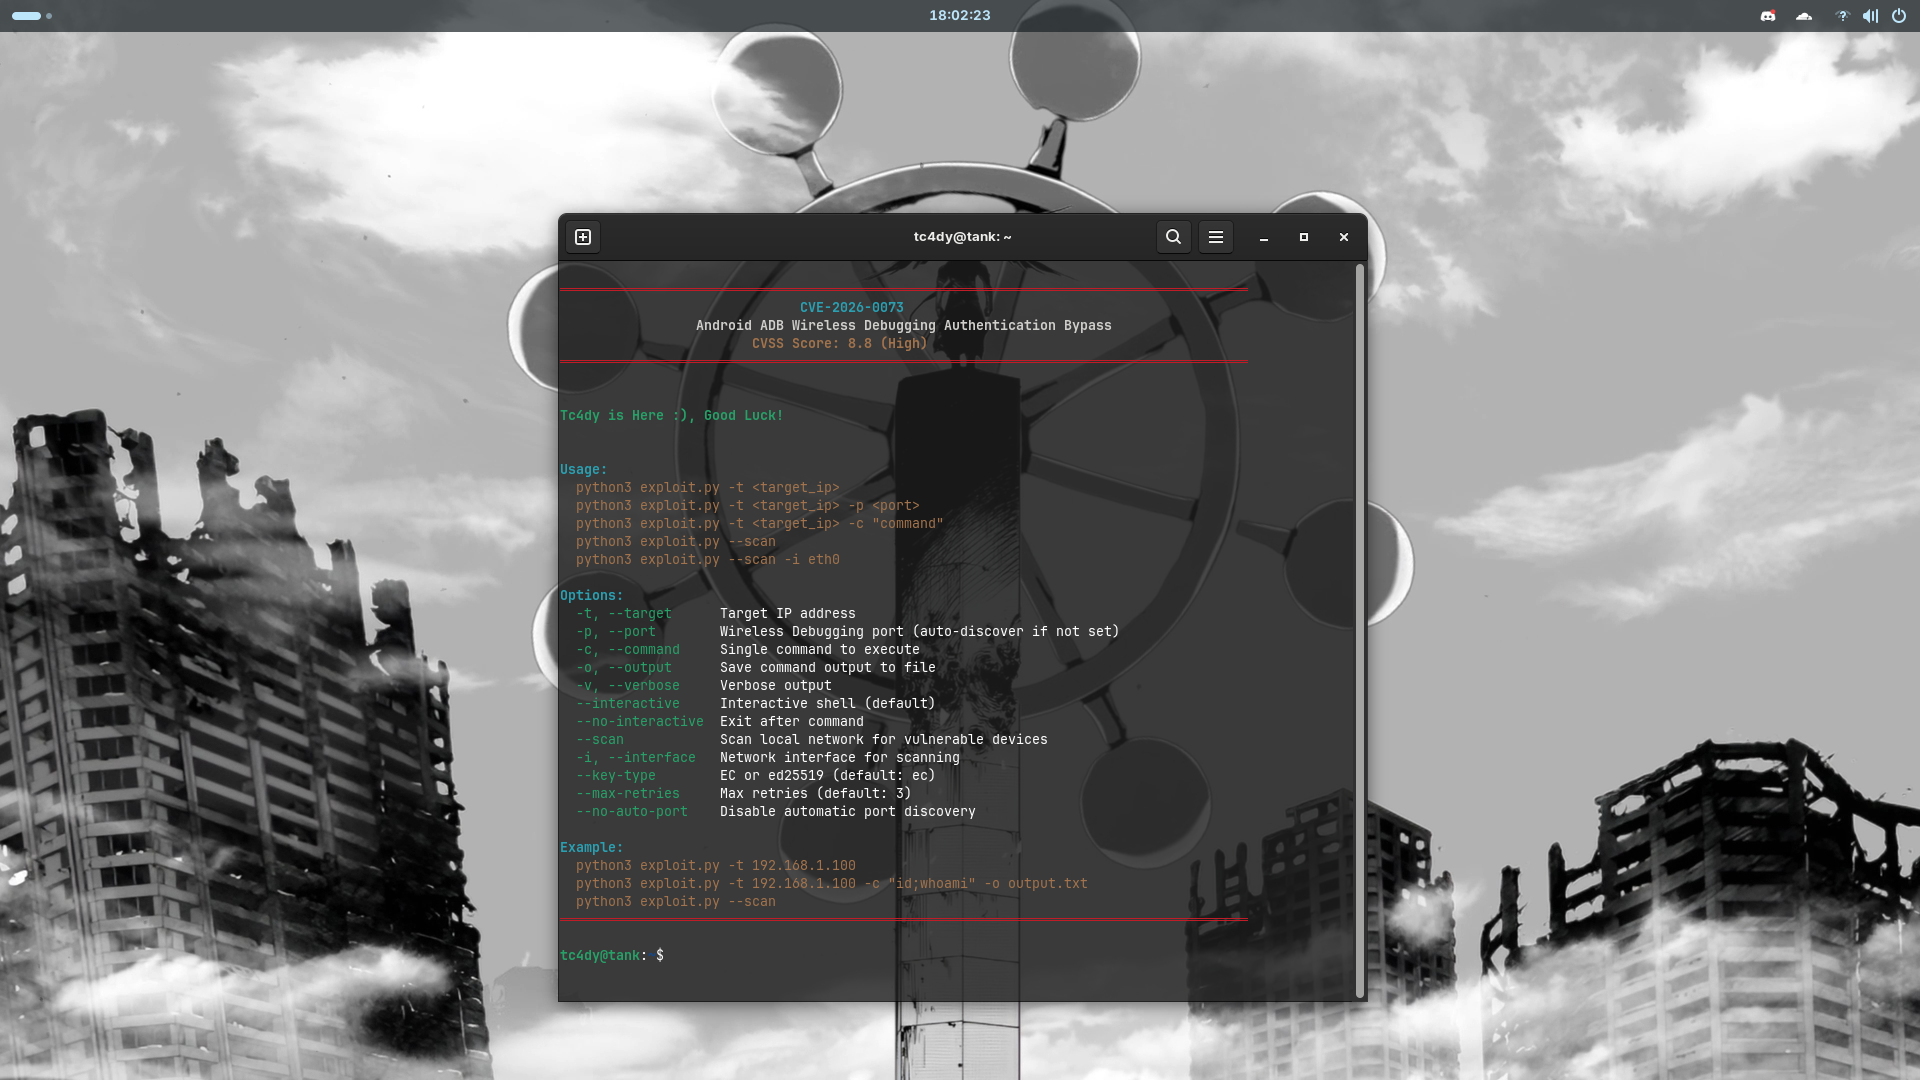 tc4dy/cve-2026-0073-poc-exploit
Zero-click authentication bypass exploit for Android ADB Wireless Debugging (CVE-2026-0073). Provides interactive shell, command execution, and…
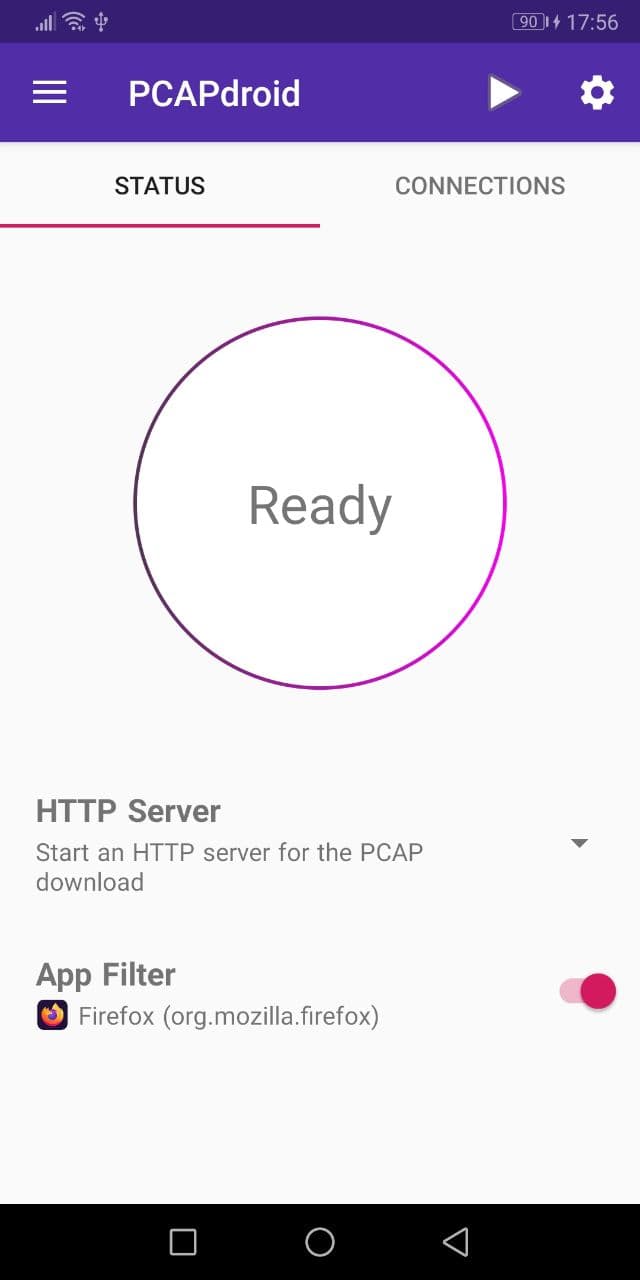 emanuele-f/pcapdroid
루트 권한이 필요 없는 안드로이드용 네트워크 모니터, 방화벽 및 PCAP 덤퍼
 gojue/ecapture
eBPF를 사용하여 CA 인증서 없이 SSL/TLS 평문을 캡처합니다. amd64/arm64용 Linux/Android 커널에서 지원됩니다.
 become-illusory/cve-2026-64560-a16
CVE-2026-64560 툴킷: Go 단일 바이너리 툴체인 + realme RMX5010 (A16, SM8750) 타깃 포트
 lyravoid/folkpatch
Root access to the kernel can be achieved simply by patching the Boot partition for reflashing. This solution is based on a non-parallel extended…
mobsf/mobile-security-framework-mobsfAndroid, iOS, Windows용 자동화된 모바일 애플리케이션 보안 테스트 프레임워크입니다. 정적 및 동적 분석, 멀웨어 탐지, CI/CD 통합을 통한 API 보안 테스트를 수행합니다.
 gmh5225/awesome-game-security
Curated index of game security research: anti-cheat internals, DMA attacks, reverse engineering, kernel/mobile protections, and graphics API hooking…
 skylot/jadx
Android Dex 및 APK 파일을 읽을 수 있는 Java 소스 코드로 디컴파일하는 명령줄 및 GUI 도구입니다. 리소스 디코딩, 난독 해제 및 Smali 디버깅 기능을 제공합니다.
 lyravoid/kernelpatch
Linux 커널을 스트립된 커널 이미지만으로 패치하고 후킹하며, 심볼을 추출하고 코드를 주입하여 arm64에서 인라인 및 시스템 콜 후킹을 수행합니다.
 librepods-org/librepods
Apple 생태계로부터 해방된 AirPods