

 pennacle-security/summit
オープンソースのWebセキュリティテストプラットフォーム:プロキシ、スキャナー、ファザーを1つのCLIに統合。Pennacle Security製。


Webセキュリティテストのためのスクリプト可能な単一CLI:スキャナー、プロキシ、ファザー、認可テスト、WAF分析、リンクハイジャック検出、偵察。
同等のツールが有償である領域を無償で - Pennacle Security による。
私たちは毎日BurpとZAPを使っています。同時に、それらが備えていない3つのものを常に求めていました。CIでスクリプトから操作できるスキャナー、どれだけ確実かを教えてくれる検出結果、そして一息で読み切れるほど小さいコードベースです。Summitはそのツールです - v0.5、MIT、依存関係は1つ(requests)、オープンに開発されています。
完全なドキュメント: pennacle-security.github.io/summit
通常は有償ツールの背後にある機能に加え、スキャンの中核:
| 機能 | Summit | 通常の手段 |
|---|---|---|
| アクセス制御の不備テスト(BOLA/IDOR) | summit authorize | Autorize系アドオン / 有償ワークフロー |
| 隠しパラメータの発見 | summit mine | Param Miner系アドオン |
| OpenAPI駆動スキャン | summit scan --openapi | アドオン |
| WAFフィンガープリンティング + バイパス探索 | 内蔵 | 部分的 / アドオン |
| リンクハイジャック検出 | 内蔵 | 有償拡張 |
| SQLi、XSS、リダイレクト、トラバーサル、テイクオーバー、ホストヘッダー、CORS | 内蔵 | コアスキャナー(無償) |
| 偵察チェーン:subfinder -> httpx -> nmap | summit recon | 手動での連結 |
| レート制限、リトライ、JWT/エンコーダーツールキット | 内蔵 | アドオン / 有償 |
| CI対応、信頼度ラベル付きの検出結果 | これが本質 | 有償自動化 |
すべての検出結果には信頼度ラベルが付きます:confirmed(観測された事実)または potential(ヒューリスティック)。この区別はツール全体を貫いています。
git clone https://github.com/pennacle-security/summit.git
cd summit
pip install -e .
Python 3.10+。次に、意図的に脆弱に作られたローカルターゲットに対して動作する様子を確認します:
python examples/vuln_app.py        # terminal 1 - the target (127.0.0.1 only)
summit scan http://127.0.0.1:8765  # terminal 2 - the scan
実際のエンゲージメントにおけるより完全なパスは次のようになります:
summit recon target.com --json recon.json                 # subdomains -> hosts -> ports
summit scan https://target.com --depth 2 --rate 10        # crawl + all checks
summit scan --openapi api-spec.json                       # API: scan what the spec admits to
summit authorize https://target.com/admin?user=1 \
  --role 'admin=Cookie: session=abc' \
  --role 'user=Cookie: session=xyz'                       # BOLA/IDOR testing
このページのすべての主張は examples/evidence.py によって再現されます - これはデモターゲットをライブで実行し、各機能を測定し、実際の数値とともに PASS/FAIL を出力します。CI はプッシュごとにこれを実行します。成立しなくなった主張はビルドを失敗させます。
python examples/evidence.py)[PASS] full scan: 16 seeded check families detected, zero false positives
53 findings in 22.9s (344 requests), missing=none, control link flagged=no, 19 finding(s) carry confidence=confirmed
[PASS] resource takeover fingerprint detected on the target's own 404
Possible AWS S3 resource takeover | AWS S3: 'nosuchbucket'
[PASS] host header injection: marker domain echoed back by the app
Host: summit-host-probe.example -> reflected (reset-link poisoning surface)
[PASS] CORS reflects an arbitrary origin with credentials allowed
ACAO: https://summit-cors-probe.example; ACAC: true
[PASS] WAF bypass: naive filter blocks, tampered payload lands decoded
raw payload -> HTTP 403 (blocked); URL-encoded once -> HTTP 200, payload reflected decoded: True
[PASS] CAPTCHA challenge detected (reported, not solved)
/login -> reCAPTCHA via marker 'recaptcha/api.js'
[PASS] rate limiting: --rate 5 paces 12 requests to ~2.2s; unlimited runs free
12 requests at rate 5 -> 2.20s (theoretical floor: 2.2s); 12 requests unlimited -> 0.02s
[PASS] concurrency on a latency-bearing target: 8 workers vs serial
40 requests x 25ms latency: serial 1.33s -> parallel 0.18s (7.3x speedup)
[PASS] smart prioritizer ranks known-injectable parameters first
probing starts with: [('query', 'search?query=laptop'), ('id', 'user?id=1'), ('url', 'example.com')]
[PASS] toolkit decodes JWT header/payload and states the signature is unverified
signature NOT verified - decoding only
[PASS] update check compares versions numerically (0.3 < 0.10)
is_outdated('0.3.0', '0.10.0') -> True; is_outdated('1.0.0', '0.9.9') -> False
[PASS] broken access control: admin panel served identically to a low-privilege role
verdict=broken; finding=Broken access control (BOLA/IDOR candidate)
[PASS] hidden parameter mining finds the undocumented debug parameter, zero noise
1 finding(s): ['debug'] (all confirmed reflections)
[PASS] openapi-driven scan: spec alone leads the engine to seeded SQLi and XSS
2 spec target(s) scanned -> 10 findings, sqli-error=yes, xss-reflection=yes
[PASS] OS command injection: marker executed and echoed by the server
semicolon: exec marker x2, control marker x1 | CWE-78
[PASS] server-side template injection: {{7*7}} came back as 49
Jinja2/Twig: {{7*7}} -> 49 | CWE-1336
[PASS] CRLF injection: X-Summit-CRLF header materialized in the response
X-Summit-CRLF: injected | CWE-113
[PASS] sensitive file exposure: /.env confirmed by content signature
content signature: 'APP_KEY=' | CWE-538
[PASS] CVE detection: Apache/2.4.49 banner maps to known CVEs
detect_cves('Apache/2.4.49') -> ['CVE-2021-41773', 'CVE-2021-42013']
evidence summary: 19/19 claims verified
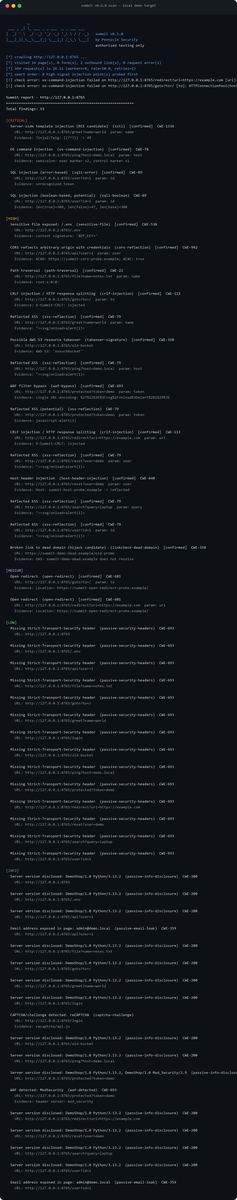
デモターゲットに対する実際のスキャンの可視化:
すべてをご自身で再現する:
python examples/vuln_app.py    # terminal 1 - the target
summit scan http://127.0.0.1:8765
python examples/evidence.py    # re-verify every claim above
デモは正常な外部リンク(https://example.com)をネガティブコントロールとしてシードします。これは決して報告されてはならず、CIはシードされた検出結果と並んでそれを検証します。それでも何か問題が見つかりましたか?報告してください。
