
 mziqudhd92/honeypot-auditor
これはハニーポットに見えますか? (DTLLAH) 対象IPがハニーポットのように振る舞うかどうかをフィンガープリントするマルチプロトコルCLI — Honeyscore、アクティブな認証/状態プローブ、および重み付きスコアを使用。

.______________________________________________________________________________.
|  :: H-AUDITOR :: v1.1.0 :: "DIALING IN... CARRIER DETECTED" ::                |
|------------------------------------------------------------------------------|
|  "warez? nah. headers. we trade banners, not bins."                          |
|  "if it answers any password, it ain't production — it's a lure."            |
|  "respect the sysop. probe only what you own. leave no STOR behind."         |
|______________________________________________________________________________|



これはハニーポットに見えますか?(DTLLAH) — 対象のIPがハニーポットのように振る舞うかどうかをフィンガープリントするマルチプロトコルCLIで、ハニーポットを識別するためのさまざまな戦略を実装しています。
サイト (BBS / NFO): https://mziqudhd92.github.io/honeypot-auditor/
エージェント / AEO: llms.txt · agents.md
  ▄▄▄▄▄▄▄▄▄▄▄▄▄▄▄▄▄▄▄▄▄▄▄▄▄▄▄▄▄▄▄▄▄▄▄▄▄▄▄▄▄▄▄▄▄▄▄▄▄▄▄▄▄▄▄▄▄▄▄▄▄▄▄▄▄▄▄▄▄▄▄▄
  █  >>> LIVE DEMO · v1.1.0 · DD-HONEYPOT · 5 SERVICES · -v / --deep <<<   █
  ▀▀▀▀▀▀▀▀▀▀▀▀▀▀▀▀▀▀▀▀▀▀▀▀▀▀▀▀▀▀▀▀▀▀▀▀▀▀▀▀▀▀▀▀▀▀▀▀▀▀▀▀▀▀▀▀▀▀▀▀▀▀▀▀▀▀▀▀▀▀▀▀
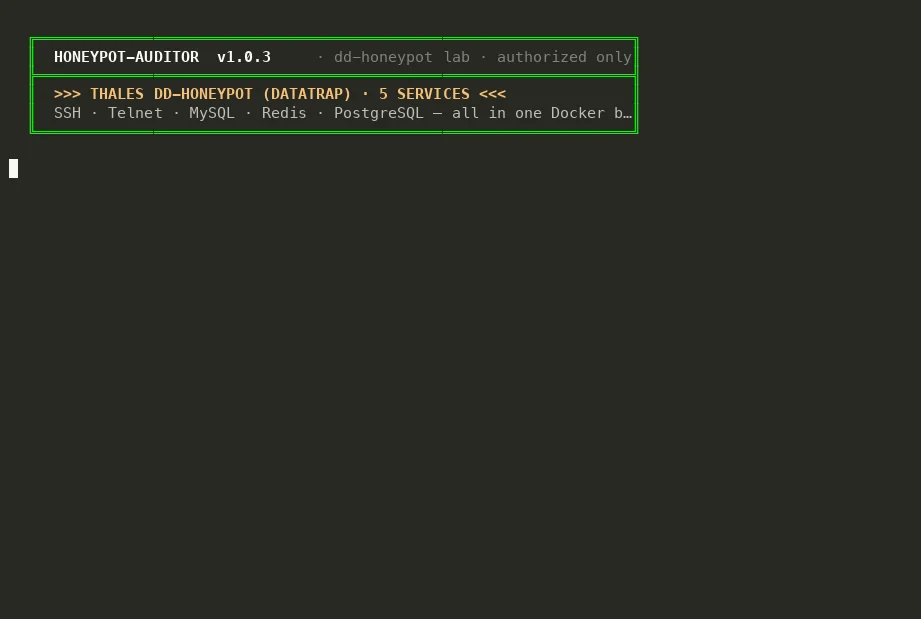
  "five DataTrap faces on loopback: map the ports, run -v, then --deep.
   Honeyscore 100% — Confirmed Honeypot. same fingerprinter, new decoy."
                        — dd-honeypot lab · v1.1.0 · authorized only
.------------------------------------------------------------------------------.
|  NFO · READ BEFORE YOU DIAL                                                  |
|------------------------------------------------------------------------------|
|  Authorized targets ONLY. Lab boxes. Decoys you own. Sensors you run.        |
|  Permission on paper (or in ticket).                                         |
|                                                                              |
|  Scanning random /16 because Shodan said "interesting" = YOU are the bait.   |
|                                                                              |
|  TYPE ...... Multi-Protocol Decoy Fingerprinter / Lab Util                   |
|  PLATFORM .. Linux · macOS · Windows (Python 3.11+)                          |
|  LICENSE ... MIT · spread the sauce · keep the copyright                     |
|  PYPI ...... pypi.org/project/honeypot-auditor                               |
|  REPO ...... github.com/mziqudhd92/honeypot-auditor                          |
'------------------------------------------------------------------------------'
Honeypot Auditor — ひとつの失礼な問いを投げかける CLI:
この IP は低対話型ハニーポットのように振る舞うのか、それとも 実際に誰かにダウンタイムの請求をしかねない何かのように振る舞うのか?
パッシブインテリジェンス(Shodan Honeyscore)に加え、よくあるデコイの表面に対するアクティブで非破壊的なプローブ。重み付けされた Honeyscore(0~100%)、Rich コンソールテーブル、バージョン管理された JSON レポートを出力します。
クイックスタートチュートリアル:AWS Spot ハニーポットラボ · ローカル Web UI(serve、XP.css)
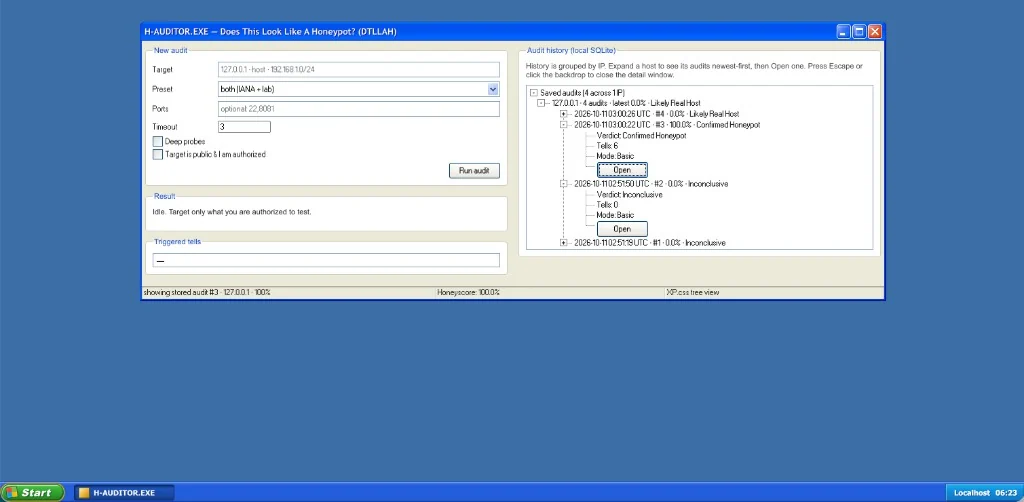
  "localhost UI · IP-grouped history · Open a saved audit for the full tell tree."
                        — honeypot-auditor serve · XP.css · 127.0.0.1 only
  [ BASIC ]  passive intel · Nmap NSE · 34 protocol engines (TCP + UDP) · up to 3 strategies each
  [ DEEP  ]  shell semantics · OS coherence · HASSH · TCP stack · FSM fuzz
             · co-tenancy buffet detect · latency · latency-under-load · egress bait
             (flag: --deep · more intrusive · same authorization rules)
"elite? nah. just consistent timeouts and a honest --confirm-authorized."
  ┌─ USERS · PyPI (public index — no pip config voodoo) ─────────────────────┐
  │  python3 -m venv .venv && source .venv/bin/activate   # recommended      │
  │  pip install honeypot-auditor                                            │
  │  pip install "honeypot-auditor[full]"    # + nmap impacket shodan scapy   │
  │  honeypot-auditor --version                                              │
  └──────────────────────────────────────────────────────────────────────────┘
| インストール | 有効になる機能 |
|---|---|
pip install honeypot-auditor | コアプローブ(Paramiko + Requests + Rich + figlet ヘッダー) |
pip install "honeypot-auditor[full]" | + Nmap 統合 · SMB/Impacket · Shodan SDK · Scapy · ディープ telnet |
SHODAN_API_KEY または --shodan-key で Shodan OSINT が有効になります(オプトイン — それ以外ではクエリされません)。[full] はクライアントライブラリのみをインストールします。
Nmap 実行ファイルは別途、信頼できるシステムインストールが必要です。
Windows PowerShell では py -m venv .venv に続いて .\.venv\Scripts\Activate.ps1 を使用します。
Raw ソケットプローブは Npcap と管理者権限のターミナルを必要とする場合があります。利用できない機能は報告され、スキップされます。
初回接続:
honeypot-auditor --help          # -h, --help, or /help (BBS figlet header)
honeypot-auditor --target 127.0.0.1
  ┌─ DEVELOPERS · from source ───────────────────────────────────────────────┐
  │  git clone https://github.com/mziqudhd92/honeypot-auditor.git            │
  │  cd honeypot-auditor && python3 -m venv .venv && source .venv/bin/activate│
  │  pip install -e ".[full,dev,security]"                                   │
  │  make test-cov && make lint && make security                             │
  └──────────────────────────────────────────────────────────────────────────┘
pip install 不要(git checkout — 最小限の依存関係を一度だけインストール):
pip install rich paramiko requests    # pyproject.toml is the single source of truth
python3 honeypot-auditor.py --help
python3 honeypot-auditor.py --target 127.0.0.1
pyfiglet / rich-argparse はスクリプトパスでは任意です(存在しない場合はプレーンなヘッダー + 標準ライブラリのヘルプになります)。完全なプローブには pip install -e ".[full]" が必要です。
リリースメンテナー向け → docs/PUBLISHING.md
# local lab · default probes IANA + docker/lab ports (22 and 2222, 80 and 8081, …)
honeypot-auditor --target 127.0.0.1

# go deep · six extra detection axes · still no exploits
honeypot-auditor --target 127.0.0.1 --deep

# internet-facing target · need explicit ack + Shodan key if you want intel
honeypot-auditor --target 203.0.113.10 --confirm-authorized

# SSH 22 only (does not scan the rest of the preset)
honeypot-auditor --target 203.0.113.10 -p 22 --confirm-authorized







