

agent-bom v0.104.0
AIサプライチェーンBOM:すべてのエージェント、MCPサーバー、AIパッケージ、およびそれぞれが到達できる範囲。コード、コンテナ、クラウド、AI向けのオープンソーススキャナーとセルフホスト型コントロールプレーン。セルフホストは無料、ローカルスキャンはアカウント不要。



AI supply-chain BOM: supported agents, MCP servers and AI packages, and what each one can reach.
For AppSec teams and developers who run Claude Code, Cursor, Codex or any MCP client: see which agents, MCP servers, tools and packages are installed, which are vulnerable, and what each one can reach. Local scans need no account.
Quick start · Try in browser · Laptop → team → org · Product tour · Docs
Quick start
From the repository you want to inspect, with uv installed:
uvx agent-bom scan . -f html -o agent-bom-report.html
Open agent-bom-report.html for inventory, findings and fix guidance. Run it
again later to see what changed. No MCP configuration in the project? Package
findings still apply.
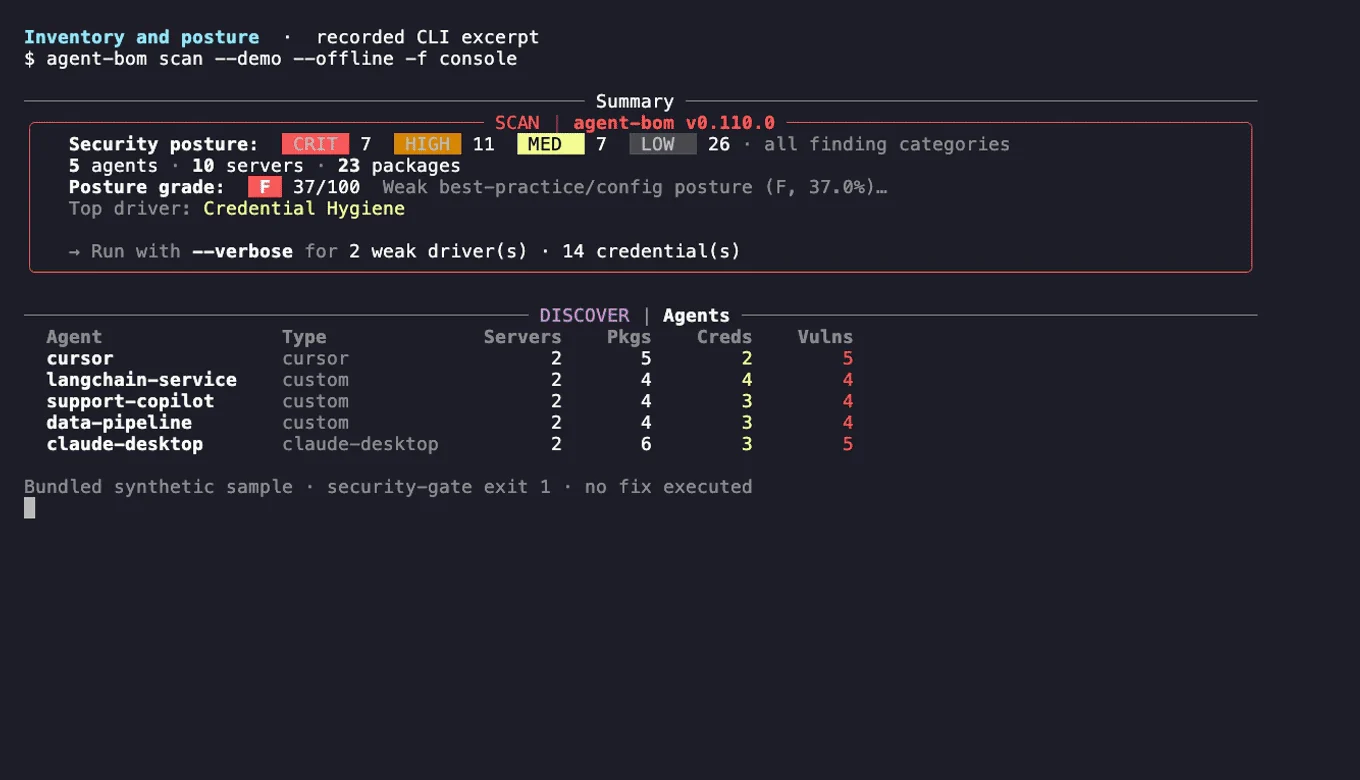
No project handy? uvx agent-bom scan --demo --offline scans a bundled sample.
Exit 1 is expected there: the sample trips the security gate. Elsewhere, a
non-zero exit can mean a security gate or incomplete assessment; inspect the
report and coverage (exit codes,
first-run guide).
What the scan reads and what it does not establish
The scan stays inside this repository: packages, MCP configuration, secrets and personal data, skills and IaC. It does not read agent configuration elsewhere on the machine. Missing evidence is reported as partial, not clean. See what a scan does and does not establish.
From laptop to team to org
- On your laptop:
uvx agent-bom scan .for findings with fixes and a delta on every rescan;claude mcp add agent-bom -- uvx agent-bom mcp serverto use agent-bom as a tool inside your coding agent (MCP server, plugins). - In your team:
uses: koda-ai-studio/agent-bom@v0on pull requests and a weeklyschedule:for a PR gate with a findings comment, SARIF in code scanning and a weekly rescan that catches new CVEs in unchanged code (GitHub Action). - Across your org:
agent-bom uplocally, then Docker Compose or the Helm chart fromoci://ghcr.io/koda-ai-studio/charts/agent-bomfor retained scans, one graph of agents, MCP servers, packages and credentials, SSO and audit in your own infrastructure (self-host).
All three are free under Apache-2.0 and are adoption paths, not editions. There is no managed cloud offering today; community support runs on GitHub (deployment chooser, support model).
Why an AI supply-chain BOM
A CVE in an AI package, a poisoned tool description or an over-scoped credential matters by what the agent that loads it can reach. A package SBOM stops at packages; agent-bom records the chain, agent → MCP server → tool → package → credential → data, and keeps the evidence for every edge.

Sample data. What the sample shows
What it covers
Agents and MCP servers, models and AI platforms, dependencies, code, containers and IaC, cloud and data platforms, and a runtime MCP proxy and gateway. Exports are SARIF, CycloneDX, SPDX, JSON and HTML.