#1

 nikaiw/vmkatz
VMメモリスナップショットと仮想ディスクからWindowsの資格情報を直接抽出する
 log2timeline/plaso
ログ、ファイル、システムアーティファクトを解析してスーパータイムラインを構築し、調査における時系列イベントの相関付けを可能にするデジタルフォレンジックスエンジン。
 threatray/threat-research
ThreatrayのThreat ResearchによるIoCsおよびYARAルール
 seladb/pcapplusplus
クロスプラットフォームのC++ライブラリで、高性能なネットワークパケットキャプチャ、解析、生成、分析を実現します。libpcap、DPDK、AF_XDP、PF_RINGをサポートし、TCP再構成、TLSフィンガープリンティング、プロトコルデコードを含みます。
 clausing/scripts
デジタルフォレンジック、インシデントレスポンス、ネットワーク分析のためのPythonおよびPerlスクリプト集。ハッシュ署名ツールやパケットgrepユーティリティを含む。
 cicd-sensor/cicd-sensor
eBPF-powered runtime security sensor for CI/CD pipelines. Detects supply-chain attacks, logs process ancestry and file access, and provides forensic…
 rorywag/hayabusa-bulk-runner
Bulk-run Hayabusa across a folder of triage collections, one run per host, with per-host reports and a cross-host triage dashboard
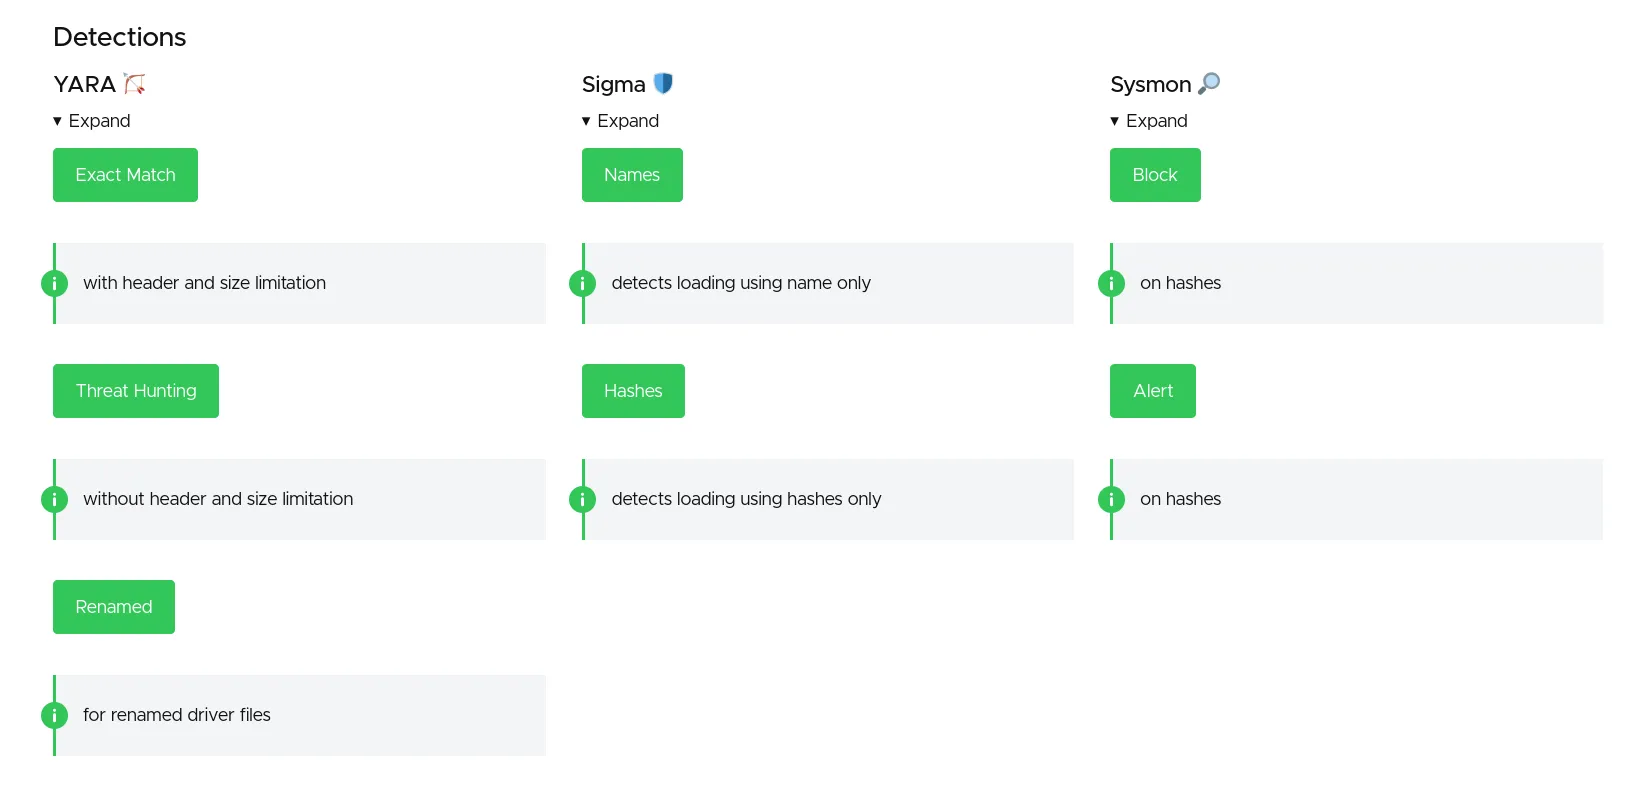 magicsword-io/loldrivers
Curated database of vulnerable and malicious Windows drivers with YARA, Sigma, ClamAV, and Sysmon detection rules for proactive threat hunting and…
 ljagiello/ctf-skills
Agent skills for solving CTF challenges - web exploitation, binary pwn, crypto, reverse engineering, forensics, OSINT, and more
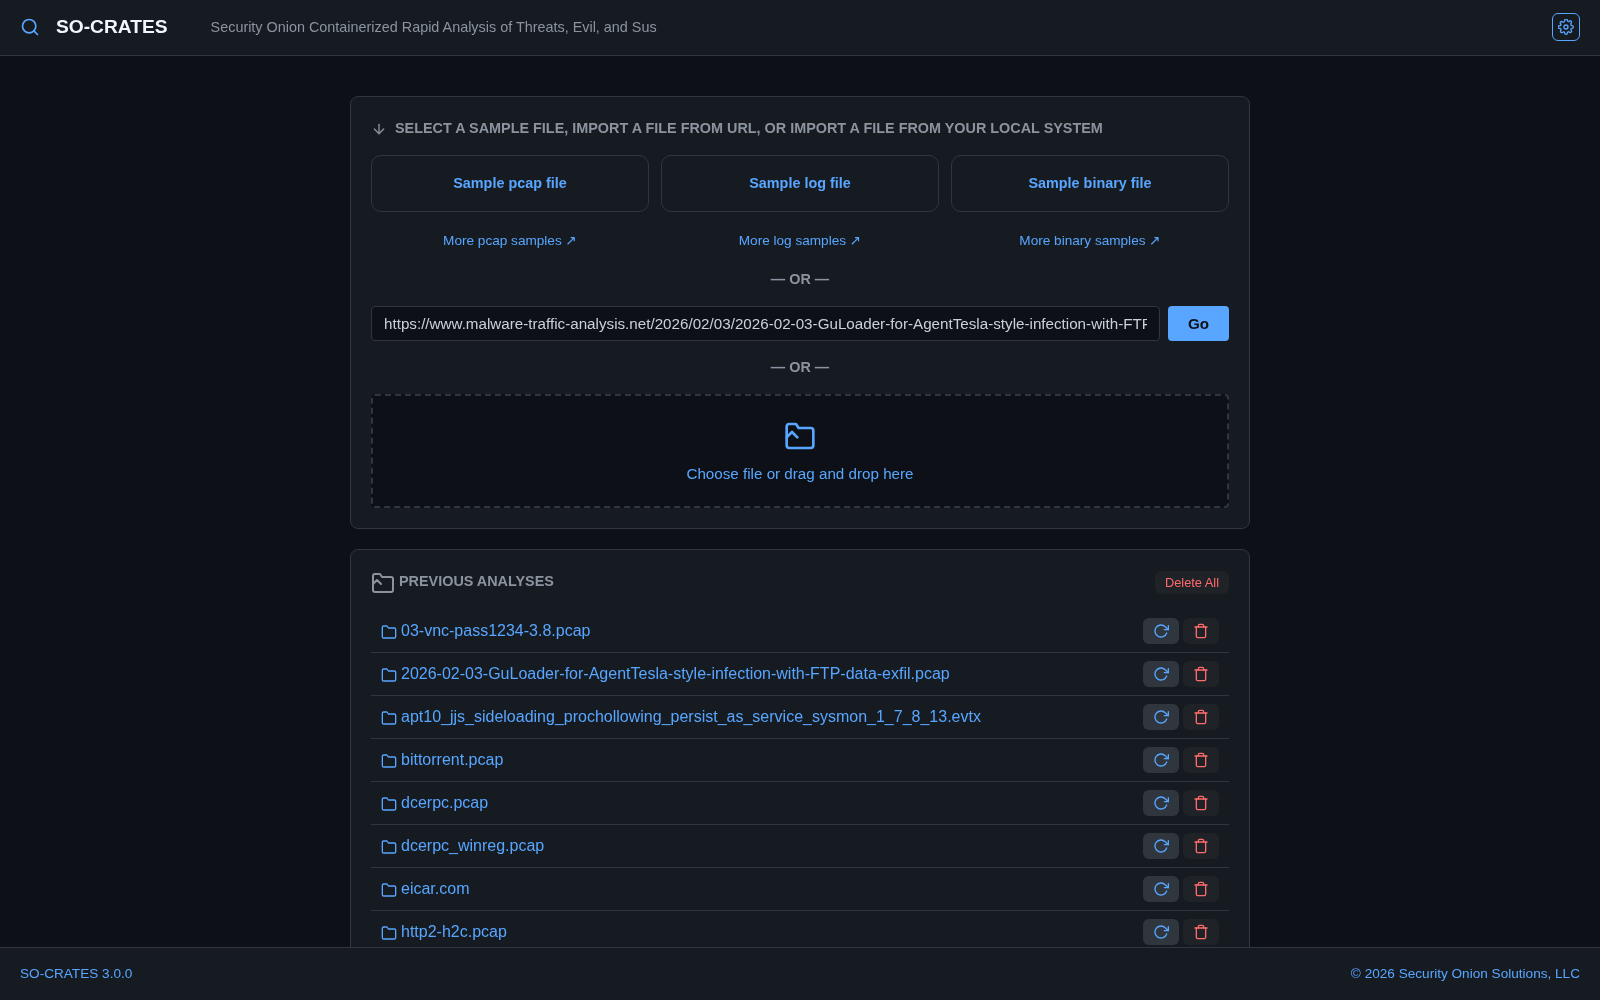 dougburks/so-crates
SO-CRATES: Security Onion コンテナ化による脅威、悪意、怪しいものの迅速分析

 piotr-kniaz/eslockdecryptor
ES File Explorerで暗号化されたファイル(.eslock)を復元および復号するためのツール
 circl/ail-framework
AILフレームワーク - 情報漏洩分析フレームワーク。プロジェクトは https://github.com/ail-project に移動しました。
 cisagov/malcolm
コンテナ化されたネットワークトラフィック解析スイート。PCAP、Zeekログ、Suricataアラートを取り込み、OpenSearch DashboardsとArkimeを介して自動正規化、エンリッチメント、相関付けを行います。