
Skip to content
KitploitKITPLOIT
StrumentiExploitsBlog
Log in
Invia
StrumentiExploitsBlog
Invia

Strumenti di Hacking, PenTest e Cybersecurity per il tuo Arsenale di Sicurezza!

Kitploit è una directory di strumenti di hacking, cybersecurity e pentesting. Scopri gli ultimi aggiornamenti dei progetti per trovare vulnerabilità, analizzare sistemi, automatizzare i test e rafforzare la tua sicurezza.

FeedContattoPrivacy© 2026 Kitploit

Directory degli strumenti

Categorie

Vedi tutte le categorie
Loading categories
hackingtool — All-in-one penetration testing toolkit aggregating 185+ tools across 20 categories including information gathering, web & wireless attacks, phishing, exploitation, forensics, and cloud security. | Kitploit
Strumenti/GitHubGitHub/z4nzu/hackingtool
Penetration Testing FrameworksPayload GenerationExploitationReverse EngineeringForensicsInformation GatheringPost-ExploitationPhishingWeb SecurityWireless SecurityPenetration TestingCloud Security
GitHubz4nzu/hackingtool

hackingtool

All-in-one penetration testing toolkit aggregating 185+ tools across 20 categories including information gathering, web & wireless attacks, phishing, exploitation, forensics, and cloud security.

Il repository upstream non è stato trovato durante l'ultimo controllo aggiornamenti di Kitploit. Questa scheda resta disponibile come riferimento, ma è stata rimossa dai risultati di ricerca.
78.9k8.9k6767 giorni faRevisionato da Kitploit
Repository Deleted

Più Popolari

Vedi tutti →

Scopri gli strumenti più utilizzati dalla nostra community.

Esplora tutti gli strumenti

Sfoglia la nostra collezione di strumenti

Vedi tutti gli strumenti →
Condividi
Contenuto non disponibile nella lingua richiesta. Visualizzazione della versione inglese.
HackingTool

AI-guided, all-in-one toolkit for authorized security testing

219 curated tools across 21 categories — recon, OSINT, web, wireless, phishing, forensics, post-exploitation and more — with an AI layer that turns plain English into the right tool and the exact command.

Built for penetration testers · red teamers · blue-team/SOC and DFIR analysts · OSINT researchers · bug-bounty hunters · CTF players · security researchers and students — all working legally, on systems they own or are authorised to test.

Sponsored by
WebVetted Intelligence - OSINT & Recon Platform

Go beyond manual recon. WebVetted turns an email, phone or username into a complete identity investigation with deep OSINT enrichment, breach intel, AI analysis, and an interactive identity graph.

Start an Investigation →


Z4nzu/hackingtool | Trendshift Z4nzu/hackingtool | Trendshift daily Z4nzu/hackingtool | Trendshift weekly


License Python Stars Forks Issues Last Commit Sponsor


Install Now  How to Use  Tool Catalog  Sponsor


Contents

  • Why hackingtool
  • Tool Categories
  • Installation
    • From source with pipx (recommended)
    • For development
    • Docker
    • Optional runtimes
  • Quick Commands
    • Command reference
  • Features
    • 🔎 /find — a tool for a need you don't have yet
    • 🎯 /goal — plan an objective, run it one step at a time
    • 🧠 Recommendations — say what you want in plain English
    • 🏷 Tags and search
    • ▶ Background panes (tmux)
    • ⚙ Settings and the AI layer
    • 📋 Headless engagements
  • Documentation
  • Contributing
  • Support & Sponsor
  • Social

Why hackingtool

  • 🧠 AI-guided workflow — describe what you want ("find subdomains of example.com") and it maps your intent to the right tools, hands you the exact documented command, plans an objective step by step, then summarizes findings and drafts an engagement report. Bring your own key or run a local model — nothing auto-executes and nothing is fabricated.
  • 🗂 219 curated tools, one interactive console — type to search every tool, then install and run across 21 categories without hunting down Git repos; a fixed tag taxonomy (63 tags in use) makes every tool discoverable.
  • 🔎 It knows what it doesn't have — /find searches your catalog first, then the GitHub API, and shows real maintained projects with the reason each was ranked.
  • 🛡 Safe by default — standard installs, no curl | bash, downloads pinned + SHA-256 verified, list-form subprocess, no forced sudo, and signed releases with an SBOM.
  • 🎯 For the whole spectrum — red team, blue team, OSINT, bug bounty, CTF/THM, forensics/IR — all on authorized targets only.
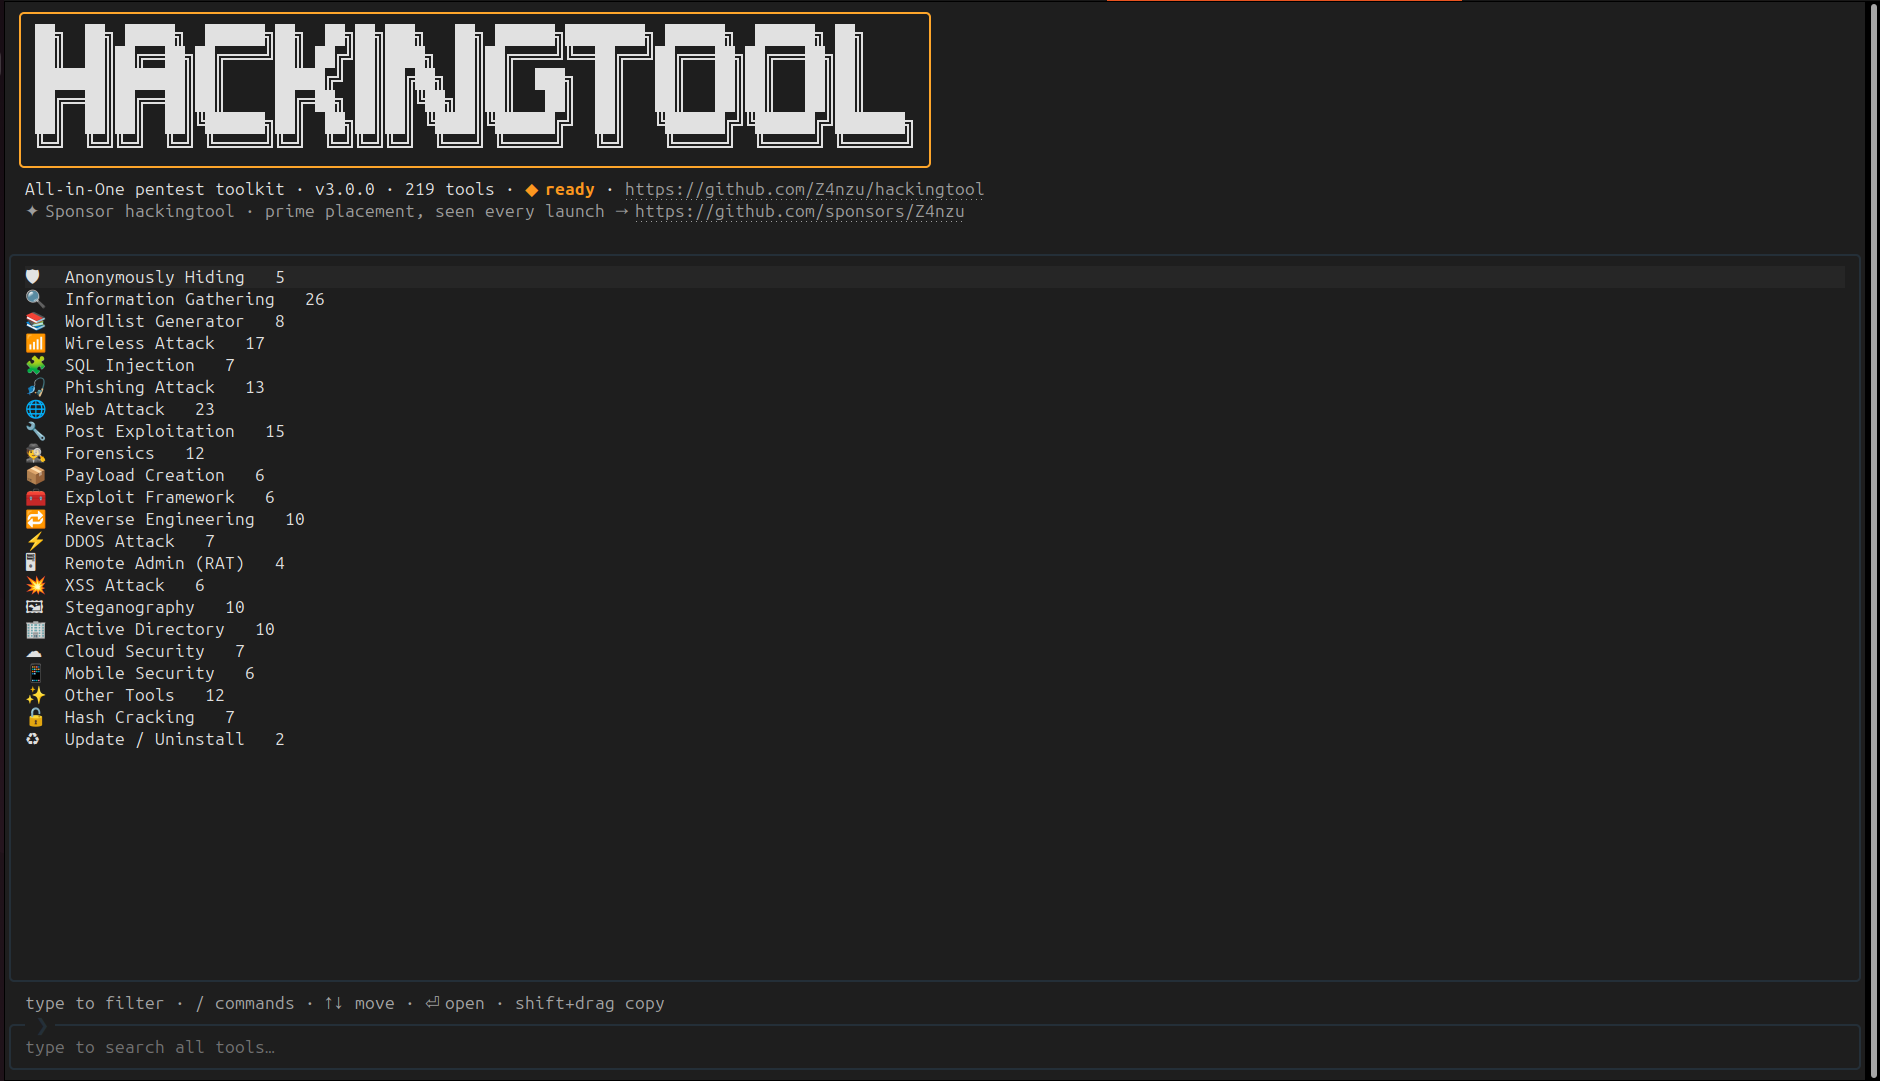
hackingtool interactive TUI: categories with live tool counts, type to search all tools, / opens the command palette
The interactive console on launch — browse categories, type to search every tool, and / opens the command palette.

Tool Categories

219 tools across 21 categories — the full list, with links and tags, is in docs/TOOLS.md.