 mafifrizi/tanuki
Tactical Identity Operator for Linux & Hybrid Active Directory

Non-Human Identity & Hybrid Active Directory Operator for Linux Workloads
Protocol-first, zero root privileges, zero host configuration footprint, zero noise.


Overview • Quick Start • Commands • Architecture • Validation • Lineage & Credits
Modern cloud-native and on-premise environments increasingly run Linux workloads (Kubernetes pods, AI coding agents, CI/CD runners, containerized batch workers) that must authenticate to enterprise Active Directory domains without a full domain join, Kerberos daemons (sssd / winbind), or root privileges.
Tanuki is a protocol-first Active Directory operator built for unprivileged Linux userspace. It runs the full Purple Team lifecycle under human-in-the-loop control: pre-flight triage, cryptographic ticket negotiation, quantitative privilege tiering, closed-loop self-healing, and forensic audit telemetry. It is also agent-operable, exposing a structured skill manifest so tools like Claude Code, Cursor, and Google Antigravity can drive it one deterministic step at a time.
Highlights:
#![forbid(unsafe_code)].sudo, no root, no CAP_SYS_TIME, and no mutation of /etc/krb5.conf or system files.For the full engine comparison and subsystem map, see docs/ARCHITECTURE.md.
# Detects the Rust musl binary or falls back to the Python standard engine
curl -sSfL https://raw.githubusercontent.com/Mafifrizi/tanuki/main/install.sh | bash
# Rust systems core
cargo install --path crates/tanuki-cli

# Python reference engine
pipx install git+https://github.com/Mafifrizi/tanuki.git
git clone https://github.com/Mafifrizi/tanuki.git
cd tanuki
python3 -m tanuki doctor --json
Both engines share the same command surface and flags. Full usage, every flag, and verified LDAPS examples are in docs/USAGE.md.
| Command | Purpose |
|---|---|
tanuki doctor | Pre-flight diagnostics across domain config, credentials, network, and OPSEC telemetry |
tanuki auth | Unprivileged userspace TGT acquisition with in-memory clock skew healing |
tanuki tgs | Kerberos service ticket acquisition for a target SPN |
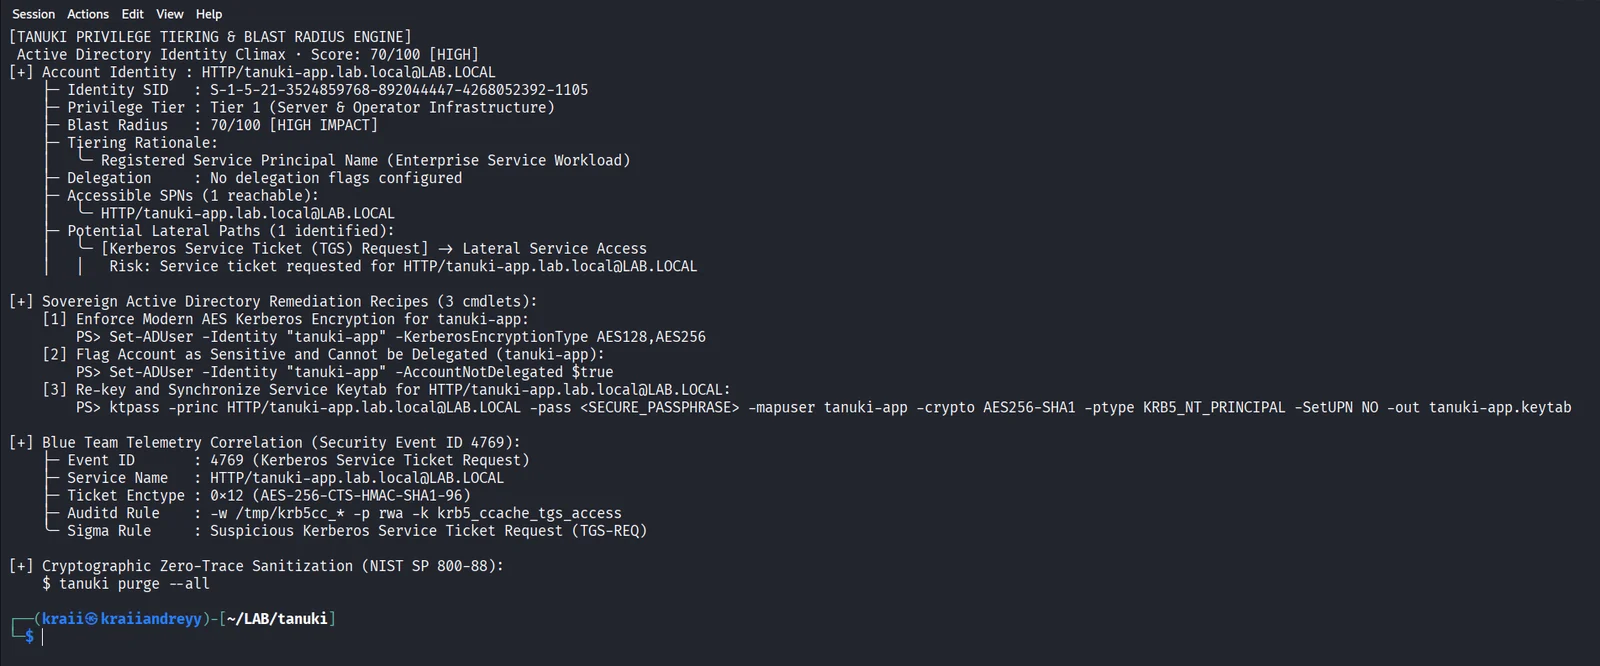
tanuki blast | Quantitative blast radius scoring, privilege tiering, and PowerShell remediation recipes |
tanuki ldap | Unprivileged LDAP recon (--query spn | asreproast | rbcd | shadow | unconstrained | all) |
tanuki adcs | Passive AD CS template scanner for ESC1 through ESC11 |
tanuki config | Zero-DNS unprivileged krb5.conf generator targeting the KDC by IP |
tanuki fix | Idempotent closed-loop remediation (--dry-run to preview) |
tanuki purge | NIST SP 800-88 cryptographic memory and credential-cache zeroization |
tanuki skill | Export the agent skill manifest (--json for machine-actionable schema) |
Add --json to any command for structured output. Run tanuki -i for the interactive wizard.
Tanuki follows a fixed 5-rung tactical decision ladder to prevent privilege escalation loops, reduce authentication noise, and keep every action forensically defensible. The model is documented in references/tactical_ladder.md.
| Rung | Action | Description |
|---|---|---|
| 0 | DIAGNOSE | Pre-flight audit of credentials, enctypes, and network paths |
| 1 | AUTHENTICATE | Userspace AS-REQ TGT negotiation with clock skew tolerance |
| 2 | AUTHORIZE | TGS service ticket acquisition for verified SPN endpoints |
| 3 | ASSESS | Quantitative blast radius calculation and tier scoring |
| 4 | PURGE | Cryptographic memory zeroization (NIST SP 800-88) |
Tanuki is validated against live hybrid infrastructure: an unprivileged Kali workstation (UID 1000) connecting directly to a Windows Server 2022 Domain Controller (DC01.lab.local), proving each rung end to end through to Blue Team forensic telemetry on the DC. It also ships 500+ Python unit tests and 39 Rust tests (library plus integration), all green.
See the full milestone walkthrough with terminal proofs in docs/VALIDATION.md.
Tanuki is engineered by Muhammad Afif Rizi (@Mafifrizi) and Muhamad Dian Alvito.
Tanuki draws inspiration and tradecraft from two foundational projects:
