
cve-lite-cli v1.30.0
Veloce, adatto agli sviluppatori, scanner di vulnerabilità per dipendenze JS/TS con scansione locale dei lockfile, corrispondenza OSV, visibilità diretta vs transitiva, --fix, output JSON e indicazioni pratiche per la remediation.
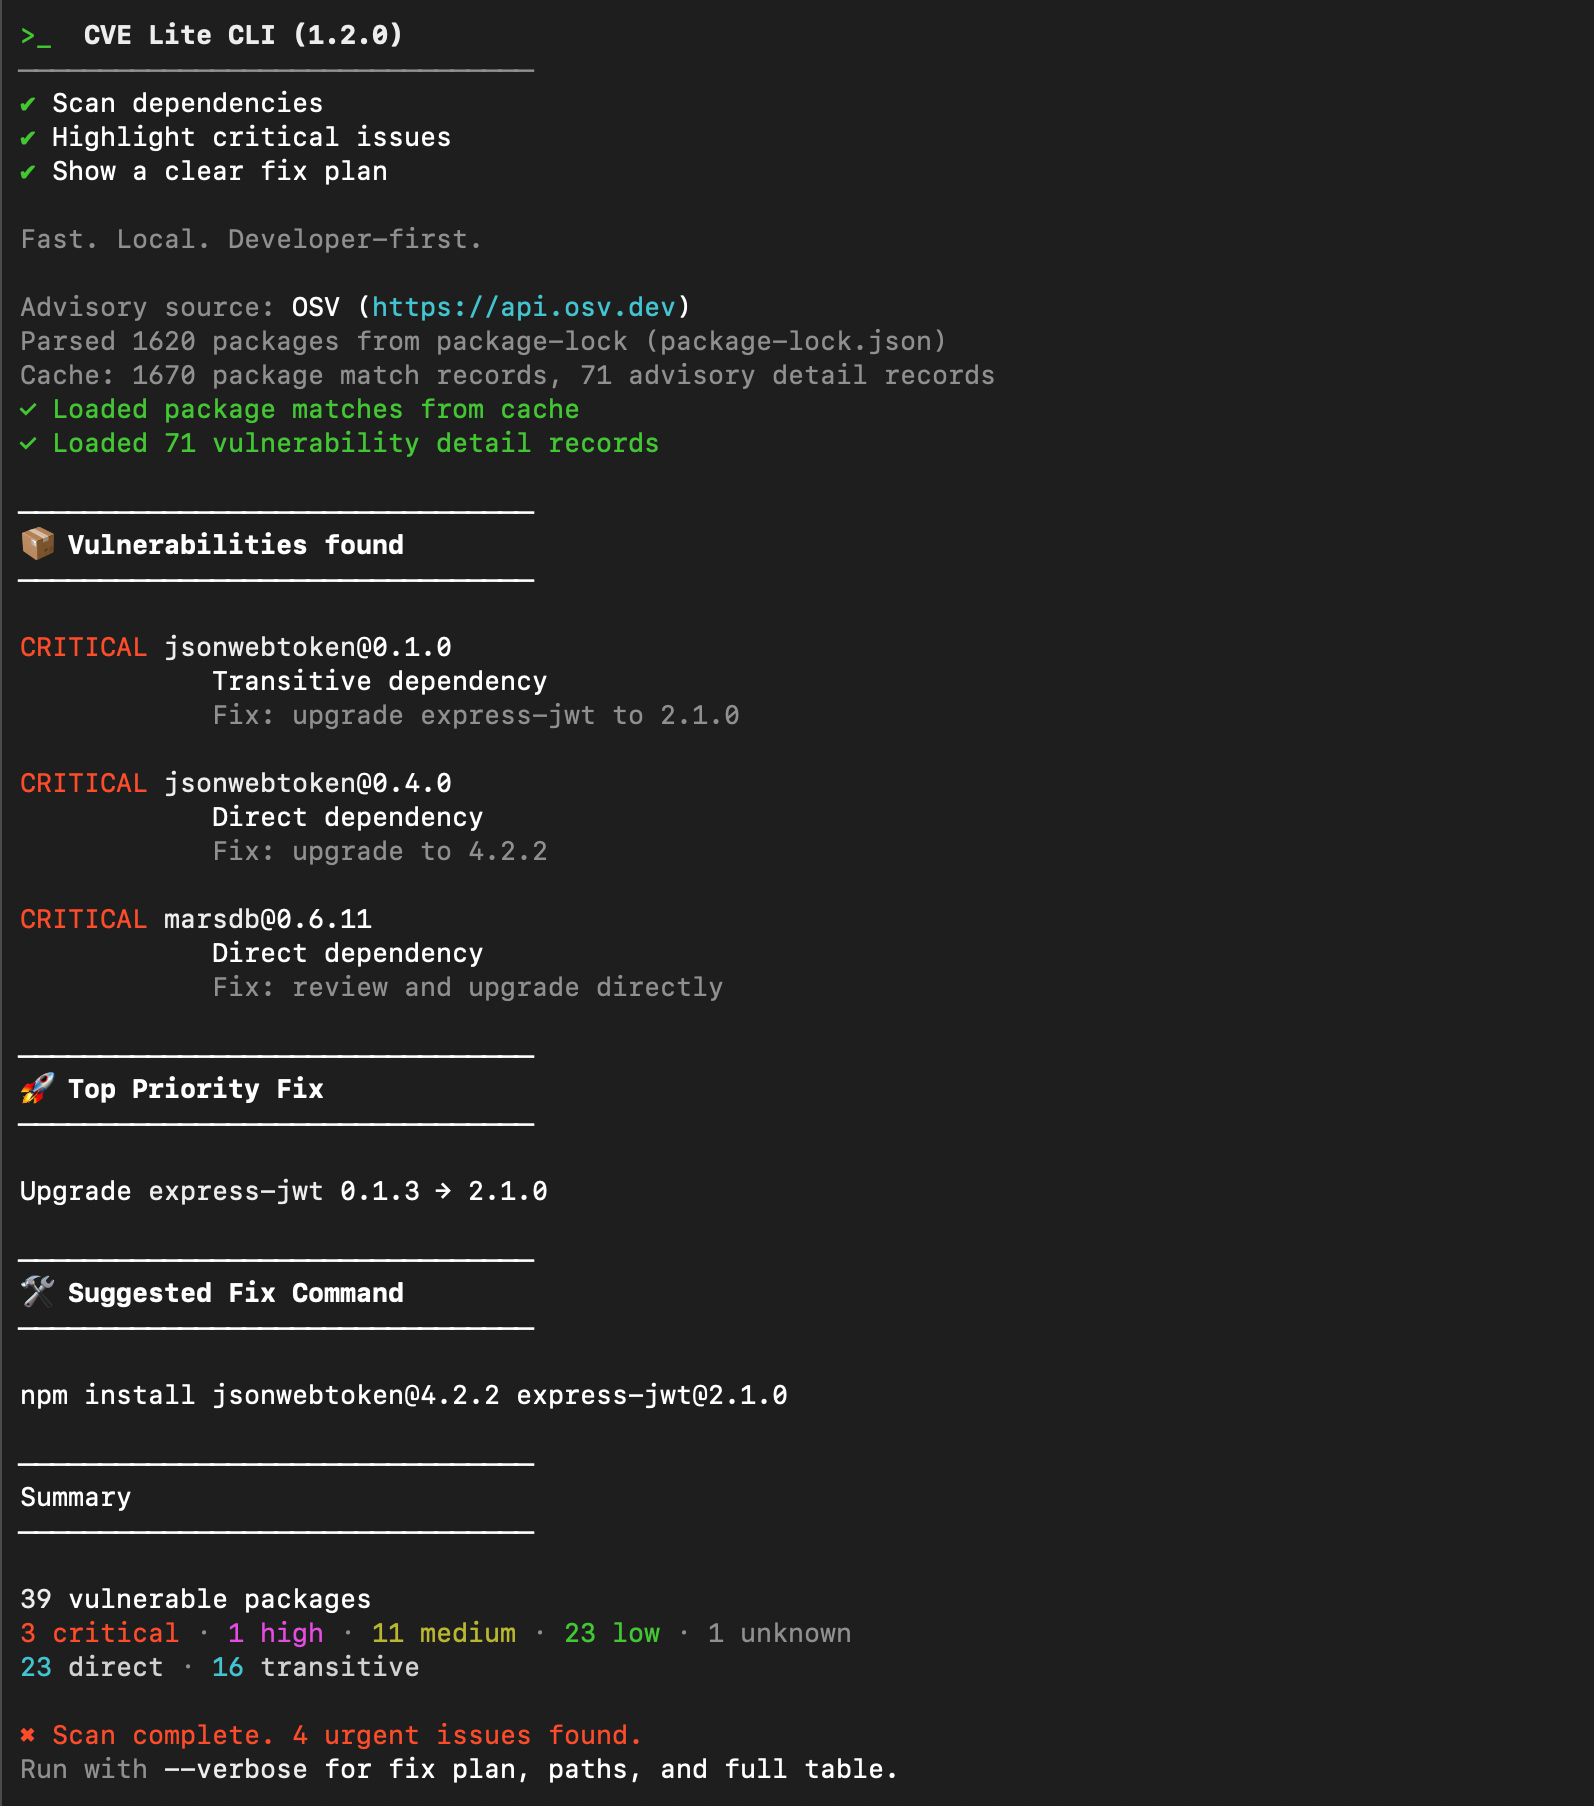
Most tools tell you what's wrong. CVE Lite CLI tells you what to run.



CVE Lite CLI
🏆 Officially recognized as an OWASP Lab Project
Vulnerability scanning that starts in your terminal and fits cleanly into CI.
Scan your lockfile, get copy-and-run fix commands, and ship clean code.
Scan. Understand. Fix.
| 🏆 | 🎯 | 🔒 |
| OWASP Lab Project Peer-reviewed by the org behind the OWASP Top 10: the security standard followed by millions of developers |
Remediation-first Validated fix commands + parent-aware transitive guidance: not just CVE IDs |
Runs locally Nothing leaves your machine: not your code, not your dependency tree |
🏆 Featured on GitHub Open Source Friday · Ranked #5 in Help Net Security's 20 open-source security tools · OpenSSF Best Practices
Covered by The Register · CSO Online · SecurityWeek · SD Times · DevOps.com · ReversingLabs
Used by
SolidJS,
Valibot,
the Government of British Columbia as a required merge gate, and
the Government of France.
In public repositories in France, Canada, Germany, Thailand and China. See who uses it.
⚡ One command. No account, no API key, nothing leaves your machine.
npx cve-lite-cli .
→ Quick Start
Quick Start • Usage • Screenshots • HTML Report • Compare • Roadmap • Contributing • Join Slack
Package Managers
 npm |
 pnpm |
 Yarn |
 Bun |
Quick start
npm install -g cve-lite-cli
cve-lite /path/to/project
Or one-off with npx:
npx cve-lite-cli /path/to/project
No account. No configuration. No source code leaves your machine.
Note: CVE Lite CLI includes
better-sqlite3, a native SQLite binding used for the local advisory database. During installation, npm may download a prebuilt binary or compile one from source. This can produce extra console output: it is expected and is not CVE Lite CLI itself running an install script. See Dependency footprint for details.