 owasp/cve-lite-cli
Fast, developer-friendly JS/TS dependency vulnerability scanner with local lockfile scanning, OSV matching, direct vs transitive visibility, --fix, JSON output, and practical remediation guidance.

*Most tools tell you what's wrong. CVE Lite CLI tells you what to run.*
[](https://owasp.org/cve-lite-cli)
[](https://www.npmjs.com/package/cve-lite-cli)
[](https://www.npmjs.com/package/cve-lite-cli)
[](https://www.npmjs.com/package/cve-lite-cli)
[](https://github.com/OWASP/cve-lite-cli/actions)
[](https://github.com/marketplace/actions/cve-lite-cli)
[](https://github.com/OWASP/cve-lite-cli/blob/main/LICENSE)
[](https://github.com/OWASP/cve-lite-cli)
[](https://www.bestpractices.dev/projects/12731)
<div align="center">
<a href="https://owasp.org/cve-lite-cli">
<img src="https://raw.githubusercontent.com/OWASP/cve-lite-cli/main/assets/logos-combined.svg" alt="CVE Lite CLI - An OWASP Foundation Project" width="500"/>
</a>
<h1>CVE Lite CLI</h1>
**🏆 Officially recognized as an [OWASP Lab Project](https://owasp.org/cve-lite-cli)**
<p>Vulnerability scanning that starts in your terminal and fits cleanly into CI.<br/>Scan your lockfile, get copy-and-run fix commands, and ship clean code.</p>
<strong>Scan. Understand. Fix.</strong>
<br/>
<table>
<tr>
<td align="center" width="33%">🏆</td>
<td align="center" width="33%">🎯</td>
<td align="center" width="33%">🔒</td>
</tr>
<tr>
<td align="center" width="33%" valign="top"><strong>OWASP Lab Project</strong><br/><sub>Peer-reviewed by the org behind the OWASP Top 10:<br/>the security standard followed by millions of developers</sub></td>
<td align="center" width="33%" valign="top"><strong>Remediation-first</strong><br/><sub>Validated fix commands + parent-aware<br/>transitive guidance: not just CVE IDs</sub></td>
<td align="center" width="33%" valign="top"><strong>Runs locally</strong><br/><sub>Nothing leaves your machine: not your<br/>code, not your dependency tree</sub></td>
</tr>
</table>
<br/>
<p>
🏆 <strong>Featured on <a href="https://www.youtube.com/watch?v=_Mmf3DLVuOQ">GitHub Open Source Friday</a></strong> ·
<strong>Ranked #5</strong> in <a href="https://www.helpnetsecurity.com/2026/07/08/20-latest-open-source-cybersecurity-tools/">Help Net Security's 20 open-source security tools</a> ·
<strong><a href="https://www.bestpractices.dev/projects/12731">OpenSSF Best Practices</a></strong>
</p>
<p>
Covered by
<a href="https://www.theregister.com/security/2026/06/23/sniff-out-stale-ai-override-advice-with-this-open-source-cli/5259853"><strong>The Register</strong></a> ·
<a href="https://www.csoonline.com/article/4176701/as-ai-speeds-coding-cve-lite-cli-keeps-security-deliberately-ai-free.html"><strong>CSO Online</strong></a> ·
<a href="https://www.securityweek.com/owasp-incubator-project-helps-developers-find-and-fix-vulnerable-dependencies-in-seconds/"><strong>SecurityWeek</strong></a> ·
<a href="https://sdtimes.com/security/shift-left-how-cve-lite-cli-is-transforming-developer-security/"><strong>SD Times</strong></a> ·
<a href="https://devops.com/owasp-adopts-cve-lite-cli-to-boost-dependency-scanning/"><strong>DevOps.com</strong></a> ·
<a href="https://www.reversinglabs.com/blog/cve-lite-cli"><strong>ReversingLabs</strong></a>
</p>
<p>
<sub>Used by
<a href="https://github.com/solidjs/solid/blob/main/.github/workflows/cve-lite.yml"><strong>SolidJS</strong></a>,
<a href="https://github.com/open-circle/valibot/blob/main/.github/workflows/security.yml"><strong>Valibot</strong></a>,
<a href="https://github.com/bcgov/nr-waste-plus/blob/main/.github/workflows/analysis.yml"><strong>the Government of British Columbia</strong></a> as a required merge gate, and
<a href="https://github.com/refugies-info/karfur/blob/dev/package.json"><strong>the Government of France</strong></a>.<br/>
In public repositories in France, Canada, Germany, Thailand and China. <a href="https://owasp.org/cve-lite-cli/who-uses">See who uses it</a>.</sub>
</p>
<br/>
<p>
⚡ <strong>One command. No account, no API key, nothing leaves your machine.</strong>
<code>npx cve-lite-cli .</code>
<a href="#quick-start"><strong>→ Quick Start</strong></a>
</p>
<br/>
<p>
<a href="#quick-start">Quick Start</a> •
<a href="#usage">Usage</a> •
<a href="#what-it-looks-like">Screenshots</a> •
<a href="https://owasp.org/cve-lite-cli/docs/html-report">HTML Report</a> •
<a href="https://owasp.org/cve-lite-cli/docs/comparison">Compare</a> •
<a href="https://owasp.org/cve-lite-cli/docs/roadmap">Roadmap</a> •
<a href="https://github.com/OWASP/cve-lite-cli/blob/main/src/docs/CONTRIBUTING.md">Contributing</a> •
<a href="https://owasp.org/slack/invite">Join Slack</a>
</p>
</div>
---
<div align="center">
**Package Managers**
<table border="0" cellspacing="0" cellpadding="12">
<tr>
<td align="center"><img src="https://cdn.jsdelivr.net/gh/devicons/devicon@latest/icons/npm/npm-original-wordmark.svg" width="48" height="48" alt="npm"/><br/><sub><b>npm</b></sub></td>
<td align="center"><img src="https://cdn.simpleicons.org/pnpm" width="48" height="48" alt="pnpm"/><br/><sub><b>pnpm</b></sub></td>
<td align="center"><img src="https://cdn.jsdelivr.net/gh/devicons/devicon@latest/icons/yarn/yarn-original.svg" width="48" height="48" alt="Yarn"/><br/><sub><b>Yarn</b></sub></td>
<td align="center"><img src="https://cdn.simpleicons.org/bun" width="48" height="48" alt="Bun"/><br/><sub><b>Bun</b></sub></td>
</tr>
</table>
</div>
---
## Quick start
```bash
npm install -g cve-lite-cli
cve-lite /path/to/project
```
Or one-off with `npx`:
```bash
npx cve-lite-cli /path/to/project
```
No account. No configuration. No source code leaves your machine.
> **Note:** CVE Lite CLI includes [`better-sqlite3`](https://github.com/WiseLibs/better-sqlite3), a native SQLite binding used for the [local advisory database](https://owasp.org/cve-lite-cli/docs/offline-advisory-db). During installation, npm may download a prebuilt binary or compile one from source. This can produce extra console output: it is expected and is not CVE Lite CLI itself running an install script. See [Dependency footprint](#dependency-footprint) for details.
## Usage
```bash
cve-lite /path/to/project # basic scan
cve-lite /path/to/project --verbose # full fix plan with dependency paths
cve-lite /path/to/project --fix # apply validated direct fixes and rescan
cve-lite /path/to/project --fail-on high # exit non-zero on high severity and above
cve-lite /path/to/project --json # JSON output
cve-lite /path/to/project --sarif # SARIF output for GitHub Code Scanning
cve-lite /path/to/project --sbom spdx # SPDX 2.3 SBOM (also: --sbom cyclonedx)
cve-lite /path/to/project --sarif --output reports # write output files into ./reports
cve-lite /path/to/project --report # interactive HTML dashboard
cve-lite /path/to/project --check-overrides # audit override hygiene alongside the CVE scan
cve-lite /path/to/project --check-maintenance # flag CVE-blocking version drag and npm-deprecated direct deps
cve-lite /path/to/project --check-licenses # detect copyleft and unknown licenses alongside the CVE scan
cve-lite advisories sync # sync advisory DB for offline use
cve-lite advisories init # create an empty advisory DB to populate yourself
cve-lite /path/to/project --offline # scan with no runtime API calls
```
For the full flag reference and exit codes see the [CLI Reference guide](https://owasp.org/cve-lite-cli/docs/cli-reference) and [Fix mode guide](https://owasp.org/cve-lite-cli/docs/fix-mode).
## Override hygiene (`overrides`)
`overrides` and `resolutions` are powerful, but they rot. CVE Lite CLI audits them across npm, pnpm, yarn, and bun, catching thirteen classes of problem:
| Rule | What it catches |
|---|---|
| `OA001` | Orphaned target: override for a package no longer in the tree |
| `OA002` | Floating tag: override pinned to a moving tag (`latest`, `next`) |
| `OA003` | Wrong section: override placed in the wrong container |
| `OA004` | Surpassed pin: the rest of the tree has moved past the pin |
| `OA005` | Nested ineffective override that never applies |
| `OA006` | Coupled platform binary: override fights a parent's exact pin |
| `OA007` | Frozen latest: registry has drifted past the pinned version (needs `--check-network`) |
| `OA008` | Materialized vulnerable copy still on disk despite the override |
| `OA009` | Stale floor: override range floor already met by all parent declarations |
| `OA010` | Vulnerable floor: override range admits a known-vulnerable version (needs `--check-network`) |
| `OA011` | Exceeds declared range: override floor can resolve into a major version no parent permits |
| `PD001` | Override-only phantom: package imported in source but only present via an override pin |
| `PD002` | Transitive-only phantom: package imported in source but only present as a transitive dependency |
Use the `overrides` subcommand for a hygiene-only run (no CVE scan, faster, fully offline-capable) with auto-fix support. Use `--check-overrides` to append hygiene results to a regular CVE scan in one pass.
```bash
cve-lite /path/to/project overrides # hygiene only - no CVE scan
cve-lite /path/to/project overrides --fix # hygiene only, auto-fix where possible
cve-lite /path/to/project --check-overrides # CVE scan + hygiene in one pass
```
For the full guide with per-rule examples and CI patterns, see the [Override Hygiene Auditing guide](https://owasp.org/cve-lite-cli/docs/override-hygiene).
## Maintenance risk (`--check-maintenance`)
A CVE scanner tells you a transitive package is vulnerable. It does not tell you *why you can't fix it* - often a direct dependency of yours pins it below the fix, and clearing it needs a breaking major upgrade the scanner never mentions. The DM001 rule surfaces exactly that, plus direct dependencies npm has marked deprecated.
| Signal | Severity | What it means |
|---|---|---|
| Constraint drag | high | A direct dependency blocks a transitive CVE fix behind a major-version upgrade |
| Deprecated on npm | medium | A direct dependency is deprecated - no fix is coming through a normal update |
Packages that have not published in years get a `Last release` context line; release age is informational, not a severity signal on its own.
```bash
cve-lite /path/to/project --check-maintenance # CVE scan + maintenance risk
cve-lite /path/to/project --check-maintenance --fail-on high
```
For the full guide, see the [Maintenance Risk Detection guide](https://owasp.org/cve-lite-cli/docs/maintenance-risk).
## Release cooldown awareness
Package managers added a release cooldown to skip the danger window right after a version is published, when a hijacked release is live but not yet caught (the `chalk`/`debug` compromise sat live for about two hours). CVE Lite CLI reads the cooldown your project already configures and warns when a recommended fix is newer than that window, so it never quietly pushes you onto a version your own package manager would refuse to install.
```
High severity fix commands
⚠ Published 2026-07-01, newer than your configured 365 day release cooldown (.npmrc); your package manager would hold this version - validate before overriding.
> npm install [email protected] (published 2026-07-01)
```
The warning is advisory and on by default (no flag, no exit-code change). It reads `min-release-age` (npm), `minimumReleaseAge` (pnpm), or `npmMinimalAgeGate` (Yarn); it never invents a window.
For the full guide, see the [Release Cooldown Awareness guide](https://owasp.org/cve-lite-cli/docs/release-cooldown).
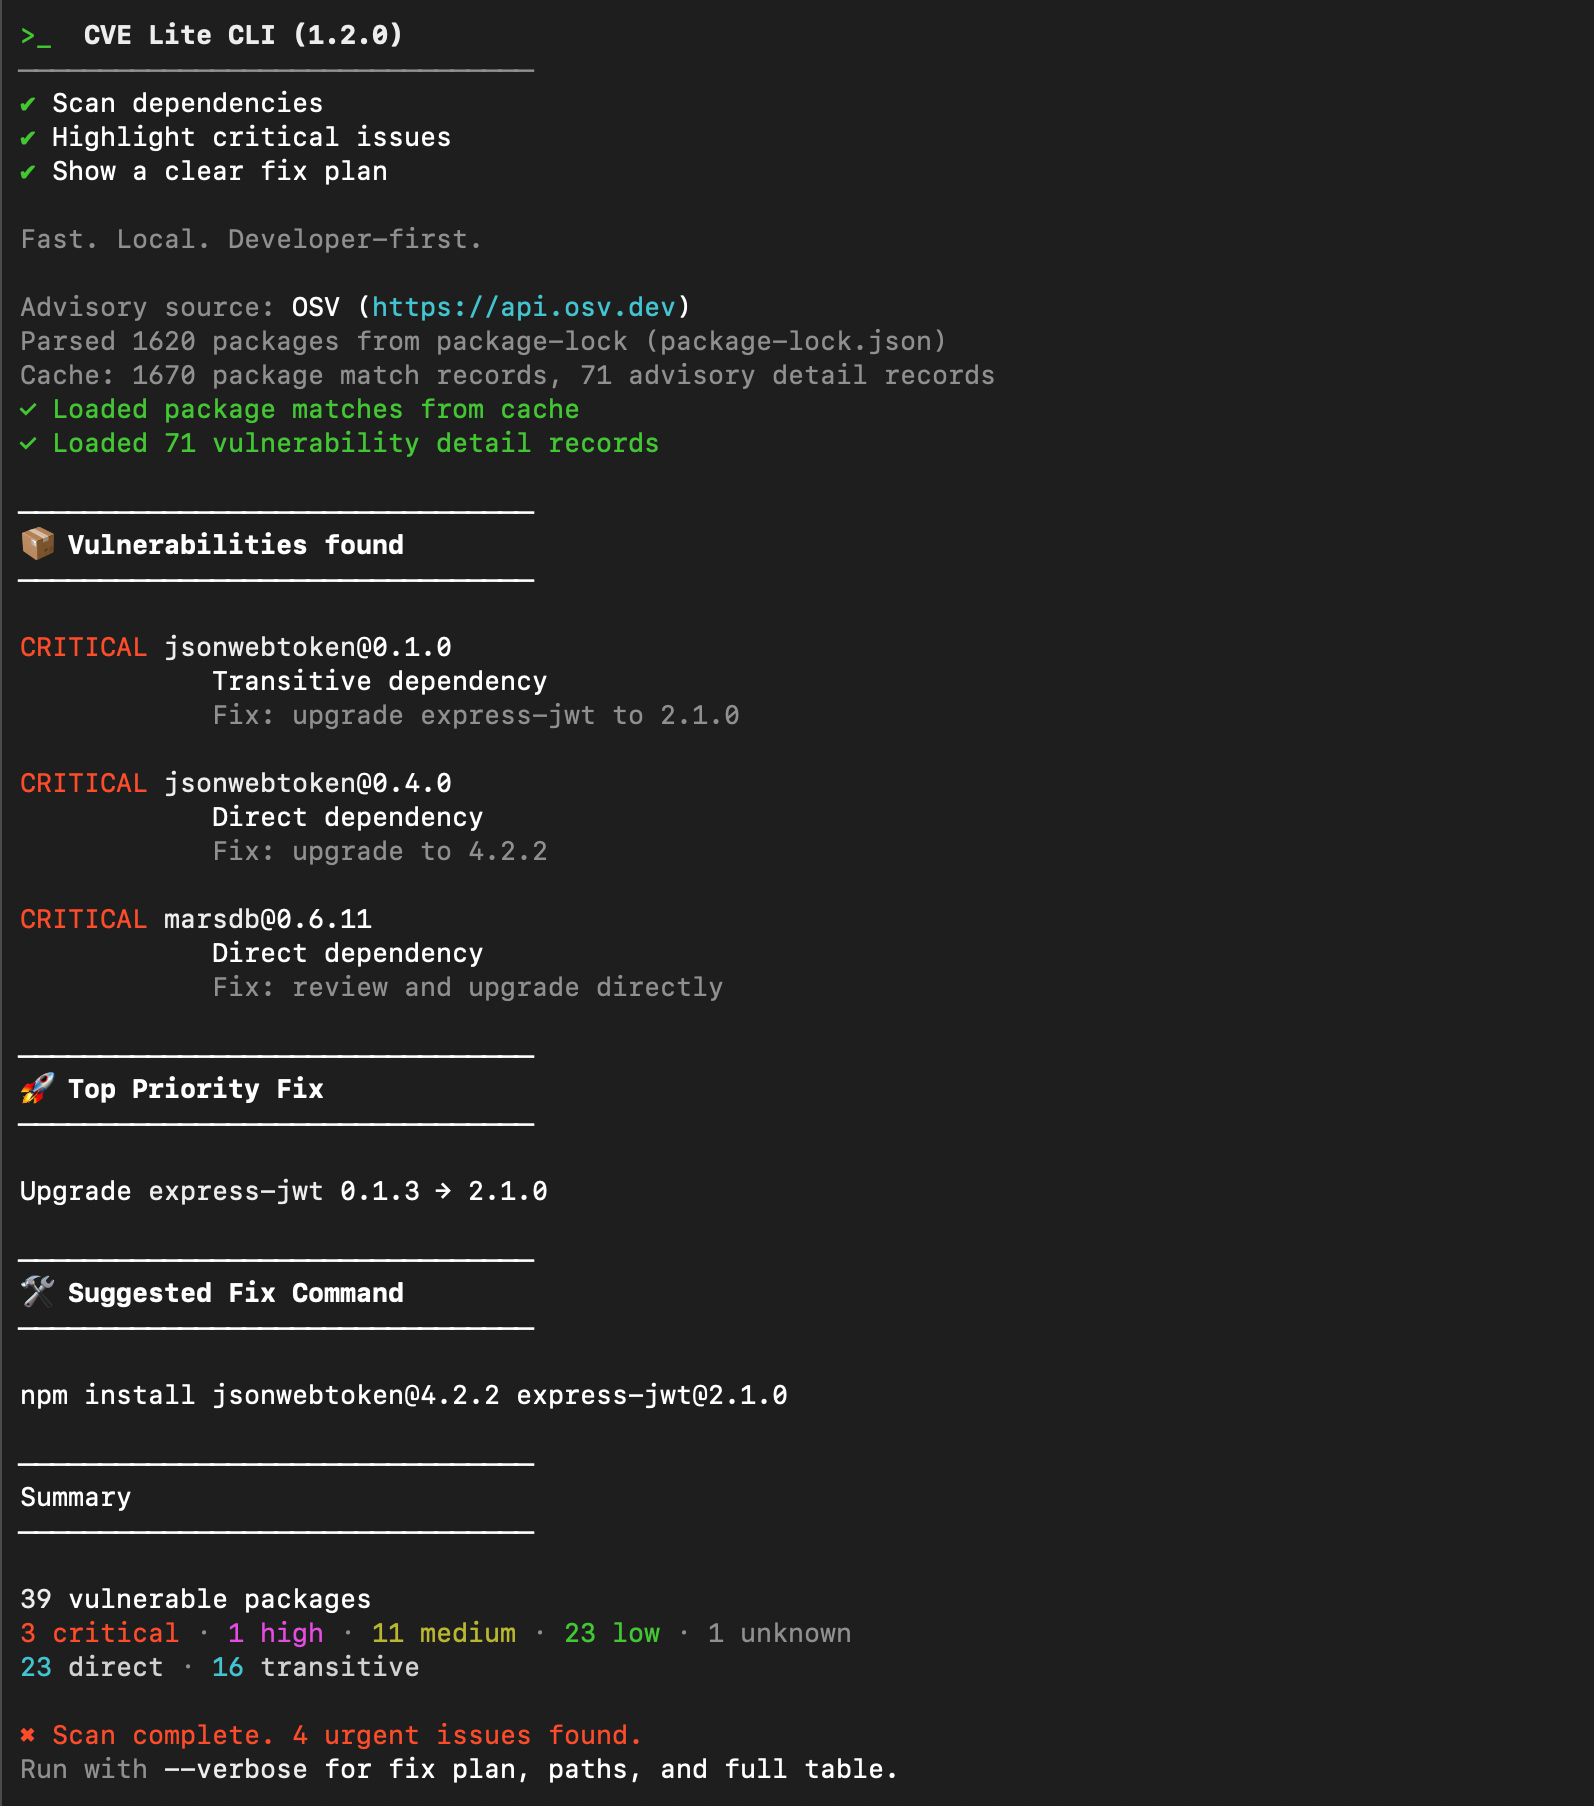
## What it looks like
<table>
<tr>
<th align="center">Terminal output</th>
<th align="center">HTML dashboard (<code>--report</code>)</th>
</tr>
<tr>
<td align="center">
<a href="https://raw.githubusercontent.com/OWASP/cve-lite-cli/main/assets/default-output.png">
<img src="https://assets.kitploit.com/production/public/readmes/7661/b72777dc2a0f00a93892a08c882954c03a39cf968b3dad433827c15b45b1c985.png" alt="CVE Lite CLI terminal output" width="440"/>
</a>
</td>
<td align="center">
<a href="https://raw.githubusercontent.com/OWASP/cve-lite-cli/main/assets/html-report-dashboard.png">
<img src="https://assets.kitploit.com/production/public/readmes/7661/699fd5cde8ad1c1dc3eb845f2bc32d09fd2dc60245042e8f911ac4bf6f946a0c.png" alt="CVE Lite CLI HTML dashboard" width="440"/>
</a>
</td>
</tr>
<tr>
<td align="center"><sub>Default scan output · <a href="https://owasp.org/cve-lite-cli/docs/reading-output">output guide</a></sub></td>
<td align="center"><sub>Generated with <code>--report</code> · <a href="https://owasp.org/cve-lite-cli/docs/html-report">HTML report guide</a></sub></td>
</tr>
</table>
<details>
<summary>Verbose terminal output: includes the full fix plan</summary>
<p align="center">
<a href="https://raw.githubusercontent.com/OWASP/cve-lite-cli/main/assets/verbose-output-1.png"><img src="https://assets.kitploit.com/production/public/readmes/7661/82e8371fbcac0238198f9e34cb0ff48f71e5690d8a991f70f120796eba8c0fba.png" alt="Verbose output part 1" width="280"/></a>
<a href="https://raw.githubusercontent.com/OWASP/cve-lite-cli/main/assets/verbose-output-2.png"><img src="https://assets.kitploit.com/production/public/readmes/7661/9888319df16a2010309888825898f16def2d25c43f41e4c9d9d0df38f774da53.png" alt="Verbose output part 2" width="280"/></a>
<a href="https://raw.githubusercontent.com/OWASP/cve-lite-cli/main/assets/verbose-output-3.png"><img src="https://assets.kitploit.com/production/public/readmes/7661/96a76fc3d204012abd305eb1b52e80fb97caa1efc0dabb32c977e500b53b0c8a.png" alt="Verbose output part 3" width="280"/></a>
</p>
</details>
## Why CVE Lite CLI
Most security tooling is built around pipelines, not developers. Dependabot opens PRs you'll get to eventually. CI scanners block merges after the fact. Dashboards surface lists of CVE IDs with no clear path to fixing them. Developers learn to ignore it.
CVE Lite CLI is built for the moment before you push. It reads your lockfile locally, queries [OSV](https://osv.dev) and the npm registry advisory API, and produces copy-and-run `npm install`, `pnpm add`, `yarn add`, or `bun add` commands, not a list of identifiers. You see which packages are direct versus transitive, get parent-aware upgrade guidance, and can scan offline in restricted environments.
The closer a security tool is to a developer's natural workflow, the more likely it is to be used.
## How it compares
No other free tool combines all of the following: lockfile scanning across npm, pnpm, Yarn, and Bun; parent-aware transitive remediation that tells you which package to upgrade (not just which one is vulnerable); fix version validation before suggesting an upgrade; a fully offline advisory DB for restricted environments; CVE + license compliance scanning in a single pass; SBOM output in both CycloneDX and SPDX with the vulnerability findings attached rather than as a separate inventory step; and an EPSS priority signal that combines CVSS severity with exploitation likelihood into four actionable tiers.
| Capability | CVE Lite CLI | npm audit | OSV-Scanner | Snyk CLI | Socket CLI |
|---|:---:|:---:|:---:|:---:|:---:|
| JS/TS lockfile scanning | ✅ | ✅ | ✅ | ✅ | ✅ |
| npm + pnpm + Yarn + Bun support | ✅ | ❌ | ✅ | ✅ | ✅ |
| No account required | ✅ | ✅ | ✅ | ❌ | ❌ |
| Free to use | ✅ | ✅ | ✅ | ❌ | ❌ |
| [Usage-aware reachability scanning](https://owasp.org/cve-lite-cli/docs/cli-reference#scan-options) | ✅ | ❌ | ❌ | ✅ | ⚠️ |
| [Direct vs transitive visibility](https://owasp.org/cve-lite-cli/docs/reading-output) | ✅ | ⚠️ | ✅ | ✅ | ✅ |
| [Dev vs runtime dependency labelling](https://owasp.org/cve-lite-cli/docs/cli-reference#scan-options) | ✅ | ⚠️ | ❌ | ⚠️ | ❌ |
| [Copy-and-run fix commands](https://owasp.org/cve-lite-cli/docs/how-remediation-works) | ✅ | ❌ | ❌ | ✅ | ⚠️ |
| [Transitive parent update guidance](https://owasp.org/cve-lite-cli/docs/remediation-strategy) | ✅ | ❌ | ⚠️ | ⚠️ | ⚠️ |
| [Suggested remediation plan](https://owasp.org/cve-lite-cli/docs/remediation-strategy) | ✅ | ❌ | ⚠️ | ✅ | ⚠️ |
| [Ratcheting mode (baseline suppression)](https://owasp.org/cve-lite-cli/docs/ratcheting) | ✅ | ❌ | ❌ | ⚠️ | ❌ |
| [Interactive HTML report](https://owasp.org/cve-lite-cli/docs/html-report) | ✅ | ❌ | ❌ | ✅ | ❌ |
| [SARIF / GitHub Code Scanning output](https://owasp.org/cve-lite-cli/docs/sarif) | ✅ | ❌ | ✅ | ✅ | ❌ |
| [JSON output](https://owasp.org/cve-lite-cli/docs/cli-reference#output-options) | ✅ | ✅ | ✅ | ✅ | ✅ |
| [SBOM output with findings attached (CycloneDX + SPDX)](https://owasp.org/cve-lite-cli/docs/spdx) | ✅ | ❌ | ❌ | ⚠️ | ⚠️ |
| [Offline/local advisory DB](https://owasp.org/cve-lite-cli/docs/offline-advisory-db) | ✅ | ❌ | ⚠️ | ❌ | ❌ |
| [Override hygiene auditing](https://owasp.org/cve-lite-cli/docs/override-hygiene) | ✅ | ❌ | ❌ | ❌ | ❌ |
| [Maintenance-risk detection (CVE-fix drag)](https://owasp.org/cve-lite-cli/docs/maintenance-risk) | ✅ | ❌ | ❌ | ❌ | ❌ |
| [License compliance scanning (copyleft / unknown)](https://owasp.org/cve-lite-cli/docs/cli-reference#license-scanning-options) | ✅ | ❌ | ❌ | ⚠️ | ⚠️ |
| [Priority signal: CVSS severity × EPSS exploitation likelihood](https://owasp.org/cve-lite-cli/docs/cli-reference#epss-priority-signal) | ✅ | ❌ | ❌ | ⚠️ | ❌ |
<sub>✅ = built-in strength · ⚠️ = partial or workflow-dependent · ❌ = not a core strength</sub>
The transitive parent guidance is a key difference: CVE Lite CLI avoids recommending direct installs for packages that are only present transitively. For npm lockfiles, it can identify when `npm update <child>` is enough to refresh a known non-vulnerable child within the current parent range, and when the parent package itself needs an upgrade.
For detailed per-tool analysis, see [Comparison with other tools](https://owasp.org/cve-lite-cli/docs/comparison).
## Replace Dependabot with one batched PR
CVE Lite CLI v1.26.0 ships a GitHub Action fix mode that runs on a schedule and opens a **single batched pull request** with all validated dependency upgrades - advisory IDs, before/after finding counts, and OSV-confirmed fix versions included.
Add this file to your repo:
```yaml
# .github/workflows/cve-lite-fix.yml
name: CVE Lite security fixes
on:
schedule:
- cron: '0 6 * * 1' # every Monday at 6am
workflow_dispatch:
permissions:
contents: write
pull-requests: write
jobs:
fix:
runs-on: ubuntu-latest
steps:
- uses: actions/checkout@3d3c42e5aac5ba805825da76410c181273ba90b1 # v7.0.1
with:
ref: ${{ github.event.repository.default_branch }}
- uses: OWASP/cve-lite-cli@v1
with:
fix: 'true'
create-pr: 'true'
```
| | Dependabot | CVE Lite fix mode |
|---|---|---|
| PRs per run | One per package | One batched PR |
| Advisory IDs in PR body | No | Yes (GHSA-xxxx, CVE-xxxx) |
| Fix version validated against OSV | No | Yes |
| Before/after finding counts | No | Yes |
| pnpm / Yarn Berry / Bun | Limited | Full native support |
| OWASP recognition | No | OWASP Lab Project |
[Full Action documentation ->](https://owasp.org/cve-lite-cli/docs/github-action) - for scan-only CI gating see the [CI and Workflow Integration guide](https://owasp.org/cve-lite-cli/docs/workflow-integration).
## Real-world validation
CVE Lite CLI has been evaluated against real open-source projects to verify that it surfaces meaningful issues - including non-obvious transitive vulnerabilities and complex upgrade paths - not just low-signal advisory matches.
- [OWASP Juice Shop](https://owasp.org/cve-lite-cli/docs/case-studies/owasp-juice-shop) - scanning a deliberately vulnerable application with known dependency issues
- [NestJS](https://owasp.org/cve-lite-cli/docs/case-studies/nestjs) - working through a real transitive dependency remediation sequence across a widely-used Node.js framework
- [Visual Studio Code](https://owasp.org/cve-lite-cli/docs/case-studies/vscode) - two direct Anthropic SDK advisories and a high-severity gulp toolchain chain in the VS Code root lockfile
- [Gatsby](https://owasp.org/cve-lite-cli/docs/case-studies/gatsby) - Yarn Classic monorepo with 128 findings, five direct CVEs, and CVE Lite vs `yarn audit` deduplication
- [Analog](https://owasp.org/cve-lite-cli/docs/case-studies/analog) - modern pnpm Angular monorepo with unexpected toolchain vulnerabilities
[20+ case studies across npm, pnpm, Yarn, and Bun projects ->](https://owasp.org/cve-lite-cli/docs/case-studies)
In-repo lockfile fixtures for most projects live under [`examples/`](https://github.com/owasp/cve-lite-cli/blob/main/examples/readme.md) - clone and scan immediately without downloading full upstream checkouts.
These are not demos. They are documented scans against real codebases with real findings, recorded before and after applying fix commands.
If you maintain an open-source JavaScript or TypeScript project and want CVE Lite CLI evaluated on it, open an issue and share the repository.
## Press
- **[Sniff out stale AI override advice with this open source CLI](https://www.theregister.com/security/2026/06/23/sniff-out-stale-ai-override-advice-with-this-open-source-cli/5259853)** - The Register (Thomas Claburn, Senior Reporter), June 2026
- **[Shift left: How CVE Lite CLI is transforming developer security](https://sdtimes.com/security/shift-left-how-cve-lite-cli-is-transforming-developer-security/)** - SD Times (David Rubinstein, Editor-in-Chief), June 2026
- **[As AI speeds coding, CVE Lite CLI keeps security deliberately AI-free](https://www.csoonline.com/article/4176701/as-ai-speeds-coding-cve-lite-cli-keeps-security-deliberately-ai-free.html)** - CSO Online (Shweta Sharma), May 2026
- **[CVE Lite CLI: Open-source dependency vulnerability scanner](https://www.helpnetsecurity.com/2026/05/20/cve-lite-cli-open-source-dependency-vulnerability-scanner/)** - Help Net Security, May 2026
[Full press coverage ->](https://owasp.org/cve-lite-cli/docs/press)
## Recognized by OWASP
OWASP (Open Web Application Security Project) is the globally recognized nonprofit behind the security standards followed by millions of developers worldwide - most notably the [OWASP Top 10](https://owasp.org/www-project-top-ten/), the most widely cited web application security reference in the industry. Organizations from startups to Fortune 500 companies use OWASP guidelines as the foundation of their security programs.
CVE Lite CLI is an [OWASP Lab Project](https://owasp.org/cve-lite-cli) - reviewed and accepted by the OWASP community as a vendor-neutral, open source security tool.
**Where it fits in the OWASP ecosystem:**
CVE Lite CLI fills a specific gap - fast, local-first JS/TS dependency scanning close to release time - that broader OWASP tools are not optimized for:
| Tool | Focus |
|---|---|
| CVE Lite CLI | Lockfile-first, local developer CLI, remediation-focused, JS/TS |
| OWASP Dependency-Check | Multi-language, SAST-style, broader ecosystem |
| OWASP dep-scan | Multi-language and environment, SBOM and cloud-native |
| OWASP Dependency-Track | Platform and SBOM management, not a local CLI |
CVE Lite CLI complements these tools. It is not a replacement for continuous monitoring or full SBOM management - it is the fast local check you run before pushing.
## Community and adoption
CVE Lite CLI runs in public repositories across governments, open-source libraries, companies, and independent developers. The [Who uses CVE Lite CLI?](https://owasp.org/cve-lite-cli/who-uses) page links every adopter to the public file that proves it.
Notable adopters include:
- **SolidJS** - the framework's creator, Ryan Carniato, added CVE Lite CLI to its CI in his own commit. It scans every push and pull request to the main branch and reports results to GitHub Code Scanning
- **Valibot** and **Formisch** - security workflows that run the scan and publish results to GitHub Code Scanning, merged by their creator, Fabian Hiller. Valibot has about 14 million npm downloads a week
- **Government of British Columbia** (Canada) - a required check on every push and pull request in its Waste Plus natural resources application, alongside Trivy and npm audit
- **Government of France** - pre-push scans that block high and critical vulnerabilities in Réfugiés.info, the government's information portal for refugees, and in IA dans l'État, the state's interministerial AI programme
## Teaching and learning
Teach dependency security with CVE Lite Classroom: free, open-source, hands-on exercises covering vulnerability remediation, critical review of AI-assisted fixes, and CI security gates. Includes runnable applications, instructor guides, worked solutions, and grading rubrics, with tracks for npm, pnpm, Yarn, and Bun.
[Explore the classroom exercises](https://github.com/sonukapoor/cve-lite-classroom)
CVE Lite Classroom is a companion project maintained by the author of CVE Lite CLI, separate from the OWASP project.
## Current limitations
- does not detect malicious packages before they appear in advisory data
- does not perform behavioral malware detection or package content analysis
- does not prove exploitability or verify runtime reachability
- does not scan container images, binaries, secrets, or IaC
- does not replace a full application security program
- currently focused on JS/TS dependency scanning
- local advisory sync performance will need continued optimization as the advisory dataset grows
## Dependency footprint
**Runtime:** `yaml` · `yarn-lockfile` · `better-sqlite3` · `fflate` · `semver`
**Dev only:** `@types/node` · `tsx` · `typescript`
This is intentional. Because CVE Lite CLI is a security-oriented tool, runtime dependencies are kept minimal and reviewable.
### Native dependency: `better-sqlite3`
`better-sqlite3` is a native Node.js addon that provides the SQLite binding for CVE Lite CLI's local advisory database. This database powers offline scanning (`--offline`, `--offline-db`), advisory sync (`cve-lite advisories sync`), and air-gapped workflows (`cve-lite advisories init`).
Because it includes compiled C/C++ code, npm must run an install script when installing `better-sqlite3`. During installation:
- **Prebuilt binary available:** `prebuild-install` downloads a prebuilt binary for your platform: fast, though npm may still print a deprecation warning for `prebuild-install` itself ([#519](https://github.com/OWASP/cve-lite-cli/issues/519)).
- **No prebuilt available:** the package falls back to compiling from source using `node-gyp`, which requires a C/C++ toolchain and produces more console output.
This install step belongs to `better-sqlite3`, not to CVE Lite CLI: the project itself does not define any `preinstall`, `install`, or `postinstall` hooks.
**npm install-script permissions:** Depending on your npm version and configuration, npm may prompt you to approve the install script before it runs. This is an npm security feature. Online scanning works even when the install script is blocked: the native binding is loaded lazily and only used by `--offline`, `--offline-db`, `cve-lite advisories sync`, and `cve-lite advisories init`. If you use any of those features, the `better-sqlite3` install script must be allowed to complete.
**npx behavior:** When using `npx cve-lite-cli`, a quiet run does not necessarily mean the install script was skipped. If npm's cache already contains the required prebuilt binary, installation is silent. On a cold cache, the same native install step runs.
## More documentation
- [Troubleshooting guide](https://owasp.org/cve-lite-cli/docs/troubleshooting) - no lockfile found, zero results, slow advisory sync, offline DB errors, `--fix` skipping findings, CI failures
- [Parser Coverage guide](https://owasp.org/cve-lite-cli/docs/parser-coverage) - supported lockfile formats, selection priority, `package.json` fallback, monorepos, private registries
- [Remediation Strategy guide](https://owasp.org/cve-lite-cli/docs/remediation-strategy) - how CVE Lite CLI chooses upgrade targets and parent update paths
- [Release Cooldown Awareness guide](https://owasp.org/cve-lite-cli/docs/release-cooldown) - how CVE Lite CLI reads your package manager's cooldown and warns on fix versions newer than the window you trust
- [SPDX SBOM guide](https://owasp.org/cve-lite-cli/docs/spdx) - SPDX 2.3 output, how findings are attached, NTIA minimum elements, and inventory-only mode
- [CycloneDX SBOM guide](https://owasp.org/cve-lite-cli/docs/cyclonedx) - CycloneDX 1.6 output and Dependency-Track integration
## Security and verification
Every release is signed - GPG-signed git tags for source, Sigstore Artifact Attestations for the release tarball, and ECDSA signatures via the npm registry. Verify with:
```bash
gh attestation verify cve-lite-cli-X.Y.Z.tgz --repo OWASP/cve-lite-cli
npm audit signatures
```
For full details, fingerprints, and the project's threat model, see [SECURITY.md](https://github.com/OWASP/cve-lite-cli/blob/main/SECURITY.md) and the [Security Assurance Case](https://owasp.org/cve-lite-cli/docs/security-assurance-case).
For governance details - roles, decision-making, and dispute resolution - see [CONTRIBUTING.md](https://github.com/OWASP/cve-lite-cli/blob/main/src/docs/CONTRIBUTING.md).
## Contributing
Feedback on output clarity, remediation guidance, ecosystem coverage, and CI usage is especially valuable.
See [CONTRIBUTING.md](https://github.com/OWASP/cve-lite-cli/blob/main/src/docs/CONTRIBUTING.md) to get started.
## Add a badge to your project
If you use CVE Lite CLI in your project, add this badge to your README:
```markdown
[](https://github.com/OWASP/cve-lite-cli)
```
[](https://github.com/OWASP/cve-lite-cli)
## Community and support
For bug reports and feature requests: [GitHub Issues](https://github.com/OWASP/cve-lite-cli/issues)
Helpful feedback includes reproducible bug reports, real-world lockfile edge cases, ideas for clearer output and remediation guidance, and CI or JSON workflow examples.
Using CVE Lite CLI at your company or in your projects? [Share your use case in the community thread](https://github.com/OWASP/cve-lite-cli/discussions/481).
For security-related reporting: [SECURITY.md](https://github.com/OWASP/cve-lite-cli/blob/main/SECURITY.md)
This project follows a [Code of Conduct](https://github.com/OWASP/cve-lite-cli/blob/main/CODE_OF_CONDUCT.md). Please review it before participating.
If CVE Lite CLI helps your release workflow, a [GitHub star](https://github.com/OWASP/cve-lite-cli) helps more developers find it.
## Contributors
Thanks to everyone who helps improve CVE Lite CLI - issues, pull requests, documentation, case studies, and real-world lockfile feedback all count.
<p align="center">
<a href="https://github.com/OWASP/cve-lite-cli/graphs/contributors">
<img src="https://contrib.rocks/image?repo=OWASP/cve-lite-cli" alt="Contributors to OWASP/cve-lite-cli" />
</a>
</p>
<p align="center">
<sub>Avatar grid generated from the <a href="https://github.com/OWASP/cve-lite-cli/graphs/contributors">GitHub contributors graph</a> via <a href="https://contrib.rocks">contrib.rocks</a>.</sub>
</p>
---
[Read more](https://github.com/owasp/cve-lite-cli)
