
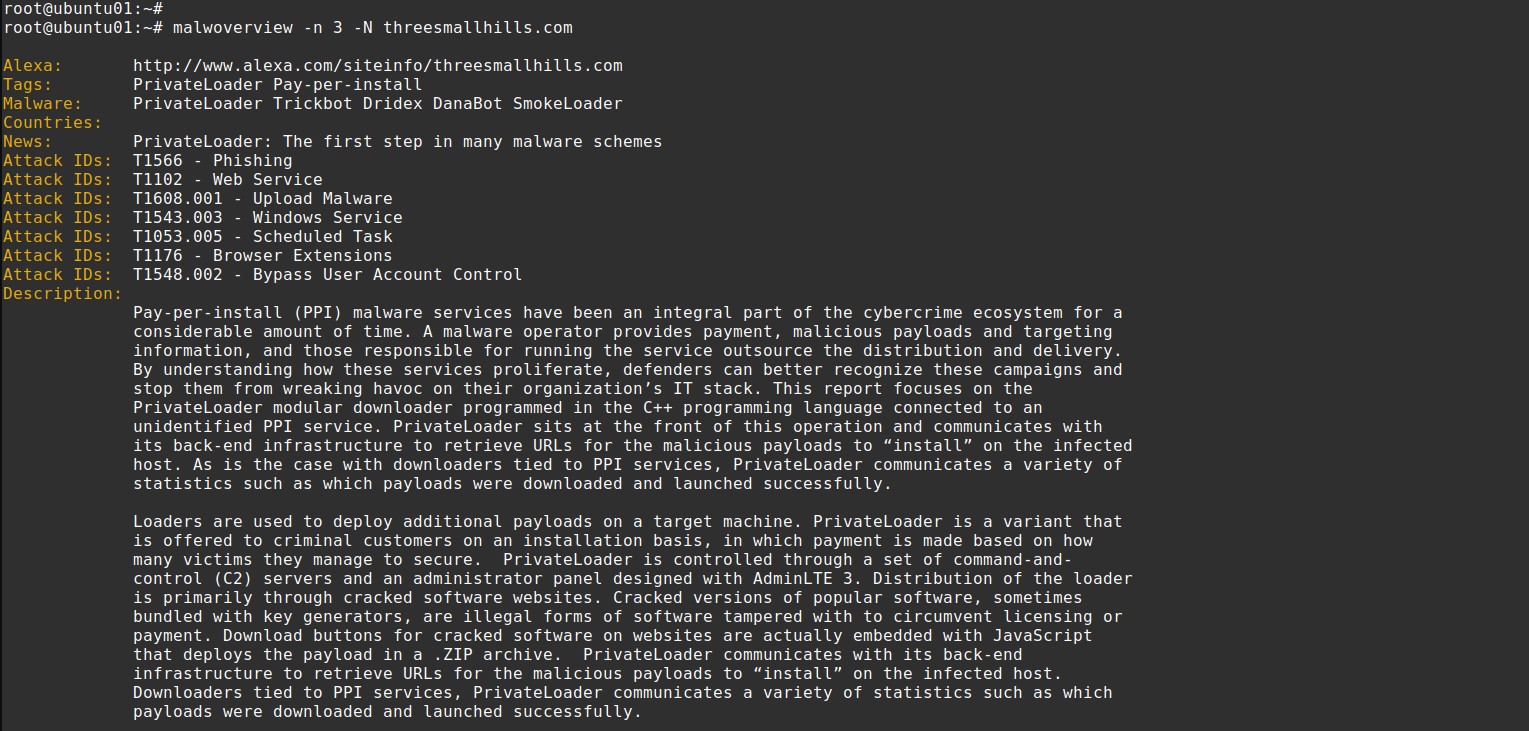
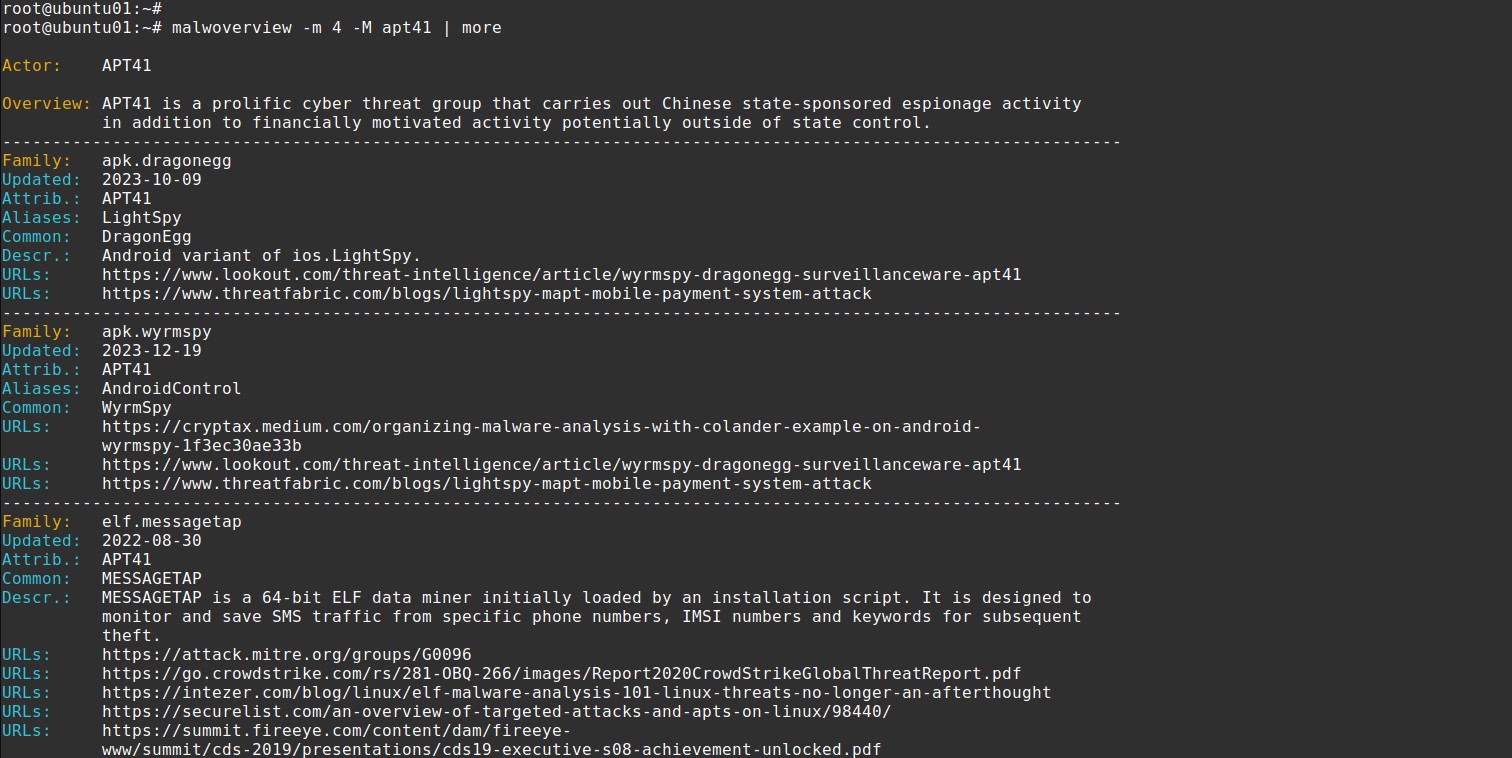
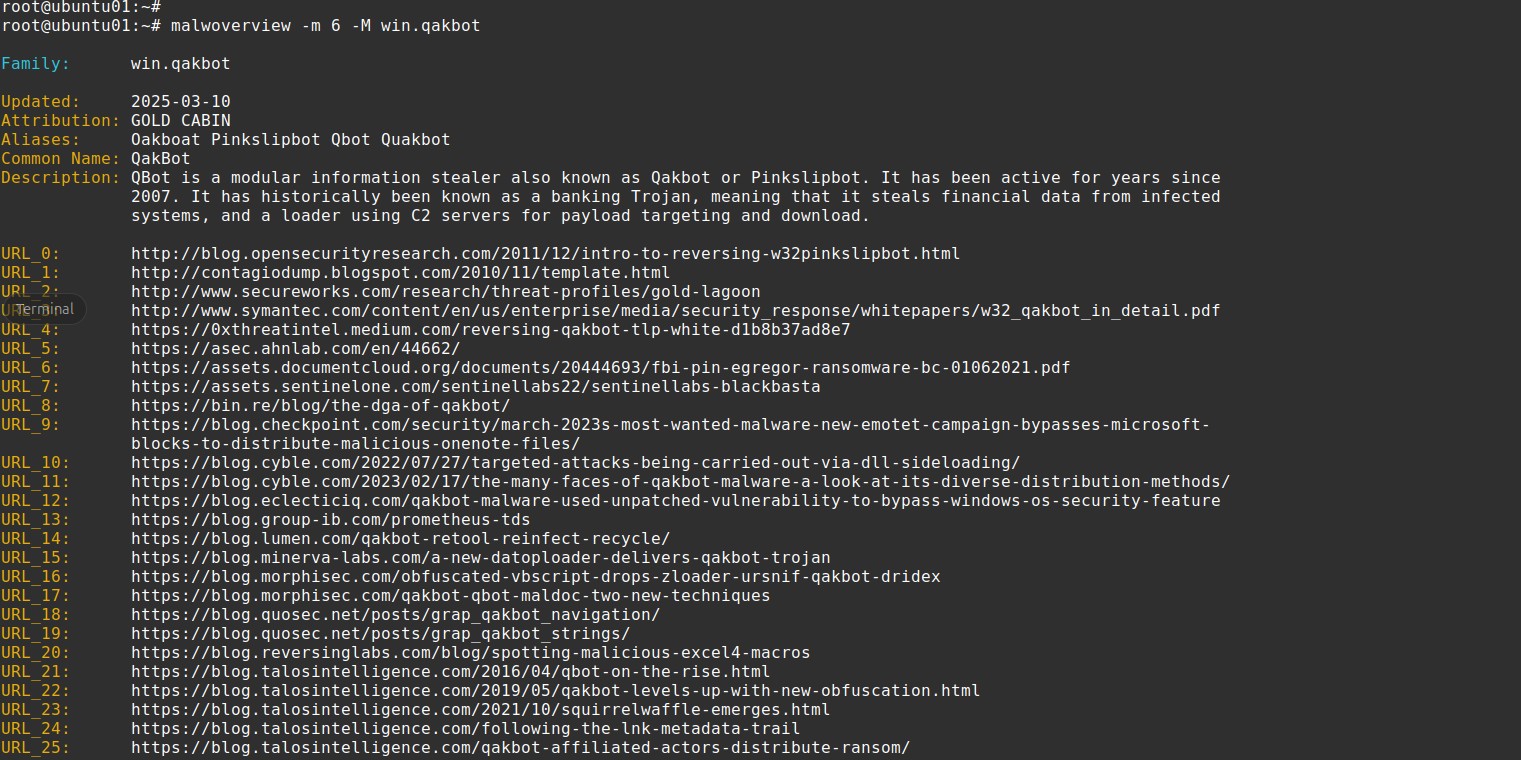
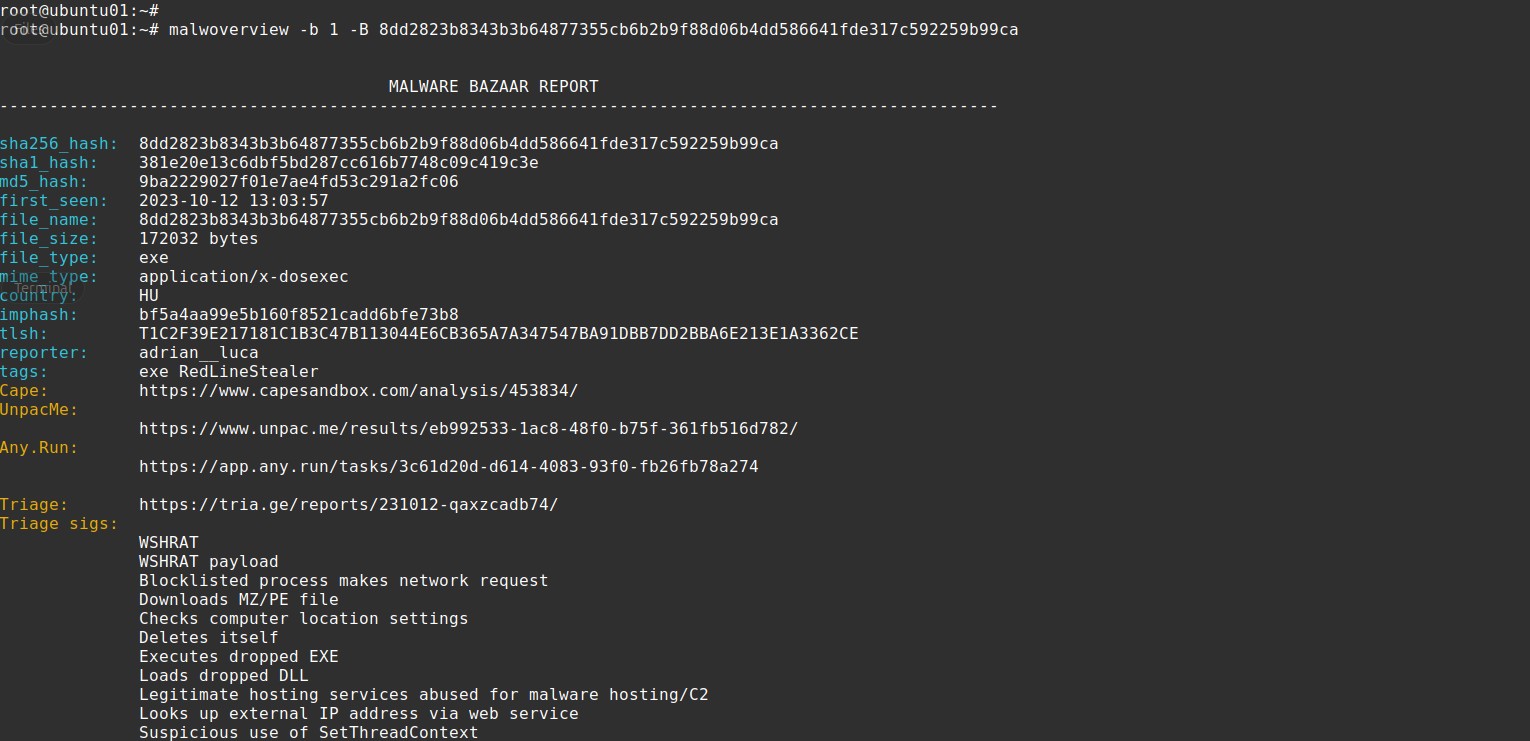
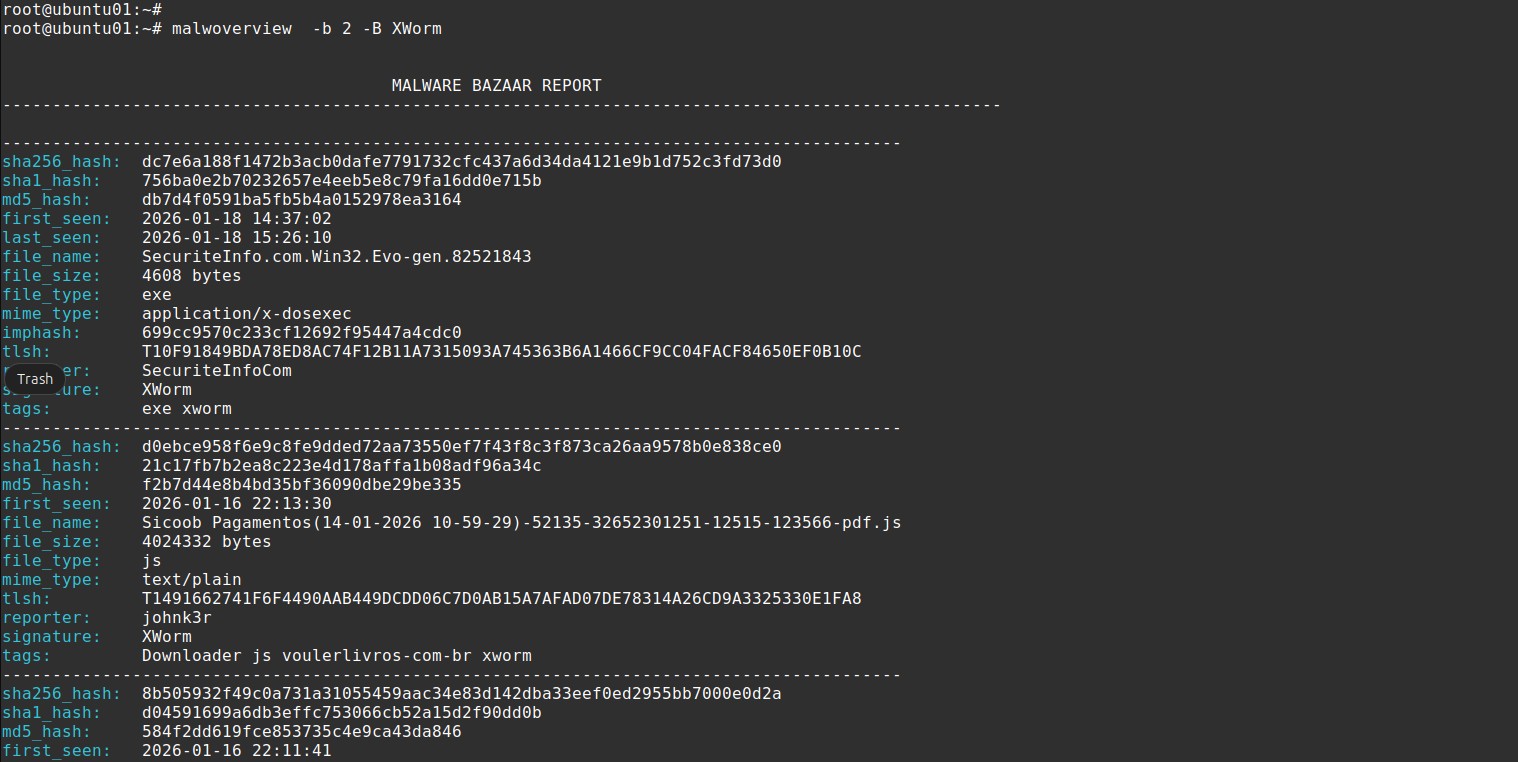
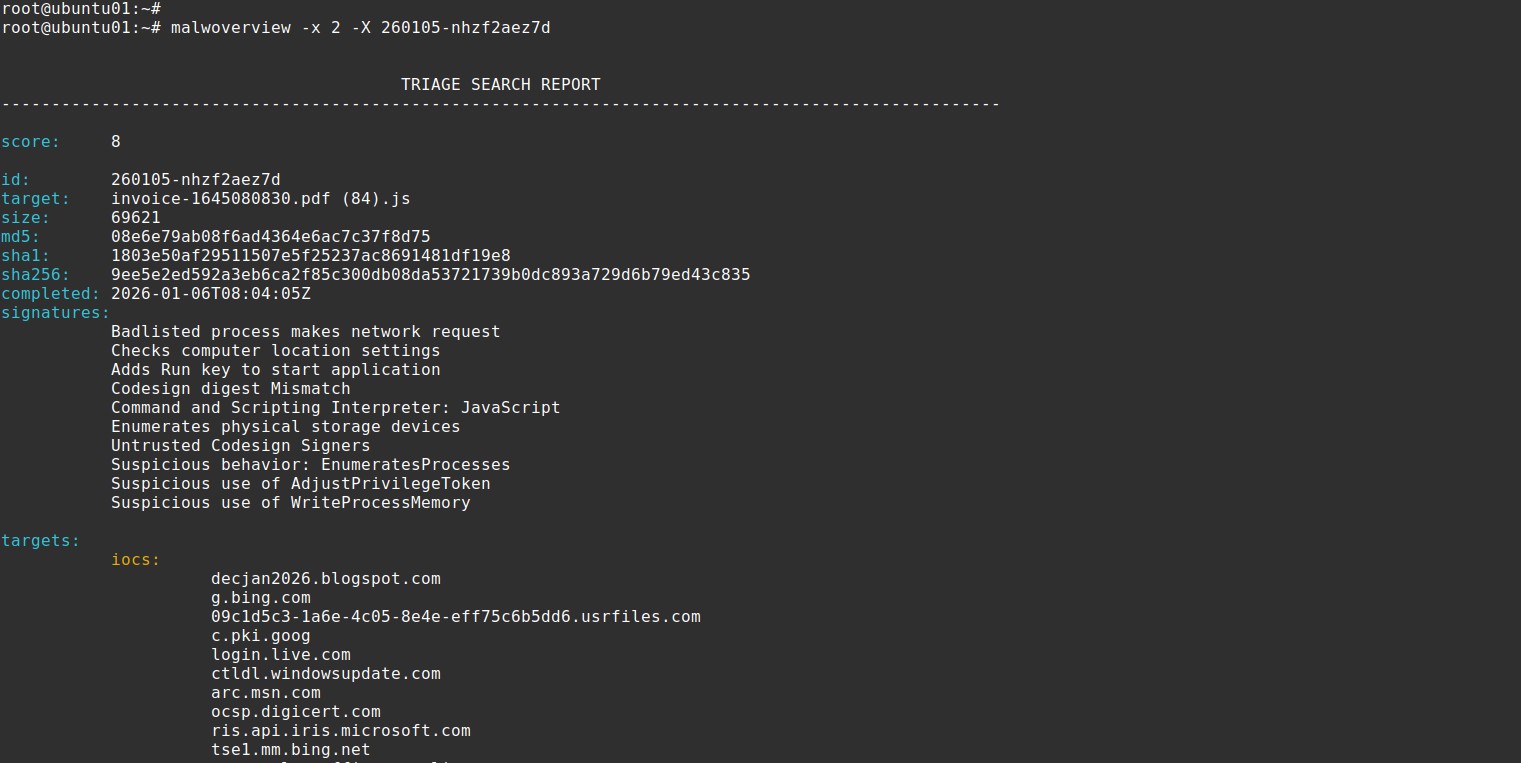
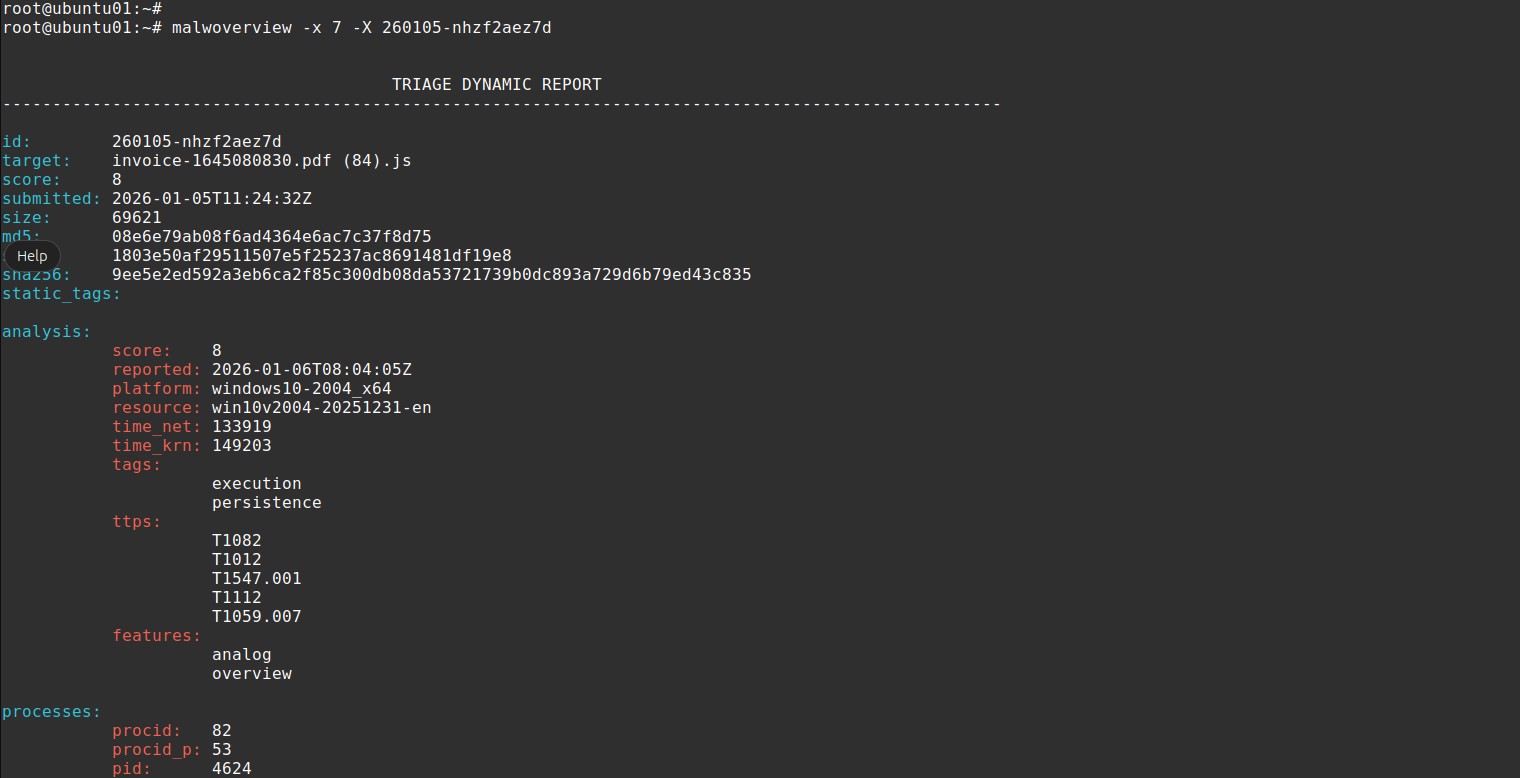
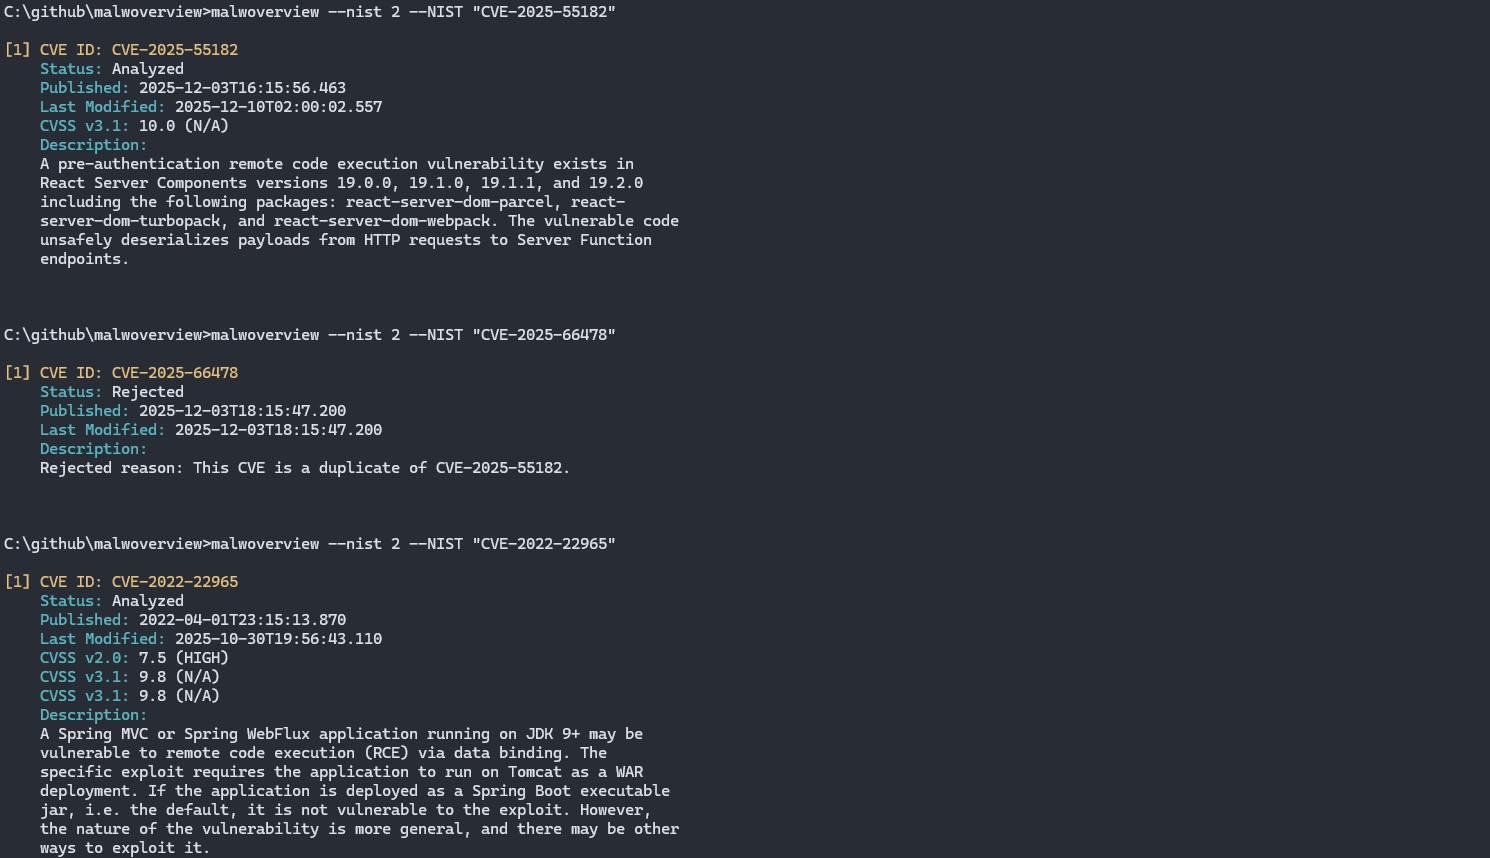
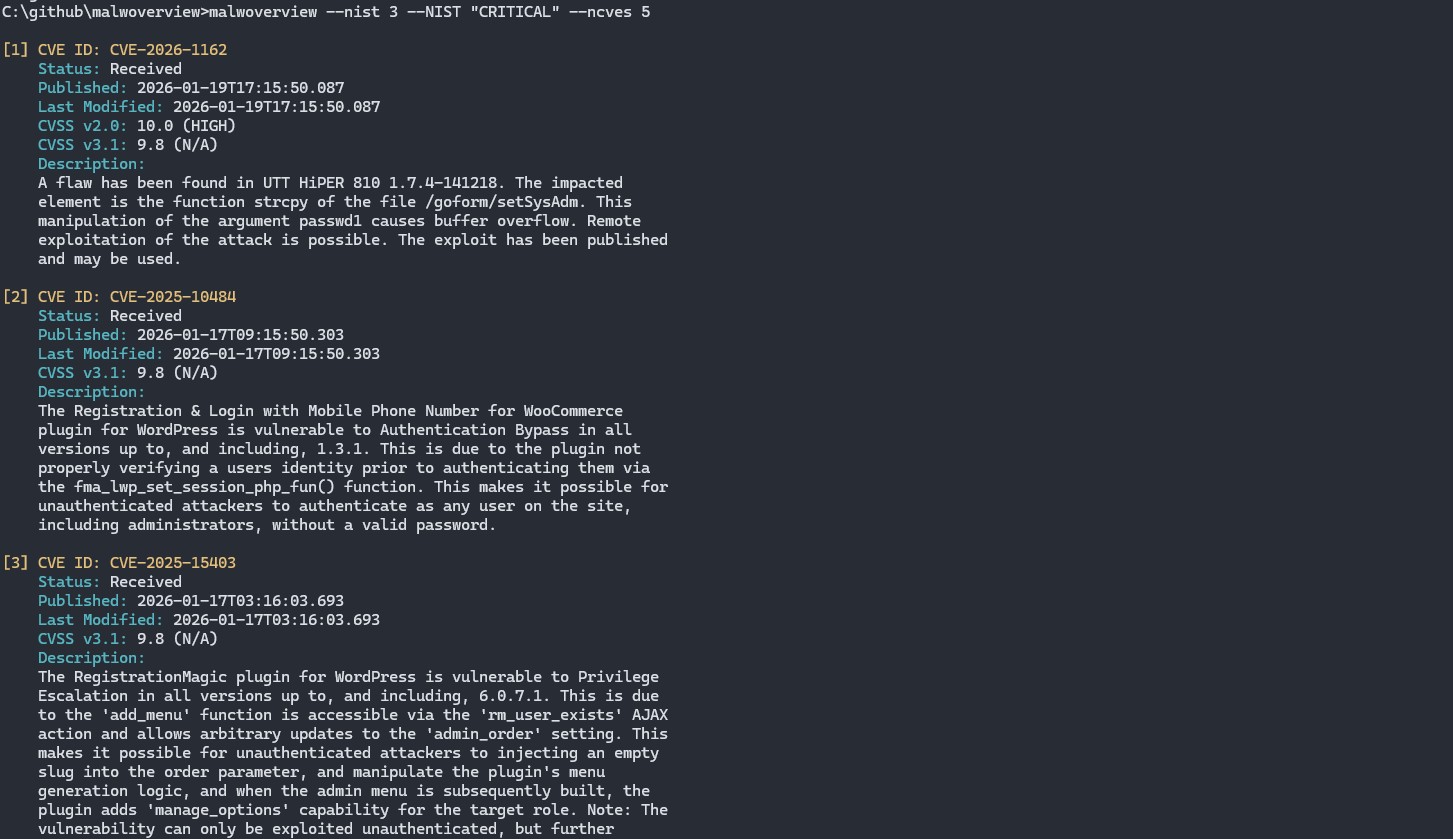
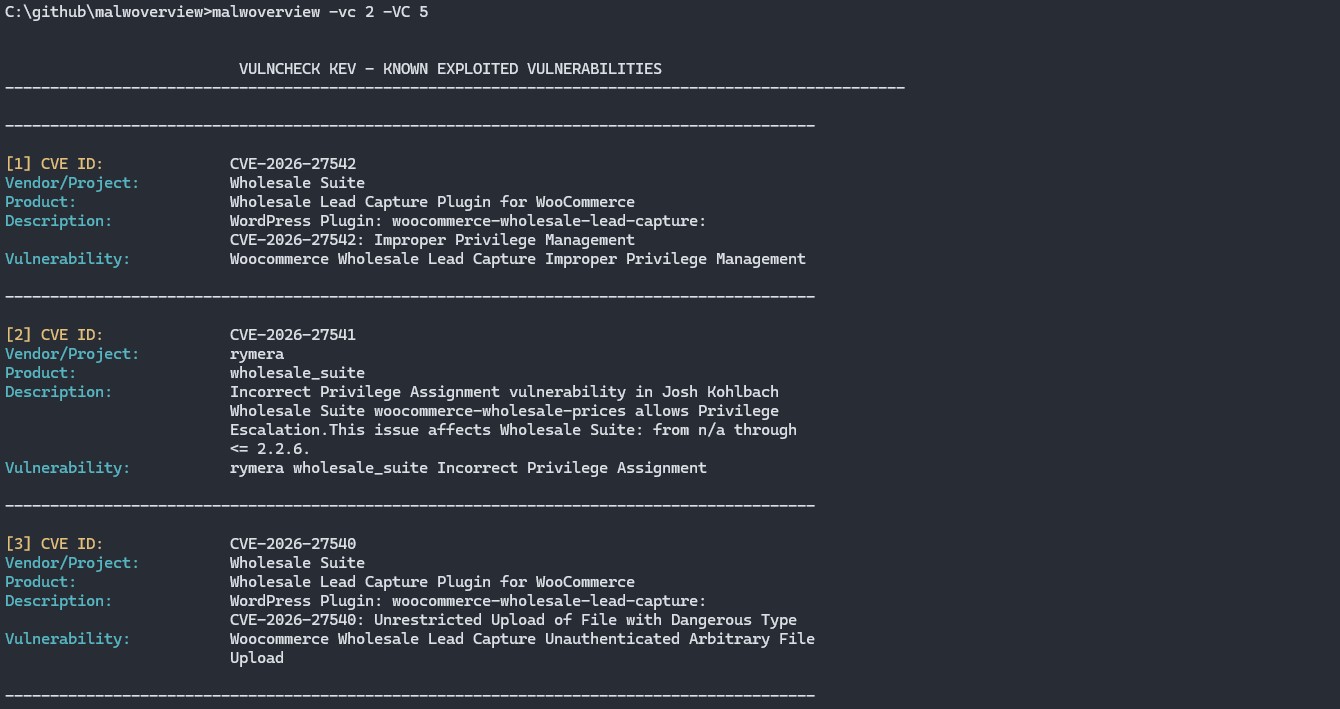
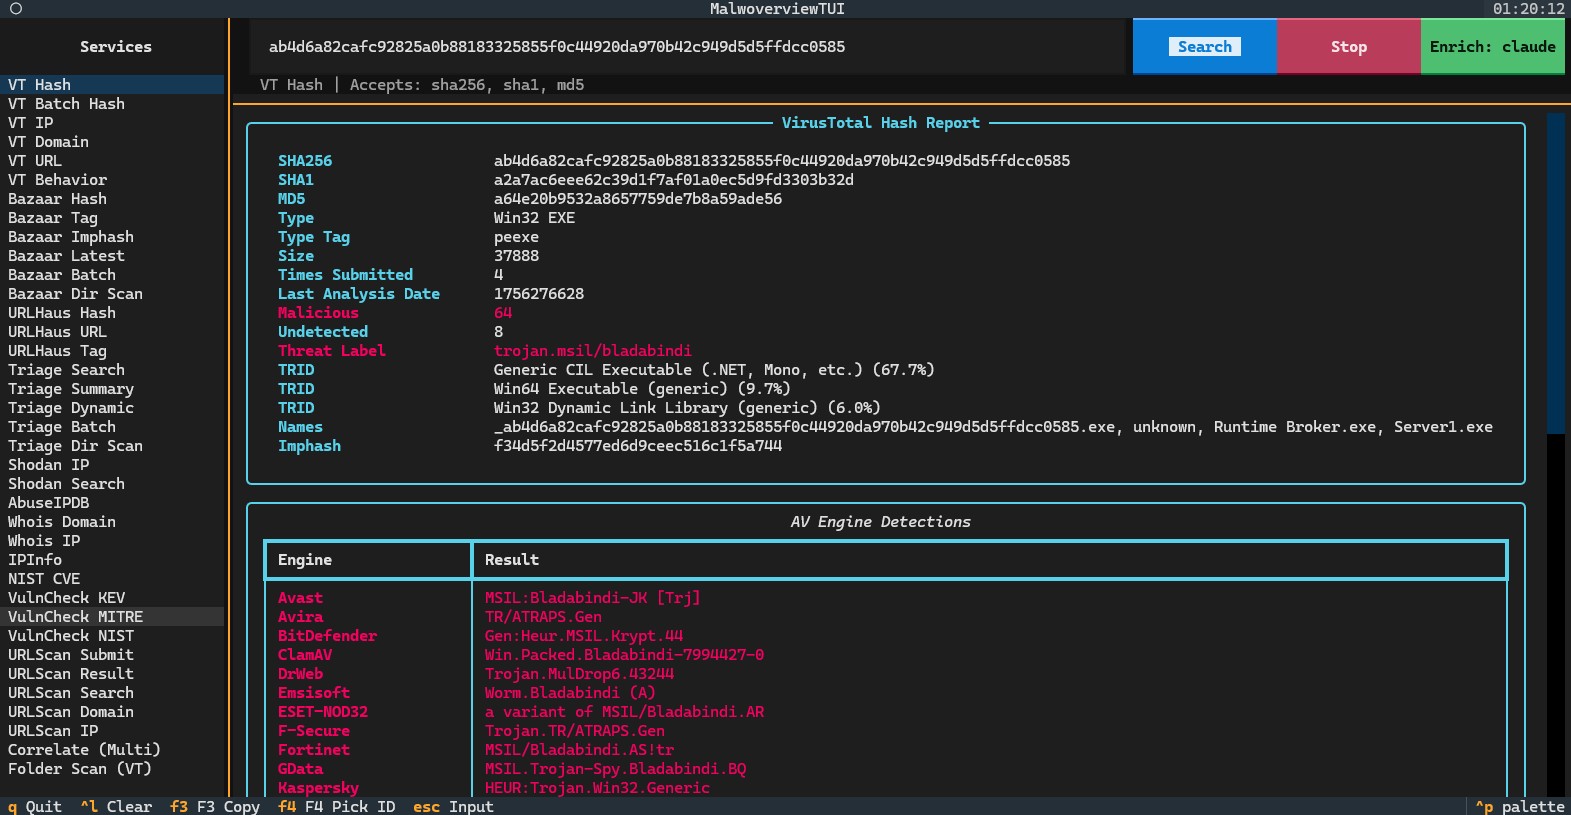
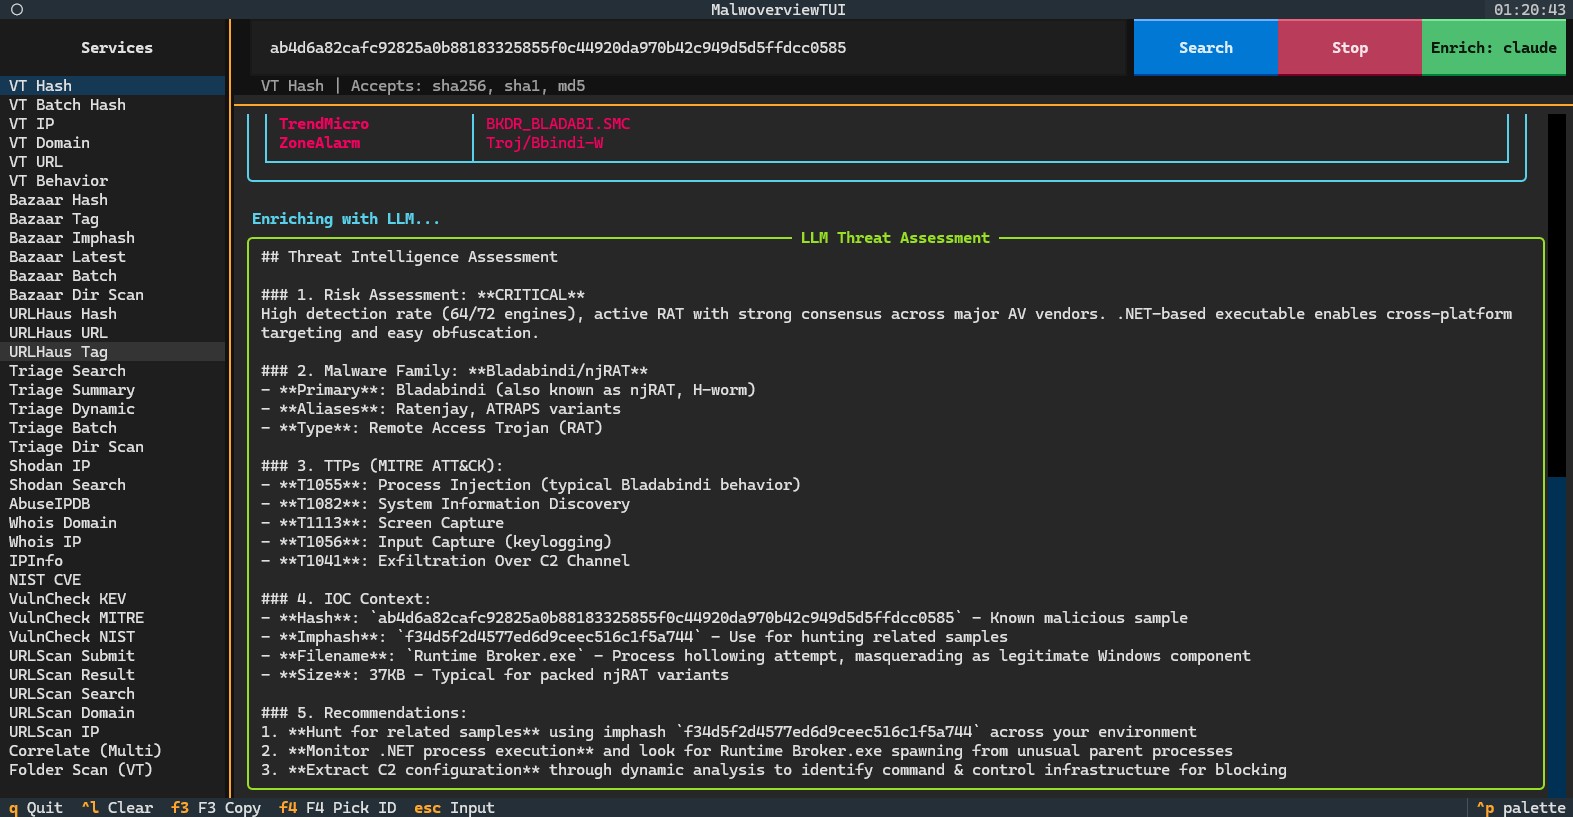
Malwoverview एक प्रथम प्रतिक्रिया उपकरण है जो VirusTotal, Hybrid Analysis, URLHaus, Polyswarm, Malshare, Alien Vault, Malpedia, Malware Bazaar, ThreatFox, Triage, IPInfo, Shodan, AbuseIPDB, GreyNoise, URLScan.io, Whois/RDAP, NIST, और VulnCheck में खतरे की खोज (threat hunting) के लिए है। यह LLM संवर्धन (enrichment), IOC निष्कर्षण, YARA स्कैनिंग, और Android विश्लेषण का समर्थन करता है।










  Copyright (C)  2018-2026 Alexandre Borges (https://exploitreversing.com)

  This program is free software: you can redistribute it and/or modify
  it under the terms of the GNU General Public License as published by
  the Free Software Foundation, either version 3 of the License, or
  (at your option) any later version.

  This program is distributed in the hope that it will be useful,
  but WITHOUT ANY WARRANTY; without even the implied warranty of
  MERCHANTABILITY or FITNESS FOR A PARTICULAR PURPOSE.  See the
  GNU General Public License for more details.

  See GNU Public License on <http://www.gnu.org/licenses/>.
 महत्वपूर्ण नोट: Malwoverview डिफ़ॉल्ट रूप से किसी भी endpoint पर सैंपल सबमिट नहीं करता है,
 इसलिए यह संभावित Non-Disclosure Agreements (NDAs) का सम्मान करता है। कुछ विशिष्ट विकल्प हैं
 जो स्पष्ट रूप से सैंपल सबमिट करते हैं, लेकिन इन विकल्पों को help में समझाया गया है।
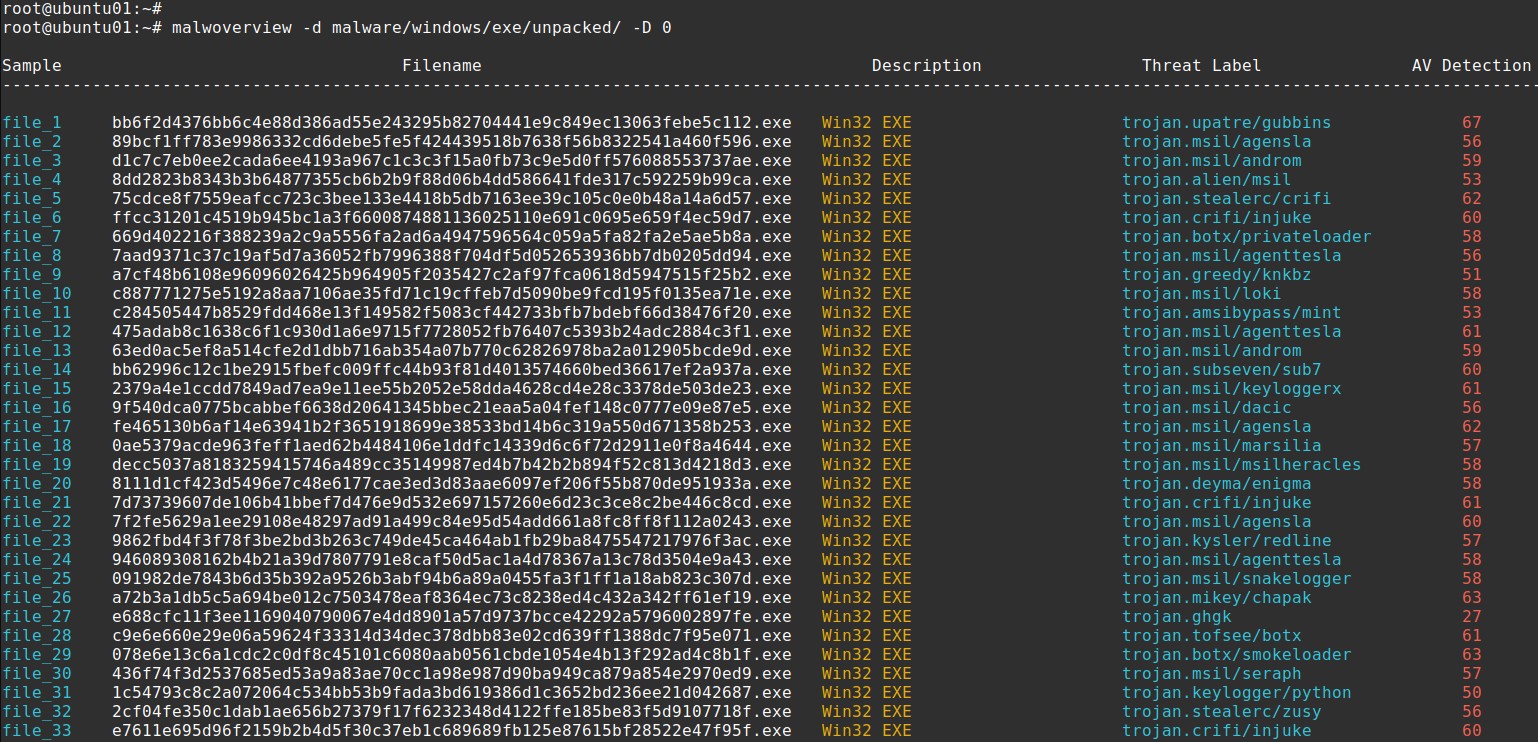
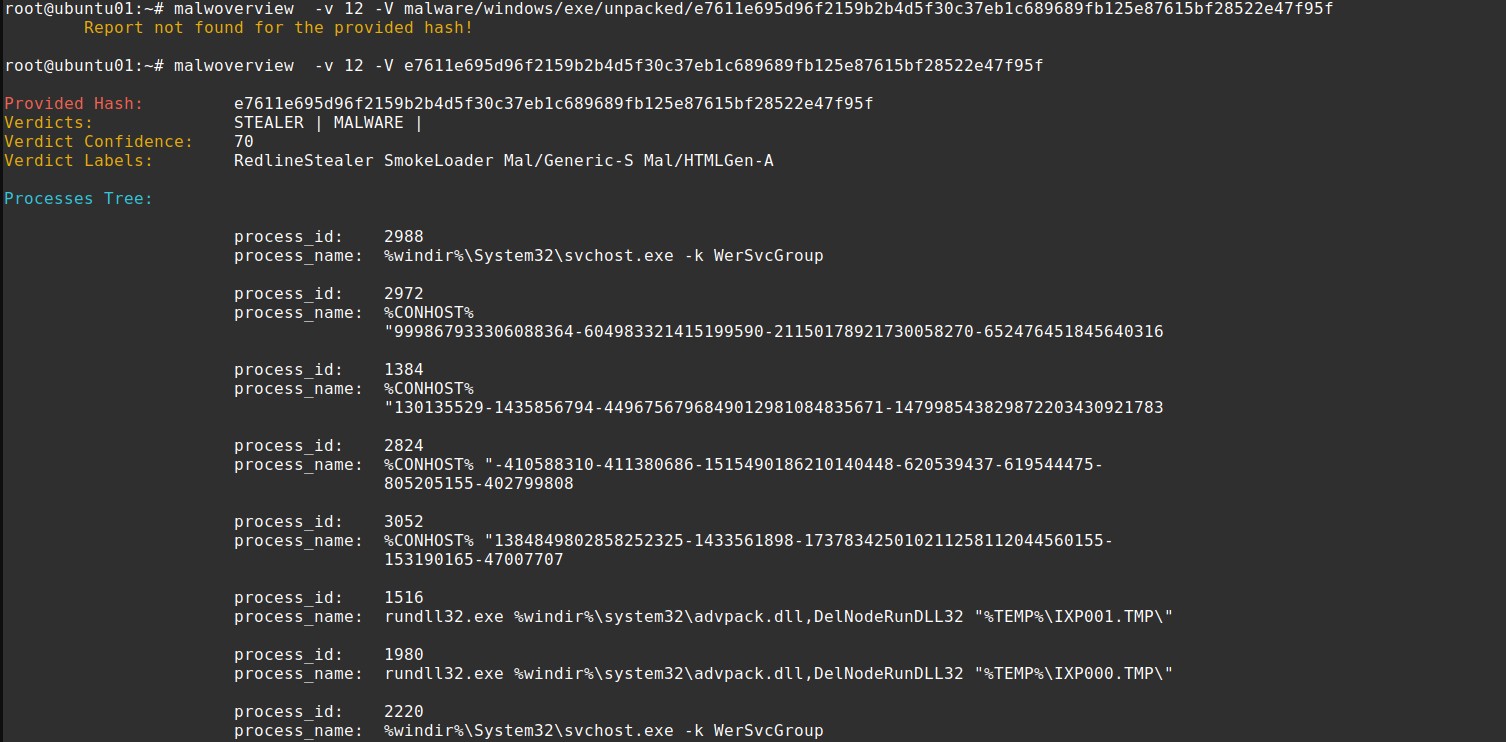
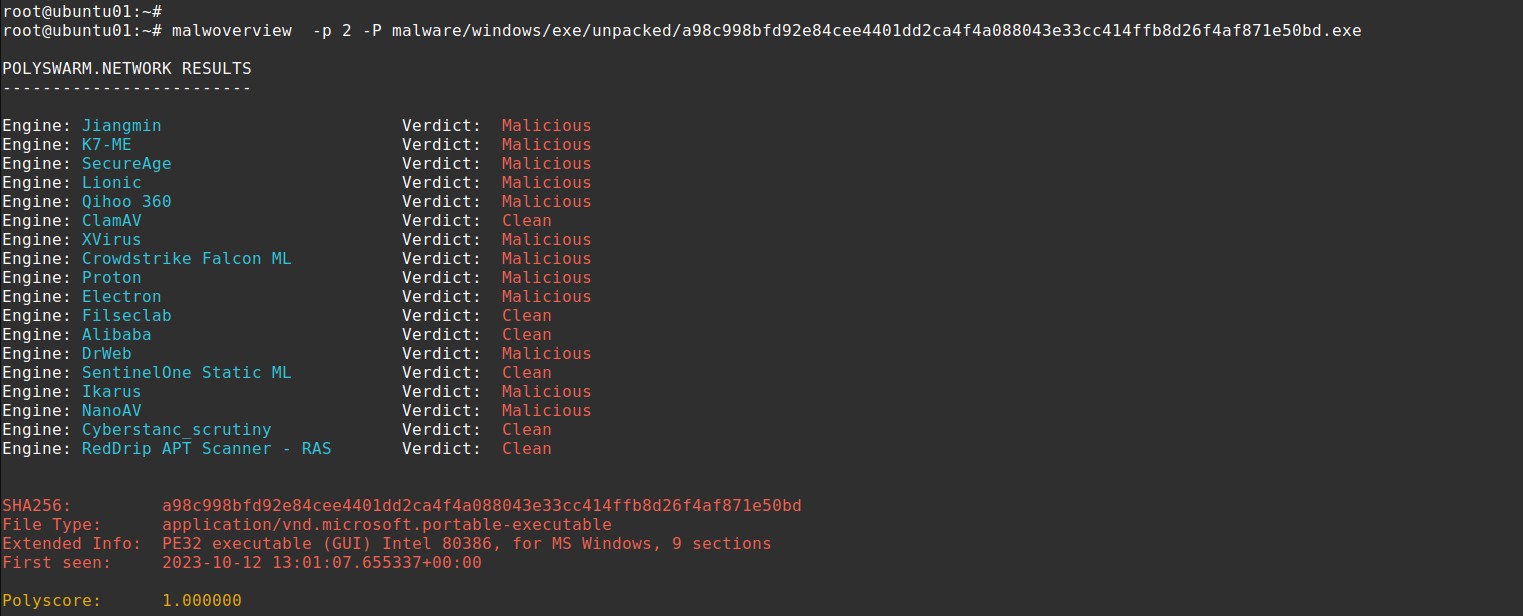
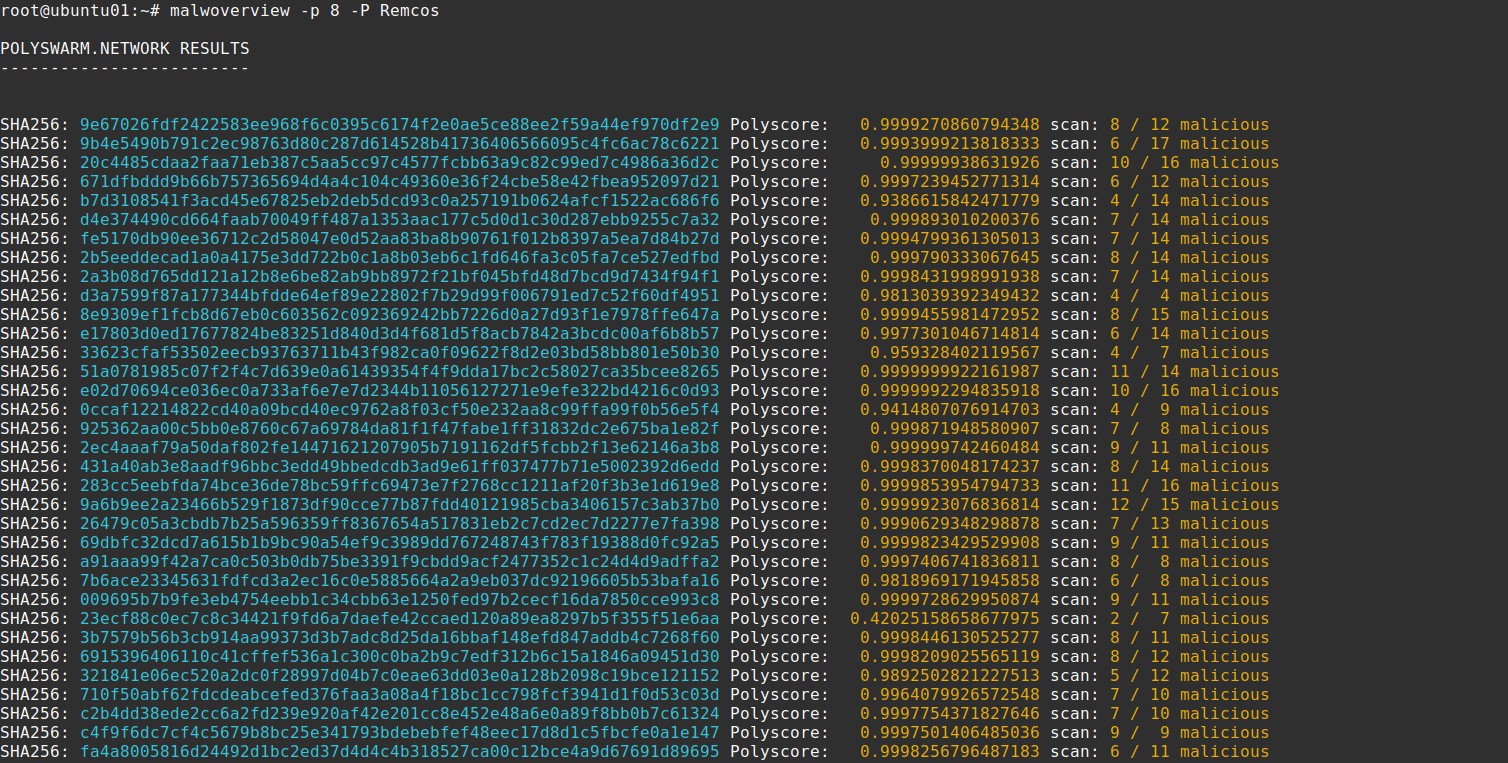
Malwoverview.py थ्रेट हंटिंग के लिए एक फर्स्ट रिस्पॉन्स टूल है, जो मैलवेयर सैंपल, URLs, IP पतों, डोमेन, मैलवेयर फैमिली, IOCs और हैश का प्रारंभिक और त्वरित ट्राइएज करता है। इसके अतिरिक्त, Malwoverview डायनामिक और स्टैटिक बिहेवियर रिपोर्ट प्राप्त करने, कई endpoints से सैंपल सबमिट और डाउनलोड करने में सक्षम है। संक्षेप में, यह मौजूदा प्रमुख सैंडबॉक्स के लिए एक क्लाइंट के रूप में कार्य करता है।
इस टूल का उद्देश्य है:

