
mobsfscan v1.0.1
mobsfscan एक स्थैतिक विश्लेषण उपकरण है जो आपके Android और iOS स्रोत कोड में असुरक्षित कोड पैटर्न खोज सकता है। यह Java, Kotlin, Swift और Objective C कोड का समर्थन करता है। mobsfscan MobSF स्थैतिक विश्लेषण नियमों का उपयोग करता है और semgrep और libsast pattern matcher द्वारा संचालित है।
mobsfscan
mobsfscan एक स्टैटिक विश्लेषण उपकरण है जो आपके Android और iOS स्रोत कोड में असुरक्षित कोड पैटर्न खोज सकता है। यह Java, Kotlin, Android XML, iOS Info.plist, Swift और Objective C कोड का समर्थन करता है। mobsfscan MobSF स्टैटिक विश्लेषण नियमों का उपयोग करता है और यह semgrep और libsast पैटर्न मैचर द्वारा संचालित है।
भारत में  के साथ निर्मित


mobsfscan का समर्थन करें
यदि आपको mobsfscan पसंद आया और यह उपयोगी लगा, तो कृपया दान करने पर विचार करें।
e-Learning पाठ्यक्रम और प्रमाणपत्र
 Automated Mobile Application Security Assessment with MobSF -MAS
 Android Security Tools Expert -ATX
स्थापना
pip install mobsfscan
Python 3.10–3.14 की आवश्यकता है
कमांड लाइन विकल्प```bash
$ mobsfscan usage: mobsfscan [-h] [--json] [--sarif] [--sonarqube] [--gitlab-sast] [--html] [--type {android,ios,auto}] [-o OUTPUT] [-c CONFIG] [-mp {default,billiard,thread}] [-w] [--no-fail] [-v] [path ...]
positional arguments: path Path can be file(s) or directories with source code
options: -h, --help show this help message and exit --json set output format as JSON --sarif set output format as SARIF 2.1.0 --sonarqube set output format as SonarQube generic issues (10.3+) --gitlab-sast set output format as GitLab SAST report --html set output format as HTML --type {android,ios,auto} optional: force android or ios rules explicitly -o OUTPUT, --output OUTPUT output filename to save the result -c CONFIG, --config CONFIG location to .mobsf config file -mp {default,billiard,thread}, --multiprocessing {default,billiard,thread} optional: specify multiprocessing strategy -w, --exit-warning non zero exit code on warning --no-fail force zero exit code, takes precedence over --exit-warning -v, --version show mobsfscan version
## उदाहरण उपयोग```bash
$ mobsfscan tests/assets/src/
- Pattern Match ████████████████████████████████████████████████████████████ 3
- Semantic Grep ██████ 37

mobsfscan: v0.3.0 | Ajin Abraham | opensecurity.in
╒══════════════╤════════════════════════════════════════════════════════════════════════════════════════════════════════════════════════════════════════════════════════╕
│ RULE ID      │ android_webview_ignore_ssl                                                                                                                             │
├──────────────┼────────────────────────────────────────────────────────────────────────────────────────────────────────────────────────────────────────────────────────┤
│ DESCRIPTION  │ Insecure WebView Implementation. WebView ignores SSL Certificate errors and accept any SSL Certificate. This application is vulnerable to MITM attacks │
├──────────────┼────────────────────────────────────────────────────────────────────────────────────────────────────────────────────────────────────────────────────────┤
│ TYPE         │ RegexAnd                                                                                                                                               │
├──────────────┼────────────────────────────────────────────────────────────────────────────────────────────────────────────────────────────────────────────────────────┤
│ PATTERN      │ ['onReceivedSslError\\(WebView', '\\.proceed\\(\\);']                                                                                                  │
├──────────────┼────────────────────────────────────────────────────────────────────────────────────────────────────────────────────────────────────────────────────────┤
│ SEVERITY     │ ERROR                                                                                                                                                   │
├──────────────┼────────────────────────────────────────────────────────────────────────────────────────────────────────────────────────────────────────────────────────┤
│ INPUTCASE    │ exact                                                                                                                                                  │
├──────────────┼────────────────────────────────────────────────────────────────────────────────────────────────────────────────────────────────────────────────────────┤
│ CVSS         │ 7.4                                                                                                                                                    │
├──────────────┼────────────────────────────────────────────────────────────────────────────────────────────────────────────────────────────────────────────────────────┤
│ CWE          │ CWE-295 Improper Certificate Validation                                                                                                                │
├──────────────┼────────────────────────────────────────────────────────────────────────────────────────────────────────────────────────────────────────────────────────┤
│ OWASP-MOBILE │ M3: Insecure Communication                                                                                                                             │
├──────────────┼────────────────────────────────────────────────────────────────────────────────────────────────────────────────────────────────────────────────────────┤
│ MASVS        │ MSTG-NETWORK-3                                                                                                                                         │
├──────────────┼────────────────────────────────────────────────────────────────────────────────────────────────────────────────────────────────────────────────────────┤
│ REF          │ https://github.com/MobSF/owasp-mstg/blob/master/Document/0x05g-Testing-Network-Communication.md#webview-server-certificate-verification                │
├──────────────┼────────────────────────────────────────────────────────────────────────────────────────────────────────────────────────────────────────────────────────┤
│ FILES        │ ╒════════════════╤═════════════════════════════════════════════════════════════════════════════════════════════╕                                       │
│              │ │ File           │ ../test_files/android_src/app/src/main/java/opensecurity/webviewignoressl/MainActivity.java │                                       │
│              │ ├────────────────┼─────────────────────────────────────────────────────────────────────────────────────────────┤                                       │
│              │ │ Match Position │ 1480 - 1491                                                                                 │                                       │
│              │ ├────────────────┼─────────────────────────────────────────────────────────────────────────────────────────────┤                                       │
│              │ │ Line Number(s) │ 50                                                                                          │                                       │
│              │ ├────────────────┼─────────────────────────────────────────────────────────────────────────────────────────────┤                                       │
│              │ │ Match String   │ .proceed();                                                                                 │                                       │
│              │ ├────────────────┼─────────────────────────────────────────────────────────────────────────────────────────────┤                                       │
│              │ │ File           │ ../test_files/android_src/app/src/main/java/opensecurity/webviewignoressl/MainActivity.java │                                       │
│              │ ├────────────────┼─────────────────────────────────────────────────────────────────────────────────────────────┤                                       │
│              │ │ Match Position │ 1331 - 1357                                                                                 │                                       │
│              │ ├────────────────┼─────────────────────────────────────────────────────────────────────────────────────────────┤                                       │
│              │ │ Line Number(s) │ 46                                                                                          │                                       │
│              │ ├────────────────┼─────────────────────────────────────────────────────────────────────────────────────────────┤                                       │
│              │ │ Match String   │ onReceivedSslError(WebView                                                                  │                                       │
│              │ ╘════════════════╧═════════════════════════════════════════════════════════════════════════════════════════════╛                                       │
╘══════════════╧════════════════════════════════════════════════════════════════════════════════════════════════════════════════════════════════════════════════════════╛
Python API```python
from mobsfscan.mobsfscan import MobSFScan src = 'tests/assets/src/java/java_vuln.java' scanner = MobSFScan([src], json=True) scanner.scan() { 'results': { 'android_logging': { 'files': [{ 'file_path': 'tests/assets/src/java/java_vuln.java', 'match_position': (13, 73), 'match_lines': (19, 19), 'match_string': ' Log.d("htbridge", "getAllRecords(): " + records.toString());' }], 'metadata': { 'cwe': 'CWE-532 Insertion of Sensitive Information into Log File', 'owasp-mobile': 'M1: Improper Platform Usage', 'masvs': 'MSTG-STORAGE-3', 'reference': 'https://github.com/MobSF/owasp-mstg/blob/master/Document/0x05d-Testing-Data-Storage.md#logs', 'description': 'The App logs information. Please ensure that sensitive information is never logged.', 'severity': 'INFO' } }, 'android_certificate_pinning': { 'metadata': { 'cwe': 'CWE-295 Improper Certificate Validation', 'owasp-mobile': 'M3: Insecure Communication', 'masvs': 'MSTG-NETWORK-4', 'reference': 'https://github.com/MobSF/owasp-mstg/blob/master/Document/0x05g-Testing-Network-Communication.md#testing-custom-certificate-stores-and-certificate-pinning-mstg-network-4', 'description': 'This App does not use TLS/SSL certificate or public key pinning to detect or prevent MITM attacks in secure communication channel.', 'severity': 'INFO' } }, 'android_root_detection': { 'metadata': { 'cwe': 'CWE-919 - Weaknesses in Mobile Applications', 'owasp-mobile': 'M8: Code Tampering', 'masvs': 'MSTG-RESILIENCE-1', 'reference': 'https://github.com/MobSF/owasp-mstg/blob/master/Document/0x05j-Testing-Resiliency-Against-Reverse-Engineering.md#testing-root-detection-mstg-resilience-1', 'description': 'This App does not have root detection capabilities. Running a sensitive application on a rooted device questions the device integrity and affects users data.', 'severity': 'INFO' } }, 'android_prevent_screenshot': { 'metadata': { 'cwe': 'CWE-200 Information Exposure', 'owasp-mobile': 'M2: Insecure Data Storage', 'masvs': 'MSTG-STORAGE-9', 'reference': 'https://github.com/MobSF/owasp-mstg/blob/master/Document/0x05d-Testing-Data-Storage.md#finding-sensitive-information-in-auto-generated-screenshots-mstg-storage-9', 'description': 'This App does not have capabilities to prevent against Screenshots from Recent Task History/ Now On Tap etc.', 'severity': 'INFO' } }, 'android_safetynet_api': { 'metadata': { 'cwe': 'CWE-353 Missing Support for Integrity Check', 'owasp-mobile': 'M8: Code Tampering', 'masvs': 'MSTG-RESILIENCE-1', 'reference': 'https://github.com/MobSF/owasp-mstg/blob/master/Document/0x05j-Testing-Resiliency-Against-Reverse-Engineering.md#testing-root-detection-mstg-resilience-1', 'description': "This App does not uses SafetyNet Attestation API that provides cryptographically-signed attestation, assessing the device's integrity. This check helps to ensure that the servers are interacting with the genuine app running on a genuine Android device. ", 'severity': 'INFO' } }, 'android_detect_tapjacking': { 'metadata': { 'cwe': 'CWE-200 Information Exposure', 'owasp-mobile': 'M1: Improper Platform Usage', 'masvs': 'MSTG-PLATFORM-9', 'reference': 'https://github.com/MobSF/owasp-mstg/blob/master/Document/0x05h-Testing-Platform-Interaction.md#testing-for-overlay-attacks-mstg-platform-9', 'description': "This app does not has capabilities to prevent tapjacking attacks. An attacker can hijack the user's taps and tricks him into performing some critical operations that he did not intend to.", 'severity': 'INFO' } } }, 'errors': [] }
## mobsfscan कॉन्फ़िगर करें

सोर्स कोड डायरेक्टरी की रूट में एक `.mobsf` फ़ाइल आपको mobsfscan कॉन्फ़िगर करने की अनुमति देती है। आप `--config` आर्ग्युमेंट का उपयोग करके एक कस्टम `.mobsf` फ़ाइल भी उपयोग कर सकते हैं।```yaml
---
- ignore-filenames:
  - skip.java

  ignore-paths:
  - __MACOSX
  - skip_dir

  ignore-rules:
  - android_kotlin_logging
  - android_safetynet_api
  - android_prevent_screenshot
  - android_detect_tapjacking
  - android_certificate_pinning
  - android_root_detection
  - android_certificate_transparency

  severity-filter:
  - WARNING
  - ERROR

  severity-overrides:
    ios_log: ERROR
    android_logging: WARNING
severity-overrides विशिष्ट rule IDs (INFO, WARNING, या ERROR) के लिए रिपोर्ट की गई severity को बदलता है। Overrides severity-filter से पहले लागू होते हैं और CLI output, exit codes, तथा report formats (SARIF, SonarQube, GitLab SAST) को प्रभावित करते हैं।
Findings को Suppress करें
आप उस line पर // mobsf-ignore: rule_id1, rule_id2 comment जोड़कर source files से findings को suppress कर सकते हैं जो finding को trigger करती है। केवल वही match suppress होता है; file में उसी rule के अन्य matches अभी भी report होते हैं।
उदाहरण:```java String password = "strong password"; // mobsf-ignore: hardcoded_password
## CI/CD एकीकरण

आप mobsfscan को अपने CI/CD या DevSecOps पाइपलाइनों में सक्षम कर सकते हैं।

#### Github Action

निम्नलिखित को `.github/workflows/mobsfscan.yml` फ़ाइल में जोड़ें।```yaml
name: mobsfscan

on:
  push:
    branches: [ master, main ]
  pull_request:
    branches: [ master, main ]

jobs:
  build:
    runs-on: ubuntu-latest
    steps:
    - uses: actions/checkout@3d3c42e5aac5ba805825da76410c181273ba90b1 # v7.0.1
    - uses: actions/setup-python@5fda3b95a4ea91299a34e894583c3862153e4b97 # v7.0.0
      with:
        python-version: '3.12'
    - name: mobsfscan
      uses: MobSF/mobsfscan@main
      with:
        args: '. --json'
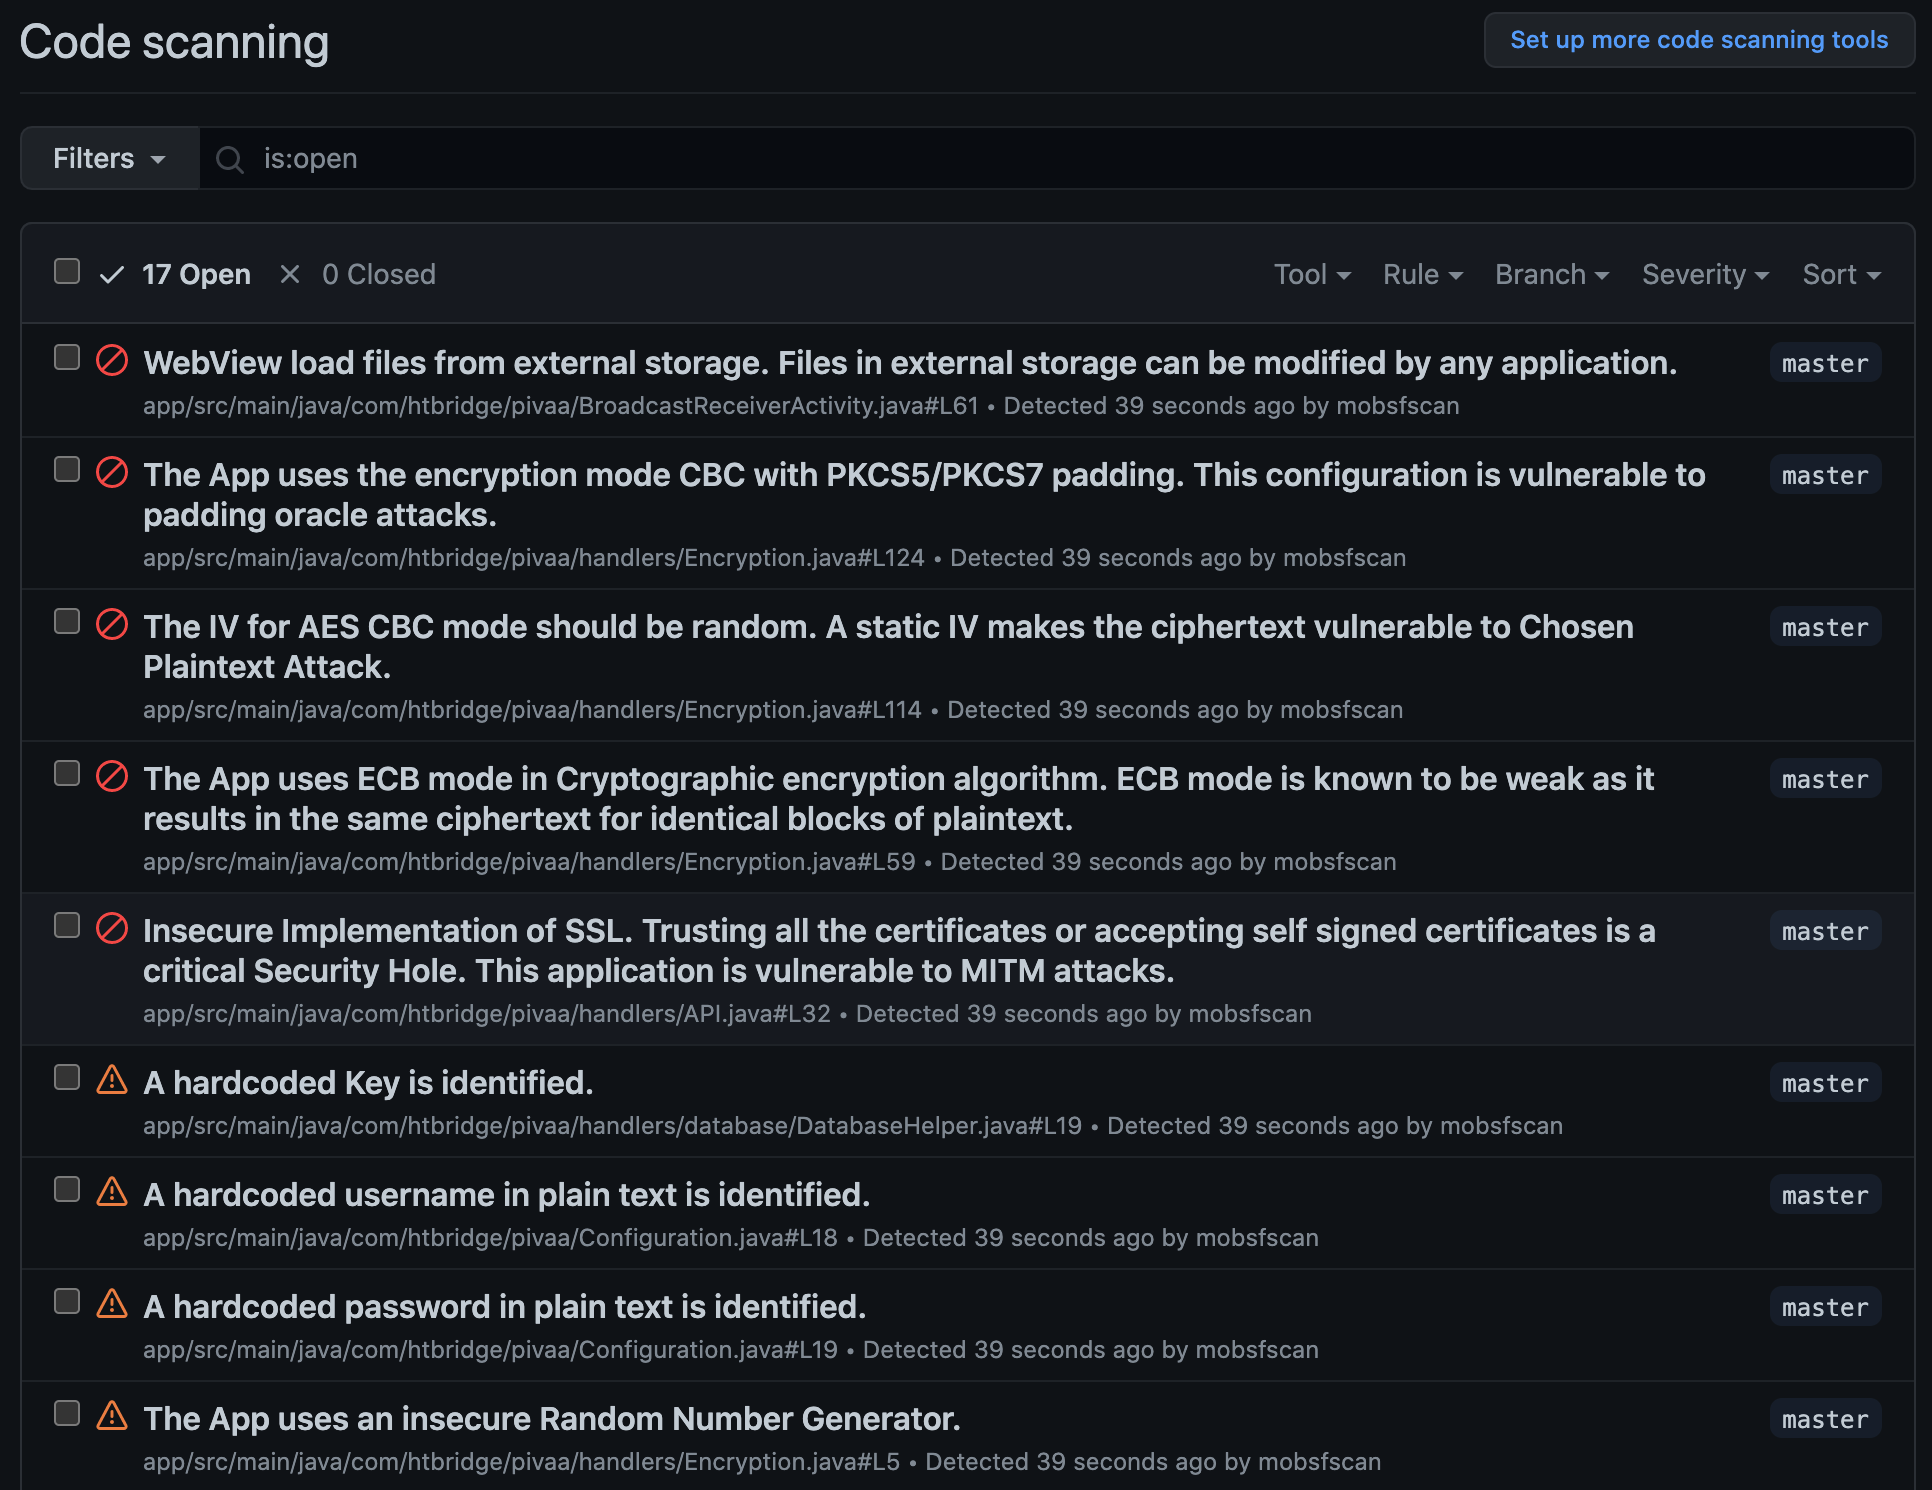
Example: pivaa with mobsfscan github action
Github Code Scanning Integration
निम्नलिखित को .github/workflows/mobsfscan_sarif.yml फ़ाइल में जोड़ें।```yaml
name: mobsfscan sarif
on:
push:
branches: [ master, main ]
pull_request:
branches: [ master, main ]
jobs: mobsfscan: runs-on: ubuntu-latest name: mobsfscan code scanning permissions: security-events: write actions: read contents: read steps: - name: Checkout the code uses: actions/checkout@3d3c42e5aac5ba805825da76410c181273ba90b1 # v7.0.1 - uses: actions/setup-python@5fda3b95a4ea91299a34e894583c3862153e4b97 # v7.0.0 with: python-version: '3.12' - name: mobsfscan uses: MobSF/mobsfscan@main with: args: '. --sarif --output results.sarif || true' - name: Upload mobsfscan report uses: github/codeql-action/upload-sarif@1c5b675653bb5c22dbe9b12b556ec555138e09fd # v4.38.1 with: sarif_file: results.sarif
#### Gitlab CI/CD
फ़ाइल `.gitlab-ci.yml` में निम्नलिखित जोड़ें।```yaml
stages:
- test
mobsfscan:
image: python:3.12
stage: test
before_script:
- pip3 install --upgrade mobsfscan
script:
- mobsfscan . --gitlab-sast -o gl-sast-report.json
artifacts:
reports:
sast: gl-sast-report.json
उदाहरण कमांड (स्थानीय):```bash mobsfscan . --gitlab-sast -o gl-sast-report.json
यह एक नेटिव [GitLab SAST रिपोर्ट](https://docs.gitlab.com/user/application_security/sast/) लिखता है ताकि निष्कर्ष SARIF कन्वर्टर के बिना Vulnerability Report / MR security widget में दिखाई दें।

#### SonarQube / SonarCloud

`--sonarqube` [generic issue format](https://docs.sonarsource.com/sonarqube-server/analyzing-source-code/importing-external-issues/generic-issue-import-format) (SonarQube 10.3+ / SonarCloud) लिखता है, जिसमें अलग-अलग `rules` और `issues` arrays होते हैं:```bash
mobsfscan . --sonarqube -o mobsfscan-sonar.json
sonar.externalIssuesReportPaths=mobsfscan-sonar.json के साथ आयात करें।
Travis CI
फ़ाइल .travis.yml में निम्नलिखित जोड़ें।```yaml
language: python
install:
- pip3 install --upgrade mobsfscan
script:
- mobsfscan .
#### Circle CI

फ़ाइल `.circleci/config.yaml` में निम्नलिखित जोड़ें```yaml
version: 2.1
jobs:
  mobsfscan:
    docker:
      - image: cimg/python:3.12
    steps:
      - checkout
      - run:
          name: Install mobsfscan
          command: pip install --upgrade mobsfscan
      - run:
           name: mobsfscan check
           command: mobsfscan .
Bitrise
फ़ाइल bitrise.yml में निम्नलिखित जोड़ें```yaml
security_audit:
steps:
- activate-ssh-key@4: run_if: '{{getenv "SSH_RSA_PRIVATE_KEY" | ne ""}}'
- [email protected]: {}
- mobsfscan@1: {}
- deploy-to-bitrise-io@2: {}
## Docker

### [DockerHub](https://hub.docker.com/r/opensecurity/mobsfscan) से पहले से बना इमेज```bash
docker pull opensecurity/mobsfscan
docker run -v /path-to-source-dir:/src opensecurity/mobsfscan /src
स्थानीय रूप से बनाएं```
docker build -t mobsfscan . docker run -v /path-to-source-dir:/src mobsfscan /src