

Skip to content
KitploitKITPLOIT
उपकरणएक्सप्लॉइटब्लॉग
Log in
जमा करें
उपकरणएक्सप्लॉइटब्लॉग
जमा करें

हैकिंग, पेनटेस्ट और साइबर सुरक्षा उपकरण आपके सुरक्षा शस्त्रागार के लिए!

Kitploit हैकिंग, साइबर सुरक्षा और पेंटेस्टिंग टूल्स की एक निर्देशिका है। कमजोरियों को खोजने, सिस्टम का विश्लेषण करने, परीक्षण को स्वचालित करने और अपनी सुरक्षा को मजबूत करने के लिए नवीनतम प्रोजेक्ट अपडेट खोजें।

फ़ीडसंपर्कगोपनीयता© 2026 Kitploit

टूल निर्देशिका

श्रेणियाँ

सभी श्रेणियाँ देखें
Loading categories
शेलकोड — पृष्ठ 12 | Kitploit
श्रेणियाँ

शेलकोड

सफल शोषण के बाद निष्पादित निम्न-स्तरीय कोड को बनाने और हेरफेर करने के उपकरण।

Kitploit अनुशंसित

शीर्ष उपकरण

10 चयनित
donut preview#1

donut

GitHubthewover/donut
4.7k1 साल पहले
sRDI preview#2

sRDI

GitHubmonoxgas/srdi
2.5k4 साल पहले
pe_to_shellcode preview#3

pe_to_shellcode

GitHubhasherezade/pe_to_shellcode
2.8k1 साल पहले
sgn preview#4

sgn

GitHubegebalci/sgn
2.0k2 महीने पहले
unicorn preview#5

unicorn

GitHubtrustedsec/unicorn
3.9k1 महीना पहले
SysWhispers2 preview#6

SysWhispers2

GitHubjthuraisamy/syswhispers2
1.8k4 साल पहले
SysWhispers3 preview#7

SysWhispers3

GitHubklezvirus/syswhispers3
1.6k2 साल पहले
metasploit-framework preview#8

metasploit-framework

GitHubrapid7/metasploit-framework
38.8k14 घंटे पहले
sliver preview#9

sliver

GitHubbishopfox/sliver
11.7k18घं 15मि पहले
merlin preview#10

merlin

GitHubne0nd0g/merlin
5.6k8 दिन पहले
नवीनतमप्रासंगिकतासबसे लोकप्रियहाल ही में अपडेट किया गया
860 परिणाम
Split preview

Split

GitHubkudaes/split

EDRs को बायपास करने के लिए divide and conquer दृष्टिकोण लागू करें

ids-ips-evasionshellcodepost-exploitation+3
2863 साल पहले
CVE-2023-3519 preview

CVE-2023-3519

GitHubbishopfox/cve-2023-3519

CVE-2023-3519 के लिए RCE एक्सप्लॉइट
vulnerability-analysisexploitationshellcode+3
2283 साल पहले
KittyStager preview

KittyStager

GitHubenelg52/kittystager

किटीस्टेजर एक सरल स्टेज 0 C2 है। यह शेलकोड होस्ट करने के लिए एक वेब सर्वर और एक इम्प्लांट, जिसे किटन कहा जाता है, से बना है। इस प्रोजेक्ट का उद्देश्य…

reconnaissanceencryption-decryption-toolsexploit-frameworks+6
2283 साल पहले
scare preview

scare

GitHubnetspooky/scare

आपकी कमांड लाइन के लिए एक मल्टी-आर्क असेंबली REPL और इम्यूलेटर।
dynamic-analysis-sandboxingreverse-engineeringshellcode+4
3111 साल पहले
themida-unmutate preview

themida-unmutate

GitHubergrelet/themida-unmutate

Themida, WinLicense और Code Virtualizer 3.x के म्यूटेशन-आधारित ऑबफस्केशन के लिए स्टैटिक डिऑबफस्केटर।

static-analysisreverse-engineeringshellcode+3
3802 साल पहले
linux_injector preview

linux_injector

GitHubnamazso/linux_injector

x64 Linux के लिए एक सरल ptrace-रहित साझा लाइब्रेरी इंजेक्टर

shellcodepost-exploitationpenetration-testing+3
2933 साल पहले
hackEmbedded preview

hackEmbedded

GitHubdoudoudedi/hackembedded

यह उपकरण विभिन्न आर्किटेक्चर उपकरणों के लिए बैकडोर, शेलकोड, सॉक्स5 प्रॉक्सी जनरेशन, सूचना पुनर्प्राप्ति और POC व्यवस्था को एन्क्रिप्ट करने के लिए…
embedded-systems-securityencryption-decryption-toolsiot-security+8
2072 महीने पहले
Obfuscator preview

Obfuscator

GitHub3xpl01tc0d3r/obfuscator

कार्यक्रम शेलकोड को अस्पष्ट करने के लिए डिज़ाइन किया गया है।
encryption-decryption-toolspayload-generationshellcode+2
2035 साल पहले
CVE-2022-26134-Godzilla-MEMSHELL preview

CVE-2022-26134-Godzilla-MEMSHELL

GitHubbeichendream/cve-2022-26134-godzilla-memshell

CVE-2022-26134 के लिए Java-आधारित एक्सप्लॉइट जो Confluence सर्वर में Godzilla वेबशेल इंजेक्ट करता है, पासवर्ड और कुंजी प्रमाणीकरण के साथ रिमोट कोड…
payload-generationexploitationshellcode+3
3404 साल पहले
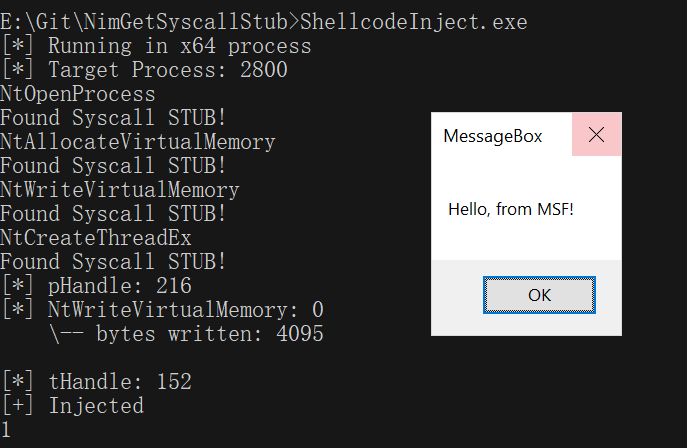
NimGetSyscallStub preview

NimGetSyscallStub

GitHubs3cur3th1ssh1t/nimgetsyscallstub

गतिशील रूप से ntdll.dll से नए सिस्कॉल स्टब्स (syscall stubs) निकालता है ताकि हस्ताक्षर-आधारित पहचान (signature-based detection) से बचा जा सके, जिसमें…
payload-generationexploitationshellcode+2
2324 साल पहले
Sharperner preview

Sharperner

GitHubaniqfakhrul/sharperner

एन्क्रिप्टेड शेलकोड के साथ सरल निष्पादन योग्य जनरेटर।

encryption-decryption-toolspayload-generationexploitation+3
2825 साल पहले
micr0_shell preview

micr0_shell

GitHubsenzee1984/micr0_shell

micr0shell एक Python स्क्रिप्ट है जो गतिशील रूप से Windows X64 PIC Null-Free रिवर्स शेल शेलकोड उत्पन्न करती है।
payload-generationexploitationshellcode+2
2226 महीने पहले
CVE-2019-0708-EXP-Windows preview

CVE-2019-0708-EXP-Windows

GitHubcbwang505/cve-2019-0708-exp-windows

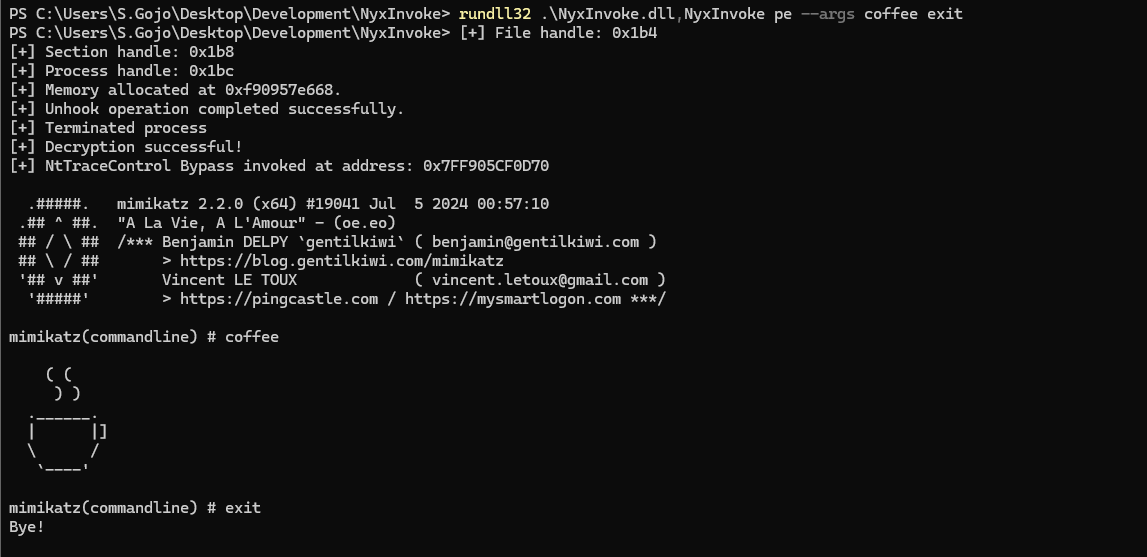
CVE-2019-0708-EXP-Windows संस्करण एकल-फ़ाइल exe संस्करण, चलाने के बाद सीधे वर्तमान कंसोल में System विशेषाधिकार वाला Shell रिवर्स करता है

payload-generationvulnerability-analysisexploitation+3
3176 साल पहले
shellme preview

shellme

GitHubhatriot/shellme

सरल शेलकोड जनरेटर

payload-generationexploitationshellcode+3
1139 साल पहले
NyxInvoke preview

NyxInvoke

GitHubblacksnufkin/nyxinvoke

NyxInvoke एक Rust CLI टूल है जो .NET असेंबली, PowerShell और BOFs को पैचलेस AMSI और ETW बायपास सुविधाओं के साथ चलाने के लिए है। दोहरे-निर्माण समर्थन…

exploitationids-ips-evasionshellcode+6
2431 साल पहले
EvilVM preview

EvilVM

GitHubjephthai/evilvm

Forth-आधारित कंपाइलर जिसे position-independent x86_64 shellcode के रूप में तैनात किया गया है, जो TCP, HTTP, ICMP, और SMB पर interactive REPL के साथ…

exploit-frameworksreverse-engineeringscripting-automation+7
2094 साल पहले
Lastenzug preview

Lastenzug

GitHubcodewhitesec/lastenzug

PIC, Websockets और असेंबली स्तर पर स्टैटिक ऑब्स्क्यूरेशन का उपयोग करने वाला Socks4a प्रॉक्सी
ids-ips-evasionshellcodepost-exploitation+3
2344 साल पहले
Remote-DLL-Injection-with-Timer-based-Shellcode-Execution preview

Remote-DLL-Injection-with-Timer-based-Shellcode-Execution

GitHubandreisss/remote-dll-injection-with-timer-based-shellcode-execution

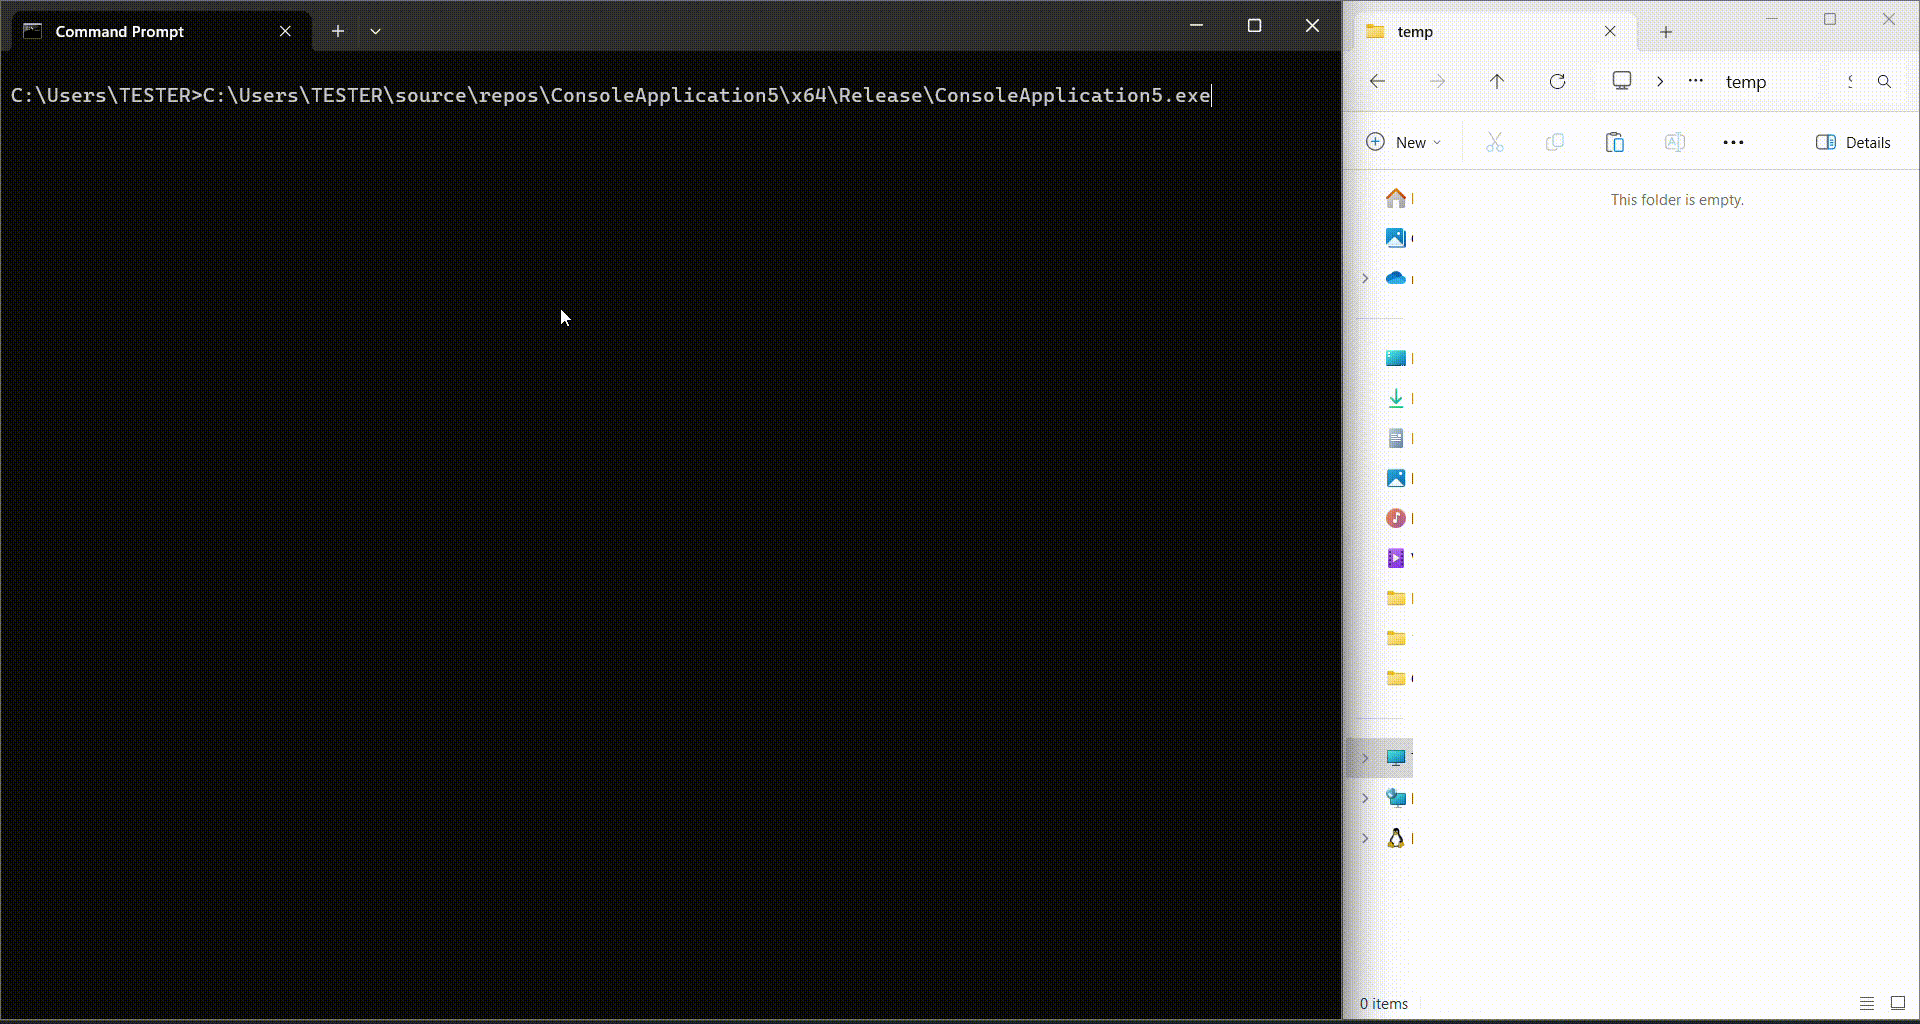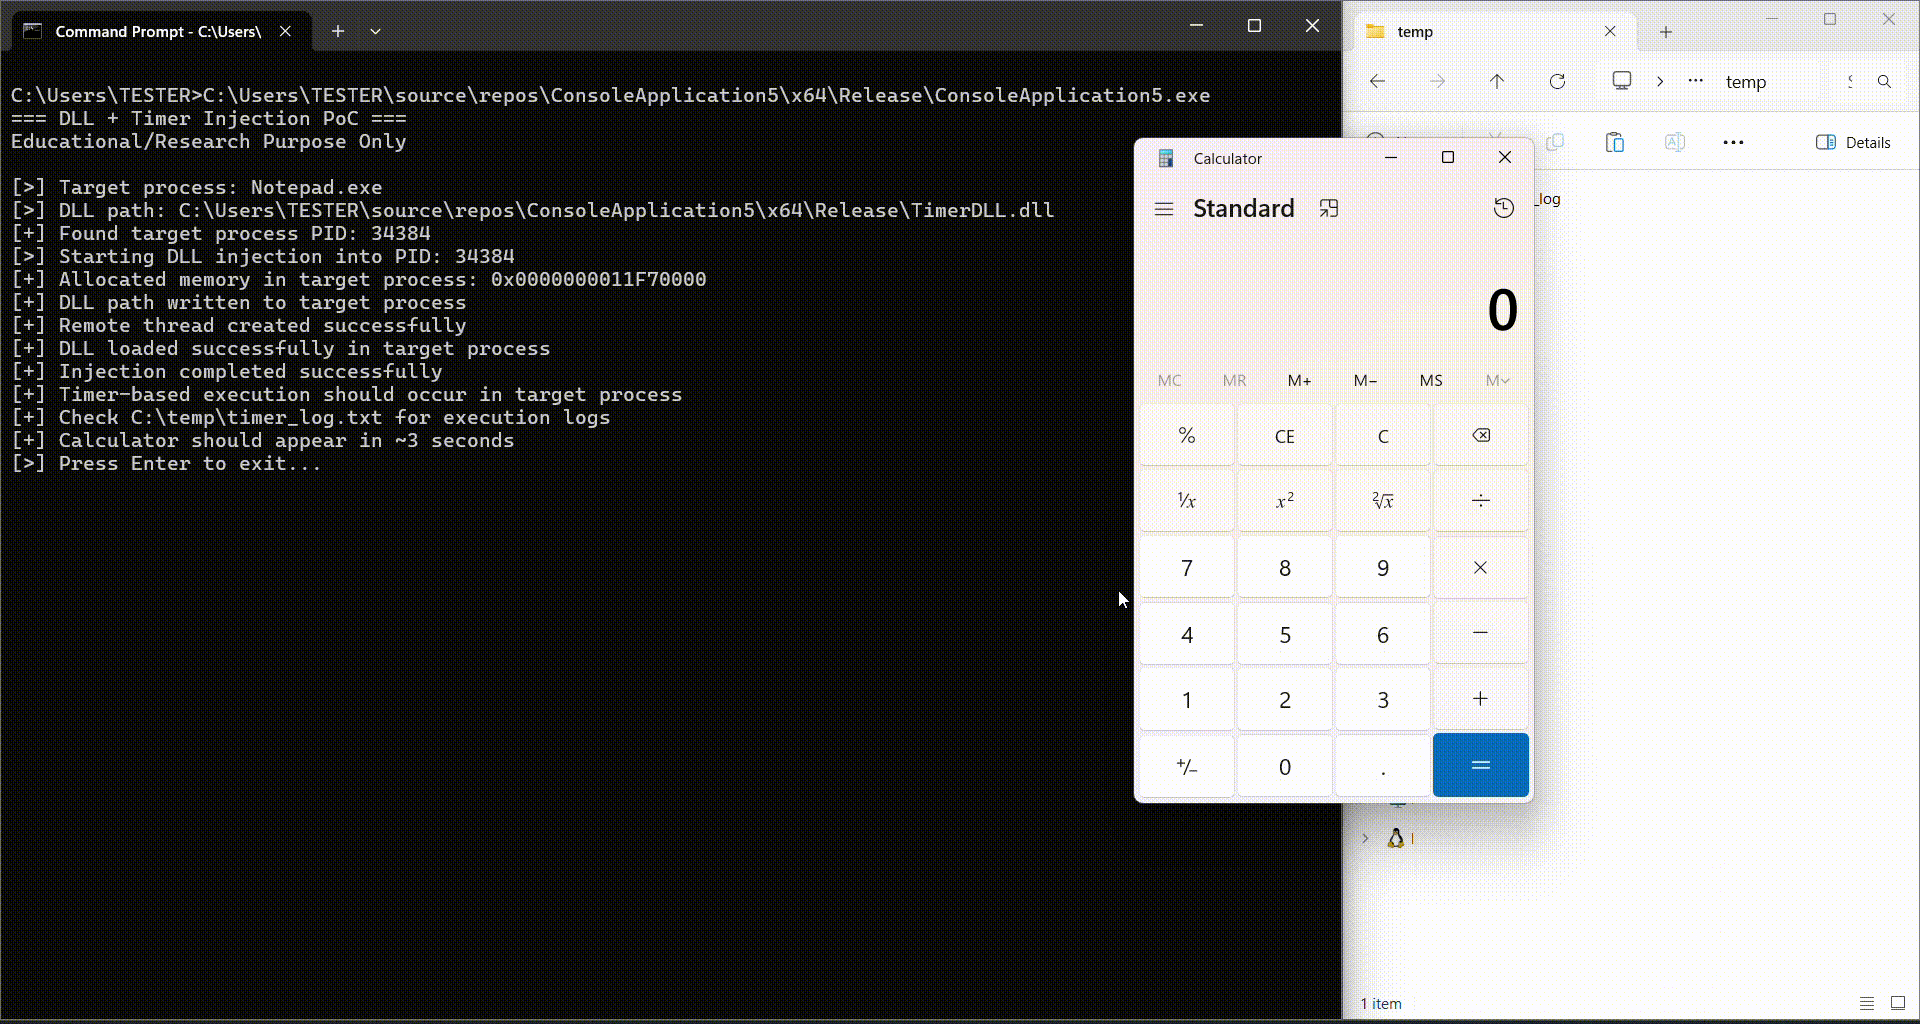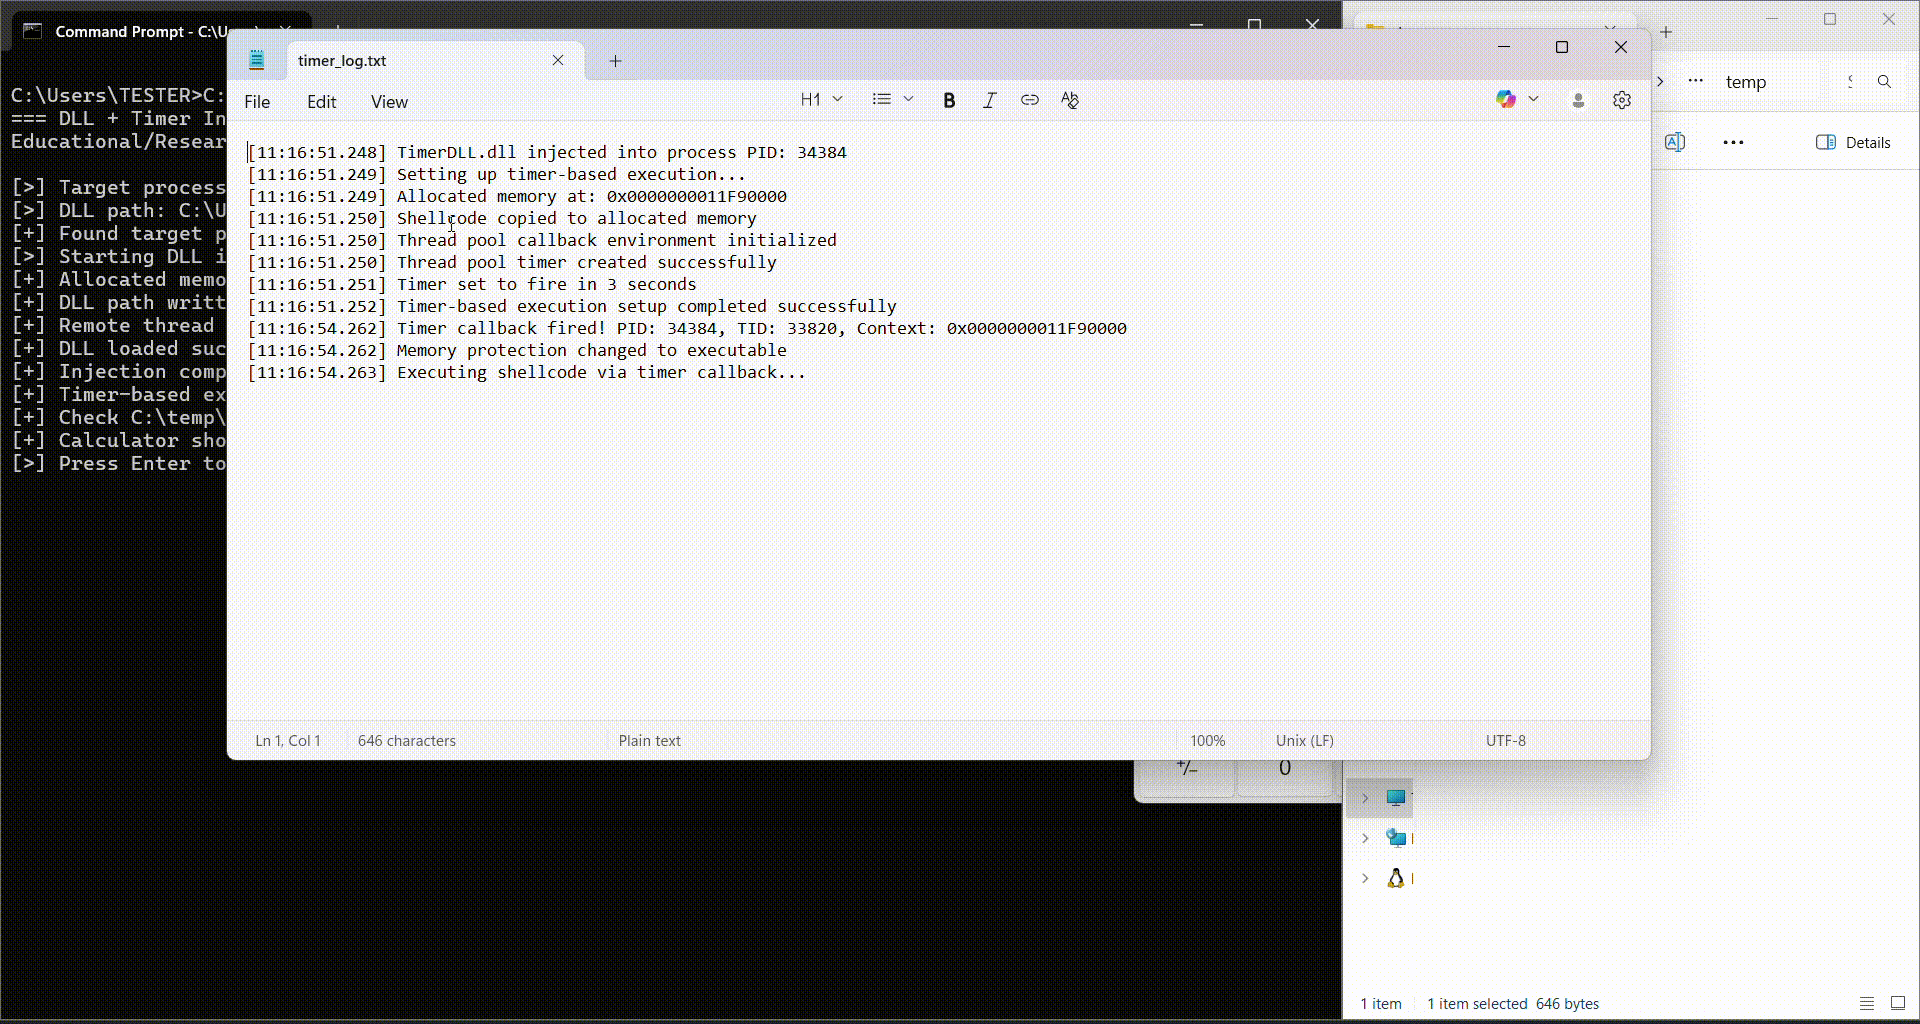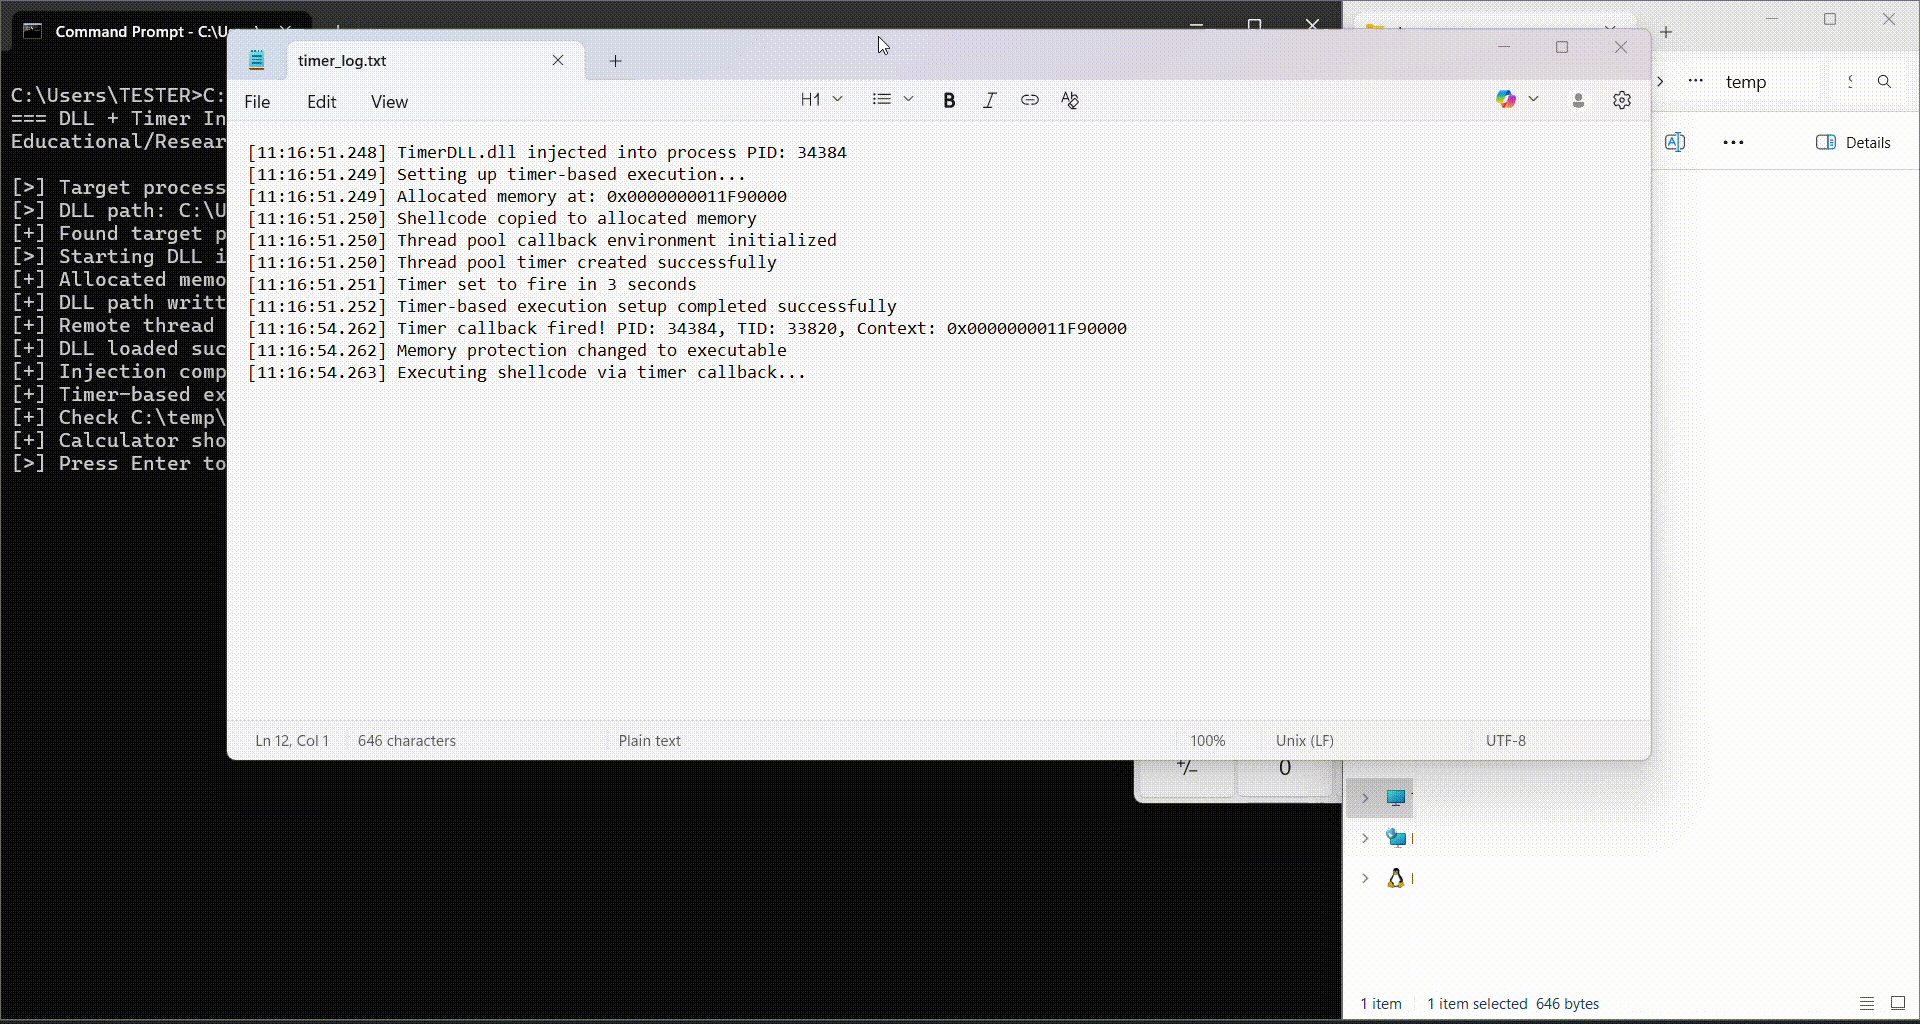
रिमोट DLL इंजेक्शन, टाइमर-आधारित शेलकोड निष्पादन के साथ

exploitationshellcodepost-exploitation+3
2161 साल पहले
पिछला1…111213…48अगला








