
 #1
LLM सुरक्षा, प्रॉम्प्ट इंजेक्शन, मॉडल एक्सट्रैक्शन, एडवर्सरियल AI और AI रेड टीमिंग उपकरण।
Kitploit अनुशंसित

 tencentcloud/cubesandbox
Instant, Concurrent, Secure & Lightweight Sandbox for AI Agents.
 huhusmang/awesome-llms-for-vulnerability-detection
समुदाय का सबसे व्यापक, निरंतर अद्यतन होने वाला सूचकांक जो सॉफ्टवेयर भेद्यता पहचान के लिए लार्ज लैंग्वेज मॉडल्स पर शोध को दर्शाता है — फ़ंक्शन-स्तर,…
 vmoranv/jshookmcp
A search-first, profile-aware reverse-engineering workspace for AI agents — 735 tools across 36 domains in one MCP server.
 linuztx/alter-zero
RAM efficient terminal agent harness for coding, cybersecurity, and automation.
 cdxgen/cdxgen
Creates CycloneDX Bill of Materials (BOM) for your projects from source and container images. Supports many languages and package managers. Integrate…
 qbnasasn/google-tensor-chips
Google Tensor Cracks
 giskard-ai/giskard-oss
🐢 LLM एजेंटों के लिए ओपन-सोर्स मूल्यांकन एवं परीक्षण लाइब्रेरी
 tencent/ai-infra-guard
एक फुल-स्टैक AI Red Teaming प्लेटफ़ॉर्म जो Agent Scan, Skills Scan, MCP scan, AI Infra scan और LLM jailbreak evaluation के माध्यम से AI इकोसिस्टम को…
 provos/ironcurtain
स्वायत्त AI एजेंटों के लिए एक सुरक्षित* रनटाइम। सरल अंग्रेज़ी संविधानों से नीति। (*https://ironcurtain.dev)
 goochbeater/spiritual-spell-red-teaming
विभिन्न LLM, मुख्य रूप से Claude को जेलब्रेक करने के लिए एक रेपो
 ascit31/dark-moon
Autonomous AI pentesting engine, continuous offensive security across web, cloud, AD & Kubernetes. Agentic reasoning + real exploit execution deliver…
 nuguardai/nuguard
opensource repo for validating agentic AI applications: redteam, behavior, supply-chain, static analysis एजेंटिक AI अनुप्रयोगों को मान्य करने के लिए…
 google-github-actions/run-gemini-cli
Gemini CLI को आह्वान करने वाली एक GitHub Action।
 hevnsnt/cvengine
AI-first external attack surface assessment with continuous discovery, evidence-based vulnerability validation, and developer-agent MCP integration.
 gautamvarmadatla/mcpsafetywarden
प्रॉक्सी सर्वर जो MCP सर्वर को व्यवहारिक प्रोफाइलिंग, सुरक्षा स्कैनिंग, जोखिम गेटिंग और सुरक्षित निष्पादन के साथ लपेटता है। प्रॉम्प्ट इंजेक्शन,…
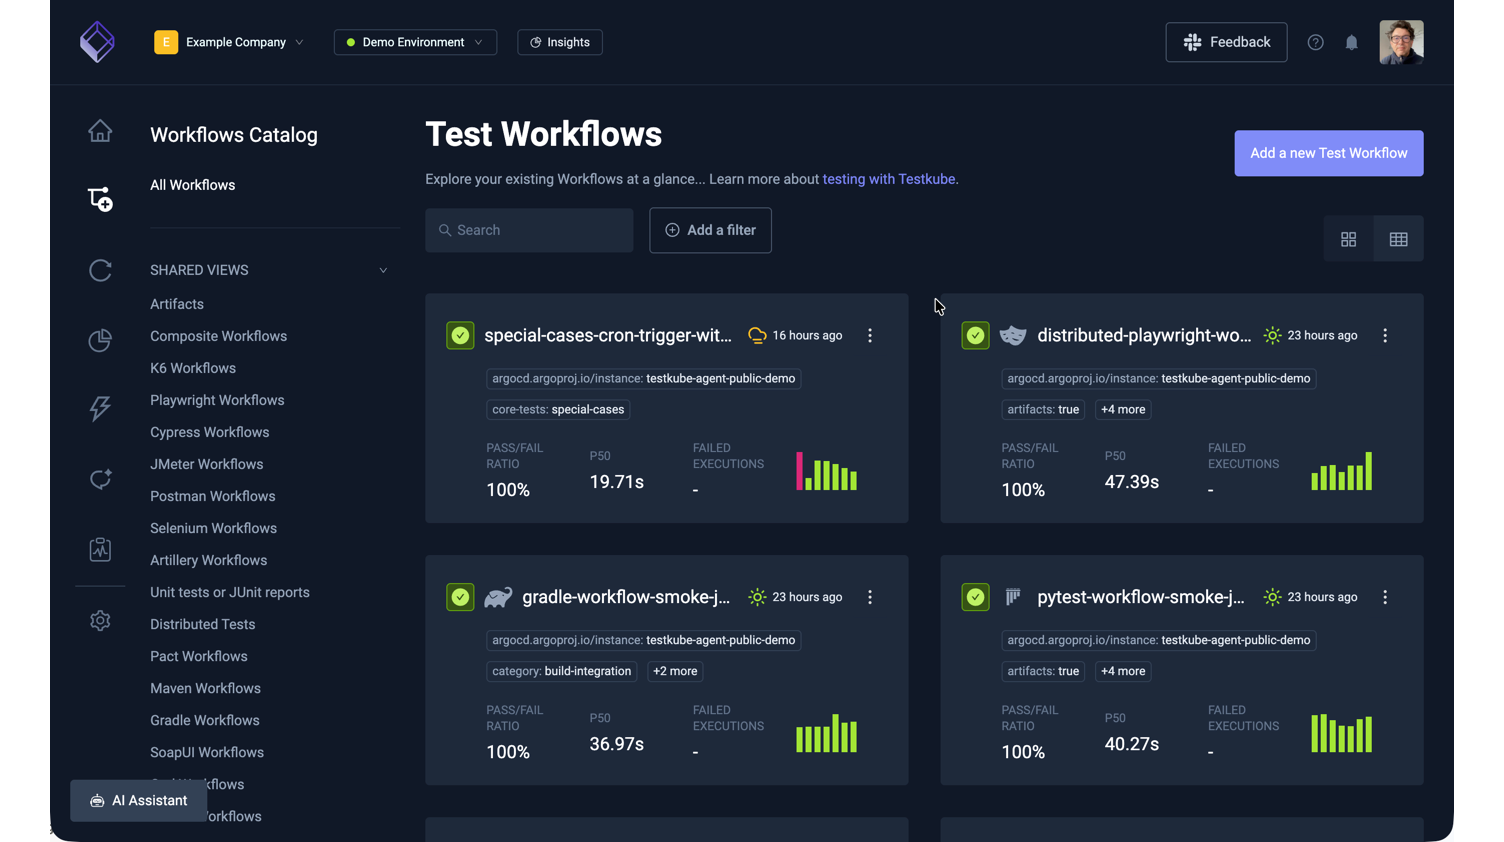 kubeshop/testkube
☸️ एजेंटिक SDLC के लिए परीक्षण प्लेटफ़ॉर्म
 rderaison/bromure
एजेंटिक कोडिंग और वेब ब्राउज़िंग के लिए उचित सैंडबॉक्सिंग






