 checkmk1/checkmk_php2shell
Checkmk extension with an agent plug-in that inventories PHP binaries and Apache mod_php on Linux hosts and reports PHP2Shell (CVE-2026-109618/109619) status, backports and stale processes.

A Checkmk extension that shows, for every PHP installation on a Linux host, whether it is affected by PHP2Shell - the pre-authentication remote code execution vulnerabilities CVE-2026-109618 and CVE-2026-109619, disclosed and fixed on 2026-10-21 in PHP 8.2.35, 8.3.36, 8.4.27 and 8.5.12.
It ships a small POSIX shell agent plug-in that only collects facts (PHP binaries,
PHP libraries of Apache mod_php, NGINX Unit and FrankenPHP, versions, package changelogs,
php.ini settings, processes still running a replaced binary). Whether that means "fixed"
or "vulnerable" is decided by the check plug-in on the Checkmk server, so new
information - another fixed release, a new CVE - only needs an updated .mkp, not a new
script on every host.
Why not just compare version numbers: distributions backport the fix without changing the upstream version. Ubuntu 24.04 ships PHP 8.3.6 and AlmaLinux 9 ships 8.0.30 - both fixed, both "vulnerable" by version. The extension therefore also reads the changelog of the package that owns each binary.
cmk_addons.plugins plugin API)./proc/<pid>/maps of all processes). Plain POSIX sh with GNU or
busybox tools; package changelogs are read with dpkg, rpm or apk. Tested on the
Debian family (Debian, Ubuntu), the Red Hat family (RHEL, AlmaLinux, Rocky Linux,
Oracle Linux, CentOS Stream, Fedora, Amazon Linux 2023, CentOS 7) and Alpine, see below.| Checkmk image | Date | Result |
|---|---|---|
checkmk/check-mk-ultimate:2.5.0p17 | 2026-10-28 | OK (build, cmk-validate-plugins, smoke test) - release 1.1.2 |
checkmk/check-mk-ultimate:3.0.0-2026.10.28 (daily) | 2026-10-28 | OK (build, cmk-validate-plugins, smoke test) - release 1.1.2 |
checkmk/check-mk-ultimate:2.5.0p17 | 2026-10-27 | OK (build, cmk-validate-plugins, smoke test, install + discovery + check + agent bake) |
checkmk/check-mk-ultimate:3.0.0-2026.10.27 (daily) | 2026-10-27 | OK (build, cmk-validate-plugins, smoke test, install + discovery + check + agent bake) |
The agent plug-in was run against the distributions' own PHP packages on 2026-10-27
(scripts/test_agent_plugin.sh). Where a target starts the web SAPIs (FPM, Apache mod_php
where the distribution still ships it, NGINX Unit, FrankenPHP), the FPM binary and libphp
were replaced on disk afterwards, and the restart detection reported the running processes.
Debian family and Alpine
| Distribution | PHP packages | Plug-in result |
|---|---|---|
| Ubuntu 24.04 | 8.3.6-0ubuntu0.24.04.13 (CLI, FPM, CGI, mod_php) | fixed by backport (changelog names both CVEs) |
| Debian 12 | 8.2.35-1~deb12u1 (CLI, FPM, mod_php) | fixed by version |
| Debian 12 + nginx | 8.2.35-1~deb12u1 (CLI, FPM behind nginx) | fixed by version |
| Debian 13 | 8.4.27-1~deb13u1 (CLI, FPM) | fixed by version |
| Alpine 3.22 | php83 8.3.36-r0 (CLI, FPM, CGI) | fixed by version |
Red Hat family
| Distribution | PHP packages | Plug-in result |
|---|---|---|
| AlmaLinux 8.10 | 7.2.24-1.module_el8.10.0 (CLI, FPM, CGI, mod_php libphp7.so) | fixed by backport (changelog names both CVEs) |
AlmaLinux 8.10, module php:8.2 | 8.2.35-1.module_el8.10.0 (CLI, FPM, CGI) | fixed by version |
| RHEL 9.8 (UBI), AlmaLinux 9.8, Rocky Linux 9.8, Oracle Linux 9.8 | 8.0.30-8.el9_8.1 (CLI, FPM, CGI) | fixed by backport (changelog names both CVEs) |
AlmaLinux 9.8, module php:8.3 | 8.3.36-1.module_el9.8.0 (CLI, FPM, CGI) | fixed by version |
| AlmaLinux 9.8 + Remi SCL | php74 7.4.33-31.el9.remi, php81 8.1.34-6.el9.remi (/opt/remi) | fixed by backport (changelog names both CVEs) |
| AlmaLinux 10.2, CentOS Stream 10 | 8.3.36-1.el10 (CLI, FPM, CGI) | fixed by version |
| Fedora 44 | 8.5.12-1.fc44 (CLI, FPM, CGI) | fixed by version |
| Amazon Linux 2023 | php8.5 8.5.12-1.amzn2023.0.1 (CLI, FPM, CGI) | fixed by version |
| CentOS 7 (end of life, vault) | 5.4.16-48.el7 (CLI, FPM, CGI) | vulnerable - no backport for EL7 outside paid extended support |
Official container images and FrankenPHP
| Image | PHP | Plug-in result |
|---|---|---|
php:8.2.20-fpm | 8.2.20, built from source | vulnerable |
unit:php8.3 (NGINX Unit) | 8.3.26 (CLI, CGI, embedded libphp) | vulnerable |
dunglas/frankenphp:latest | 8.5.12 (CLI, CGI, embedded libphp) | fixed by version |
| FrankenPHP static binary (GitHub release) | 8.5.12 | fixed by version |
It has not yet run on a production host outside containers - in particular not with SELinux enforcing (RHEL family); the agent normally runs unconfined there.
Download the .mkp from a release (or build it yourself, see
Development).
Setup > Maintenance > Extension packages > Upload package, or on the command line inside the site:
mkp add php2shell-<version>.mkp
mkp enable php2shell <version>
Deploy the agent plug-in to the hosts you want to check:
Run a service discovery on the hosts. Every PHP binary and Apache PHP module gets its
own service, plus one PHP2Shell restart service per host.
Optional: adjust the states in Setup > Services > Service monitoring rules > PHP2Shell (CVE-2026-109618 / CVE-2026-109619) and PHP2Shell restart.
Copy package/agents/plugins/php2shell into a cache-interval subdirectory of the agent's
plug-in directory and make it executable:
install -m 755 php2shell /usr/lib/check_mk_agent/plugins/3600/php2shell
The 3600 directory makes the agent run it in the background once an hour and serve the
cached result in between. Do not put it directly into plugins/: it runs every PHP binary
and reads the memory map of every process, which is too much for every agent query.
| Service | One per | States (default, configurable) |
|---|---|---|
PHP2Shell <path> | PHP binary or library, e.g. PHP2Shell /usr/sbin/php-fpm8.3 | OK fixed - CRIT vulnerable web SAPI - WARN vulnerable web SAPI with all interim mitigations - WARN vulnerable CLI - UNKNOWN version not determinable |
PHP2Shell restart | host with PHP | OK - CRIT processes still run a replaced PHP binary or libphp |
The screenshots come from a Checkmk 2.5.0p17 test site whose four hosts get the recordings in sample-data/ instead of a real agent (no real hosts): Ubuntu 24.04 and AlmaLinux 8 fixed by backport but not restarted, CentOS 7 without any fix, and NGINX Unit with an outdated PHP.
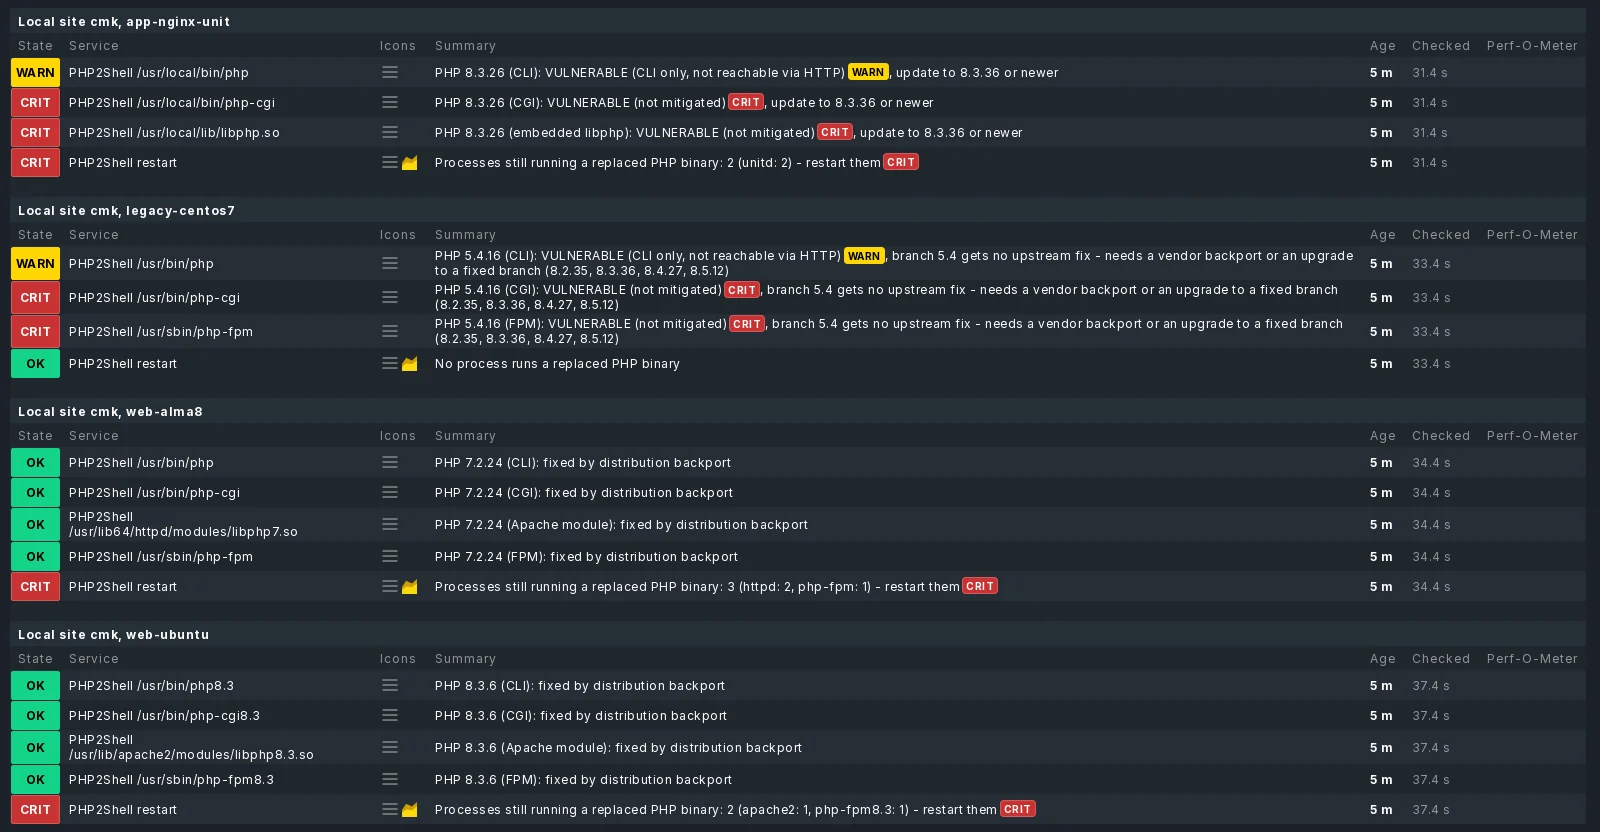
The details of a service name the missing interim mitigations, the package and what its changelog says:






