Skip to content
KitploitKITPLOIT
OutilsExploitsBlog
Log in
Soumettre
OutilsExploitsBlog
Soumettre

Outils de Hacking, PenTest et Cybersécurité pour votre Arsenal de Sécurité !

Kitploit est un répertoire d'outils de hacking, de cybersécurité et de pentesting. Découvrez les dernières mises à jour des projets pour trouver des vulnérabilités, analyser des systèmes, automatiser les tests et renforcer votre sécurité.

FluxContactConfidentialité© 2026 Kitploit

Répertoire d'outils

Catégories

Voir toutes les catégories
Loading categories
Outils/GitHubGitHub/vxlang/vxlang-page
Reverse Engineering
GitHubvxlang/vxlang-page

vxlang-page

Code obfuscation, virtualization, and anti-tamper protector for x86-64 Windows binaries (EXE/DLL/SYS) and .NET modules, with beta ELF support. Features code flattening, memory encryption, and multi-VM engine.

Voir le dépôtSite web
7665036il y a 3 joursVérifié par Kitploit
Partager
Contenu non disponible dans la langue demandée. Affichage de la version anglaise.

VxLang


  • Contents
    • Docs
    • What is VxLang?
    • Supported File Formats
    • Preview
      • Virtualization Preview
      • Dual-Mode Preview
      • Obfuscation Preview
      • Code-Flattening Preview
      • Runtime Code Encryption
    • How to get the full version
      • Donate and Subscription
        • Patreon
          • Link
          • Event

Document

  • Link

What is VxLang?

VxLang is a binary protection solution designed to make reverse engineering and tampering with Windows executables more difficult. It combines technologies such as executable packing, code obfuscation, code virtualization, control-flow flattening, and Runtime Code Encryption to protect important code and data.

The VxLang project currently targets x86-64 system and .NET binaries, native binary files for the Microsoft Windows operating system, including executables with the ".exe" extension, dynamic link library files with the ".dll" extension, and kernel driver files with the ".sys" extension. (The types of target binaries supported by vxlang will be expanded in future updates).

  • Added beta code for the ELF file format.
    • The beta version only supports general code-flattening.
    • Beta features require users to specify target code.
    • VxLang recommends using the -fno-pic option in ELF 32bit binary builds.

Supported File Formats

Windows EXE/DLL Windows Kernel Drive
Obfuscator Obfuscator
Virtualizer Virtualizer
Protector Protector
Windows UEFI Modules Windows .NET
Obfuscator Obfuscator
Virtualizer Virtualizer
Protector Protector
Linux ELF
Obfuscator
Virtualizer
Protector

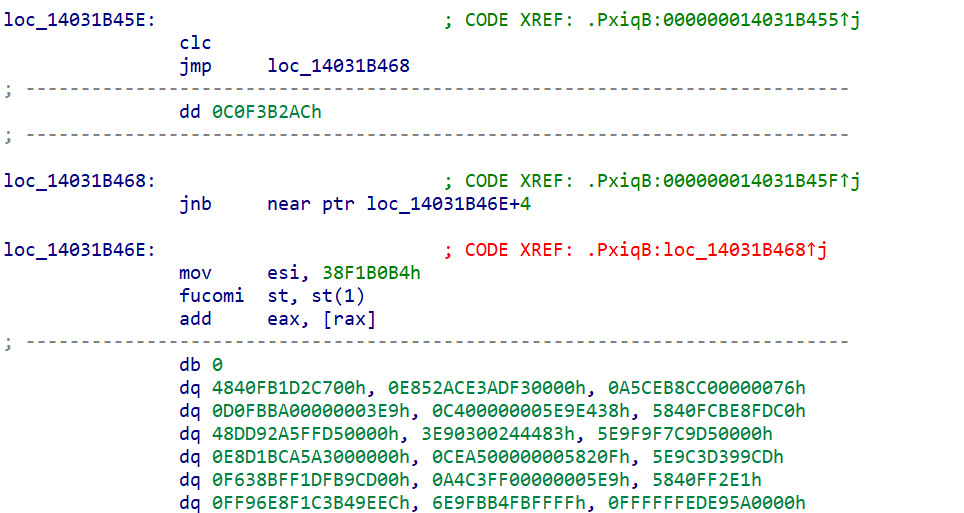
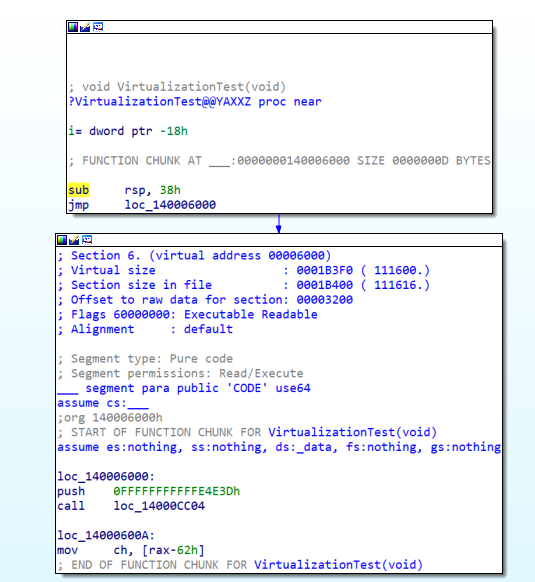
Virtualization Preview

; x86-64 asm
cmp         qword ptr [rsp + 0x20], rax
jae         0x140001bf5
mov         rax, qword ptr [rsp + 0x20]
movzx       eax, byte ptr [rsp + rax + 0x50]
; to v-asm
movi   exr_0, ${RANDOM}
movi   r7, ${RANDOM}
xorr   r7, exr_0
movi   exr_0, ${RANDOM}
movi   exr_1, ${RANDOM}
xorr   exr_0, exr_1
mulr   r7, exr_0
addr   r6, r7
movi   exr_0, ${RANDOM}
movi   r7, ${RANDOM}
xorr   r7, exr_0
addr   r6, r7
movr   r0, r6
movr   r1, rax
ldrr   r2, r0
cmpr   r2, r1
be     0x2c59
movr   r0, rax
movr   r6, rsp
movi   exr_0, ${RANDOM}
movi   r7, ${RANDOM}
xorr   r7, exr_0
movi   exr_0, ${RANDOM}
movi   exr_1, ${RANDOM}
xorr   exr_0, exr_1
mulr   r7, exr_0
addr   r6, r7
movi   exr_0, ${RANDOM}
movi   r7, ${RANDOM}
xorr   r7, exr_0
addr   r6, r7
movr   r1, r6
ldrr   r2, r1
movr   rax, r2
; compile
e7 f8 f1 e5 01 e1 a2 9a 22 87 c3 93 61 e5 06 e1
a2 9a 22 87 c3 93 61 eb 06 01 e6 01 e0 a2 9a 22 
e6 0a e1 a2 9a 22 ec 01 0a d6 06 01 da 07 06 e5 
01 e1 a2 9a 22 87 c3 93 61 e5 06 c1 a2 9a 22 87 
c3 93 61 eb 06 01 da 07 06 e7 f7 f8 e7 fc e5 c6 
00 08 a9 00 03 bb c6 01 00 00 e7 f7 e5 e7 f8 f1 
e5 01 6d 86 d3 6d 7f 86 9d a2 e5 06 6d 86 d3 6d 
7f 86 9d a2 eb 06 01 e6 01 6c 86 d3 6d e6 0a 6d 
86 d3 6d ec 01 0a d6 06 01 da 07 06 e5 01 6d 86 
d3 6d 7f 86 9d a2 e5 06 4d 86 d3 6d 7f 86 9d a2            

Before
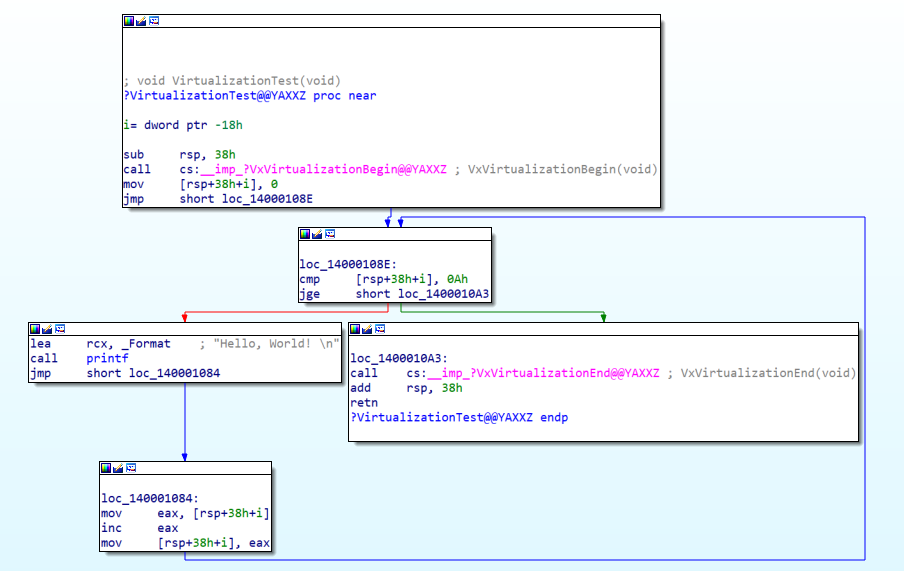
After
Dual-Mode(Obfuscation + Virtualization) Preview

Obfuscation Preview

Preview

Code-Flattening Preview

Before

After

Runtime Code Encryption

Télécharger l’outil

Populaires

Voir tout →

Découvrez les outils les plus utilisés par notre communauté.

  • 1

    OsintHunter

    letox4/osinthunter

    🎯 La boîte à outils OSINT ultime : graphe d'enquête, notation de confiance, familles d'alias, carte, chronologie et rapports. 49 modules, plus de 400 sites, aucune clé API requise.

    576
  • 2

    ghostlock-app

    yukonga/ghostlock-app

    # Application d'exécution en un clic GhostLock (CVE-2026-43499)

    477
  • 3

    ARTEX

    baarai/artex

    Plateforme autonome de tests d'intrusion multi-agents basée sur des LLM, avec agents planificateur/ouvrier, graphes d'actifs et d'exploration, enregistrement du trafic MITM et retest des vulnérabilités.

    388
  • 4

    redforge

    cybersecurity91/redforge

    Boîte à outils red team côté navigateur avec 102 outils hors ligne pour la reconnaissance, la génération de payloads, les attaques par identifiants, la cryptographie, l'encodage et le reporting d'engagement.

    330
  • 5

    CyberStrikeAI

    ed1s0nz/cyberstrikeai

    Le système d'action pour la cybersécurité native IA—où l'intention devient une exécution gouvernée, les preuves deviennent une mémoire opérationnelle, et chaque opération améliore la suivante.

    255
  • 6

    antifox

    antifox-ai/antifox

    Plateforme de test d'intrusion autonome multi-agents par IA qui exécute la reconnaissance, la découverte de la surface d'attaque, la validation de l'exploitation et la livraison de rapports étayés par des preuves.

    247

Explorer tous les outils

Parcourez notre collection d'outils

Voir tous les outils →