Skip to content
KitploitKITPLOIT
OutilsExploitsBlog
Log in
Soumettre
OutilsExploitsBlog
Soumettre

Outils de Hacking, PenTest et Cybersécurité pour votre Arsenal de Sécurité !

Kitploit est un répertoire d'outils de hacking, de cybersécurité et de pentesting. Découvrez les dernières mises à jour des projets pour trouver des vulnérabilités, analyser des systèmes, automatiser les tests et renforcer votre sécurité.

FluxContactConfidentialité© 2026 Kitploit

Répertoire d'outils

Catégories

Voir toutes les catégories
Loading categories
Kittysploit-framework — Python Exploitation Framework, V8 Engine Debugger, Proxy interceptor, marketplace, post-exploitation, backdoor generator,.... | Kitploit
Outils/GitHubGitHub/sia-iotechnology/kittysploit-framework
OSINT (Open Source Intelligence)Penetration Testing FrameworksReconnaissanceExploit FrameworksWeb Proxies & InterceptionDebuggersPost-ExploitationCommand and ControlRed TeamingPayload DevelopmentAI Security
5939873il y a 4 joursVérifié par Kitploit
Partager
GitHub
sia-iotechnology/kittysploit-framework

Kittysploit-framework

Python Exploitation Framework, V8 Engine Debugger, Proxy interceptor, marketplace, post-exploitation, backdoor generator,....
Voir le dépôtSite web
Contenu non disponible dans la langue demandée. Affichage de la version anglaise.
KittySploit logo

KittySploit

Exploitation and post-exploitation framework — one console.

Recon, scanning, exploits, interactive sessions, and post-exploitation across 60+ session connectors (shell, browser, databases, cloud, IoT/ICS, and more).
Python License Discord GitHub stars

Installation · Quick start · Full guide · Website

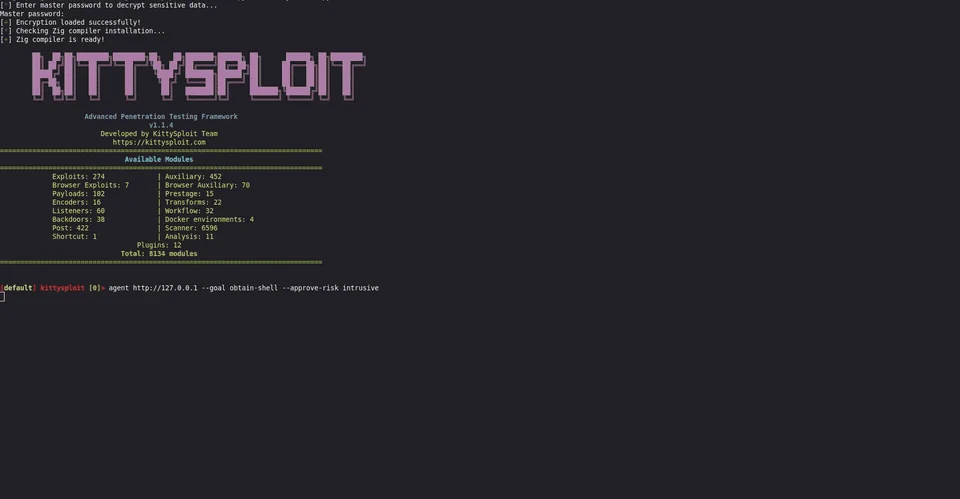
KittySploit — console, exploitation, and sessions

At a glance

StepWhat KittySploit does
1. FindWeb, network, cloud, and service scanners and recon
2. ExploitExploit modules, chains, and optional local-LLM agent
3. Post-exploit60+ session connectors — loot, pivot, persistence, enumeration

Everything stays in one console: modules, listeners, payloads, built-in C2, and reporting.

Use only on targets you own or are explicitly authorized to test.

Why KittySploit?

Typical stacks split the scanner, exploit framework, C2, and notes across different tools.

KittySploit brings them together: exploit to get a session, then run post-exploitation without switching apps.

Post-exploitation connector examples: Linux/Windows shell, browser (JS session), SSH, MySQL/PostgreSQL/Redis/MongoDB, SMB, FTP, Kubernetes, AWS/GCP/Azure, PHP webshell, WinRM, LDAP, BLE, MQTT, Modbus, BACnet, ONVIF, and more.

Module scale (approximate): thousands of scanners/auxiliary modules, 700+ exploits, 400+ post modules.

Installation

Linux and macOS

git clone https://github.com/SIA-IOTechnology/Kittysploit-framework.git
cd Kittysploit-framework
./install/install.sh
python3 kittyconsole.py

One-line install:

curl -fsSL https://raw.githubusercontent.com/SIA-IOTechnology/Kittysploit-framework/main/install/install-standalone.sh | bash

Windows

git clone https://github.com/SIA-IOTechnology/Kittysploit-framework.git
cd Kittysploit-framework
install\install.bat
python kittyconsole.py

Quick start

kittysploit> doctor
kittysploit> search cve:2024 type:exploit
kittysploit> use exploits/multi/http/...
kittysploit> run

kittysploit> sessions -l
kittysploit> sessions -i 1
kittysploit> search type:post platform:windows

Automated web mission (authorized lab):

kittysploit> agent https://lab.local

Shell goal on an internal lab:

kittysploit> agent http://192.168.56.10 \
  --profile internal-lab \
  --goal obtain-shell \
  --approve-risk intrusive \
  --shell-hunter

Use --plan-only or --dry-run to preview without intrusive actions.

Core features

  • Exploitation — search / use / run, payloads, listeners, exploit queues
  • Sessions and C2 — shells, callbacks, pivots, multi-session management
  • Post-exploitation — modules per session type (gather, manage, pivot, loot)
  • Agent (optional) — local LLM (Ollama), mission profiles, scope controls
  • Automation — CLI, API/RPC, and MCP for IDE or scripted workflows

Agent profiles, compound evidence, environment variables, and cookbooks are in USAGE.md.

Ecosystem

ProjectPurpose
KittyProxyHTTP capture and analysis
KittyCosmicGraphical interface
KittyOsintVisual OSINT
KittyProtocolProtocol analysis
KittyV8DebuggerV8 debugging

Demo video · Site and marketplace · Wiki

Community

  • Discord
  • Issues
  • Liberapay

The project is still evolving — validate in a lab before production engagements.

Acknowledgments

Thanks to Woody for their contributions.

License

Released under the MIT License.

Télécharger l’outil

Populaires

Voir tout →

Découvrez les outils les plus utilisés par notre communauté.

  • 1

    OsintHunter

    letox4/osinthunter

    🎯 La boîte à outils OSINT ultime : graphe d'enquête, notation de confiance, familles d'alias, carte, chronologie et rapports. 49 modules, plus de 400 sites, aucune clé API requise.

    755
  • 2

    ghostlock-app

    yukonga/ghostlock-app

    # Application d'exécution en un clic GhostLock (CVE-2026-43499)

    510
  • 3

    ARTEX

    baarai/artex

    Plateforme autonome de tests d'intrusion multi-agents basée sur des LLM, avec agents planificateur/ouvrier, graphes d'actifs et d'exploration, enregistrement du trafic MITM et retest des vulnérabilités.

    415
  • 4

    redforge

    cybersecurity91/redforge

    Boîte à outils red team côté navigateur avec 102 outils hors ligne pour la reconnaissance, la génération de payloads, les attaques par identifiants, la cryptographie, l'encodage et le reporting d'engagement.

    343
  • 5

    antifox

    antifox-ai/antifox

    Plateforme de test d'intrusion autonome multi-agents par IA qui exécute la reconnaissance, la découverte de la surface d'attaque, la validation de l'exploitation et la livraison de rapports étayés par des preuves.

    259
  • 6

    CyberStrikeAI

    ed1s0nz/cyberstrikeai

    Le système d'action pour la cybersécurité native IA—où l'intention devient une exécution gouvernée, les preuves deviennent une mémoire opérationnelle, et chaque opération améliore la suivante.

    258

Explorer tous les outils

Parcourez notre collection d'outils

Voir tous les outils →