
Skip to content
KitploitKITPLOIT
OutilsExploitsBlog
Log in
Soumettre
OutilsExploitsBlog
Soumettre

Outils de Hacking, PenTest et Cybersécurité pour votre Arsenal de Sécurité !

Kitploit est un répertoire d'outils de hacking, de cybersécurité et de pentesting. Découvrez les dernières mises à jour des projets pour trouver des vulnérabilités, analyser des systèmes, automatiser les tests et renforcer votre sécurité.

FluxContactConfidentialité© 2026 Kitploit

Répertoire d'outils

Catégories

Voir toutes les catégories
Loading categories
Rétro-ingénierie — Page 67 | Kitploit
Catégories

Rétro-ingénierie

Outils pour la décompilation, le désassemblage et la compréhension des mécanismes internes des malwares et des binaires complexes.

Recommandé par Kitploit
Meilleurs outils

10 sélectionnés
ghidra preview#1

ghidra

GitHubnationalsecurityagency/ghidra
71.1kil y a 1 jour
radare2 preview#2

radare2

GitHubradareorg/radare2
24.5kil y a 11h 34m
cutter preview#3

cutter

GitHubrizinorg/cutter
19.4kil y a 1 jour
rizin preview#4

rizin

GitHubrizinorg/rizin
4.1kil y a 13 jours
x64dbg preview#5

x64dbg

GitHubx64dbg/x64dbg
49.1kil y a 7 jours
ImHex preview#6

ImHex

GitHubwerwolv/imhex
54.4kil y a 27 jours
angr preview#7

angr

GitHubangr/angr
9.0kil y a 11h 56m
unicorn preview#8

unicorn

GitHubunicorn-engine/unicorn
9.2kil y a 8 mois
capstone preview#9

capstone

GitHubcapstone-engine/capstone
8.9kil y a 16h 38m
keystone preview#10

keystone

GitHubkeystone-engine/keystone
2.7kil y a 3 mois
Plus récentsPertinencePlus populairesMis à jour récemment
1868 résultats
vivo_iqoo_neo_9_root_research_on_CVE-2025-21479 preview

vivo_iqoo_neo_9_root_research_on_CVE-2025-21479

GitHublinux-tools/vivo_iqoo_neo_9_root_research_on_cve-2025-21479

Android kernel root exploit for iQOO Neo9 (CVE-2025-21479, Adreno GPU SDS) providing arbitrary physical write, kernel cap bypass, and root daemon/su…

android-securityprivilege-escalationexploitation+4
11il y a 1 mois
OpenShell preview

OpenShell

GitHubiss4cf0ng/openshell

Serveur de gestion de reverse shell léger basé sur Go avec une interface graphique web pour des sessions shell interactives, la gestion de sessions,…

reverse-engineeringweb-securitypenetration-testing+3
24il y a 8 mois
dae preview

dae

GitHubejfkdev/dae

Analyseur de snapshots AOT Dart piloté par configuration qui exporte des symboles et des structures compatibles blutter pour IDA, radare2 et Frida,…

android-securitystatic-analysisdynamic-analysis-sandboxing+6
13il y a 4 jours
eps-CVE-2017-0261 preview

eps-CVE-2017-0261

GitHubkcufid/eps-cve-2017-0261

Analyse et exploit PoC pour la vulnérabilité EPS CVE-2017-0261, y compris désassemblage IDA, documents intermédiaires et fichiers d'exploit originaux.
vulnerability-analysisexploitationreverse-engineering+2
10il y a 7 ans
CTFTiny preview

CTFTiny

GitHubnyu-llm-ctf/ctftiny

Dépôt officiel pour CTFTiny

reverse-engineeringforensicsweb-security+8
18il y a 7 mois
tandasat.github.io preview

tandasat.github.io

GitHubtandasat/tandasat.github.io

Cours à distance sur le développement d'hyperviseurs pour chercheurs en sécurité ; couvre les mécanismes internes de la virtualisation, la sécurité…
vulnerability-analysisreverse-engineeringsecurity-virtualization+2
19il y a 5 mois
BlackLotus-analysis-stage2-bootkit-rootkit-stage preview

BlackLotus-analysis-stage2-bootkit-rootkit-stage

GitHubspiralbl0ck/blacklotus-analysis-stage2-bootkit-rootkit-stage

Z2A-BlackLotus Challenge analyse du bootkit-rootkit de l'étape 2

static-analysisdynamic-analysis-sandboxingreverse-engineering+5
17il y a 3 ans
Sandroid_Dexray-Intercept preview

Sandroid_Dexray-Intercept

GitHubfkie-cad/sandroid_dexray-intercept

Un outil d'analyse de logiciels malveillants Android qui crée des profils d'exécution complets en s'accrochant au comportement des applications à…
android-securitydynamic-analysis-sandboxingdynamic-code-analysis+8
10il y a 12 jours
EAC-Kernel-Packet-Fucker preview

EAC-Kernel-Packet-Fucker

GitHubgmh5225/eac-kernel-packet-fucker

Contournement du pilote noyau Easy Anti-Cheat rétro-ingénieré qui intercepte l'allocation mémoire pour supprimer les paquets de violation, avec des…
encryption-decryption-toolsmemory-forensicsexploitation+6
17il y a 4 ans
windows-x86-shellcode-poc preview

windows-x86-shellcode-poc

GitHubnataliadiak/windows-x86-shellcode-poc

Windows x86 PoC : Débordement de tampon basé sur la pile avec shellcode personnalisé sur Windows 32 bits legacy.
vulnerability-analysisreverse-engineeringshellcode+3
8il y a 5 mois
cve-2023-33476 preview

cve-2023-33476

GitHubmellow-hype/cve-2023-33476

Exploits pour un débordement de tas dans MiniDLNA <=1.3.2 (CVE-2023-33476)

embedded-systems-securityvulnerability-analysisexploitation+3
19il y a 3 ans
agent preview

agent

GitHubbinref/agent

Instructions de l'agent modèle de langage pour Binary Refinery

reverse-engineeringscripting-automationmalware-analysis+2
13il y a 1 mois
MCPDebugger preview

MCPDebugger

GitHubfatmike-gh/mcpdebugger

Un serveur de débogage MCP pour exécutables Windows (x86 et x64). Expose les fonctionnalités de débogage en tant qu'outils MCP pour l'analyse…

static-analysisdynamic-analysis-sandboxingmemory-forensics+4
13il y a 7 mois
frida-il2cpp-datacollector preview

frida-il2cpp-datacollector

GitHubgmh5225/frida-il2cpp-datacollector

Outil basé sur Frida qui porte MonoDataCollector de Cheat Engine vers Android et iOS, permettant la collecte de données Mono/IL2CPP à l'exécution et…
android-securitydynamic-analysis-sandboxingios-security+5
13il y a 4 ans
pyrmax preview

pyrmax

GitHubinfobyte/pyrmax

Décodeur/encodeur pour les trames du protocole sans fil Ubiquiti AirMAX ; analyse des captures pcap/en direct, découverte de périphériques, recherche…

vulnerability-scannersreverse-engineeringfuzzing+2
3il y a 3 mois
ReflectivePluginLoader preview

ReflectivePluginLoader

GitHubracoten/reflectivepluginloader

Mappeur PE réflectif Windows x64 minimal qui charge des DLL depuis la mémoire sans LoadLibrary, résout les exports et distribue les appels via une…
defensive-toolspersistence-mechanismsreverse-engineering+7
5il y a 17 jours
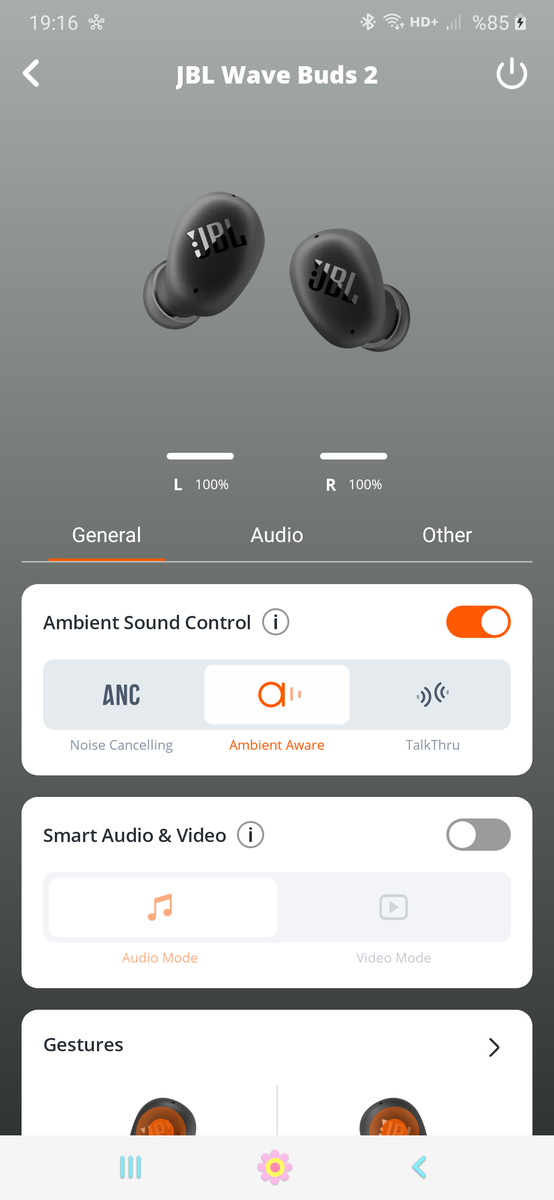
jbl-wave-buds2-firmware-research preview

jbl-wave-buds2-firmware-research

GitHubc8dhjp4tyv-bit/jbl-wave-buds2-firmware-research

Reverse-engineering notes and Python tooling for JBL Wave Buds 2 (BES1306) firmware: OTA container format, flash layout, BLE/GATT protocol, and…

embedded-systems-securitybluetooth-securityiot-security+7
9il y a 7 jours
libmempool preview

libmempool

GitHubnccgroup/libmempool

Outil d'analyse du tas pour mempool

embedded-systems-securitymemory-forensicsreverse-engineering+3
13il y a 4 ans
Précédent1…666768…100Suivant








