tiliondev/fortress
Motor Chromium sigiloso que evita que los scrapers y agentes de navegador sean bloqueados, con un solo cambio de línea de código.


Stealth Chromium engine · v3 (Chromium 153)


Fortress is a Chromium fork that stops scrapers and browser agents from getting blocked. Bot detectors flag automation by reading the browser fingerprint. Fortress corrects that fingerprint inside Chromium's C++, so the browser reads as an ordinary Chrome install. Point your existing Playwright or Puppeteer at it over CDP; nothing else in your code changes.
Headless, on datacenter IPs, with no proxies, Fortress loaded 86.4% of 92 protected sites. The next best stack (Camoufox) loaded 74.5%.
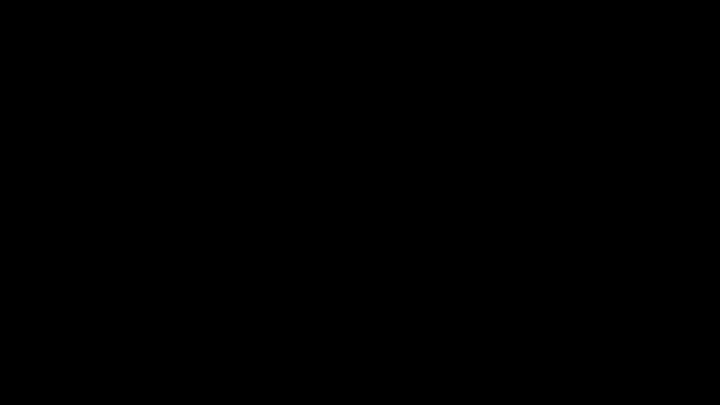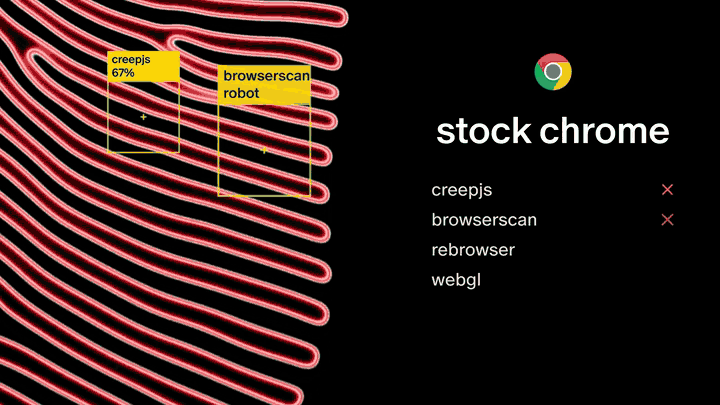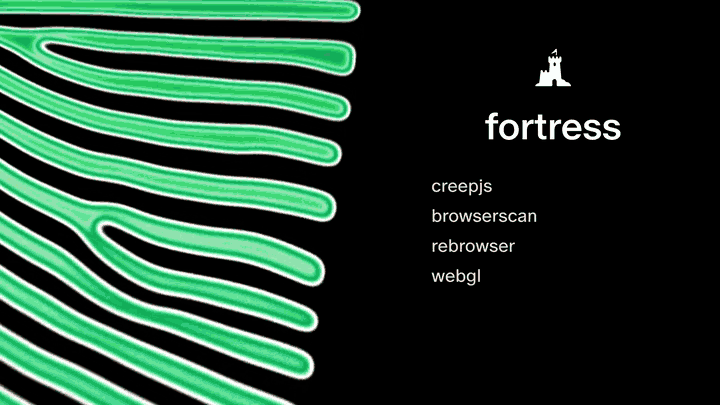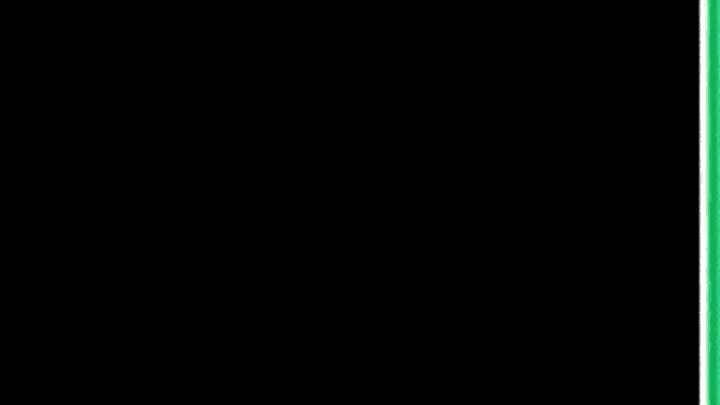
A site reads the fingerprint. Stock Chrome driven by a script fails CreepJS, BrowserScan, rebrowser and the WebGL check and is blocked; Fortress passes all four.
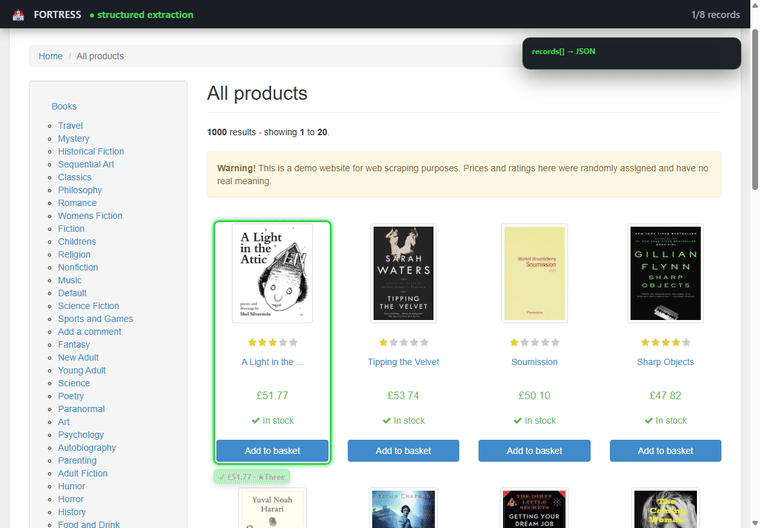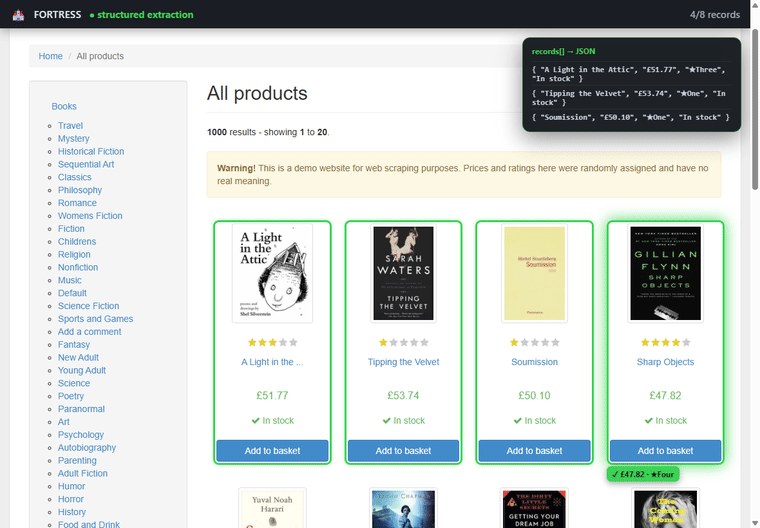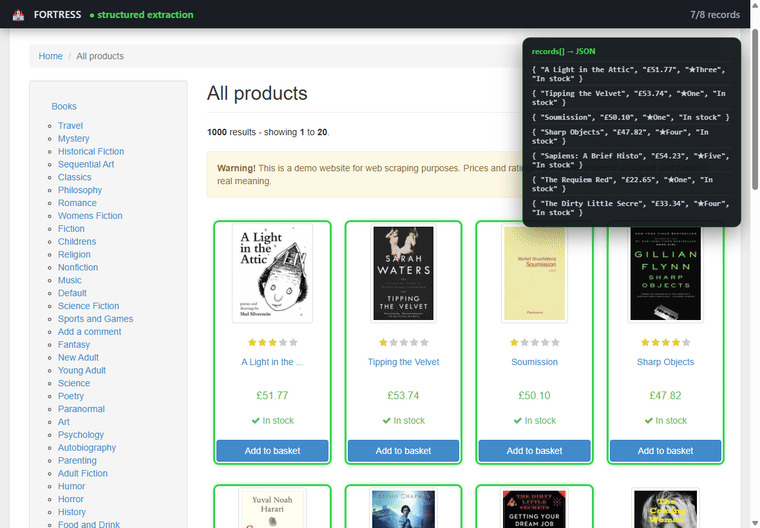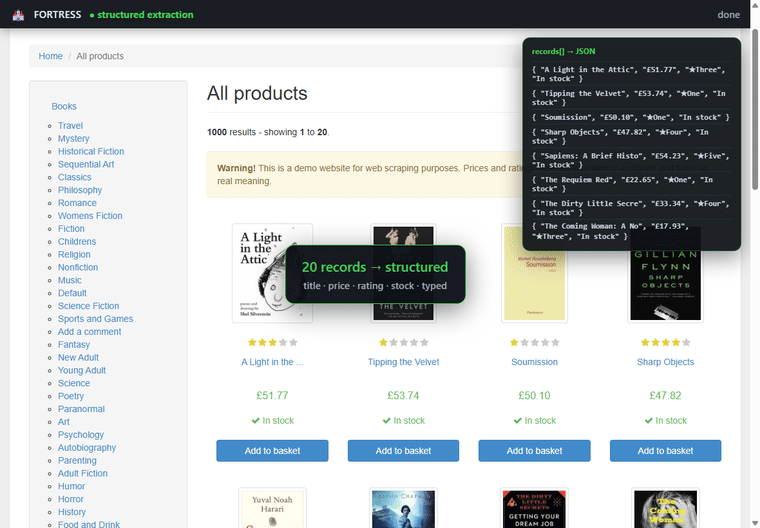
Unedited captures over CDP, with no stealth plugins. Reproduce with examples/scrape_demos.py.
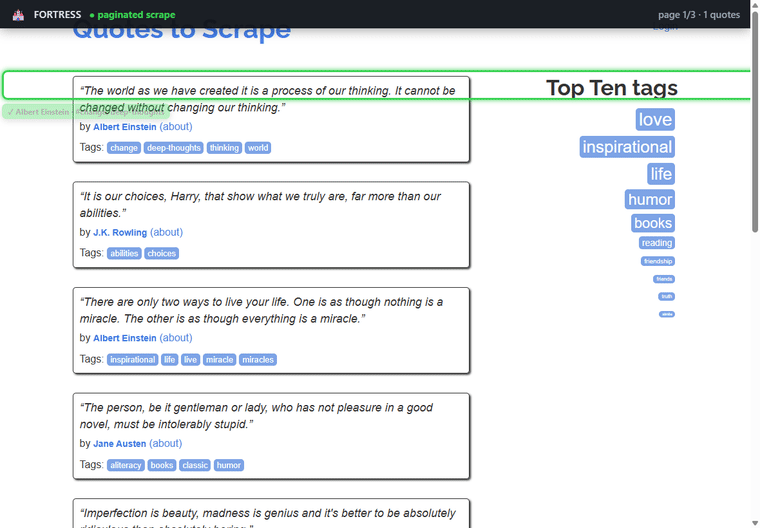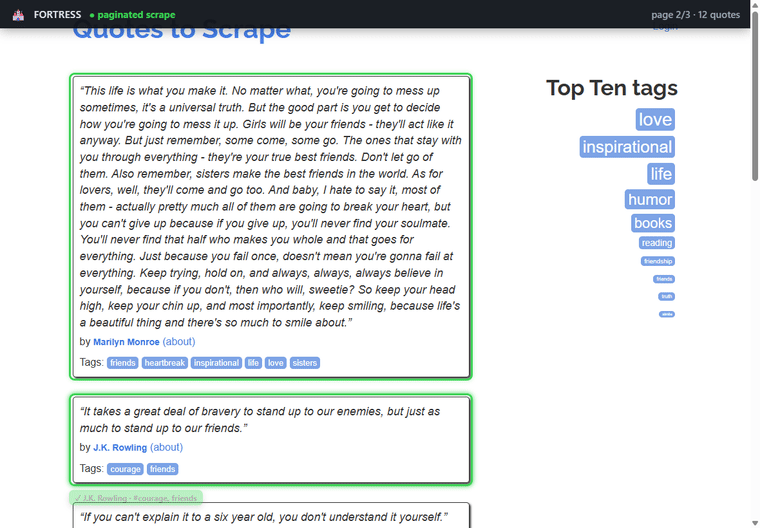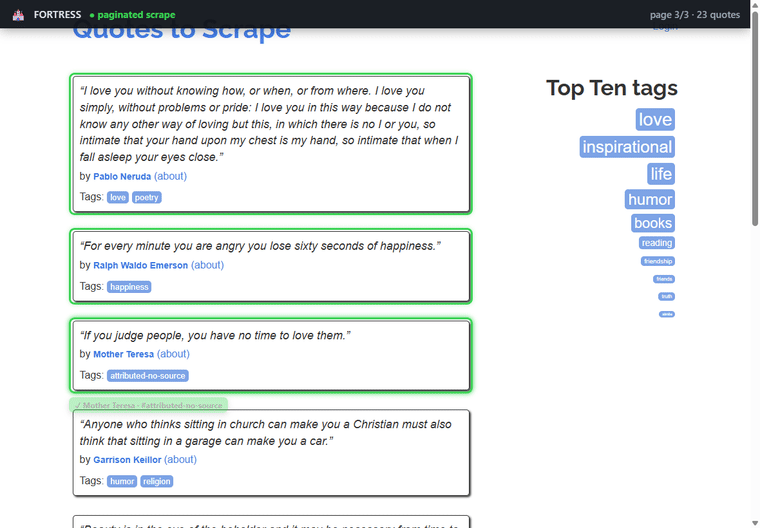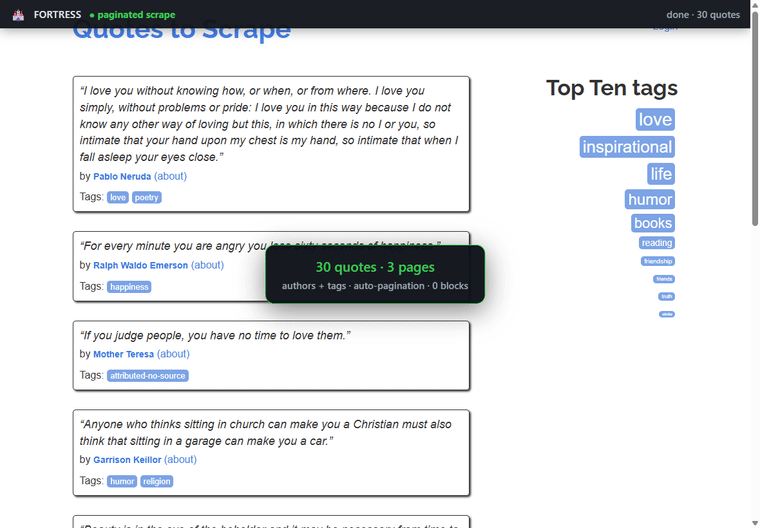 Auto-pagination: 30 quotes across 3 pages. |
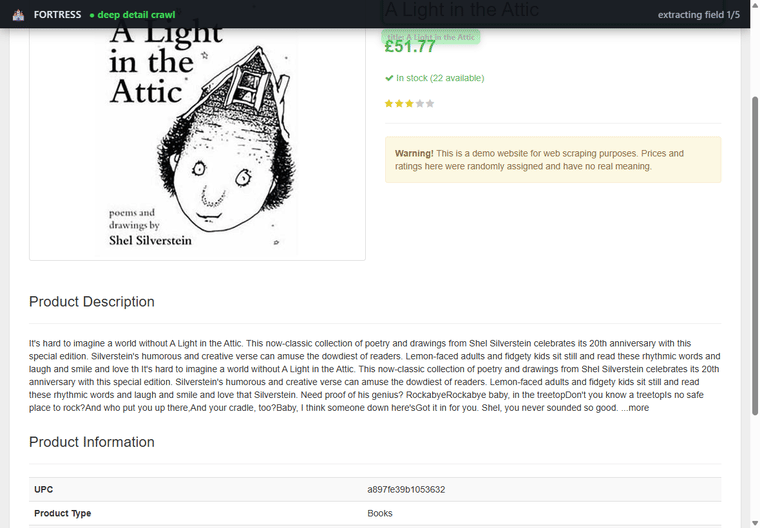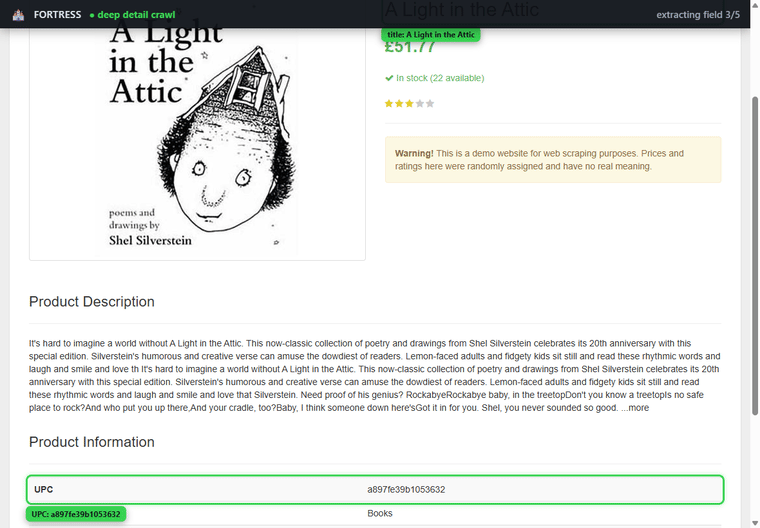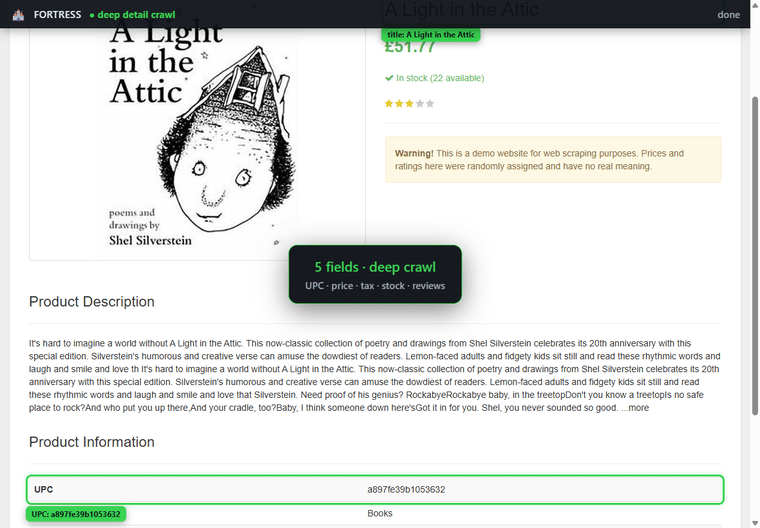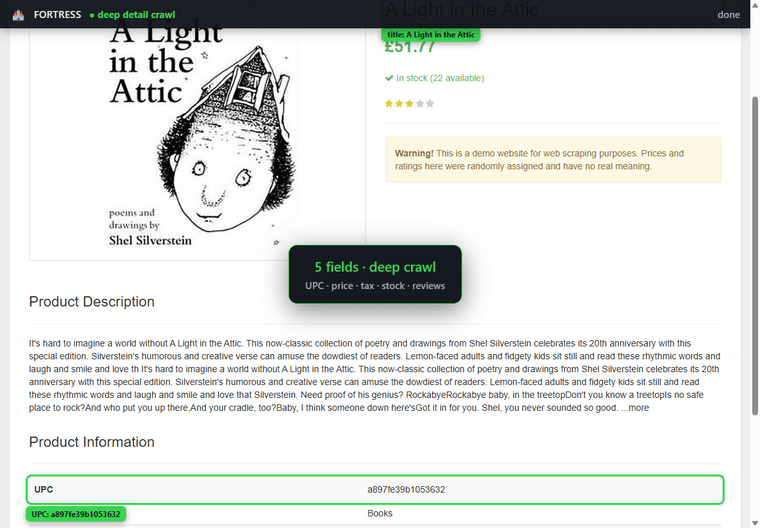 Deep detail crawl: UPC · price · tax · stock · reviews. |
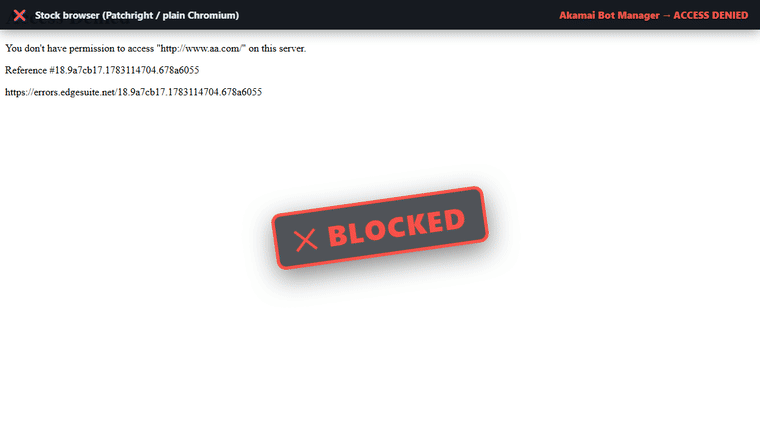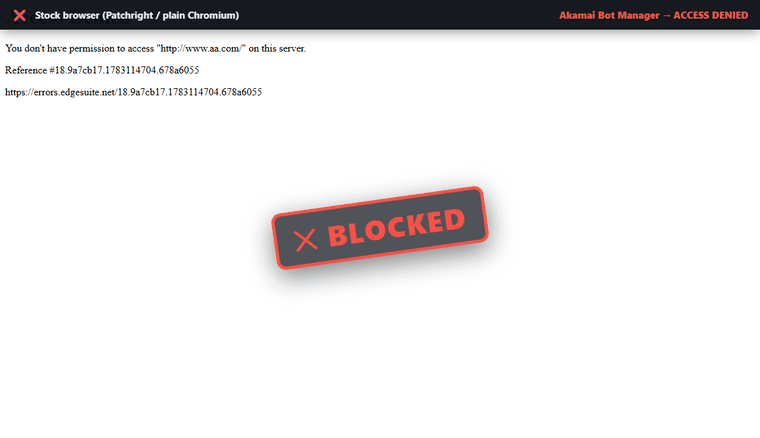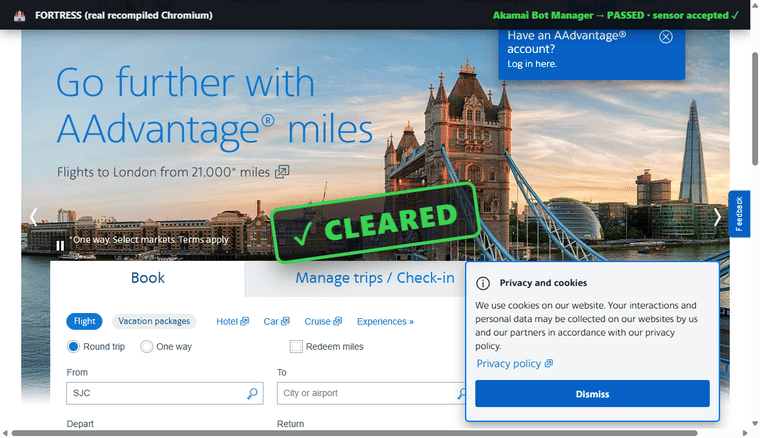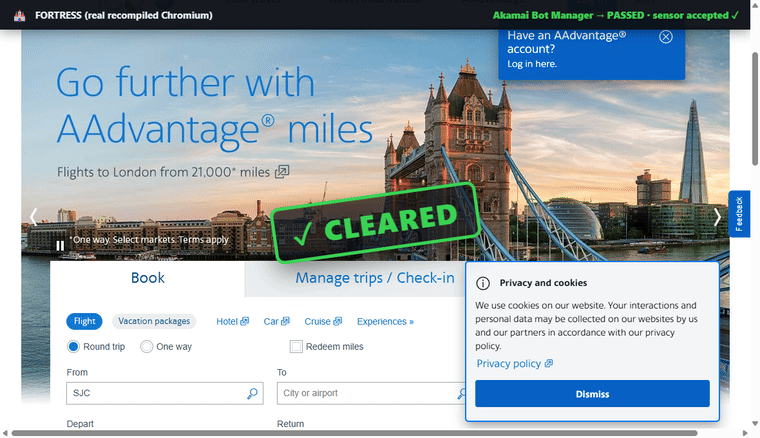
Akamai, before and after, on aa.com from the same residential IP: a stock browser gets Access Denied, Fortress loads the page and Akamai issues its _abck sensor cookie. Same result on lowes.com, macys.com and kohls.com.
Quick start · Every session a distinct machine · The Fortress MCP · Works with your stack · Why patch the engine · How Fortress compares · Results · Configure the persona · Build & verify · Reference
pip install tilion-fortress                       # or: npm install tilion-fortress
docker run --rm -p 9222:9222 tilion/fortress:latest   # any OS, raw CDP on :9222
from tilion_fortress import Fortress
from playwright.sync_api import sync_playwright

with Fortress() as f:                       # launches the engine on a CDP endpoint
    with sync_playwright() as p:
        browser = p.chromium.connect_over_cdp(f.cdp_url)
        page = browser.new_page()
        page.goto("https://bot.sannysoft.com")
import { Fortress } from "tilion-fortress";
import { chromium } from "playwright";

const f = await Fortress.launch();
const browser = await chromium.connectOverCDP(f.cdpUrl);
const page = await browser.newPage();
await page.goto("https://browserscan.net");
The pip and npm SDKs download a prebuilt, SHA-256-verified binary (Linux x64, Windows x64). Portable tarballs, a .deb and the Windows .zip are on Releases.
v3 is free for developers, with no machine, session or concurrency caps. Activate once:
tilion activate # sign in with GitHub, Google or email; key saved to ~/.tilion/license.jwt
The key is checked offline and Fortress never reports usage. Without activation it still runs, on the public first-generation engine. For CI, Docker and agents, set TILION_LICENSE_KEY=<key> or run tilion activate --token <key>; one key covers a fleet. Production keys for larger organizations are at fortress.tilion.com/pricing.
tilion CLI| Command | What it does |
|---|---|
tilion activate | Unlock v3 with a one-click device flow (browser sign-in) |
tilion activate --headless | Same flow, prints the URL and code (SSH or remote hosts) |
tilion activate --token <jwt> | Save a key with no browser (CI, agents) |
tilion license status [--json] | Show the saved key's tier and expiry (--json for scripts) |
tilion license refresh | Re-issue the key before it expires |
tilion license logout | Remove the saved key and drop back to v1 |
tilion get [platform] | Download the build for this host. tilion get list shows all: linux-x64, arm64, armhf, x86, win-x64, mac-arm64, mac-x64 |
tilion mcp | Run the Fortress MCP server, stealth browsing as agent tools |
tilion [--port N] | Launch the engine and print the CDP endpoint |