secrary/makin
makin - revela trucos de antidepuración y anti-máquina virtual [Este proyecto ya no se mantiene]

I create makin to make initial malware assessment little bit easier for me, I think it's useful for others as well, It helps to reveal a debugger detection techniques used by a sample.
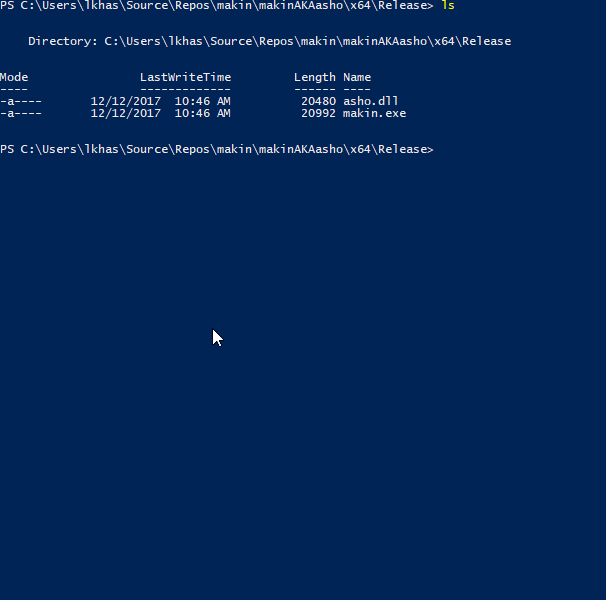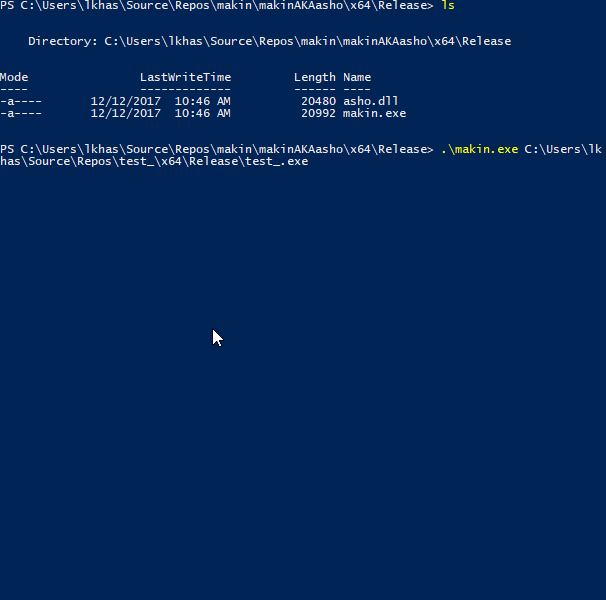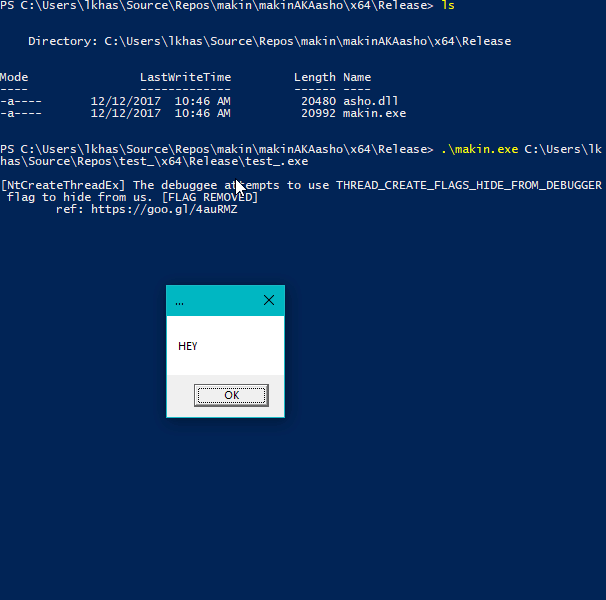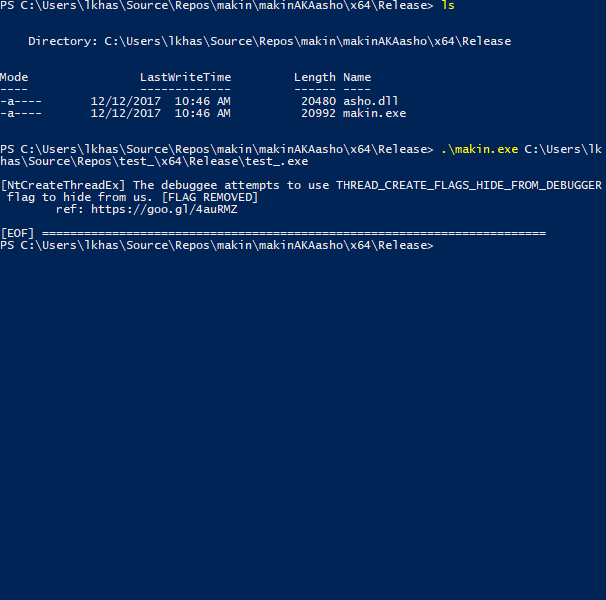
makin abre una muestra como depurado e inyecta asho.dll(el módulo principal renombra todas las dlls antes de la inyección), asho.dll engancha varias funciones en las bibliotecas ntdll.dll y kernelbase.dll y después de verificar los parámetros, envía el mensaje correspondiente al depurador (makin.exe).
makin también genera un script para IDA Pro para establecer puntos de interrupción en las APIs detectadas.
Por el momento, makin puede revelar las siguientes técnicas:
ntdll.dll:
NtClose - ref: The "Ultimate" Anti-Debugging Reference: 7.B.iiNtOpenProcess - ref: The "Ultimate" Anti-Debugging Reference: 7.B.iNtCreateFile - ref: The "Ultimate" Anti-Debugging Reference: 7.B.iii (Abrir a sí mismo)NtCreateFile - ref: The "Ultimate" Anti-Debugging Reference: 7.B.iii (Abrir un controlador)LdrLoadDll - ref: The "Ultimate" Anti-Debugging Reference: 7.B.ivNtSetDebugFilterState - ref: The "Ultimate" Anti-Debugging Reference: 7.D.viNtQueryInformationProcess - ref: The "Ultimate" Anti-Debugging Reference: 7.D.viii.a, 7.D.viii.b, 7.D.viii.cNtQuerySystemInformation - ref: The "Ultimate" Anti-Debugging Reference: 7.E.iiiNtSetInformationThread - ref: The "Ultimate" Anti-Debugging Reference 7.F.iiiNtCreateUserProcess - ref: The "Ultimate" Anti-Debugging Reference 7.G.iNtCreateThreadEx - ref: entrada de blog ntueryNtSystemDebugControl - ref: @waleedassar - pastebinNtYieldExecution - ref: The "Ultimate" Anti-Debugging Reference 7.D.xiiiNtSetLdtEntries - ref: ANTI-UNPACKER TRICKS: PARTE UNO - 2.1.2NtQueryInformationThread - ref: ntquery - NtQueryInformationThreadNtCreateDebugObject y NtQueryObject - ref: Anti-Debug NtQueryObjectRtlAdjustPrivilege - ref: Usando RtlAdjustPrivilege para detectar depurador por insid3codeteamPEB->BeingDebugged - En lugar de llamar a IsDebuggerPresent(), algunos programas verifican manualmente el PEB (Process Environment Block) por la bandera BeingDebugged.PEB->NtGlobalFlag - ref: al-khaserUserSharedData->KdDebuggerEnabled - ref: al-khaser - SharedUserData_KernelDebuggerPROCTECTED handle - ref: al-khaser - HANDLE_FLAG_PROTECT_FROM_CLOSEkernelbase.dll:
IsDebuggerPresent - ref: MSDNCheckRemoteDebuggerPresent - ref: MSDNSetUnhandledExceptionFilter - ref: The "Ultimate" Anti-Debugging Reference: D.xvRegOpenKeyExInternalW - verifica claves del registroRegQueryValueExW - verifica valores de claves del registroPuedes agregar más comprobaciones de VM editando el archivo checks.json, sin modificar el ejecutable
Eso es todo por ahora, puedes agregar tantas como desees :)