Skip to content
KitploitKITPLOIT
HerramientasExploitsBlog
Log in
Enviar
HerramientasExploitsBlog
Enviar

¡Herramientas de Hacking, PenTest y Ciberseguridad para tu Arsenal de Seguridad!

Kitploit es un directorio de herramientas de hacking, ciberseguridad y pentesting. Descubre las últimas actualizaciones de proyectos para encontrar vulnerabilidades, analizar sistemas, automatizar pruebas y fortalecer tu seguridad.

FeedsContactoPrivacidad© 2026 Kitploit

Directorio de Herramientas

Categorías

Ver todas las categorías
Loading categories
wrongsecrets — Aplicación vulnerable con ejemplos que muestran cómo no usar secretos | Kitploit
Herramientas/GitHubGitHub/owasp/wrongsecrets
Seguridad de ContenedoresAnálisis de VulnerabilidadesCTFSeguridad en la NubeDevSecOpsDetección de SecretosAprendizaje y EducaciónLabs y PrácticaTop en Labs y Práctica #8Top en Detección de Secretos #19
1.5k59993hace 4h 56mRevisado por Kitploit

Más Populares

Ver todos →

Descubre las herramientas más usadas por nuestra comunidad.

Explora todas las herramientas

Explora nuestra colección de herramientas

Ver todas las herramientas →
Compartir
GitHubowasp/wrongsecrets

wrongsecrets

Aplicación vulnerable con ejemplos que muestran cómo no usar secretos
Ver RepositorioSitio web
Contenido no disponible en el idioma solicitado. Mostrando versión en inglés.

OWASP WrongSecrets

Tweet

Java checkstyle and testing Pre-commit Terraform FMT CodeQL Dead Link Checker Javadoc and Swaggerdoc generator Test Heroku with cypress Build Dev Container

Test minikube script (k8s) Test minikube script (k8s&vault) Docker container test Test container on podman DAST with ZAP PR Preview and Visual Diff Build Preview Visual Diff

OWASP Production Project OpenSSF Best Practices Discussions Docker pulls

Welcome to the OWASP WrongSecrets game! The game is packed with real life examples of how to not store secrets in your software. Each of these examples is captured in a challenge, which you need to solve using various tools and techniques. Solving these challenges will help you recognize common mistakes & can help you to reflect on your own secrets management strategy.

Can you solve all the challenges?

Try some of them on our Heroku demo environment.

Want to play the other challenges? Read the instructions on how to set them up below.

🚀 Quick Start

New to WrongSecrets? Start here:

  1. Try Online First: Visit our Heroku demo to get familiar with the challenges
  2. Run Locally: Use Docker for the full experience with all challenges:
    docker run -p 8080:8080 -p 8090:8090 jeroenwillemsen/wrongsecrets:latest-no-vault
    
    Then open http://localhost:8080
  3. Want to see what's ahead? Try our bleeding-edge master container with the latest features:
    docker run -p 8080:8080 -p 8090:8090 ghcr.io/owasp/wrongsecrets/wrongsecrets-master:latest-master
    
    ⚠️ Note: This is a development version and may be unstable
  4. Advanced Setup: For cloud challenges and Kubernetes exercises, see the detailed instructions below

What you'll learn:

  • Common secrets management mistakes
  • How to identify exposed credentials
  • Best practices for securing secrets
  • Tools and techniques for secret detection

How it works: This repository contains intentionally vulnerable code and configuration files with real and fake secrets hidden throughout the codebase. You'll examine source code, configuration files, Docker containers, and cloud deployments to discover these secrets. Each challenge teaches you different ways secrets can be accidentally exposed in real-world applications.
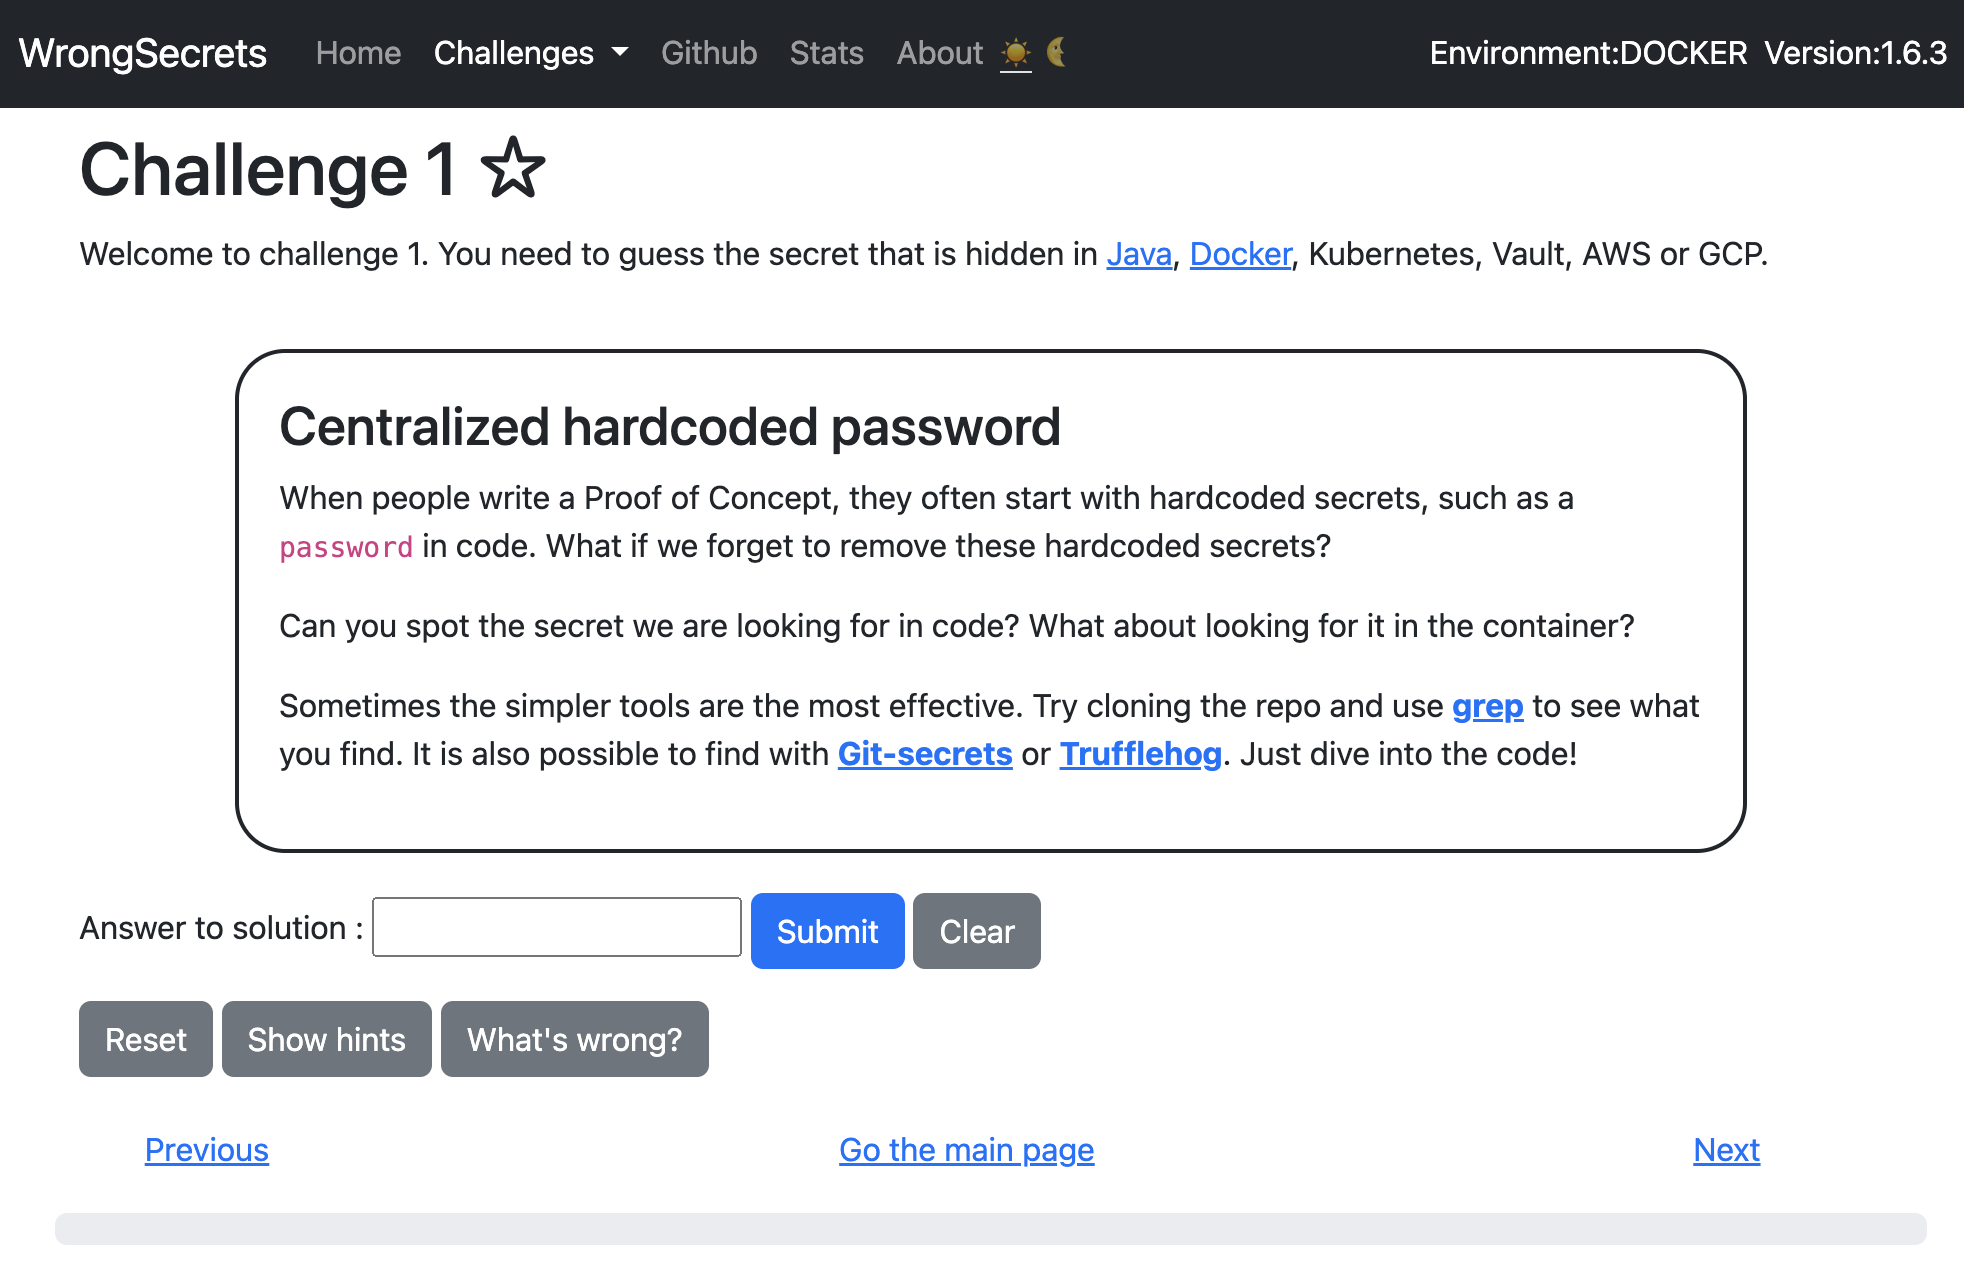
screenshotOfChallenge1

📋 Prerequisites

For basic usage:

  • A web browser
  • Docker (for local setup) - Install here

For advanced setups:

  • Kubernetes/Minikube - Install here
  • Cloud account (AWS/GCP/Azure) for cloud challenges
  • Command line familiarity
Descargar herramienta