 ayoubfaouzi/al-khaser
Técnicas de malware público utilizadas en la naturaleza: Máquina virtual, Emulación, Depuradores, Detección de sandbox.

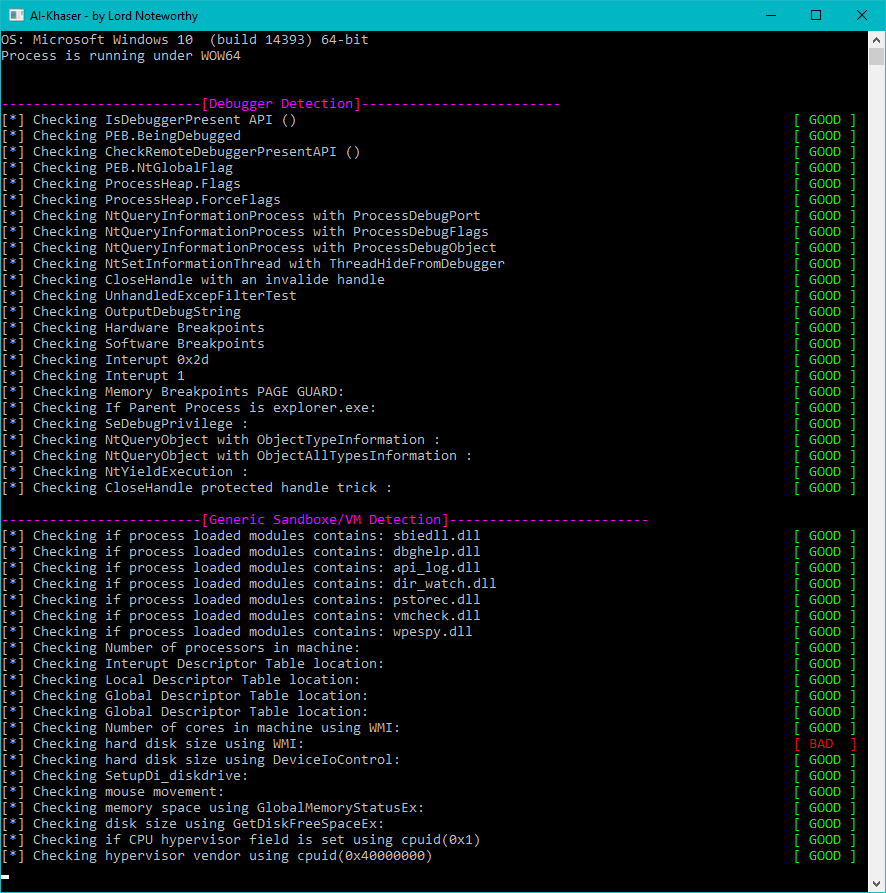
al-khaser es una aplicación de "malware" PoC con buenas intenciones que tiene como objetivo poner a prueba tu sistema antimalware. Realiza un montón de trucos comunes de malware con el objetivo de ver si pasas desapercibido.
$ ./al-khaser.exe -h
Usage: al-khaser.exe [OPTIONS]
Options:
  --check <type>      Enable specific check(s). Can be used multiple times. Valid types are:
                        TLS              (Thread Local Storage callback checks)
                        DEBUG            (Anti-debugging checks)
                        INJECTION        (Code injection checks)
                        GEN_SANDBOX      (Generic sandbox checks)
                        VBOX             (VirtualBox detection)
                        VMWARE           (VMware detection)
                        VPC              (Virtual PC detection)
                        QEMU             (QEMU detection)
                        KVM              (KVM detection)
                        XEN              (Xen detection)
                        WINE             (Wine detection)
                        PARALLELS        (Parallels detection)
                        HYPERV           (Hyper-V detection)
                        CODE_INJECTIONS  (Additional code injection techniques)
                        TIMING_ATTACKS   (Timing/sleep-based sandbox evasion)
                        DUMPING_CHECK    (Dumping memory/process checks)
                        ANALYSIS_TOOLS   (Analysis tools detection)
                        ANTI_DISASSM     (Anti-disassembly checks)
  --sleep <seconds>   Set sleep/delay duration in seconds (default: 600).
  --delay <seconds>   Alias for --sleep.
  -h, --help          Show this help message and exit.

Examples:
  al-khaser.exe --check DEBUG --check TIMING_ATTACKS --sleep 30
  al-khaser.exe --check VMWARE --check QEMU
  al-khaser.exe --sleep 30
Puedes descargar los binarios compilados (x86, x64) desde la página de lanzamientos de este proyecto. La contraseña para los 7z se puede encontrar aquí.
Por favor, si encuentras alguno de los trucos anti-análisis que has visto en un malware, no dudes en contribuir.
sample.exe o sandbox.exe.