CVE-2024-24919-Sniper

CVE-2024-24919 Sniper - A powerful tool for scanning Check Point Security Gateway CVE-2024-24919 vulnerability. Supports single & bulk scanning,…

CVE-2024-24919 Sniper - A powerful tool for scanning Check Point Security Gateway CVE-2024-24919 vulnerability. Supports single & bulk scanning,…

Structured security knowledge base with production-inspired cases: vulnerability analysis, exploit explanation, remediation, and DevSecOps for…

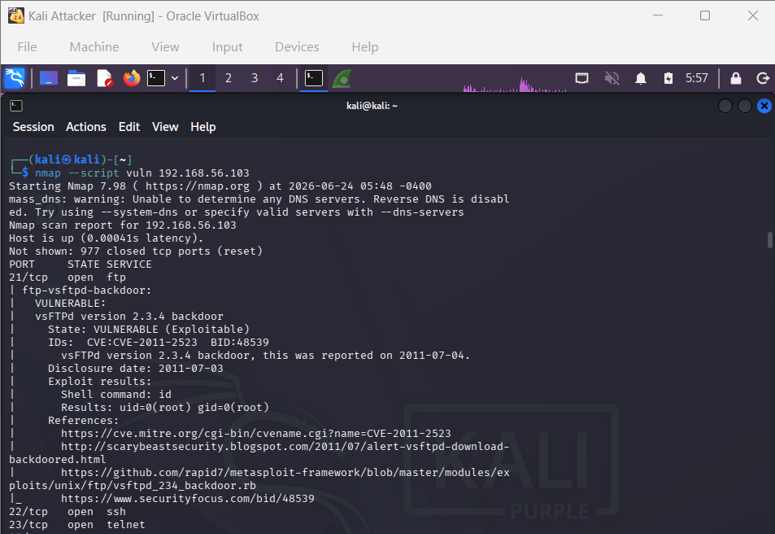
VAPT report for vsFTPd 2.3.4 backdoor CVE-2011-2523, covering Nmap vulnerability scanning, Metasploit exploitation, post-exploitation root access,…

Patch for CVE-2026-04321, a critical OS command injection vulnerability in Zyxel firewalls. Includes deployment status and references for remediation.

Batch script for exploiting CVE-2017-12615 (Apache Tomcat PUT method vulnerability) to upload and execute arbitrary JSP files on vulnerable servers.

Complete exploitation toolkit for CVE-2026-3180 - WordPress Contest Gallery SQL Injection vulnerability. Features automated data extraction, WAF…

Exploit tool for CVE-2024-36104 targeting Apache OFBiz code execution vulnerability. Supports single and batch URL scanning with proxy and threading…

Exploit for CVE-2024-28995 targeting Serv-U arbitrary file read vulnerability. Supports single and batch URL scanning with proxy and threading…

Minimal test repository for CVE-2021-3572, demonstrating a pip dependency confusion vulnerability and its fix across vulnerable and patched versions.

PoC exploit for CVE-2026-3844, a critical unauthenticated file upload vulnerability in the WordPress Breeze plugin leading to RCE.

Proof-of-concept exploit for CVE-2024-36837, an unauthenticated arbitrary file read vulnerability in Zhilianyun SRM2.0. Includes batch scanning and…

Python PoC script and Nuclei YAML template for detecting and exploiting CVE-2025-68493, an XXE vulnerability in Apache Struts, enabling file read and…

Proof-of-concept exploit for CVE-2022-41401, a server-side request forgery (SSRF) vulnerability in OpenRefine <= v3.5.2, enabling unauthorized…

Proof-of-concept exploit for CVE-2023-27163, a Server-Side Request Forgery (SSRF) vulnerability in request-baskets up to v1.2.1. Includes automated…

Proof-of-concept exploit for CVE-2026-42228, an unauthenticated chat execution hijacking vulnerability in n8n, with automated scanning and attack…

Proof-of-concept exploit for CVE-2025-48703, an unauthenticated remote code execution vulnerability in CentOS Web Panel (CWP) versions prior to…

Cybersecurity Capstone Project completed during the NCSC Nashama CyberCamp 11, delivered in collaboration with IT Security C&T. The project…

Proof-of-concept exploit for CVE-2026-43735, a WebKit cross-origin information disclosure vulnerability in Safari < 26.5.2. Demonstrates leaking user…