
HintInject
 frkngksl/hintinject
A PoC project for embedding shellcode to Hint/Name Table
binary-analysisexploitationpayload-development+3
113
frkngksl/hintinjectA PoC project for embedding shellcode to Hint/Name Table
 g0h4n/rec2
REC2 (Rusty External Command and Control) is client and server tool allowing auditor to execute command from VirusTotal and Mastodon APIs written in…
 je5442804/wptaskscheduler_cve-2024-49039
WPTaskScheduler RPC Persistence & CVE-2024-49039 via Task Scheduler
 omribaso/sccm-cve-2026-47301-remote-code-execution-exploit
Proof-of-concept exploit chain (CVE-2026-47301) for Microsoft Configuration Manager (SCCM), combining a broken access, CAB arbitrary-write path…
 schierlm/javapayload
JavaPayload is a collection of pure Java payloads to be used for post-exploitation from pure Java exploits or from common misconfigurations (like not…
 byt3bl33d3r/nimdllsideload
DLL sideloading/proxying with Nim!
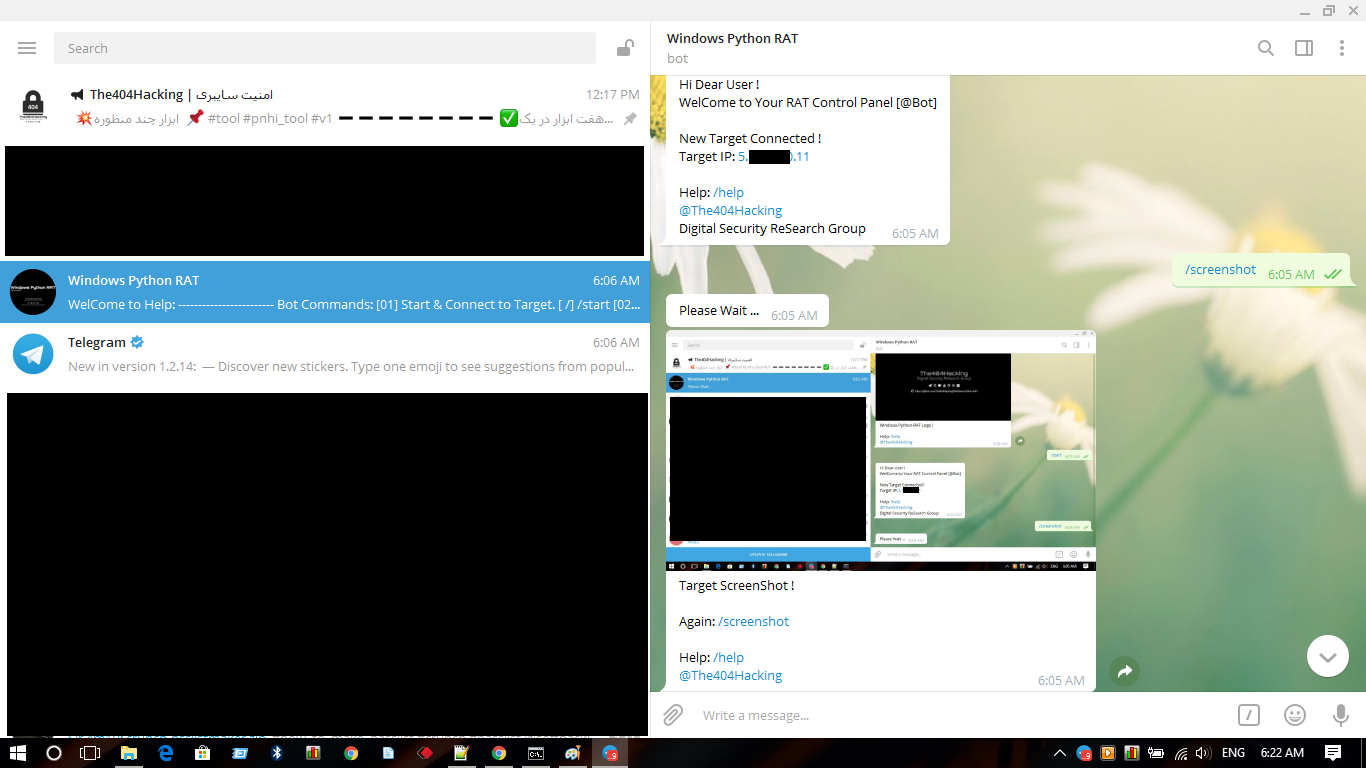 the404hacking/windows-python-rat
A New Microsoft Windows Remote Administrator Tool [RAT] with Python by Sir.4m1R.
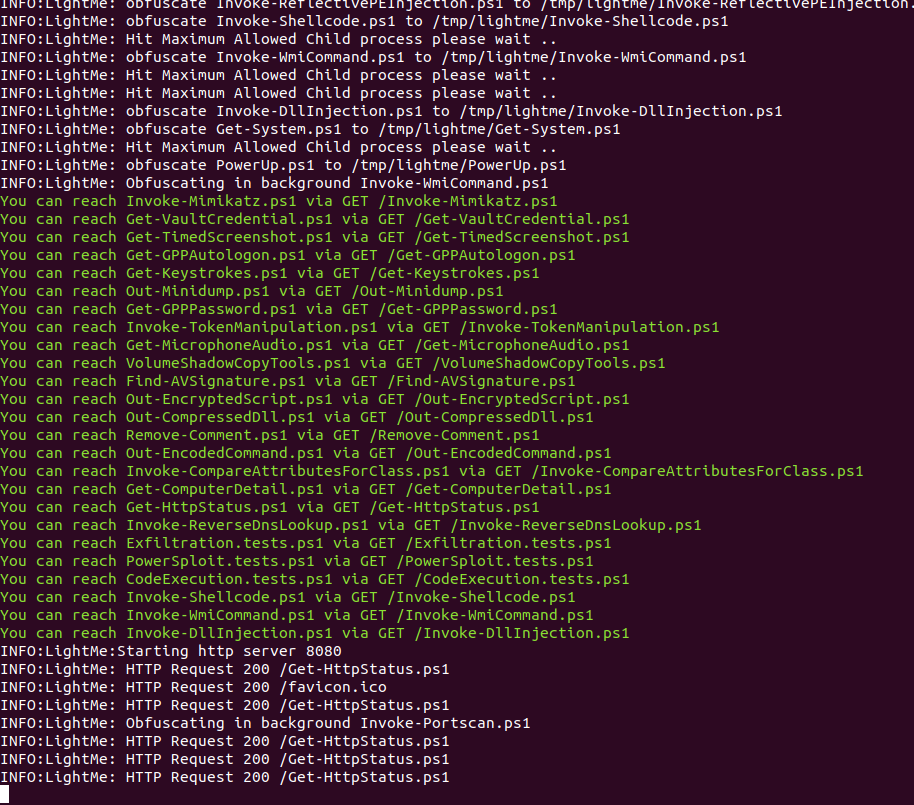 safebuffer/lightme
HTTP Server serving obfuscated Powershell Scripts/Payloads
 cbwang505/cve-2020-1066-exp
Local privilege escalation exploit for CVE-2020-1066 targeting Windows 7 and Server 2008 R2. Leverages arbitrary file replacement via Windows…
 ofasgard/execute-assembly-pico
A PICO for Crystal Palace that implements CLR hosting to execute a .NET assembly in memory.
 bishopfox/asminject
Heavily-modified fork of David Buchanan's dlinject project. Injects arbitrary assembly (or precompiled binary) payloads directly into x86-64, x86,…

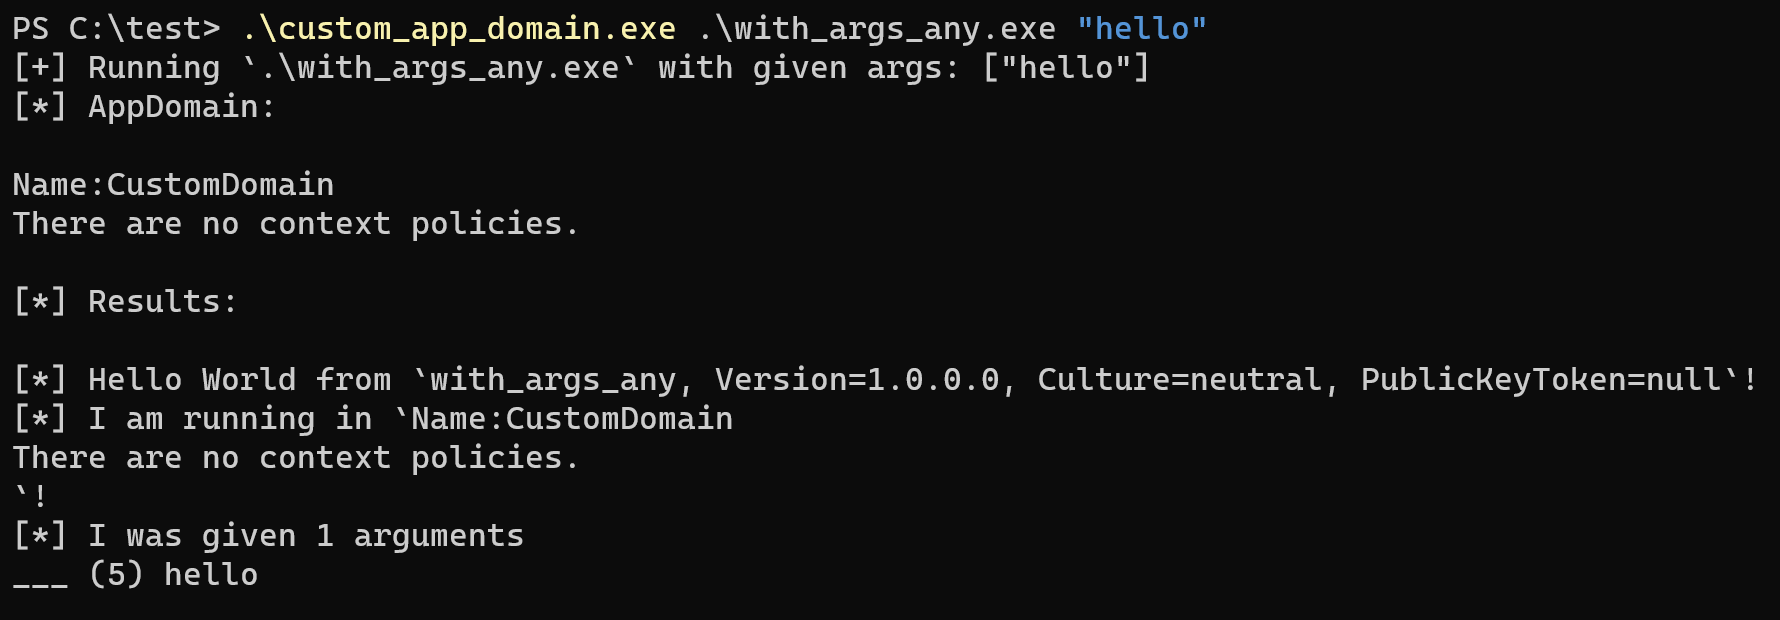 yamakadi/clroxide
A rust library that allows you to host the CLR and execute dotnet binaries.
 iilegacyyii/datainject-bof
Hijacks code execution via overwriting Control Flow Guard pointers in combase.dll
 csenox/semanagevolumeexploit
Windows local privilege escalation exploit abusing SeManageVolumePrivilege to grant full C:\ drive access and gain a SYSTEM shell via PrintConfig.dll…
 checkpointsw/vectoredoverloading
Local PE injection technique using hardware breakpoints and vectored exception handling to manipulate DLL loading and execute arbitrary payloads, as…
 blacksnufkin/rusty-playground
Some Rust program I wrote while learning Malware Development
 ahhh/ntp_trojan
Reverse NTP remote access trojan in python, for penetration testers