
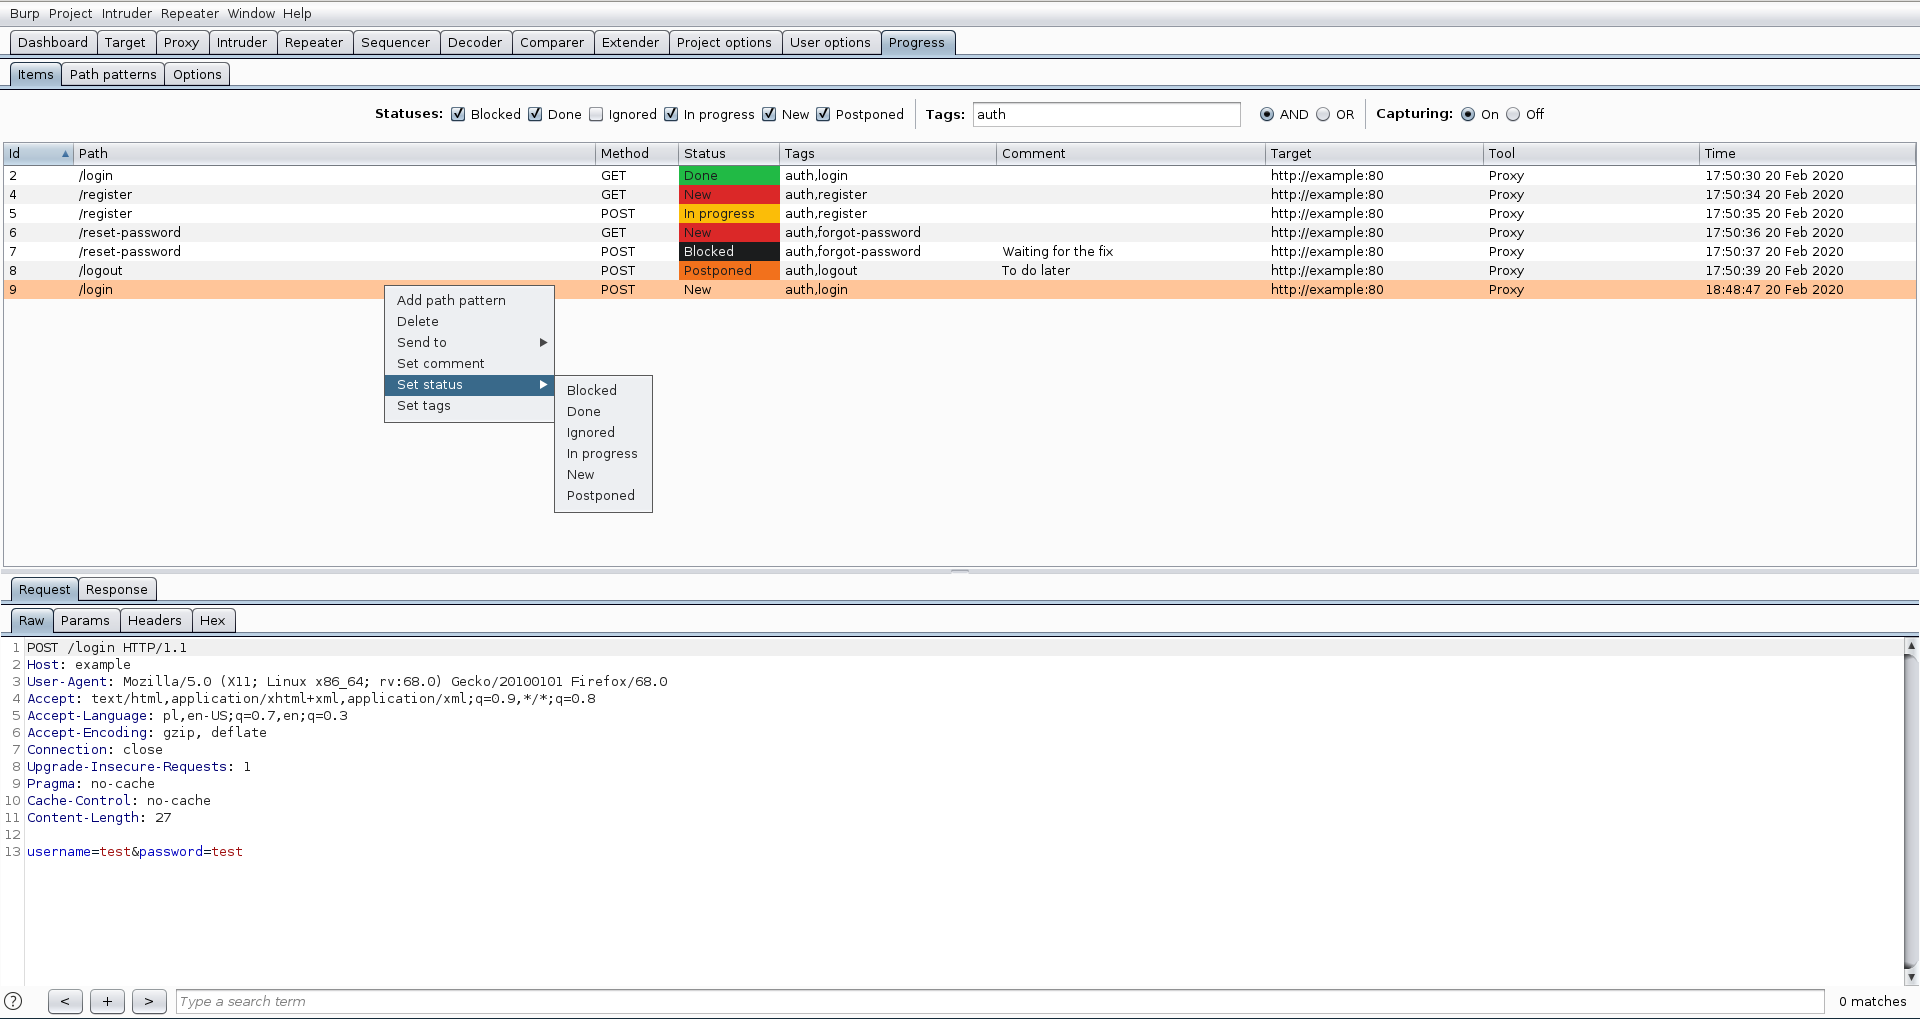
progress-burp
 dariusztytko/progress-burp
Burp Suite extension to track vulnerability assessment progress
penetration-testingutilities-frameworksvulnerability-analysis+1
59
dariusztytko/progress-burpBurp Suite extension to track vulnerability assessment progress
 ikkisoft/bradamsa
Burp Suite extension to generate Intruder payloads using Radamsa
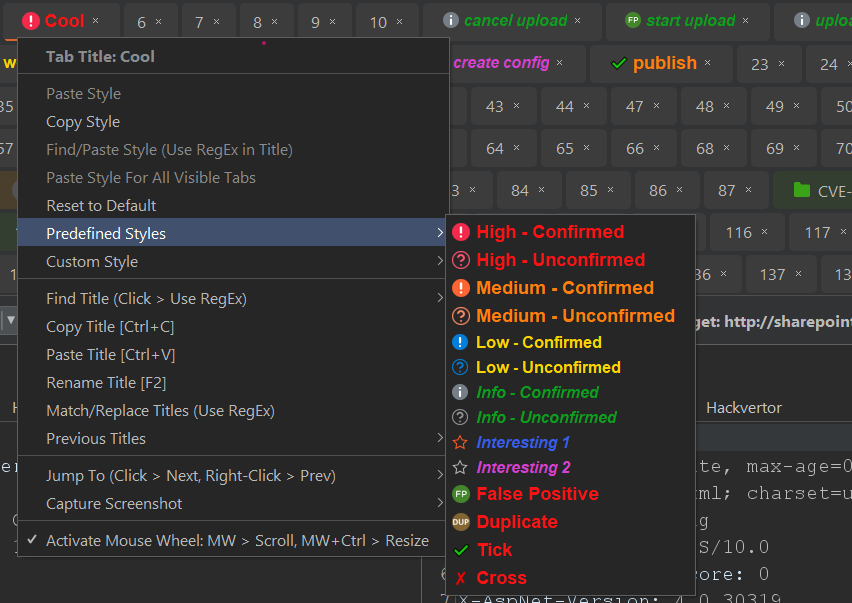 irsdl/burpsuitesharpenerex
This extension enhances Burp Suite by adding several UI and functional features, making it more user-friendly.
 moeinfatehi/admin-panel_finder
Burp Suite extension that finds exposed admin panels and login pages of web applications and infrastructure. 1,000+ payloads, OWASP WSTG-CONF-05.
 nccgroup/berserko
Burp Suite extension to perform Kerberos authentication
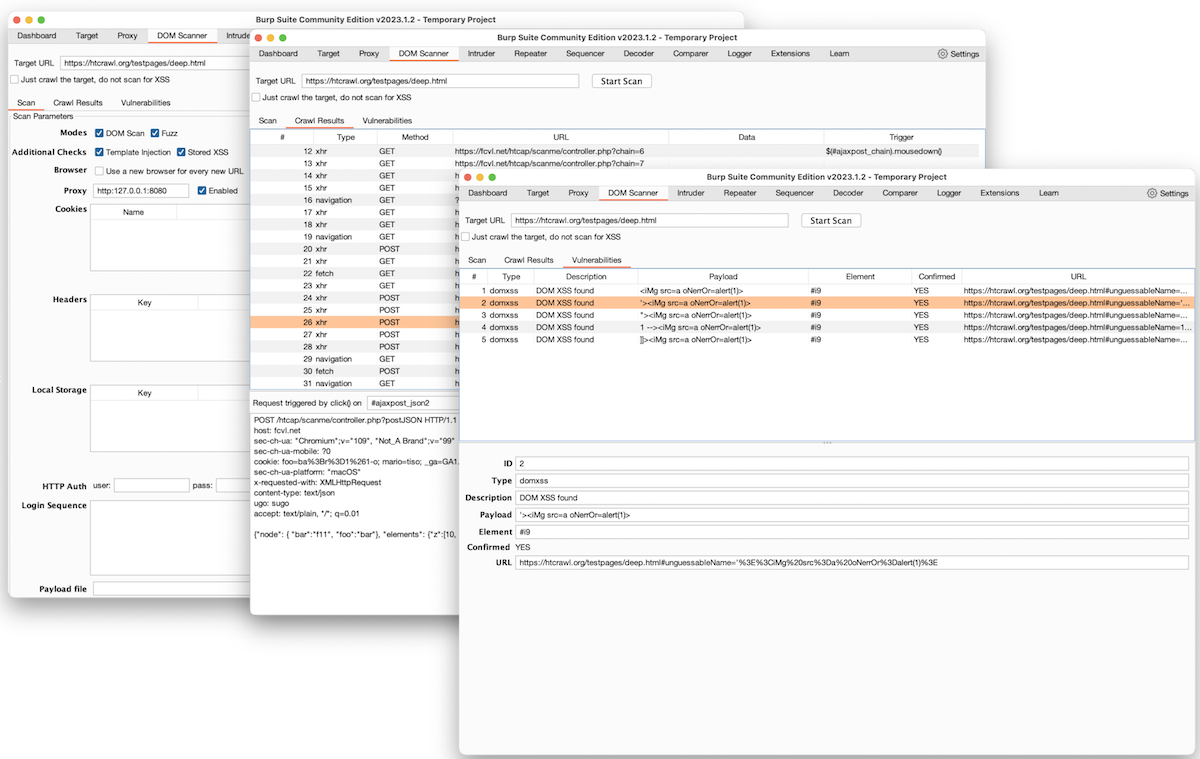 fcavallarin/burp-dom-scanner
Burp Suite's extension to scan and crawl Single Page Applications
 ztgrace/mole
Framework for identifying and exploiting out-of-band (OOB) application vulnerabilities with a custom DNS/token server, Burp Suite extension, and…
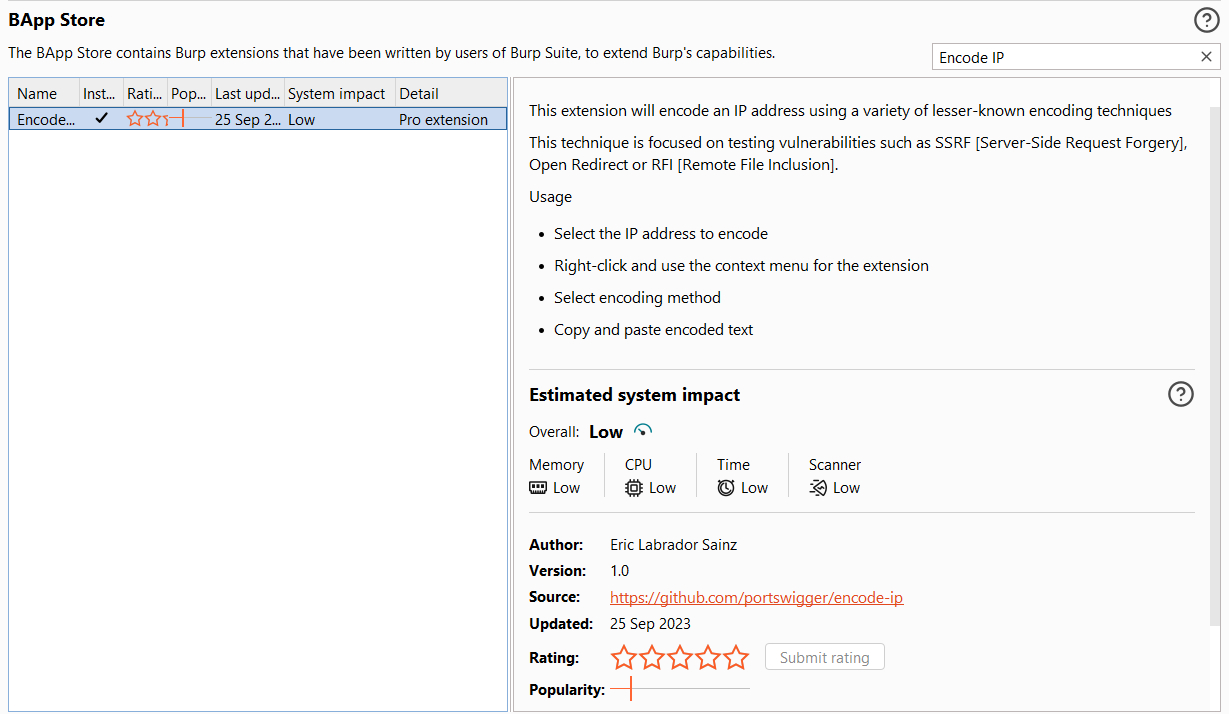 e1abrador/burp-encode-ip
Burp Suite extension to encode an IP address focused to bypass application IP / domain blacklist.
 mirfansulaiman/customheader
This Burp Suite extension allows you to customize header with put a new header into HTTP REQUEST BurpSuite (Scanner, Intruder, Repeater, Proxy…
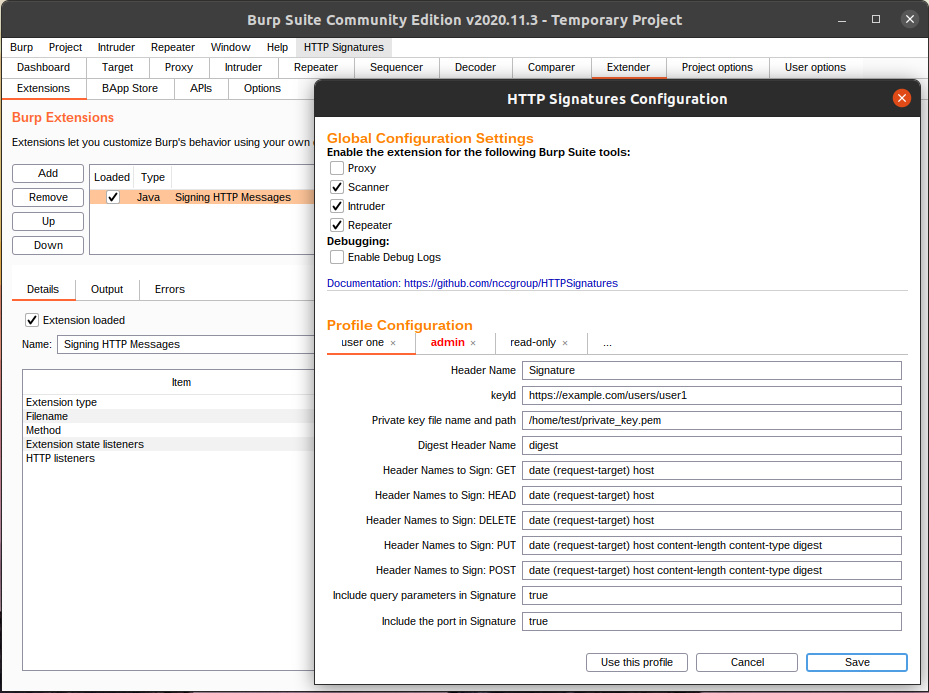 nccgroup/httpsignatures
A Burp Suite extension implementing the Signing HTTP Messages draft-ietf-httpbis-message-signatures-01 draft.
 raz0r/burp-radamsa
Radamsa fuzzer extension for Burp Suite
 josue87/burpmetafinder
Burp Suite extension for extracting metadata from files
 weirdmachine64/redom
A Burp Suite extension that brings full DOM rendering capabilities directly into Burp, enabling effective security testing of modern JavaScript-heavy…
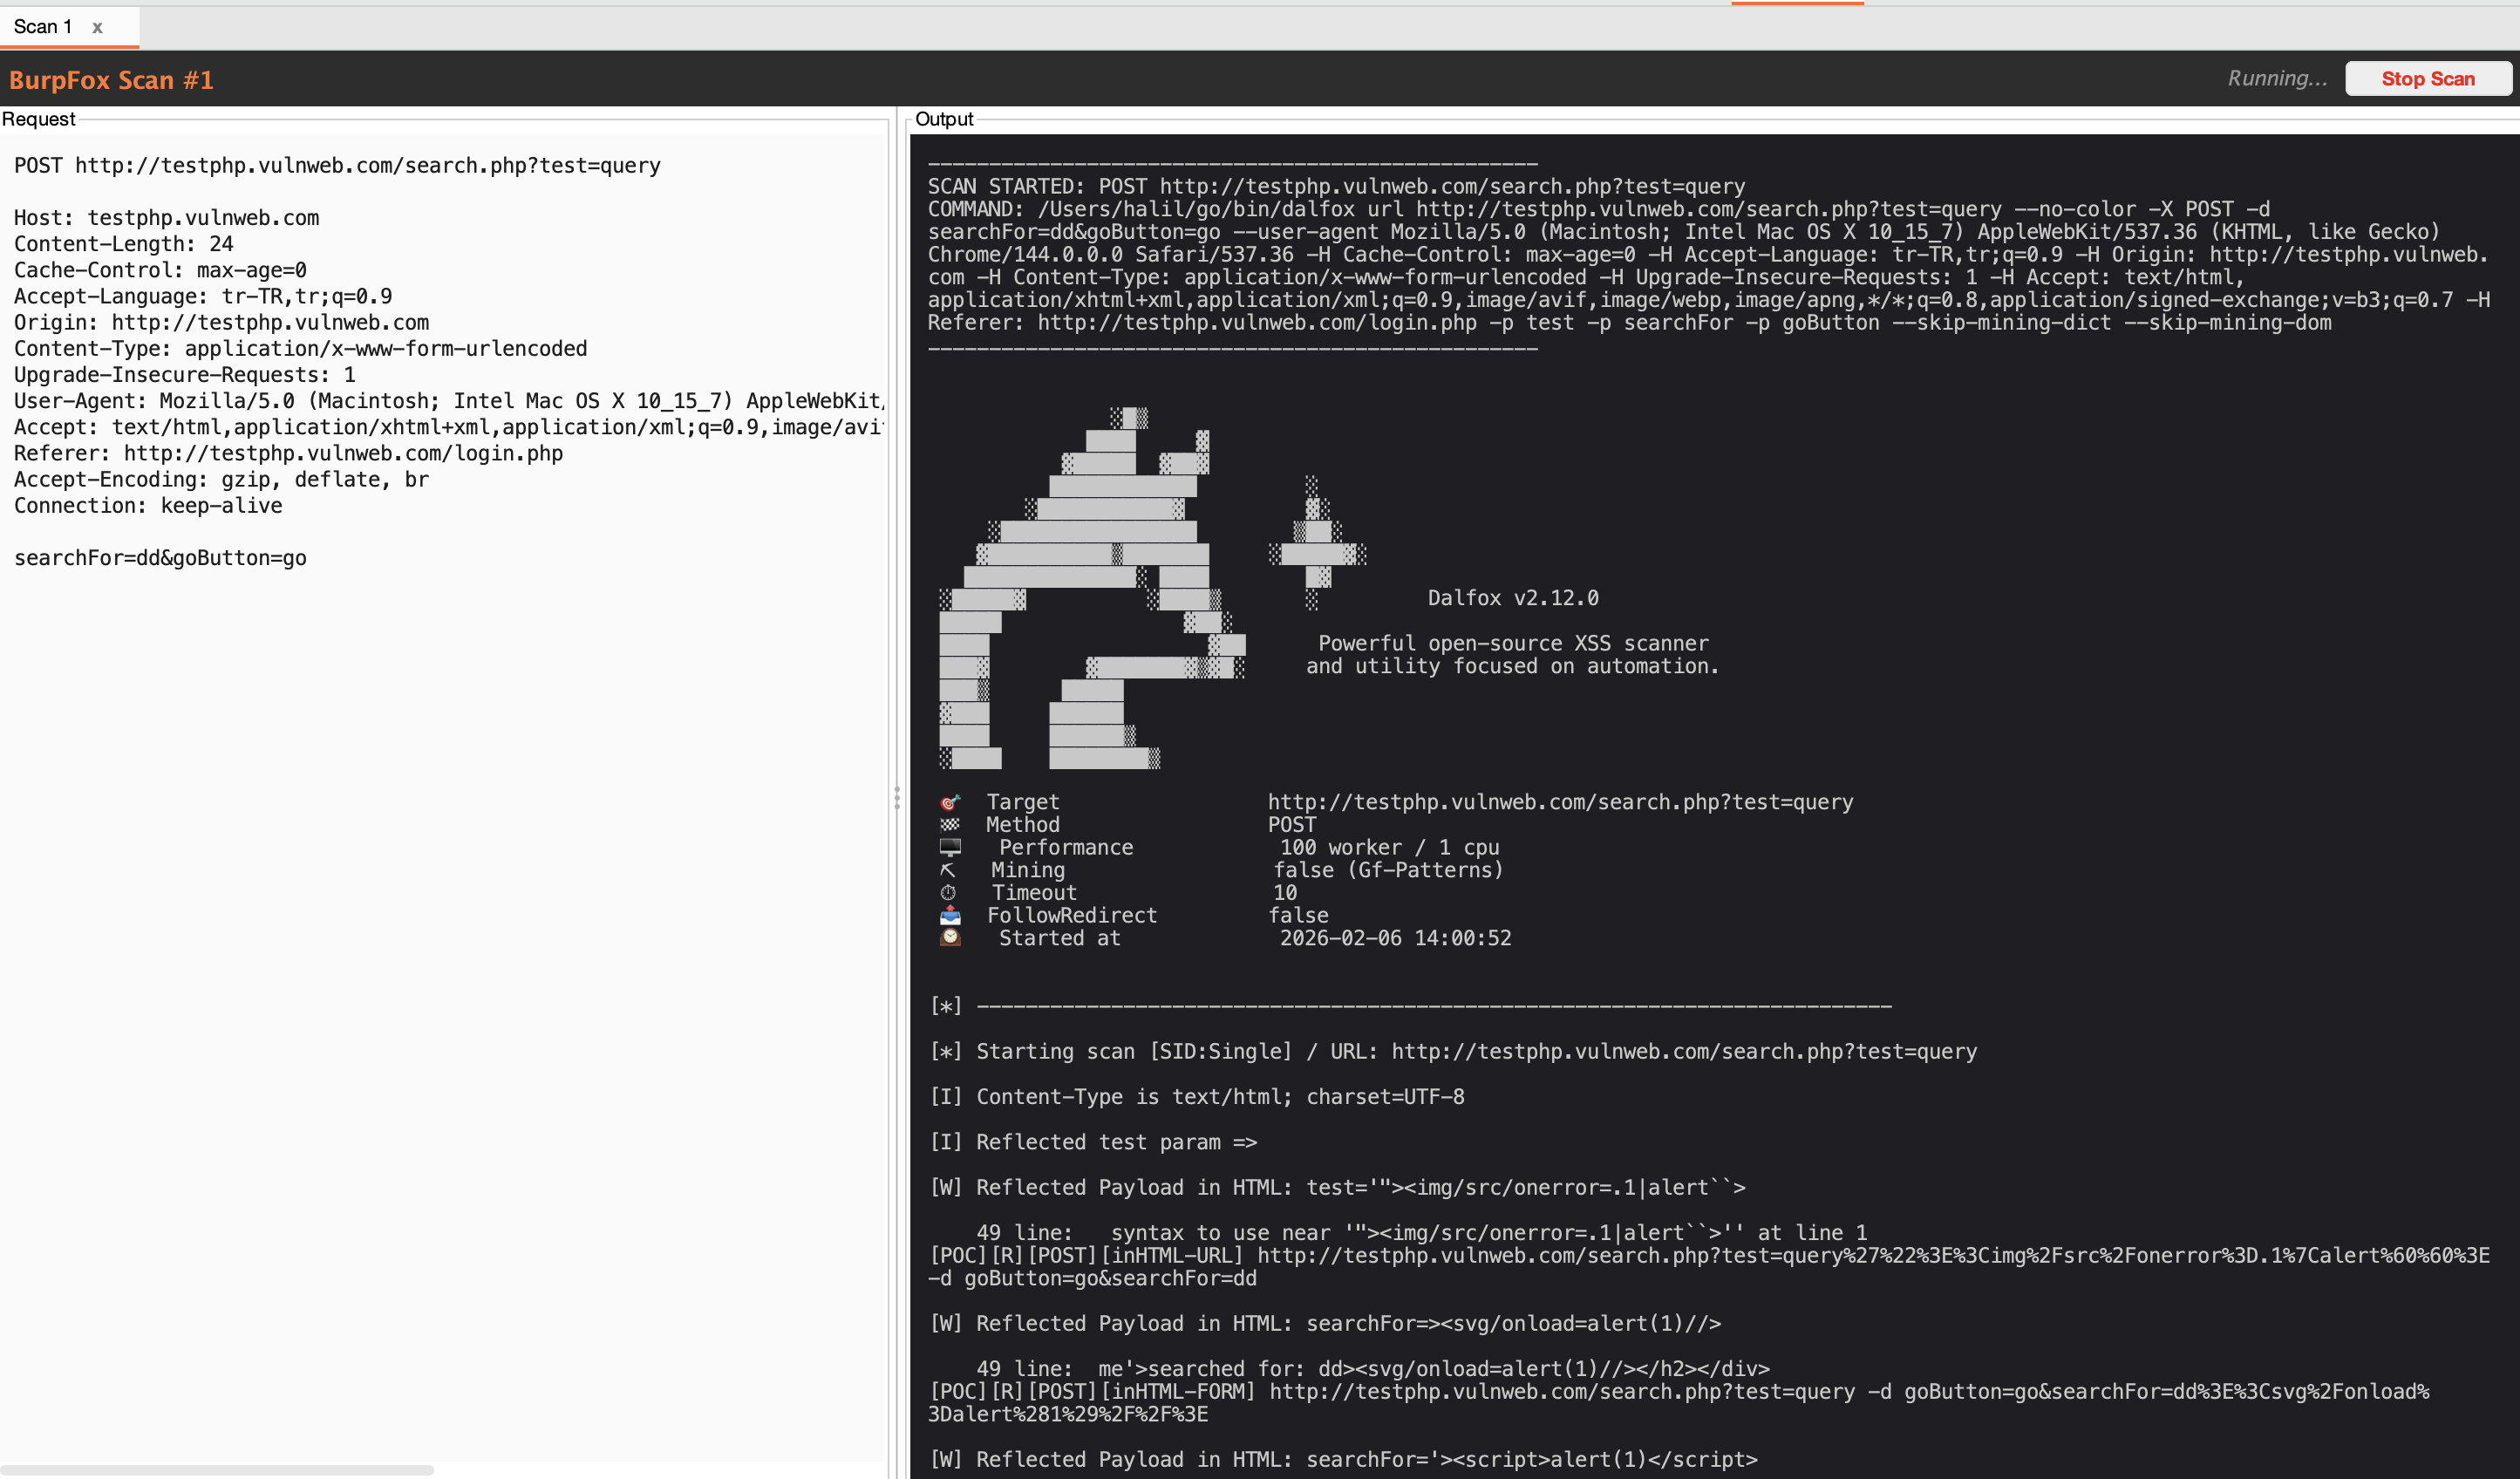 halilkirazkaya/burpfox
A Burp Suite extension that integrates Dalfox XSS scanner directly into your workflow.
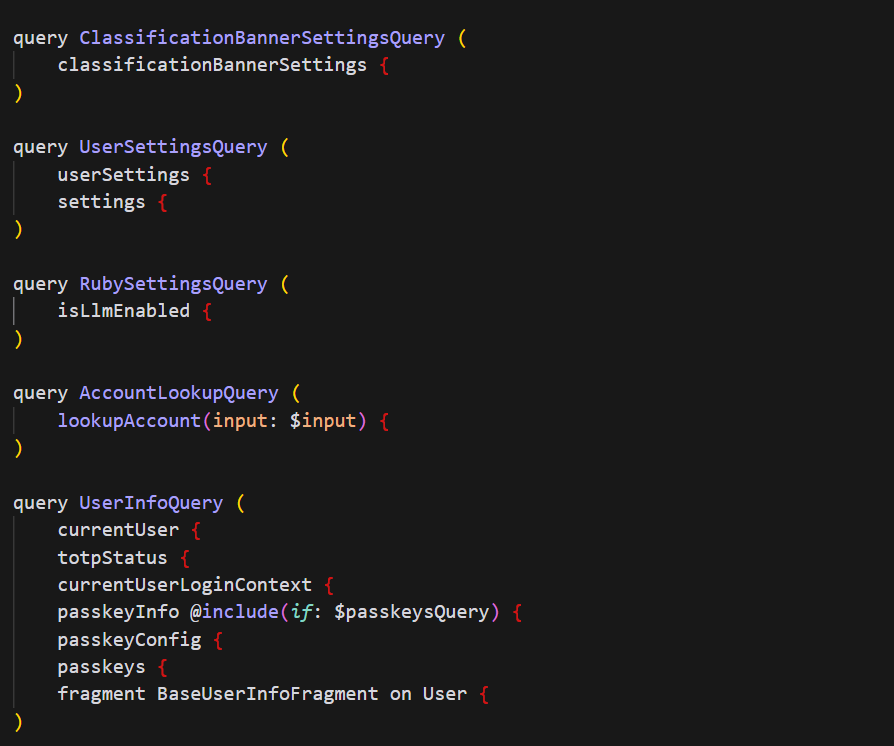 m19o/graphqlgrapper
Burp Suite extension to extract and collect GraphQL API endpoints from HTTP request history for security testing and reconnaissance.
 tobiasguta/next.js-rsc-rce-scanner-burp-suite-extension
Burp Suite extension to detect the Next.js / React Server Components (RSC) Remote Code Execution vulnerability (CVE-2025-55182 & CVE-2025-66478).
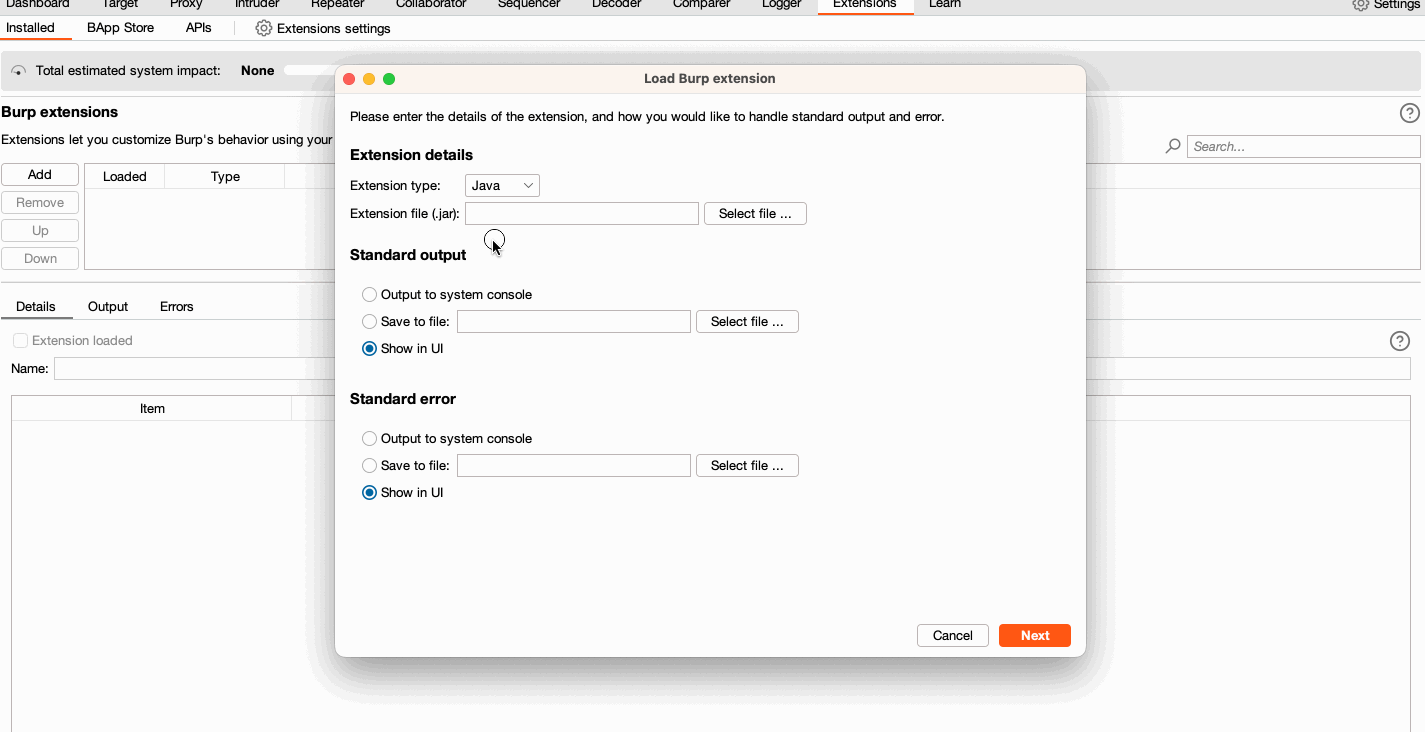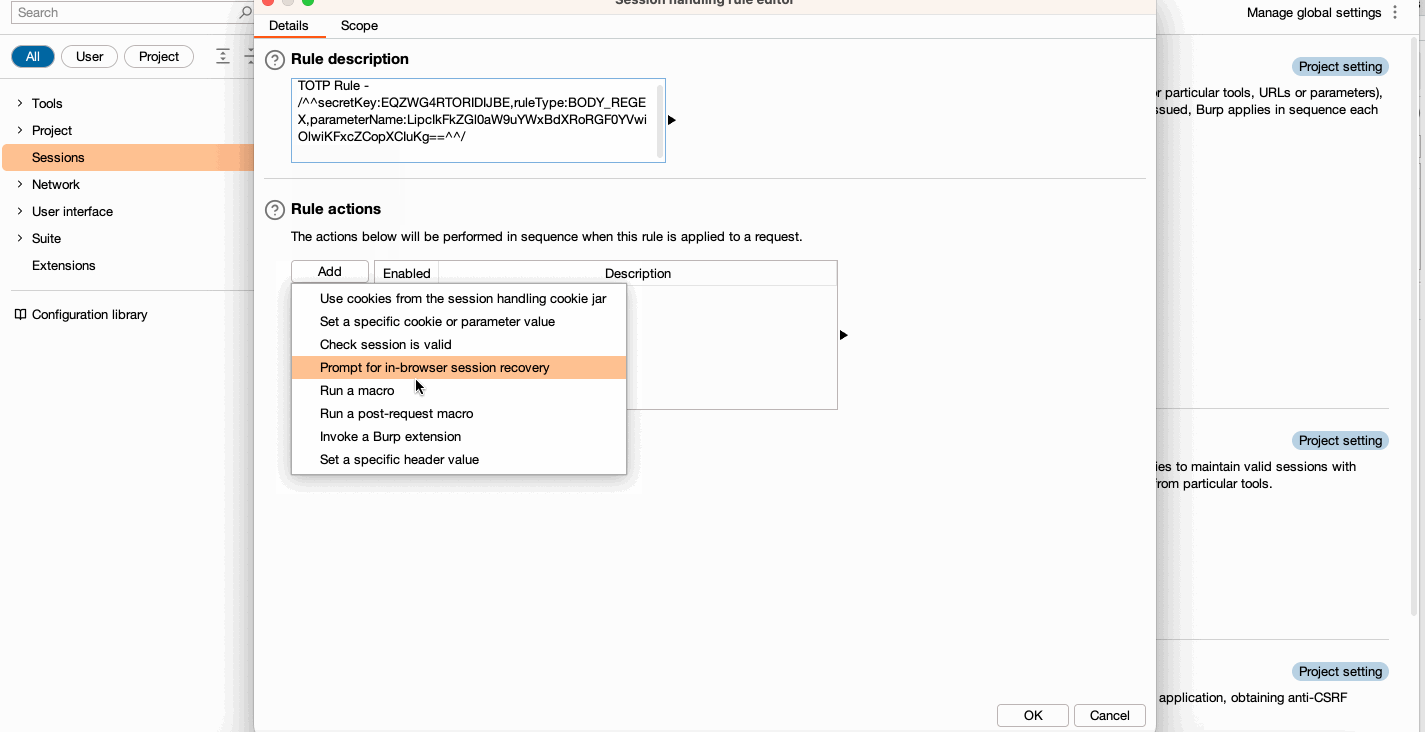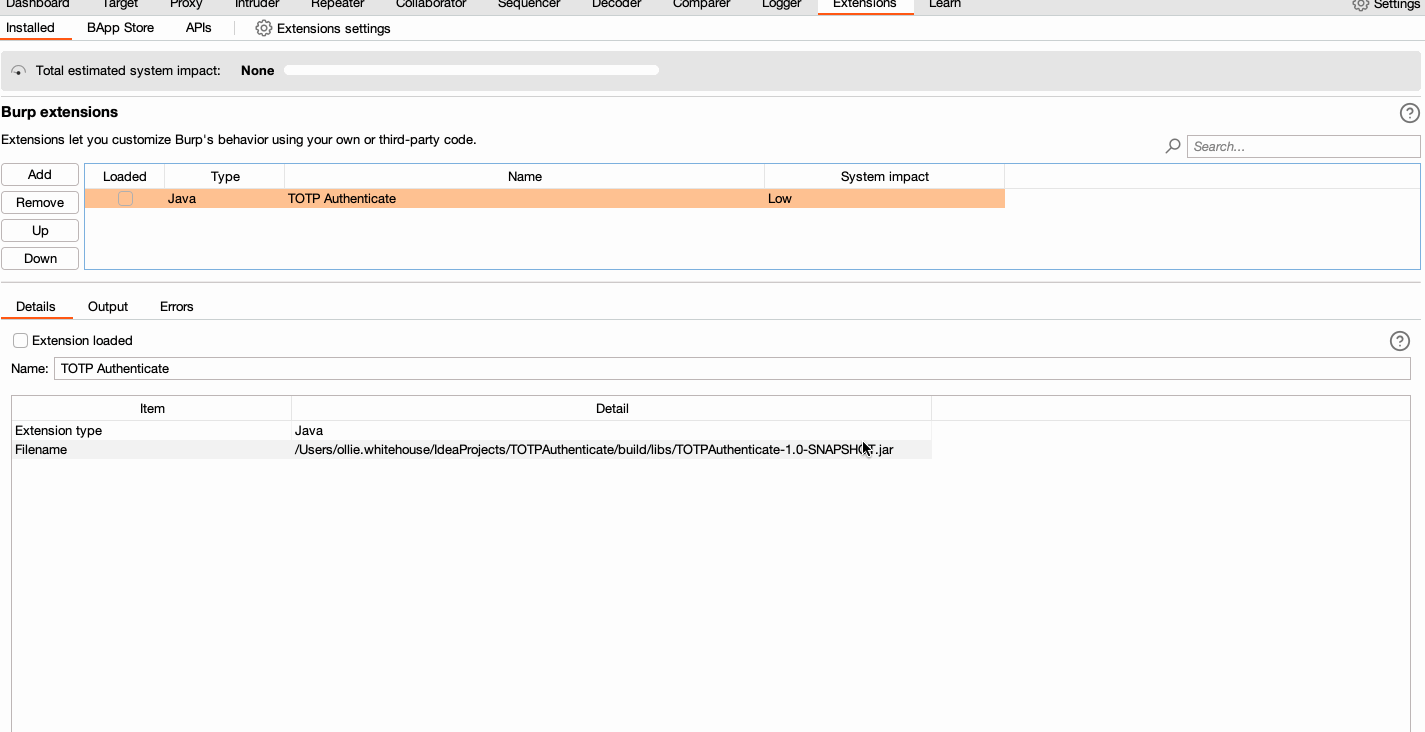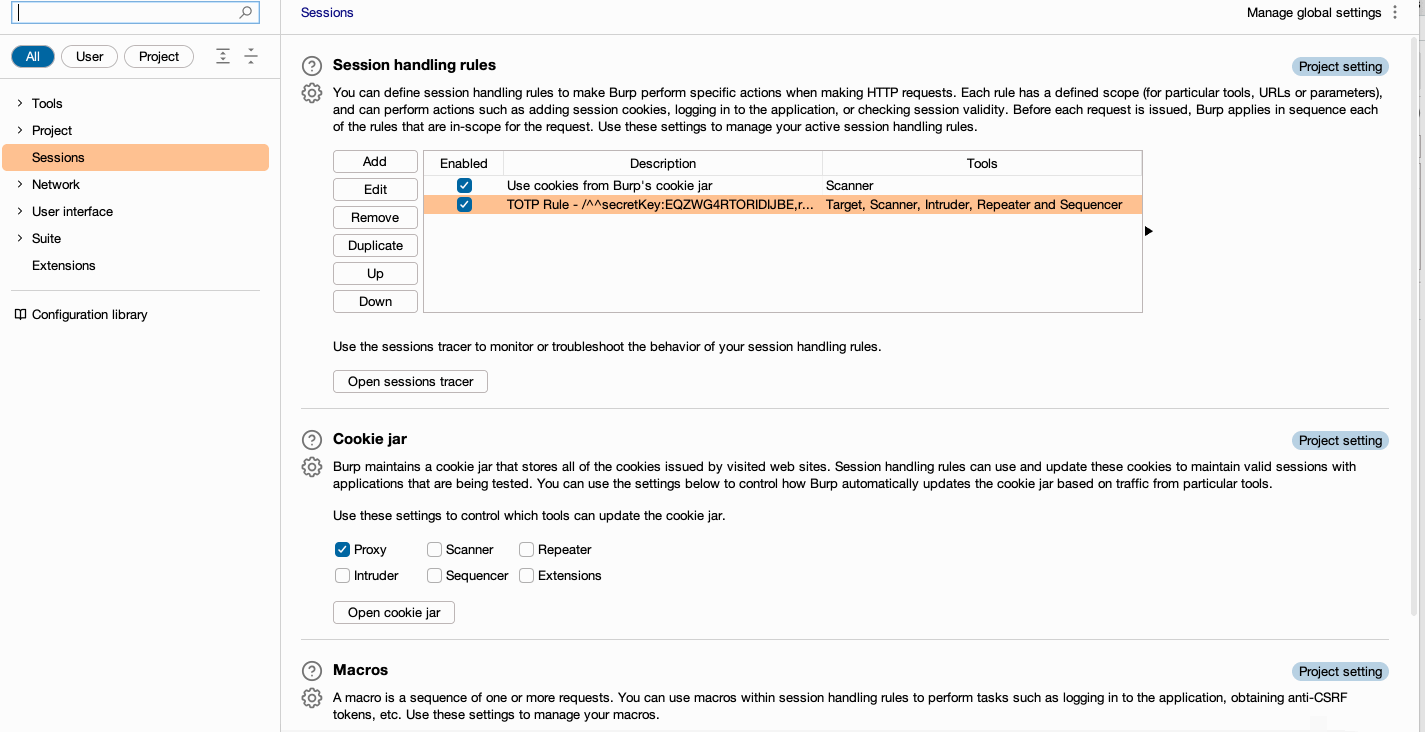 hannah-portswigger/totpauthenticate
This extension, for Burp Suite Enterprise Edition, utilizes session handling rules to provide a TOTP token to outgoing requests.
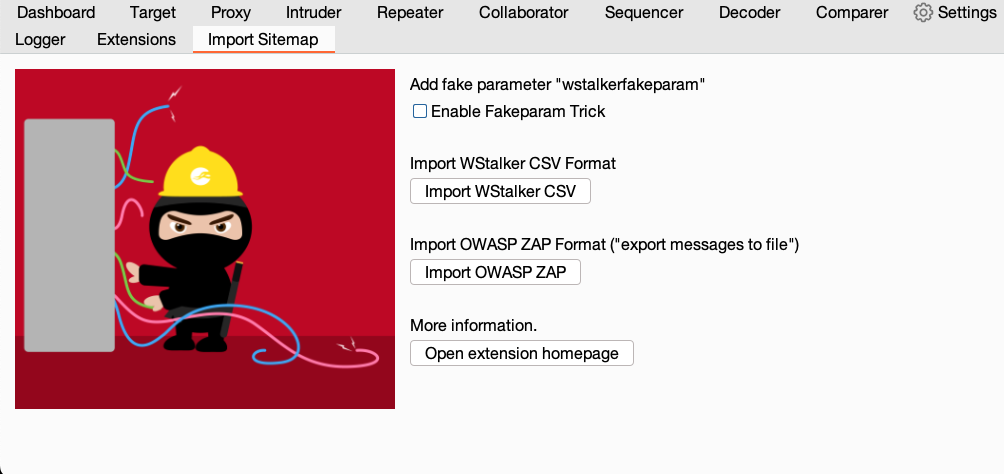 nccgroup/burpimportsitemap
Import To Sitemap is a Burp Suite Extension to import wstalker CSV file or ZAP export file into Burp Sitemap