Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
105 results
CVE-2021-4034-PwnKit preview

CVE-2021-4034-PwnKit

GitHubnavisec/cve-2021-4034-pwnkit

Nim-based proof-of-concept for CVE-2021-4034 (PwnKit), a local privilege escalation in polkit's pkexec, with embedded payload library for standalone…

binary-exploitationexploitationexploit-frameworks+2
6
4 years ago
ketshash preview

ketshash

GitHubcyberark/ketshash

A little tool for detecting suspicious privileged NTLM connections, in particular Pass-The-Hash attack, based on event viewer logs.

authenticationdefensive-toolsincident-response+3
1681 year ago
Grafana-Plugin-Enumerator-CVE-2021-43798 preview

Grafana-Plugin-Enumerator-CVE-2021-43798

GitHubsqu1shification/grafana-plugin-enumerator-cve-2021-43798

Bash-based scanner that enumerates Grafana plugin IDs and tests for CVE-2021-43798 directory traversal by attempting to read /etc/passwd or win.ini…

exploitationinformation-gatheringpenetration-testing+4
1 month ago
bypass-firewalls-by-DNS-history preview

bypass-firewalls-by-DNS-history

GitHubvincentcox/bypass-firewalls-by-dns-history

Firewall bypass script based on DNS history records. This script will search for DNS A history records and check if the server replies for that…

dns-analysispenetration-testingreconnaissance+2
1.3k6 years ago
scalpel preview

scalpel

GitHubsleuthkit/scalpel

File carving and indexing tool for digital forensics, recovering files from disk images based on header/footer pattern matching, regular expressions,…

data-recoverydigital-forensicsdisk-forensics+1
6905 years ago
PQCrypto-LWEKE preview

PQCrypto-LWEKE

GitHubmicrosoft/pqcrypto-lweke

C library implementing FrodoKEM, a post-quantum key encapsulation mechanism based on the Learning with Errors problem, with variants for AES and…

cryptographyencryption-decryption-toolssecurity-virtualization
1671 month ago
CVE-2020-10665 preview

CVE-2020-10665

GitHubspaceraccoon/cve-2020-10665

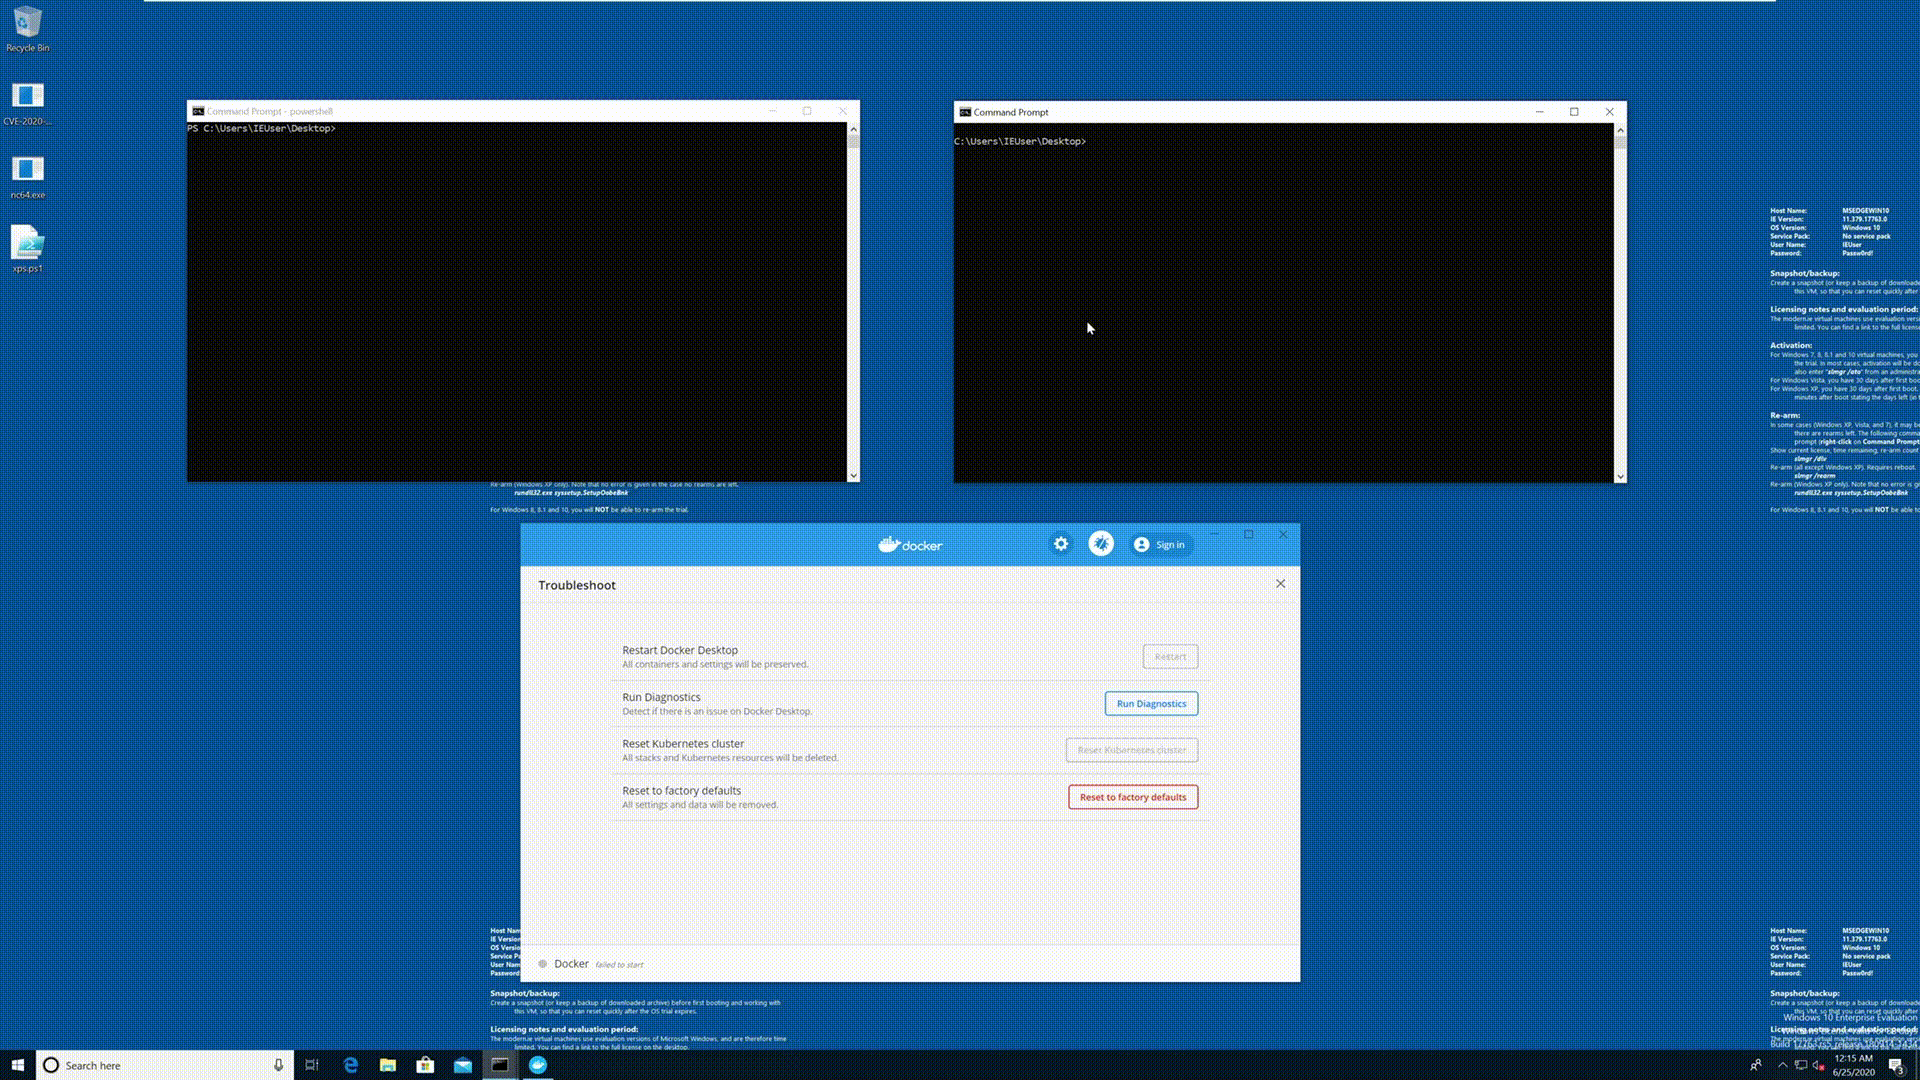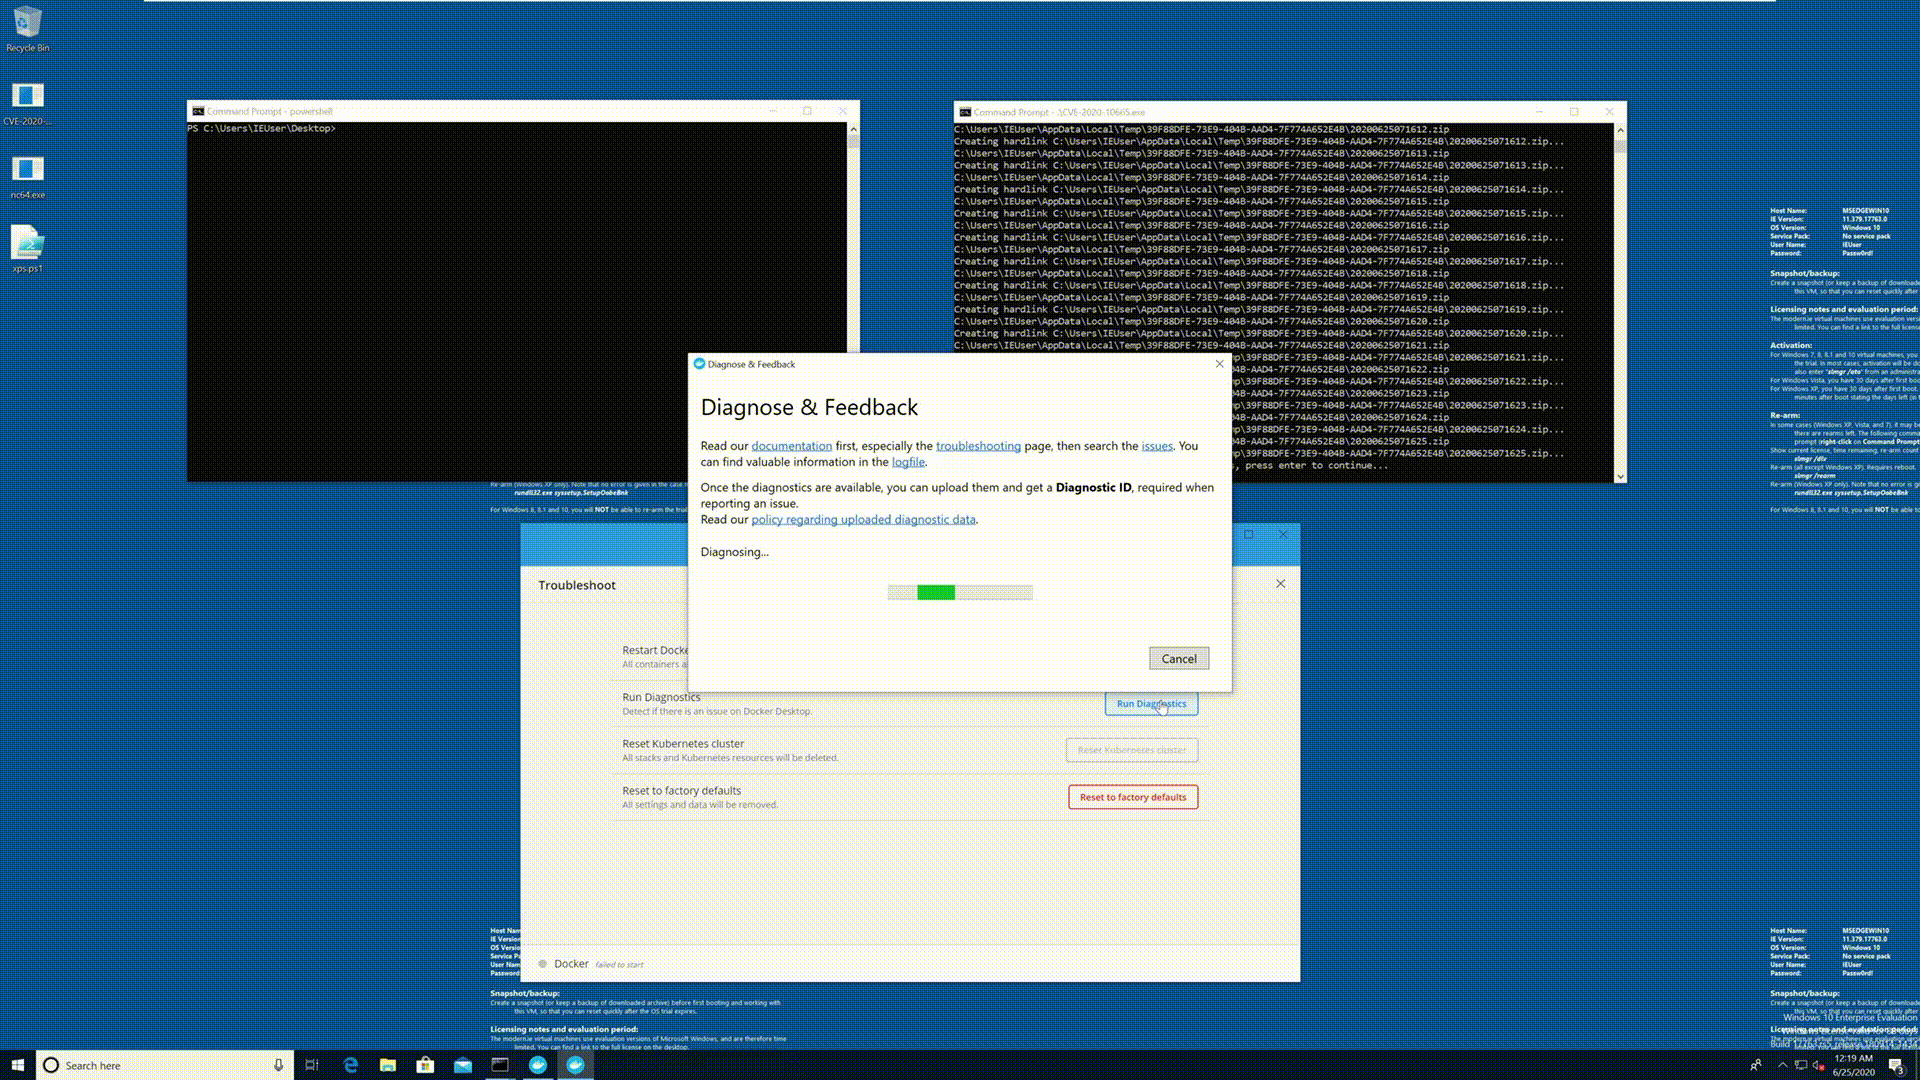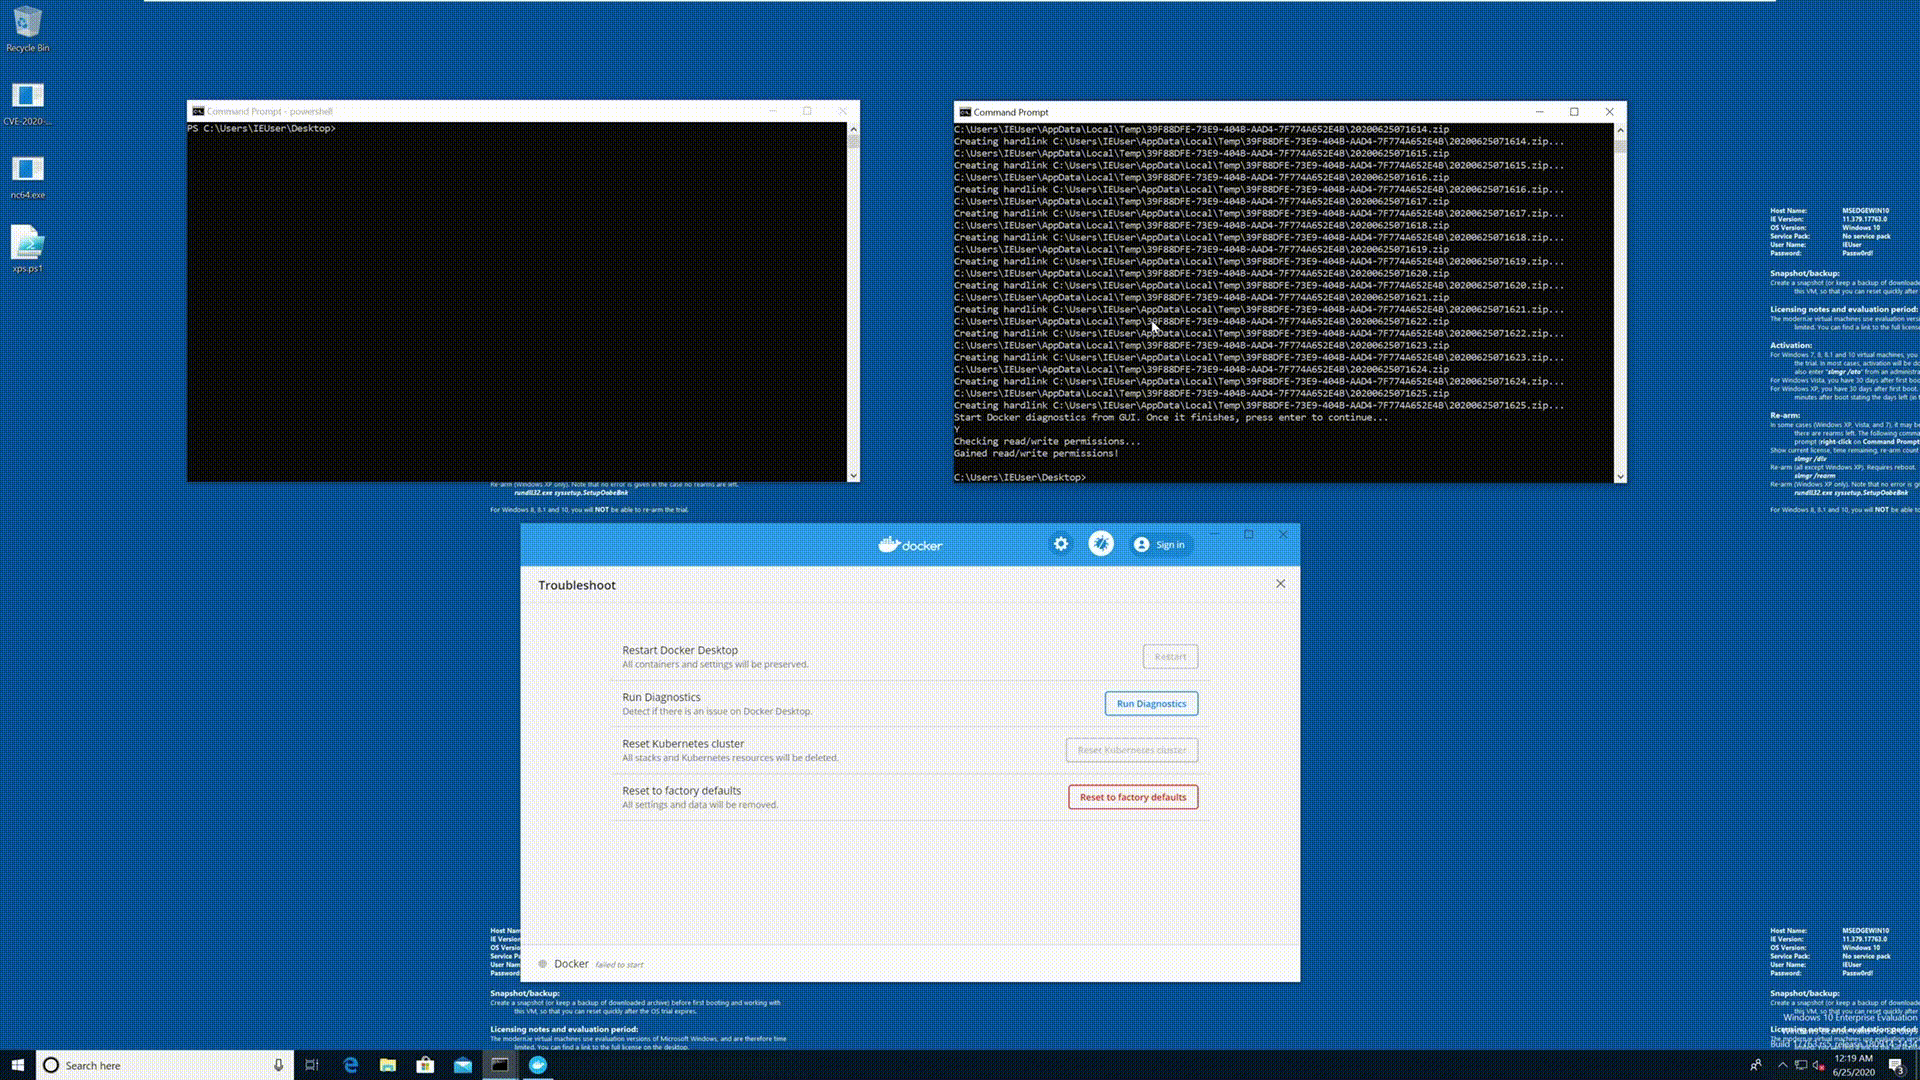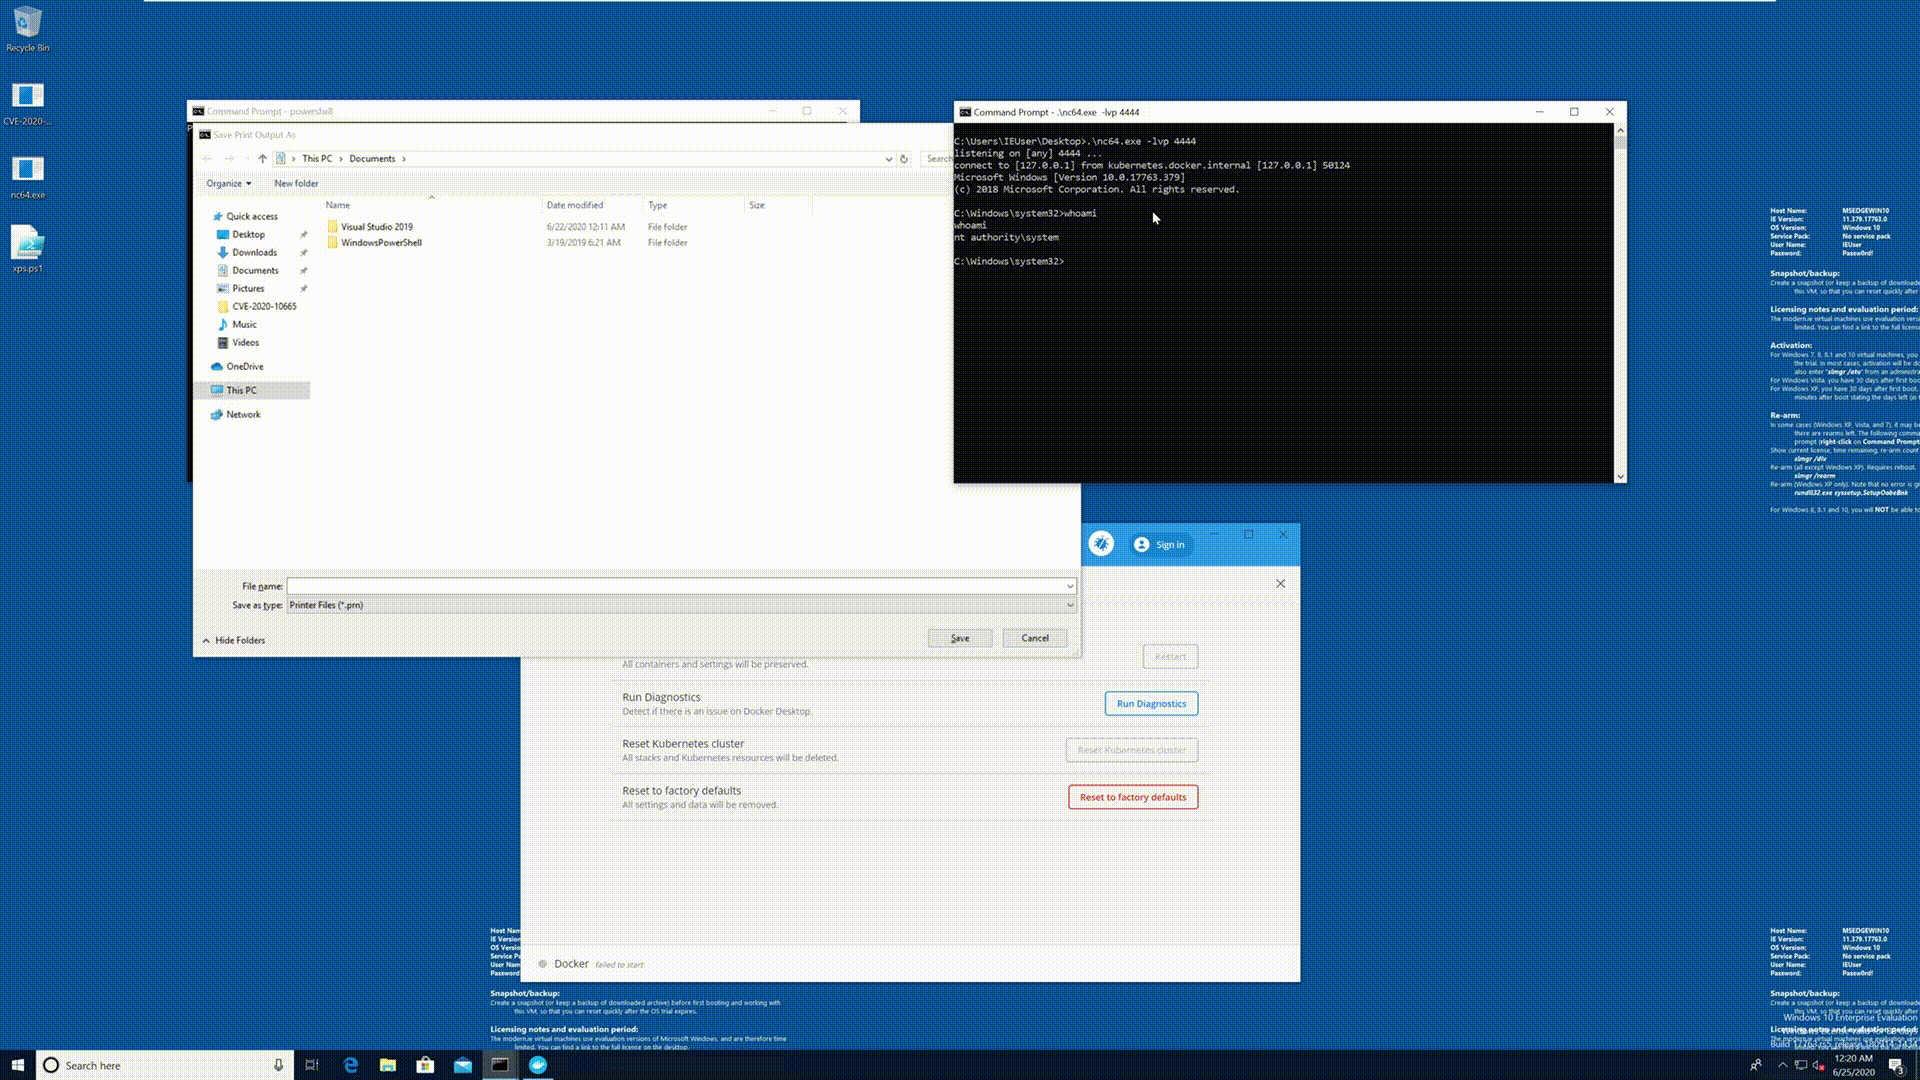
POC for CVE-2020-10665 Docker Desktop Local Privilege Escalation

binary-exploitationcontainer-securityexploitation+2
526 years ago
LOAD preview

LOAD

GitHub0xballpoint/load

Lord Of Active Directory - automatic vulnerable active directory on AWS

cloud-infrastructure-securityeducationlabs-practice+3
1553 years ago
WinRar_ACE_exploit_CVE-2018-20250 preview

WinRar_ACE_exploit_CVE-2018-20250

GitHubh4xl0r/winrar_ace_exploit_cve-2018-20250

This program is an script developed in Python which exploit the ACE vulnerability on WinRar - Vulnerability CVE-2018-20250

binary-exploitationeducationexploitation+3
7 years ago
CVE-2025-32433-Exploit-edited preview

CVE-2025-32433-Exploit-edited

GitHubchuzoux/cve-2025-32433-exploit-edited

Based on the original version:https://github.com/vulhub/vulhub/blob/master/erlang/CVE-2025-32433/exploit.py Replace Unicode checkmark with ASCII…

educationexploitationpenetration-testing+3
4 months ago
cve-2019-12750 preview

cve-2019-12750

GitHubv-p-b/cve-2019-12750

sploit

binary-exploitationexploitationprivilege-escalation+1
666 years ago
matrix-rs preview
Archived

matrix-rs

GitHubmemn0ps/matrix-rs

Rusty Hypervisor - Windows Kernel Blue Pill Type-2 Hypervisor in Rust (Codename: Matrix)

dynamic-code-analysiseducationids-ips-evasion+3
3605 months ago
lsarelayx preview

lsarelayx

GitHubccob/lsarelayx

System-wide NTLM relay tool that hooks Windows authentication APIs to relay incoming NTLM connections, downgrade Kerberos, and dump NetNTLM hashes…

authenticationexploitationpassword-attacks+2
5874 years ago
unicorn preview

unicorn

GitHubtrustedsec/unicorn

Unicorn is a simple tool for using a PowerShell downgrade attack and inject shellcode straight into memory. Based on Matthew Graeber's powershell…

command-and-controlexploit-frameworksids-ips-evasion+8
4.0k1 day ago
CMD_Bypass_Assessment preview

CMD_Bypass_Assessment

GitHubalperenugurlu/cmd_bypass_assessment

PowerShell script that automatically tests CMD bypass methods on Windows, evaluates results, calculates a security score, and provides hardening…

configuration-auditingdefensive-toolseducation+1
113 years ago
nmap preview

nmap

GitHubnmap/nmap

High-performance network discovery and security auditing tool with advanced port scanning, OS detection, service version detection, and scriptable…

bluetooth-securitydatabase-securitydata-exfiltration+18
13.9k5 days ago
Androl4b preview

Androl4b

GitHubsh4hin/androl4b

A Virtual Machine For Assessing Android applications, Reverse Engineering and Malware Analysis

android-securityeducationlabs-practice+4
1.2k6 years ago
fence preview

fence

GitHubfencesandbox/fence

Lightweight, container-free sandbox for running commands with network and filesystem restrictions

container-securitydefensive-toolsdevsecops+5
1.0k1 month ago
Previous123456Next