CVE-2026-70481
Proof-of-concept exploit for an authorization flaw in Open WebUI that lets low-privileged users edit and delete other members' channel messages via…

Proof-of-concept exploit for an authorization flaw in Open WebUI that lets low-privileged users edit and delete other members' channel messages via…

Detects unauthenticated MLflow webhook SSRF (CVE-2026-64849) that accesses internal or cloud metadata services and leaks response details via…

Reproducer for CVE-2026-46453 — Apache Camel camel-elasticsearch-rest-client unprefixed-header injection (operation/query override via inbound HTTP…

Reproducer for CVE-2026-46587: Apache Camel camel-couchbase CCB_* header injection enabling document disclosure, tampering, and TTL-forced data…

Proof-of-concept exploit and advisory for CVE-2026-54356, a Budibase missing-authorization flaw that lets low-privilege users mint S3 pre-signed…

PoC reproducer for CVE-2026-49099 (Apache Camel camel-salesforce): the non-Camel-prefixed sObjectQuery header escapes the HTTP header filter and…

Local Docker lab for reproducing CVE-2026-55255, an IDOR vulnerability in Langflow's Responses API. Validates cross-user flow execution in vulnerable…

Reproducer for CVE-2026-46588: Apache Camel camel-couchdb CouchDb* header injection (operation confusion) subverting a write-only endpoint into read…

Reproducer for CVE-2026-48204: Apache Camel camel-mongodb-gridfs gridfs.* header injection overriding the GridFS operation (enumerate/read/delete…

Milvus 认证安全检测脚本:CVE-2025-64513 (sourceid后门) / CVE-2026-26190 (/expr弱token) / 内部端口53100

PoC and detection guide for the critical unauthenticated RCE in IBM Langflow OSS, covering the auto_login token bypass and unsafe /validate/code…

CVE-2023-23752 nuclei template

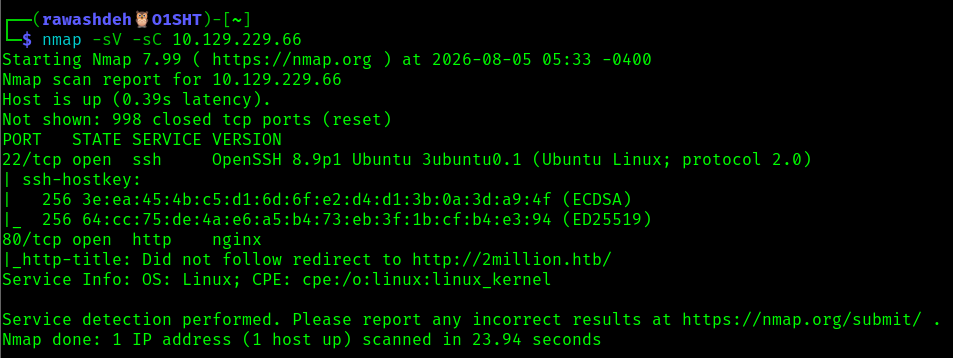
Hack The Box TwoMillion machine writeup — JWT/invite-code bypass, IDOR, command injection, and CVE-2023-0386 privilege escalation.

Scanner: CVE-2025-34291 Langflow Origin Validation Error / CORS Misconfiguration — Python checker (CISA KEV)

Drop-in fix for the unpatched MCP STDIO command-injection flaw (CVE-2026-30623 family)

GitHub Action for Offensive360 SAST scans and SARIF results. See the open-source program for eligibility and setup.

Find the vulnerability your tests were never written to catch. A ReGrade demo modeling CVE-2023-5968: catch a password-hash leak by comparing an app…

MCP server that runs SAST scans on local codebases and returns findings with severity and fixes, enabling AI assistants to perform security analysis…