
CVE-2026-34344
 nhh9905/cve-2026-34344
PoC for CVE-2026-34344, a Windows afd.sys type confusion causing a kernel crash via AfdQueryProviderInfo. Provides trigger code, crash log, and…
binary-exploitationeducationexploitation+1
2
nhh9905/cve-2026-34344PoC for CVE-2026-34344, a Windows afd.sys type confusion causing a kernel crash via AfdQueryProviderInfo. Provides trigger code, crash log, and…
 jaf0rk/cve-2026-5281
Proof-of-concept exploit for CVE-2026-5281, a heap-use-after-free vulnerability in Chromium's Dawn WebGPU implementation, with ASAN log and build…
 skelersecurity/wordpress-skelersecurity-core-security-cve-2026-63030
Temporary WordPress plugin requiring authentication for the Core REST Batch API endpoint to mitigate the wp2shell vulnerability chain…
 layer-6/cve-2026-5027-langflow
Multi-CVE exploit tool for pre-auth remote code execution on Ivanti Sentry and FortiSandbox. Features interactive shell, webshell deployment,…
 vinh0212/cve-2024-23700
PoC for CVE-2024-23700, Android slient privilege escalation allow to read/write contacts, SMS, calendar, call log and voicemail, make outgoing calls…
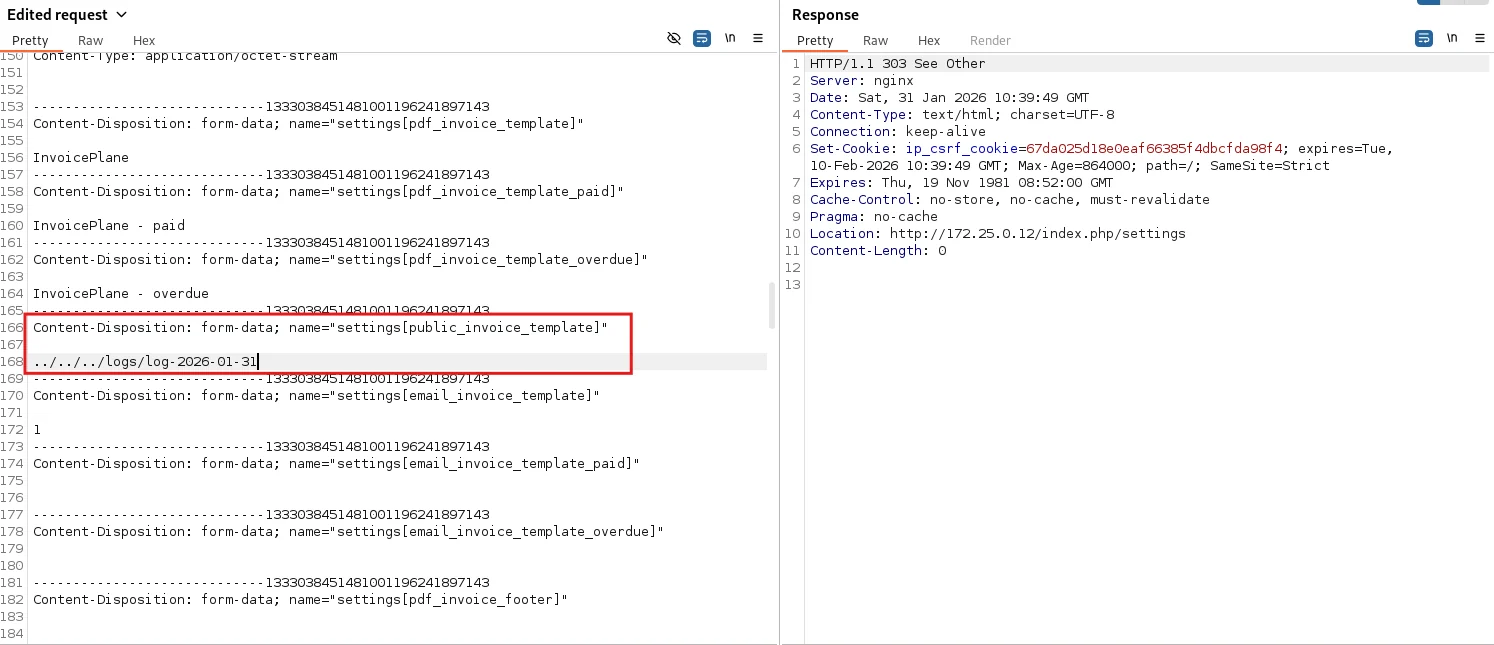 lagathos/cve-2026-25548
Detailed technical write-up and proof-of-concept for CVE-2026-25548, a critical RCE in InvoicePlane 1.7.0 via LFI and log poisoning, including attack…
 kairo-one/cve-2023-26469-jorani
Proof-of-concept exploit for CVE-2023-26469 targeting Jorani 1.0.0. Combines path traversal and log injection to achieve remote code execution with…
 lopqto/cve-2021-41773_honeypot
Lightweight honeypot for Apache HTTP Server path traversal vulnerability CVE-2021-41773, designed to capture and log exploitation attempts.
 security-onion-solutions/security-onion
Security Onion 16.04 - Linux distro for threat hunting, enterprise security monitoring, and log management
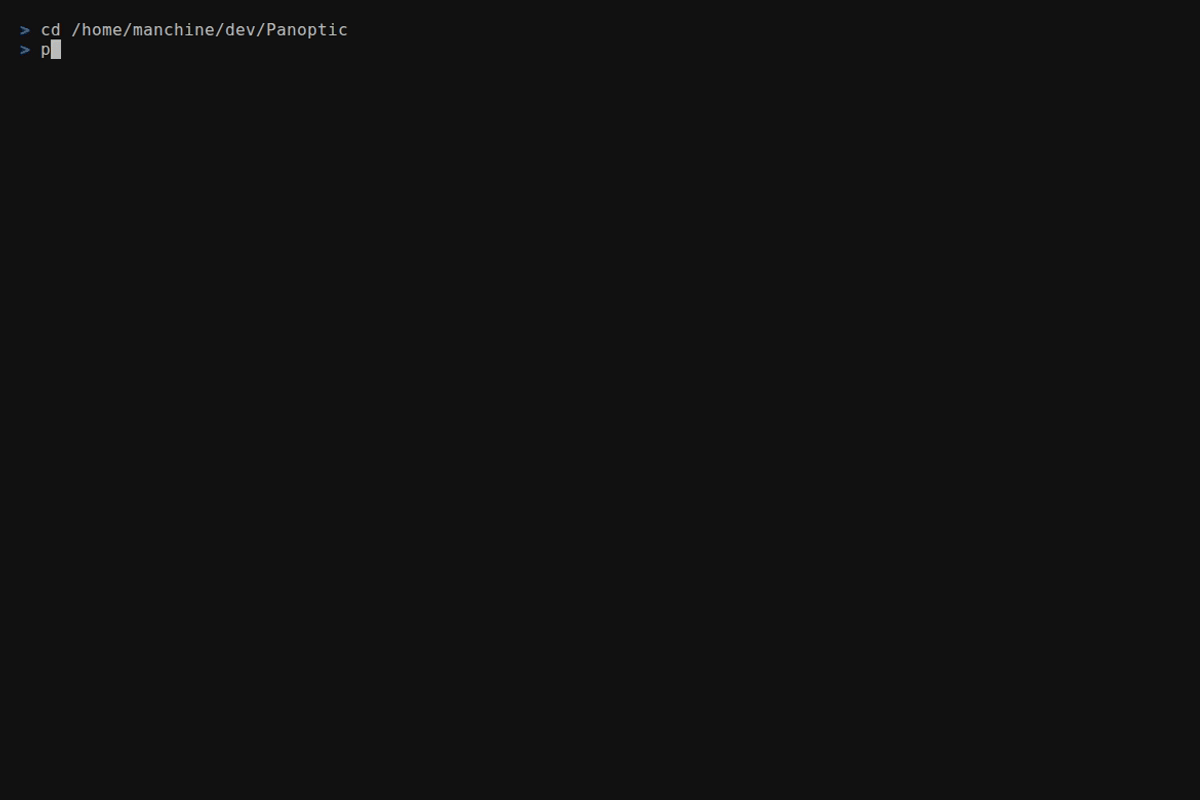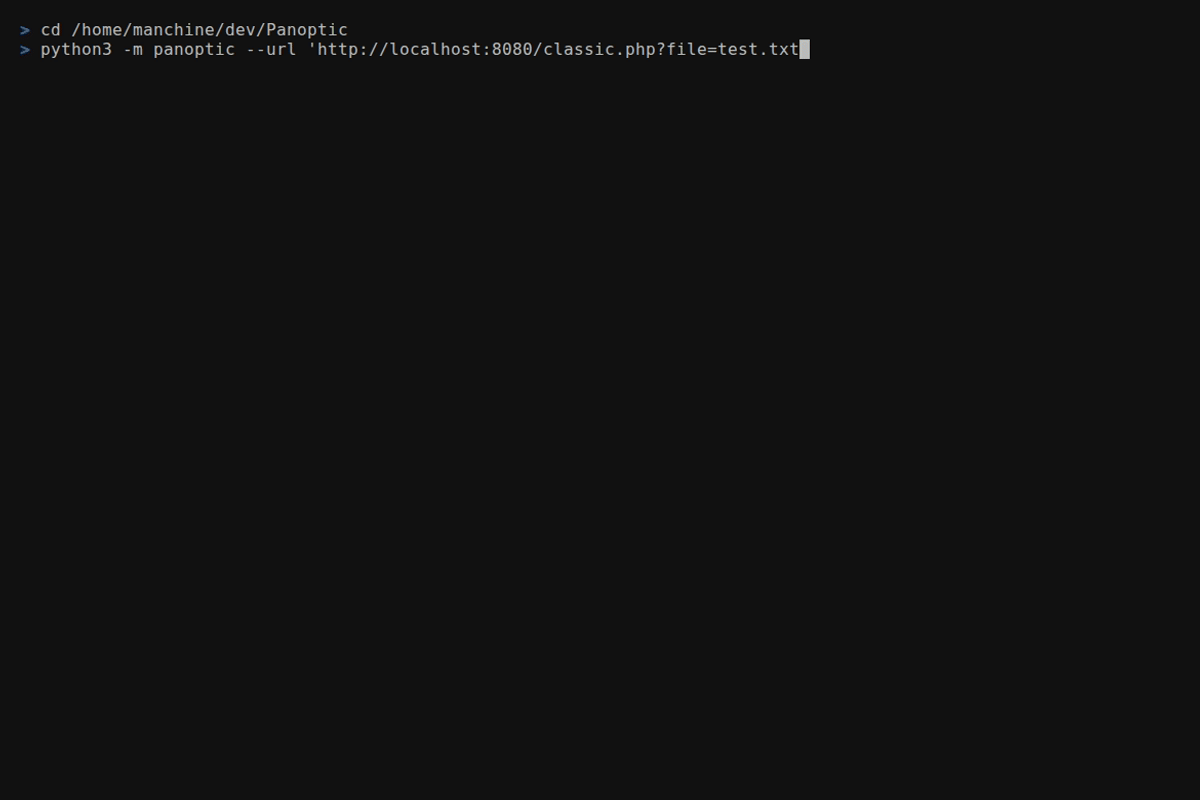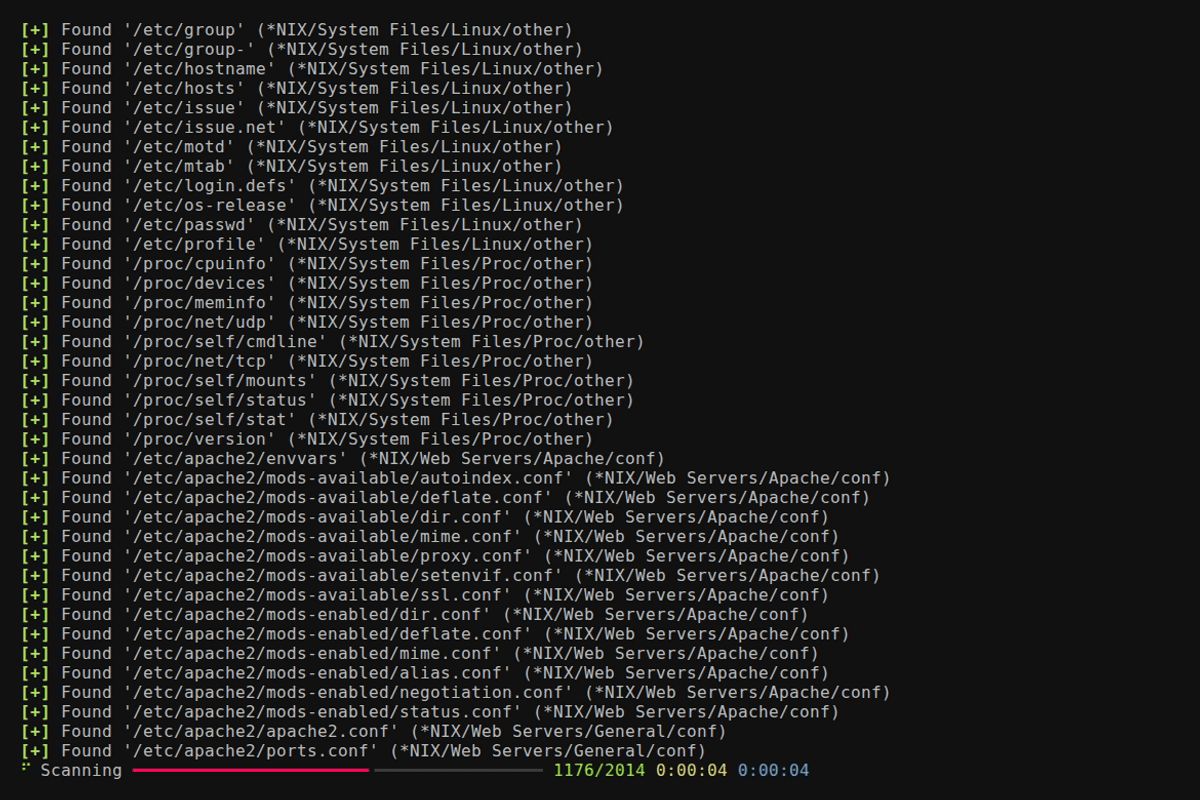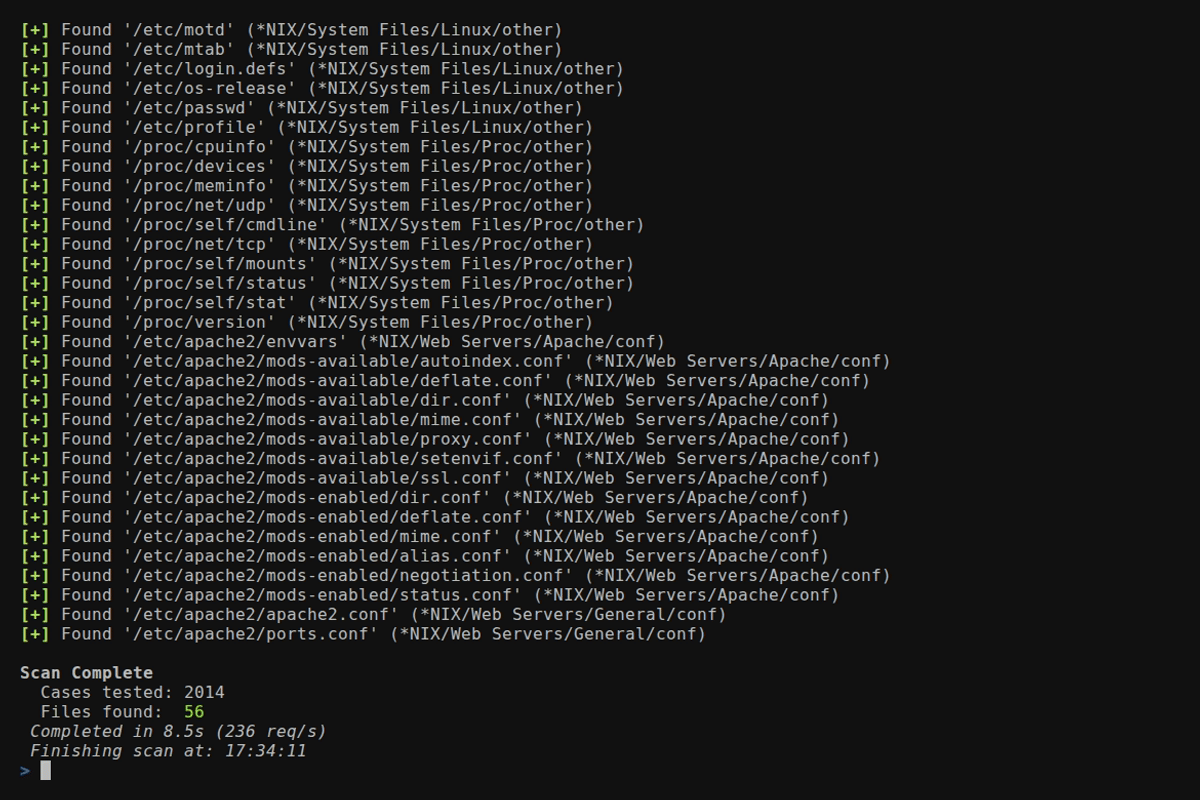 lightos/panoptic
Panoptic is an open source penetration testing tool that automates the process of search and retrieval of content for common log and config files…
 garrettfoster13/aced
Parses and resolves a single Active Directory principal's DACL to identify inbound access privileges, resolve SIDs, and log LDAP attributes for…
 mkultra6969/anysniff
AnySniff is a tool for monitoring TCP connections of processes like AnyDesk on Windows. It uses the CVE-2024-52940 vulnerability to track open…
 mdanzaruddin/cve-2021-33558.
Exploit code for CVE-2021-33558 targeting Boa/0.94.13 misconfigurations that expose sensitive information via backup, preview, log, and config files.
 intel-xeon/cve-2021-44228---detection-with-powershell
PowerShell-based scanner to detect Log4j CVE-2021-44228 vulnerability by searching directories and log files for exploitation indicators.
 security-onion-solutions/securityonion
Open-source security monitoring platform for threat hunting, intrusion detection, log management, incident response, and endpoint visibility with…
 pablosnt/rekono
Offensive security platform that automates attack surface discovery and vulnerability management
 randomuserid/adama
Searches For Threat Hunting and Security Analytics
 jay123anta/laravel-threat-detection
Passive Laravel middleware that detects and logs SQL injection, XSS, RCE, bot scanners, and 175+ attack patterns. Features a built-in dashboard,…