
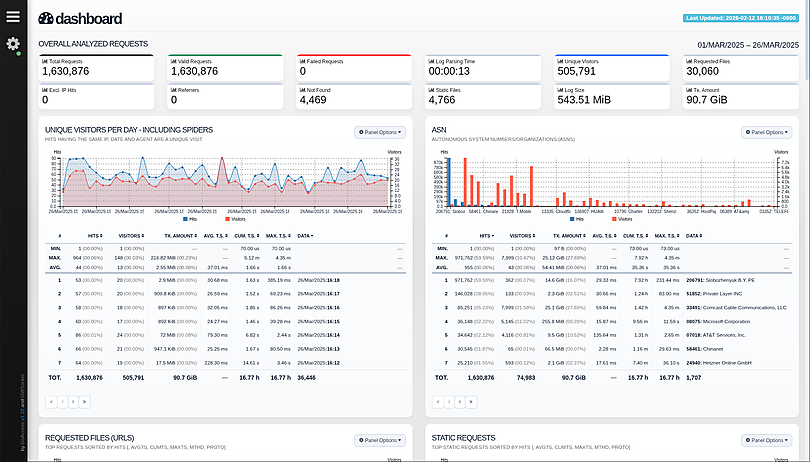
goaccess
 allinurl/goaccess
GoAccess is a real-time web log analyzer and interactive viewer that runs in a terminal in *nix systems or through your browser.
anomaly-detectiongeneral-purpose-utilitieslog-analysis+1
20.9k
allinurl/goaccessGoAccess is a real-time web log analyzer and interactive viewer that runs in a terminal in *nix systems or through your browser.
 nxploited/cve-2024-12849-poc
Exploit for CVE-2024-12849, an arbitrary file read vulnerability in WordPress Error Log Viewer plugin. Downloads sensitive files via unauthenticated…
 cyberark/ketshash
A little tool for detecting suspicious privileged NTLM connections, in particular Pass-The-Hash attack, based on event viewer logs.
 jonny-jhnson/ldapmon
Proof-of-concept telemetry collector for Windows LDAP client activity via ETW, logging structured events to Event Viewer with a Sentinel parser for…
 0x4d31/awesome-threat-detection
Curated list of threat detection and hunting resources: detection rules, SIEM and log analysis tools, endpoint/network monitoring, datasets,…
 horizon3ai/vcenter_saml_login
A tool to extract the IdP cert from vCenter backups and log in as Administrator
 realitynet/android-forensics-references
Curated reference for Android forensic artifacts and log paths, with links to CTF writeups, research papers, and mobile device analysis tooling.
 mrash/psad
psad: Intrusion Detection and Log Analysis with iptables
 andrewmichaelsmith/bluepot
Java-based Bluetooth honeypot that captures and stores malware from BlueBugging and BlueSnarfing attacks, with a GUI for monitoring and log analysis.

 sultanahamer/opencontacts
Android contact manager that stores contacts in an isolated database, preventing other apps from accessing them. Provides call log and caller ID…
 malwaretech/citrixhoneypot
Detect and log CVE-2019-19781 scan and exploitation attempts.
 nhh9905/cve-2026-62735
Proof-of-concept for CVE-2026-62735, an integer overflow in http.sys leading to heap overflow and SYSTEM shell. Includes crash log and stack trace…
 alloysecuregroup/phantomfs
Windows honeypot using ProjFS to project decoy files that trigger Event Log and desktop alerts when accessed, with SMB remote session logging for…
 canyie/cve-2024-23700
PoC for CVE-2024-23700, Android slient privilege escalation allow to read/write contacts, SMS, calendar, call log and voicemail, make outgoing calls…
 twocanoes/audit
Audit Preference Pane and Log Reader for OS X
 signalapp/key-transparency-auditor
Continuously fetches and cryptographically verifies key transparency log updates, maintains a condensed prefix and log tree view, and returns signed…
 eriknl/cve-2020-16152
Proof-of-concept exploit for CVE-2020-16152: LFI-to-RCE in Aerohive/Extreme Networks HiveOS via PHP string truncation and log poisoning, enabling…
 cxlfhx/ghostlock-pfem10
GhostLock (CVE-2026-43499 / IonStack) research for OPPO Find X5 Pro (PFEM10): exploit chain, progress, blocker log, and OPPO 5-series kernel notes