

web-threat-mitigation
 brunoh6/web-threat-mitigation
Hands-on lab on detecting and mitigating web app threats using OWASP ZAP, Burp Suite, and ModSecurity WAF (with OWASP CRS). Case study: Spring4Shell…
configuration-auditingdevsecopseducation+8
brunoh6/web-threat-mitigationHands-on lab on detecting and mitigating web app threats using OWASP ZAP, Burp Suite, and ModSecurity WAF (with OWASP CRS). Case study: Spring4Shell…
 khaliquesx/cve-2024-48415
Proof-of-concept for CVE-2024-48415: stored XSS vulnerability in itsourcecode Loan Management System v1.0 via borrower profile fields. Includes…
 nvisium-jack-mannino/owasp-goatdroid-project
*This project is no longer maintained* OWASP GoatDroid is a fully functional and self-contained training environment for educating developers and…
 spiderlabs/owasp-modsecurity-crs
OWASP ModSecurity Core Rule Set (CRS) Project (Official Repository)
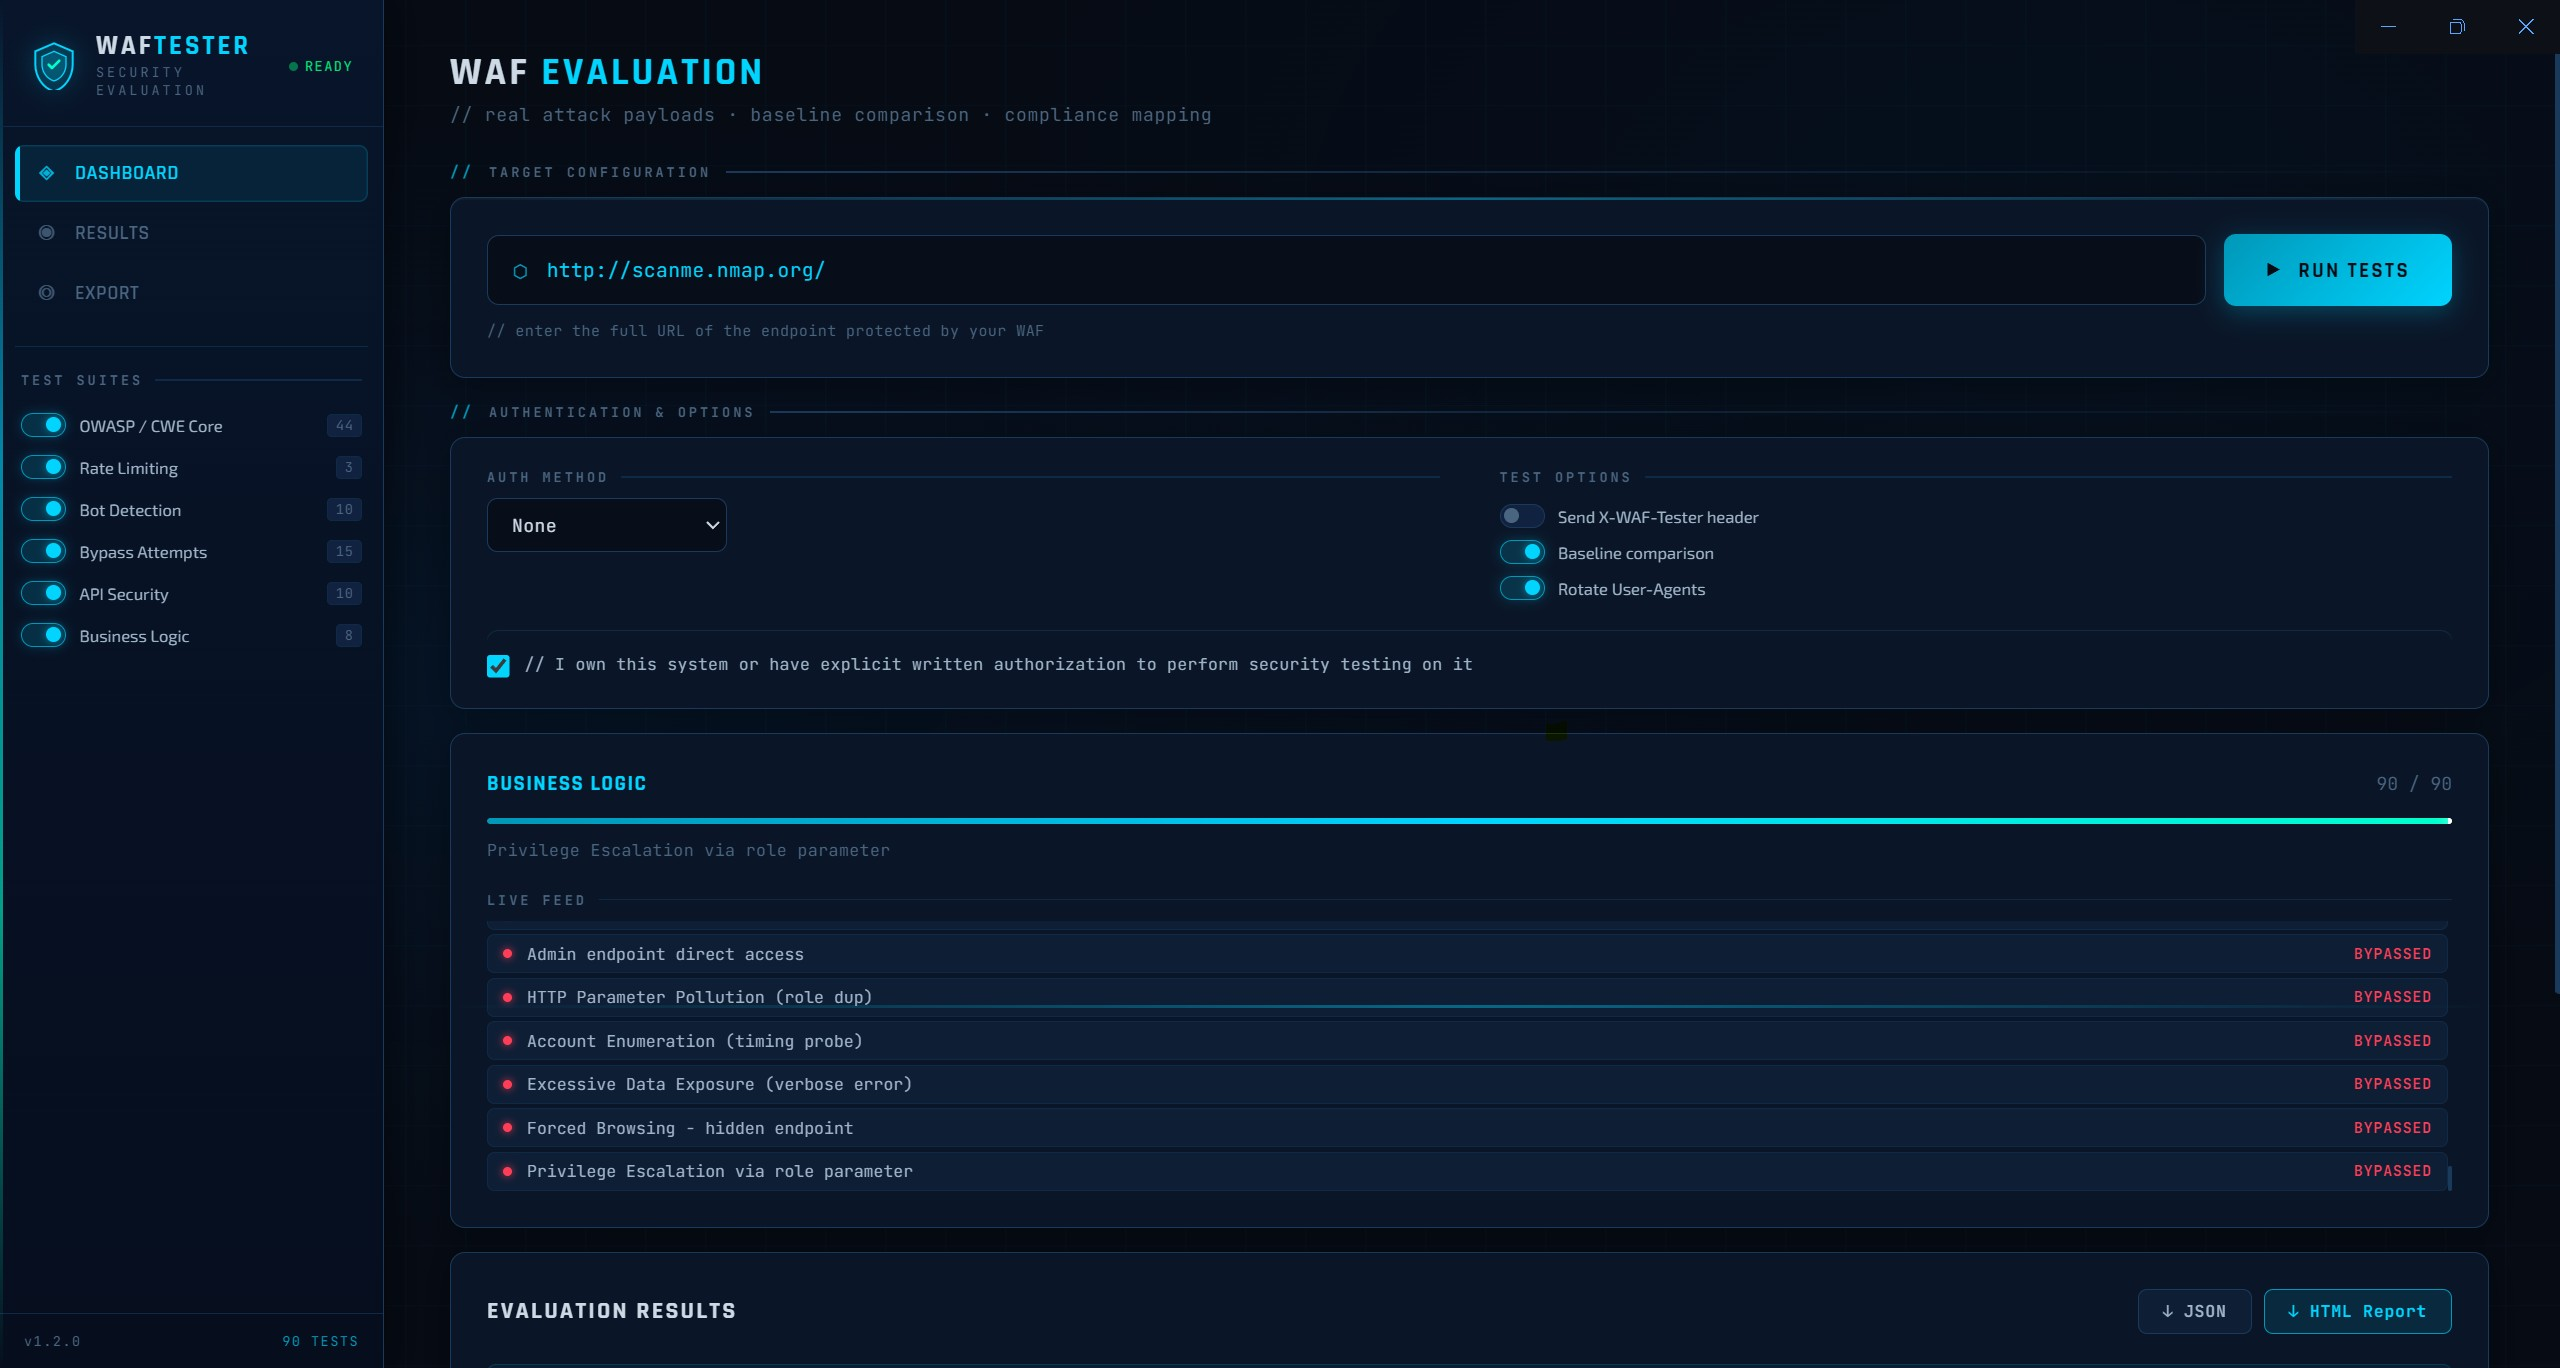 kpomin57/waf-tester
A program for testing WAF functionality
 ottosulin/awesome-ai-security
A collection of awesome resources related AI security
 bugcrowd/hunt
Flags parameters commonly associated with injection, SSRF, path traversal, IDOR, and SSTI, via passive Burp/ZAP scanning; also organizes manual…
 owasp-dep-scan/dep-scan
Next-generation dependency vulnerability scanner with reachability analysis, SBOM generation, license audit, and container image scanning for CI/CD…
 ine-labs/azuregoat
AzureGoat : A Damn Vulnerable Azure Infrastructure
 factionsecurity/faction
Pen Test Report Generation and Assessment Collaboration
 ine-labs/gcpgoat
GCPGoat : A Damn Vulnerable GCP Infrastructure
 palindromelabs/stews
A Security Tool for Enumerating WebSockets
 bhavsec/autopentest-ai
Agentic Pentesting MCP server that discovers, exploits, and reports web application vulnerabilities.
 mthbernardes/artlas
Apache Real Time Logs Analyzer System
 ghostwolflab/ai_security_top
A structured knowledge base covering AI security fundamentals, threat modeling, red team offensive techniques, and blue team defenses, including LLM…
 wireghoul/lbmap
Advanced HTTP fingerprinting PoC
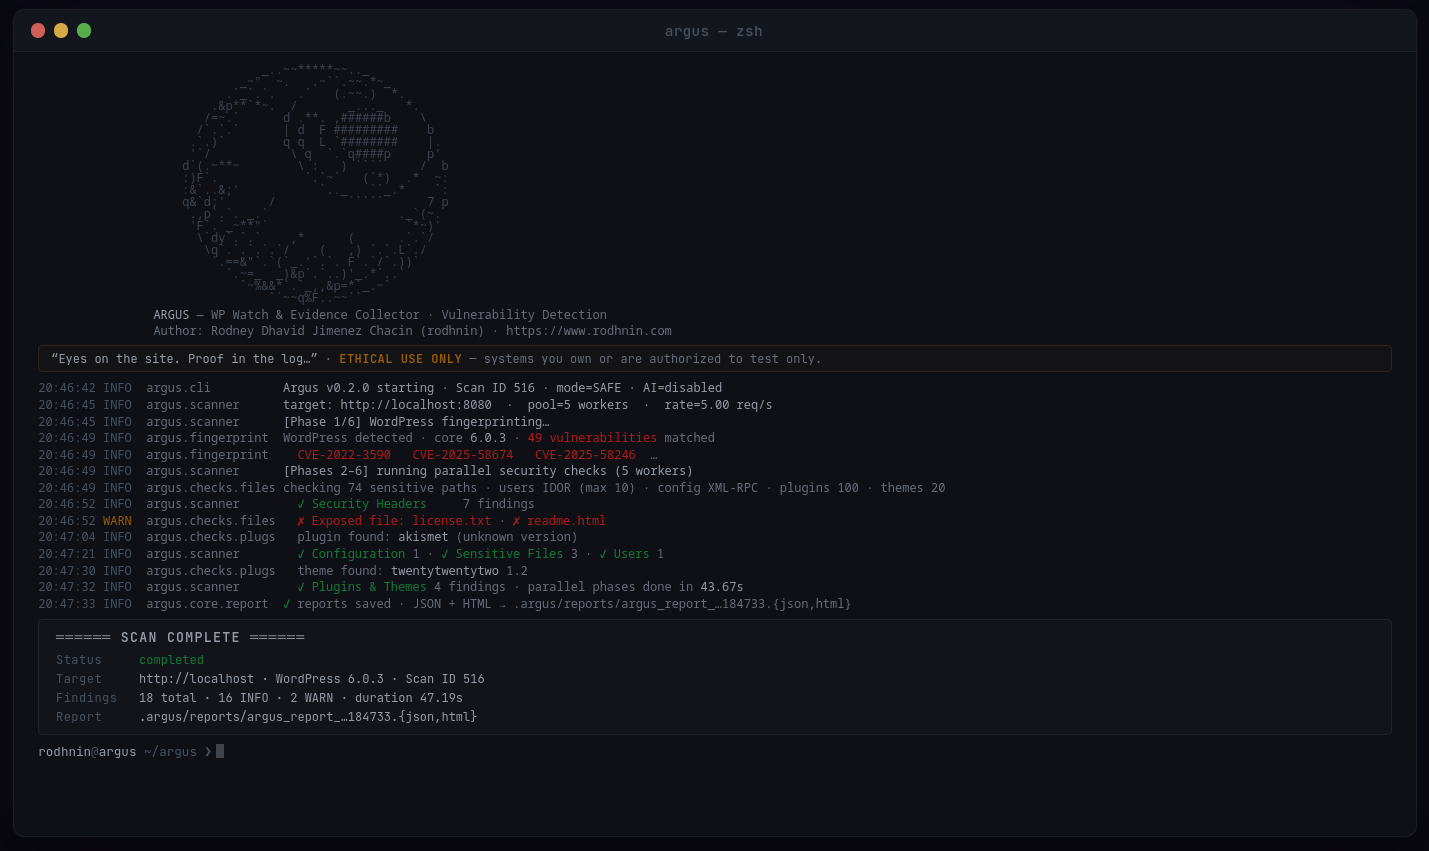 rodhnin/argus-wp-watcher
WordPress security scanner with AI-powered analysis, ethical compliance framework, and professional reporting.
 boku7/cve-2020-23839
Public PoC Disclosure for CVE-2020-23839 - GetSimple CMS v3.3.16 suffers from a Reflected XSS on the Admin Login Portal