mimosa
 owasp/mimosa
Open-source web application security challenge platform with auto-approved registration, SQL dump generation, and Docker deployment for hands-on…
ctfeducationlabs-practice+3
owasp/mimosaOpen-source web application security challenge platform with auto-approved registration, SQL dump generation, and Docker deployment for hands-on…
owasp/ninja-pinguHigh-performance network scanner for large-scale IP and port scanning with service identification, embedded device detection, and vulnerability…
 owasp/threat-model-cookbook
This project is about creating and publishing threat model examples.
 corazawaf/coraza
Go-based Web Application Firewall library compatible with ModSecurity SecLang rules and OWASP Core Rule Set v4, providing real-time HTTP traffic…
 1n3/blackwidow
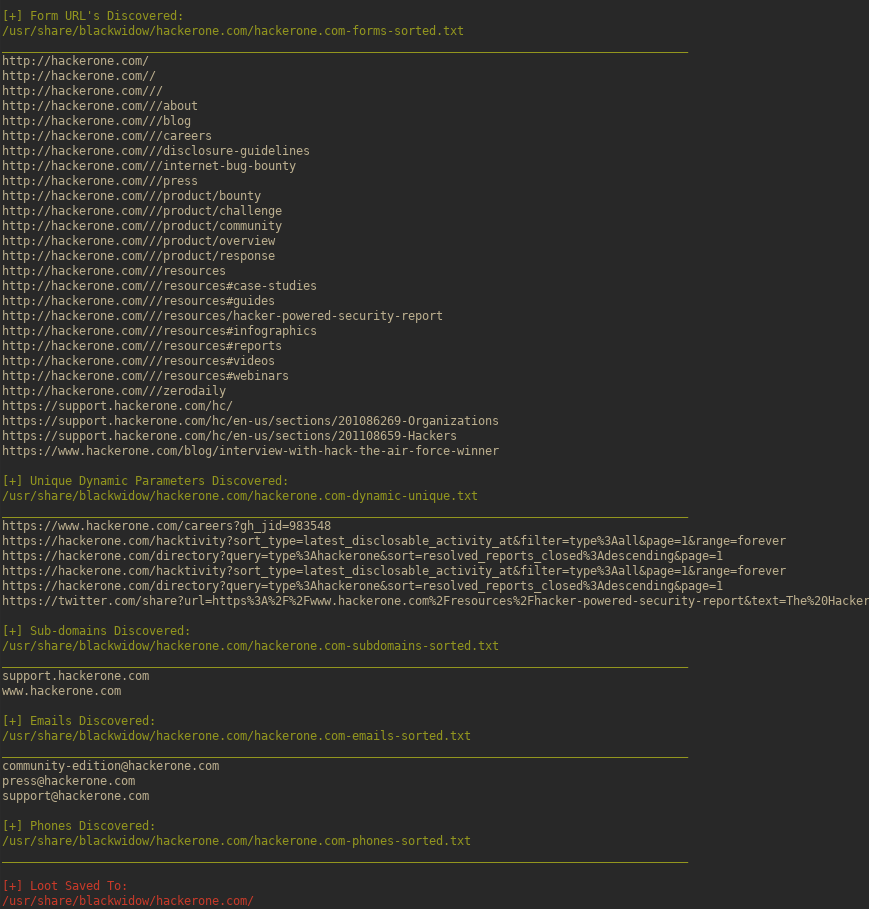
A Python based web application scanner to gather OSINT and fuzz for OWASP vulnerabilities on a target website.
 moeinfatehi/admin-panel_finder
Burp Suite extension that finds exposed admin panels and login pages of web applications and infrastructure. 1,000+ payloads, OWASP WSTG-CONF-05.
 doretox/atomicvulns
Atomic web vulnerability labs. One OWASP flaw per app — minimal Flask + Docker, intentionally broken for hands-on study with Burp Suite.
 dheeraj-jayaswal/cicd-goat-vapt-writeup
Full VAPT writeup of OWASP CICD-Goat — 9 CTFd flags captured, 4 critical + 5 high findings (incl. CVE-2024-23897) mapped to the OWASP Top 10 CI/CD…
 nexaiceo/nexus-os
The Governed Agentic AI Operating System — Rust + Tauri 2.0 | 65 crates, 658 commands, 84 pages, 5,029 tests, 10/10 OWASP
 sarthak4126/web-app-pentesting
Web application penetration testing lab — vulnerable Flask app, automated scanner, and professional pentest report. Covers OWASP Top 10, SQLi, XSS,…
 domain-protect/domain-protect
OWASP Domain Protect - prevent subdomain takeover
 owasp-amass/amass
In-depth attack surface mapping and asset discovery
 wallarm/gotestwaf
An open-source project in Golang to asess different API Security tools and WAF for detection logic and bypasses
 dipjyotimetia/hybridtestframework
End to End testing of Web, API, Cloud, Events and Security
 syscallx-18113/apkx-hunter
C-based Android static analysis framework for decompilation, secret detection, endpoint discovery, permission analysis, and native library scanning…
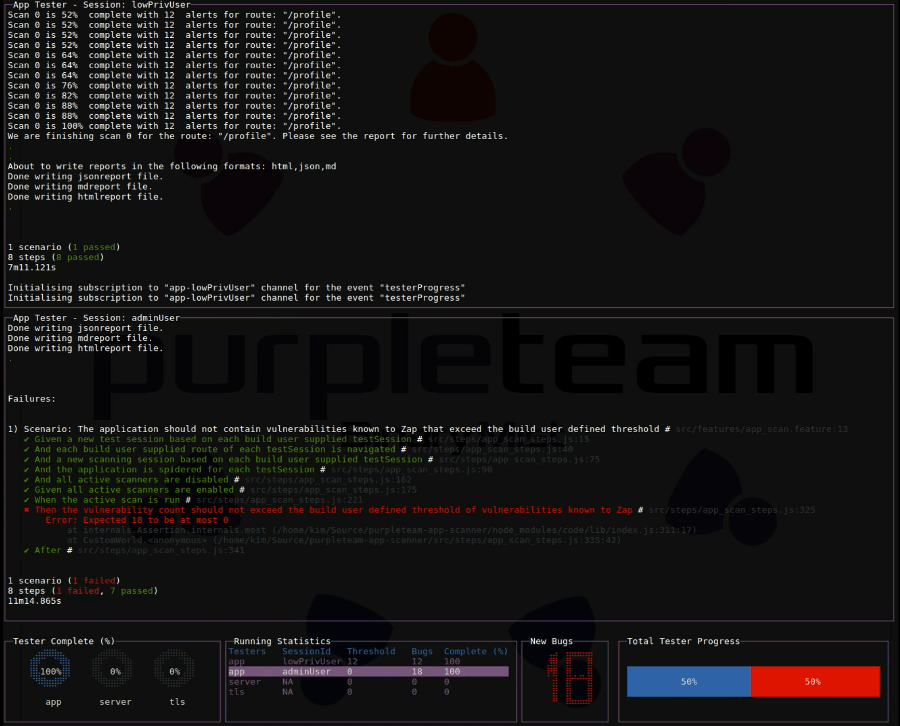 purpleteam-labs/purpleteam
CLI component of purpleteam
 purpleteam-labs/purpleteam-app-scanner
Application scanning component of purpleteam
 purpleteam-labs/purpleteam-server-scanner
Server scanning component of purpleteam