x-stream__xstream_CVE-2021-21345_1-4-15

Java XML serialization library with a focus on CVE-2021-21345 exploit analysis and deserialization vulnerability testing for web applications.

Java XML serialization library with a focus on CVE-2021-21345 exploit analysis and deserialization vulnerability testing for web applications.

通过 jvm 启动参数 以及 jps pid进行拦截非法参数

Documentation and reverse engineering of reCAPTCHA

GNU IFUNC is the real culprit behind CVE-2024-3094


Next generation web scanner

Automatic SSTI detection tool with interactive interface

WordPress security scanner that detects vulnerabilities, enumerates plugins/themes/users, and checks for weak passwords. Integrates with the WPScan…

Fast XSS scanner with parameter analysis, WAF fingerprinting, and DOM/AST verification. Supports reflected, stored, and DOM-based XSS detection via…

A coding-agent skill for multi-phase security audits with independently verified, machine-readable findings

Exploit for Jenkins serialization vulnerability - CVE-2016-0792

Laravel debug mode - Remote Code Execution (RCE)

Academic research on N-Day Linux kernel vulnerabilities, analyzing CVE-2024-36886 in the TIPC networking subsystem, lifecycle, impact, and mitigation…

Python exploit script for CVE-2020-28458, a prototype pollution vulnerability in DataTables. It sends crafted payloads to target URLs, supports proxy…

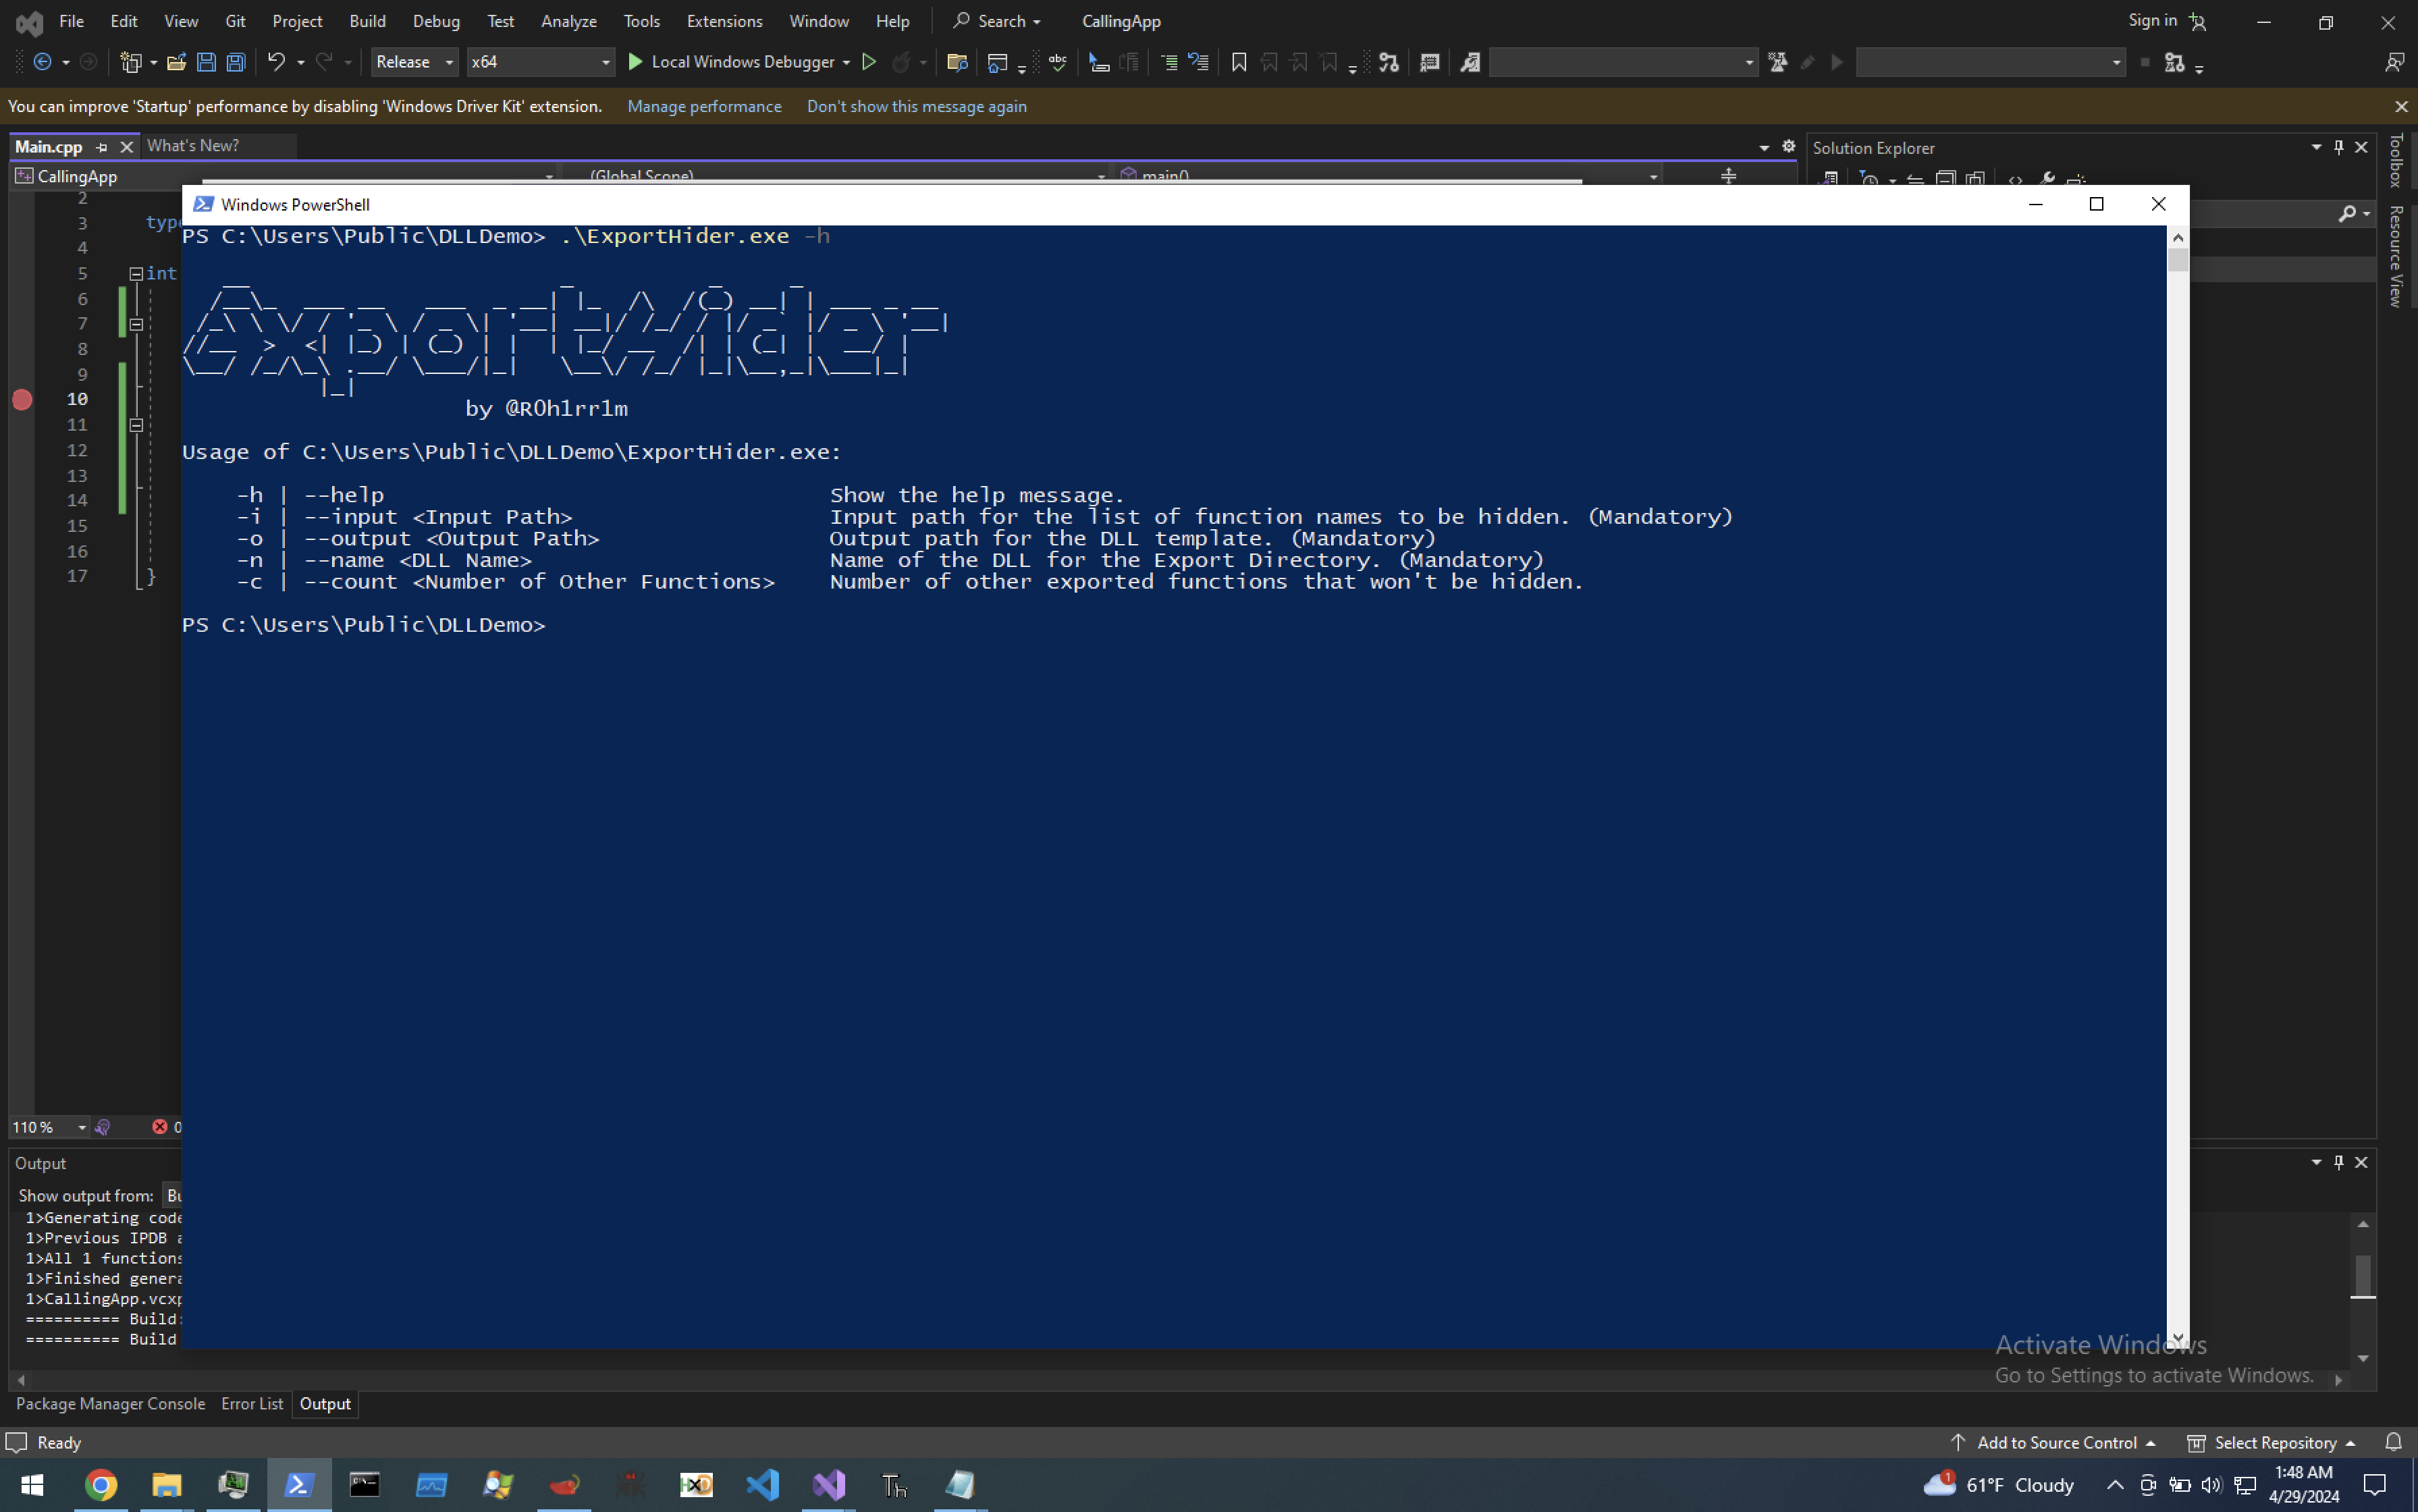
ExportHider: Generating Export Table during Runtime to Hide the Exported Functions from the DLL File.

Automated DLL Hijacking Discovery, Validation, and Confirmation. Turning local misconfigurations into weaponized, confirmed attack paths.

Web vulnerability scanner and exploitation tool with POC/EXP modes for known CVEs across webapps such as Weblogic, Shiro, Struts2, and Tomcat;…

Automated Web Application Firewall fingerprinting tool that identifies and detects over 200 WAF products by analyzing HTTP responses to normal and…