
 owasp/damn-vulnerable-ml-model
Intentionally vulnerable machine learning model for hands-on security training. Explore common ML vulnerabilities, adversarial attacks, and defensive…
 wireghoul/lbmap
Advanced HTTP fingerprinting PoC
 owasp/tcasvs
OWASP Thick Client Application Security Verification Standard
 owasp/top10
Official OWASP Top 10 Document Repository
 silentchainai/silentchain
AI-powered vulnerability scanner extension for Burp Suite with multi-provider support (Ollama, OpenAI, Claude, Gemini)
 appsecco/dvcsharp-api
Damn Vulnerable C# Application (API)
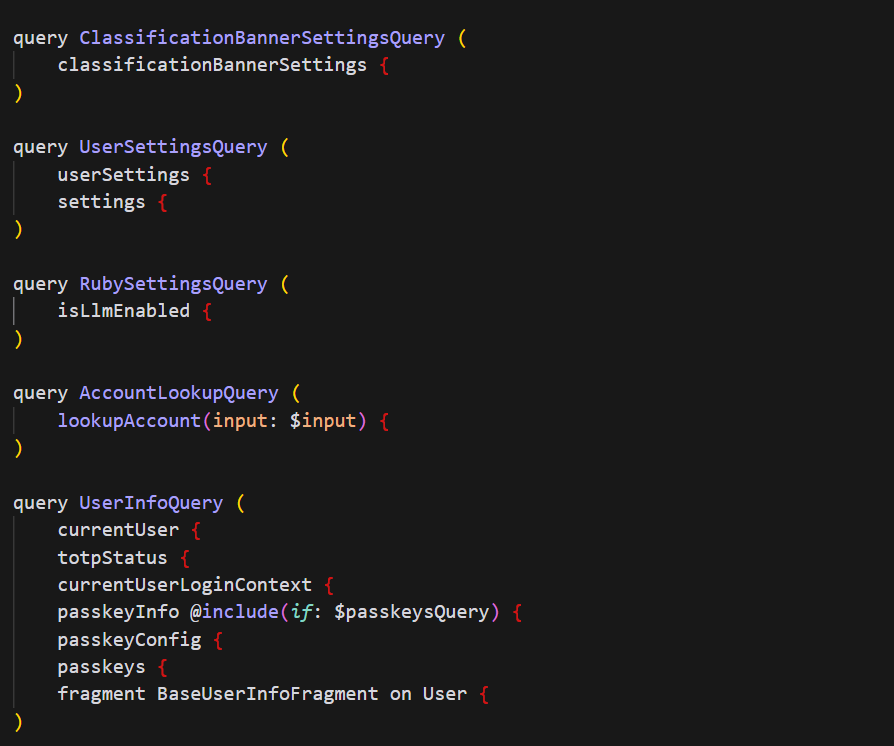 m19o/graphqlgrapper
Burp Suite extension to extract and collect GraphQL API endpoints from HTTP request history for security testing and reconnaissance.
 zaproxy/zap-api-rust
Rust client library for the OWASP ZAP API, enabling programmatic access to web application security scanning, vulnerability detection, and proxy…
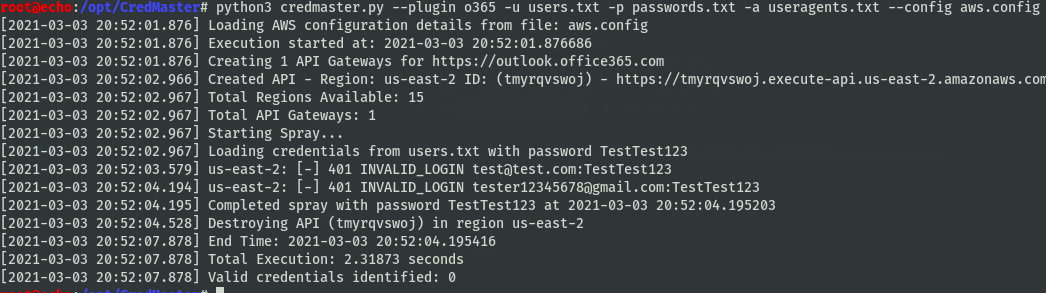 knavesec/credmaster
Refactored & improved CredKing password spraying tool, uses FireProx APIs to rotate IP addresses, stay anonymous, and beat throttling
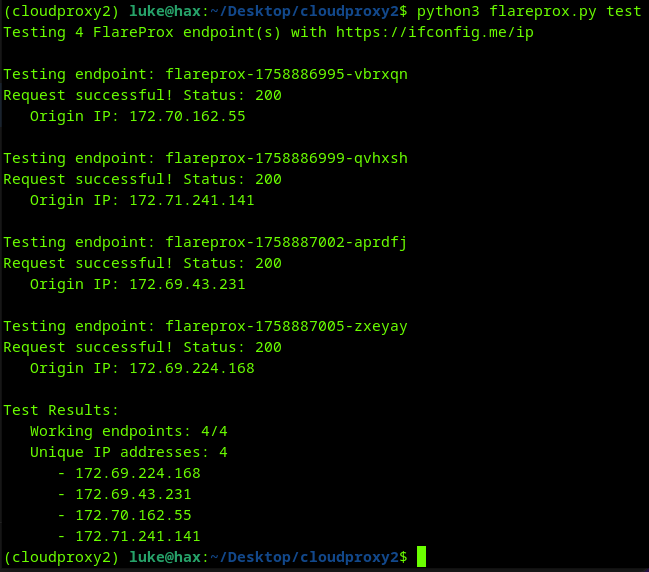 mrturvey/flareprox
Use Cloudflare to create HTTP pass-through proxies for unique IP rotation, similar to fireprox
 emo-crab/slinger
An HTTP client specifically developed for security researchers
 projectdiscovery/chaos-client
Go client to communicate with Chaos DB API.
 owasp/owaspbugbounty
This is a container of web applications that work with OWASP Bug Bounty for Projects
 owasp/owaspwebgoatphp
A deliberately vulnerable web application for learning web application security.
 owasp/packman
A documentation and tracking project with the goal of making package management systems more secure.
 owasp/pscf
OWASP framework providing structured security capabilities for software products, derived from regulatory and industry standards analysis to guide…