

Rubeus
 ghostpack/rubeus
Trying to tame the three-headed dog.
authenticationexploitationlateral-movement+6
ghostpack/rubeusTrying to tame the three-headed dog.
 gentilkiwi/mimikatz
A little tool to play with Windows security
 the-viper-one/psmapexec
Dominate Active Directory with PowerShell.
 rxwx/chlonium
Clone and import Chromium cookies and passwords across browsers with offline DPAPI state key decryption, supporting AES-256 GCM encrypted databases…
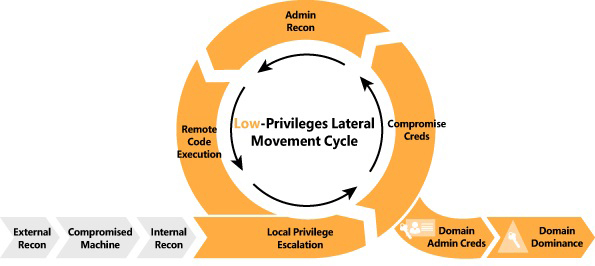 ihebski/a-red-teamer-diaries
RedTeam/Pentest notes and experiments tested on several infrastructures related to professional engagements.
 skelsec/pypykatz
Mimikatz implementation in pure Python
 netwrix/pingcastle
Active Directory security risk assessment tool that evaluates vulnerabilities, misconfigurations, and maturity using a streamlined methodology,…
 ghostpack/sharpdpapi
SharpDPAPI is a C# port of some Mimikatz DPAPI functionality.
 ricardojoserf/trickdump
Dump lsass using only NTAPI functions creating 3 JSON and 1 ZIP file... and generate the MiniDump file later!
 nikaiw/vmkatz
Extract Windows credentials directly from VM memory snapshots and virtual disks
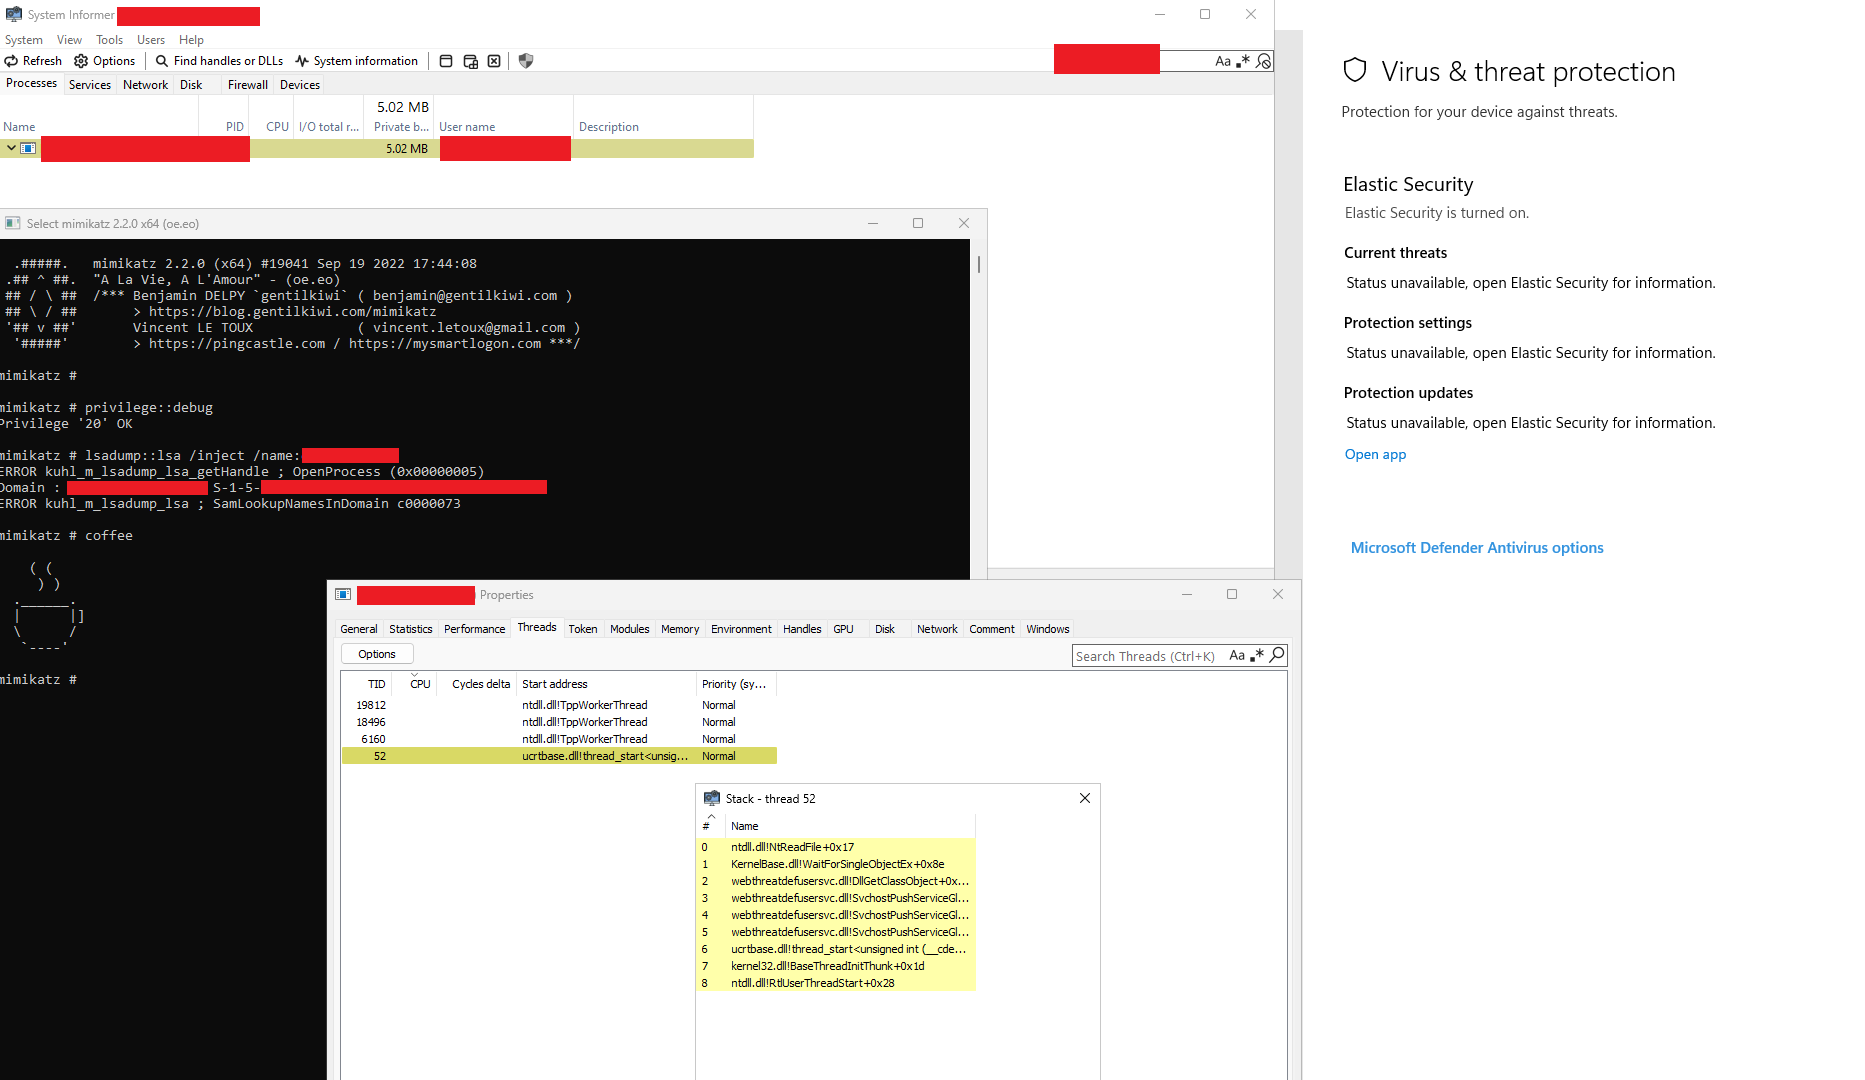 maldev-academy/maldevacademyldr.2
RunPE implementation with multiple evasive techniques (2)
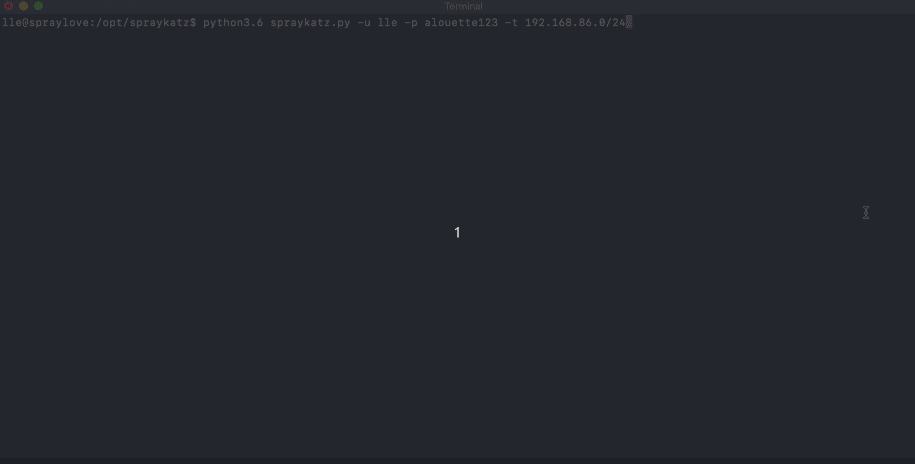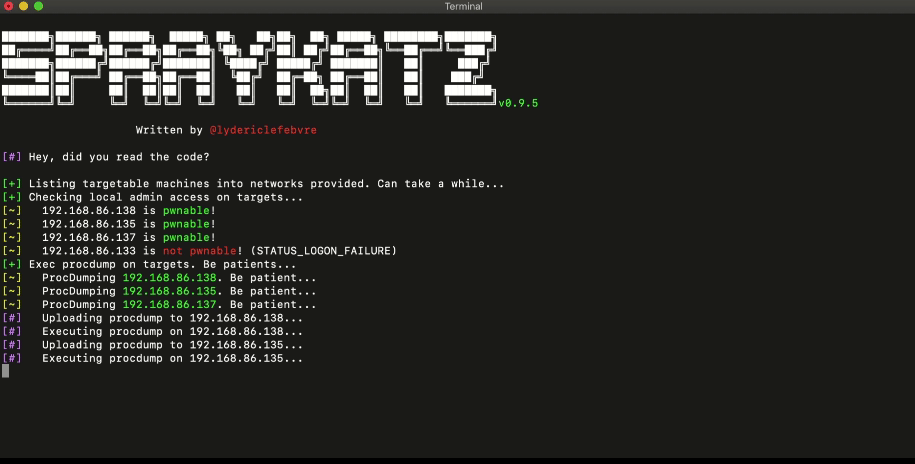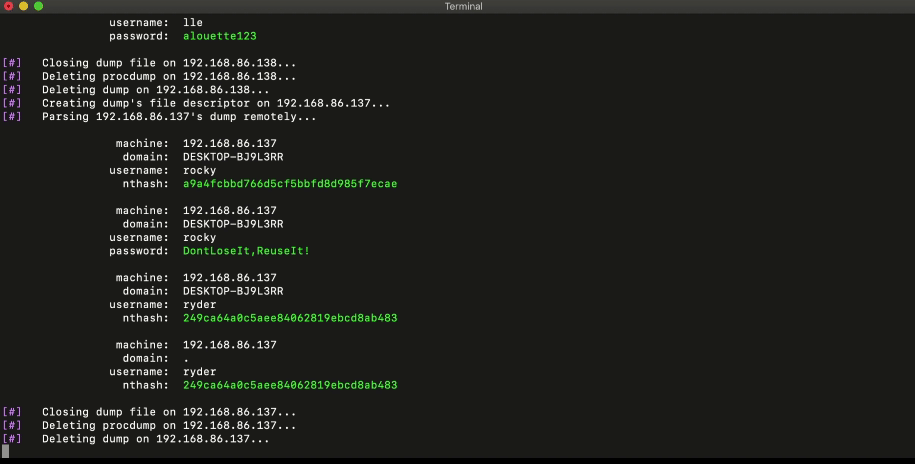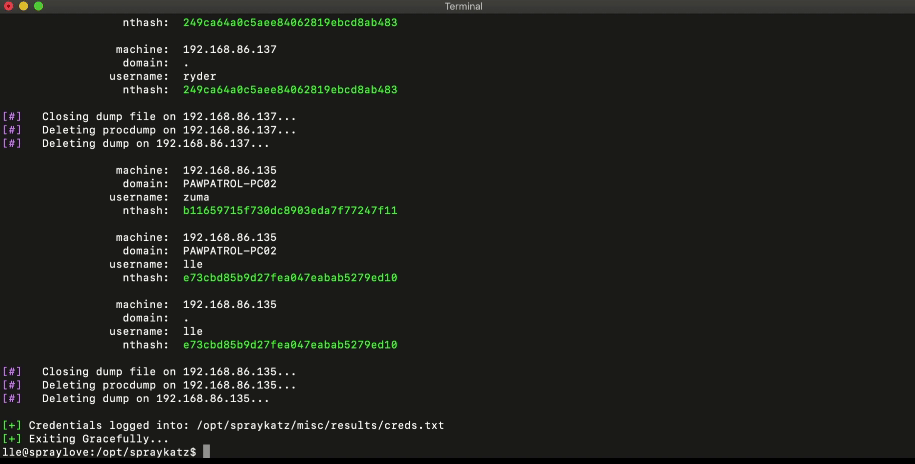 aas-n/spraykatz
Credentials gathering tool automating remote procdump and parse of lsass process.
 zblurx/dploot
Loot and decrypt Windows DPAPI secrets remotely or offline, including masterkeys, credentials, vaults, certificates, browser data, and cached Azure…
 parrotsec/mimikatz
Tool for extracting Windows credentials (passwords, hashes, Kerberos tickets) from memory and performing pass-the-hash, pass-the-ticket, and golden…
 0xdea/blindsight
Red teaming tool to dump LSASS memory, bypassing basic countermeasures.
 anthemtotheego/sharpsploitconsole
C# console application for post-exploitation and red team operations, integrating SharpSploit to execute Mimikatz commands, perform Kerberoasting,…
 sans-blue-team/deepbluecli
PowerShell-based threat hunting tool that analyzes Windows Event Logs to detect malicious activity including credential attacks, obfuscated commands,…
 lintstar/lstar
LSTAR - CobaltStrike 综合后渗透插件