
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
29 results
Internal-Monologue preview

Internal-Monologue

GitHubeladshamir/internal-monologue

Internal Monologue Attack: Retrieving NTLM Hashes without Touching LSASS

lateral-movementpassword-attackspenetration-testing+2
1.7k
8 years ago
mimikatz preview

mimikatz

GitHubgentilkiwi/mimikatz

A little tool to play with Windows security
authenticationexploitationexploit-frameworks+10
21.9k6 months ago
mimikatz preview

mimikatz

GitHubparrotsec/mimikatz

Tool for extracting Windows credentials (passwords, hashes, Kerberos tickets) from memory and performing pass-the-hash, pass-the-ticket, and golden…
authenticationexploitationlateral-movement+5
2.7k6 years ago
Invoke-DCSync preview

Invoke-DCSync

GitHubal1ex/invoke-dcsync

Invoke-DCSync

exploitationlateral-movementpassword-attacks+3
16 years ago
mscache preview

mscache

GitHubqax-a-team/mscache

a tool to manipulate dcc(domain cached credentials) in windows registry, based mainly on the work of mimikatz and impacket
authenticationpassword-crackingpost-exploitation
678 years ago
DeepBlueCLI preview

DeepBlueCLI

GitHubsans-blue-team/deepbluecli

PowerShell-based threat hunting tool that analyzes Windows Event Logs to detect malicious activity including credential attacks, obfuscated commands,…

digital-forensicsincident-responseintrusion-detection+2
2.4k3 years ago
chlonium preview

chlonium

GitHubrxwx/chlonium

Clone and import Chromium cookies and passwords across browsers with offline DPAPI state key decryption, supporting AES-256 GCM encrypted databases…
data-exfiltrationencryption-decryption-toolsforensics+6
3163 years ago
blindsight preview

blindsight

GitHub0xdea/blindsight

Red teaming tool to dump LSASS memory, bypassing basic countermeasures.

ids-ips-evasionpost-exploitationred-teaming
2462 months ago
Rubeus preview

Rubeus

GitHubghostpack/rubeus

Trying to tame the three-headed dog.
authenticationexploitationlateral-movement+6
5.2k11 months ago
SharpSploitConsole preview

SharpSploitConsole

GitHubanthemtotheego/sharpsploitconsole

C# console application for post-exploitation and red team operations, integrating SharpSploit to execute Mimikatz commands, perform Kerberoasting,…
command-and-controlexploitationinformation-gathering+9
1814 years ago
AutoPtT preview

AutoPtT

GitHubricardojoserf/autoptt

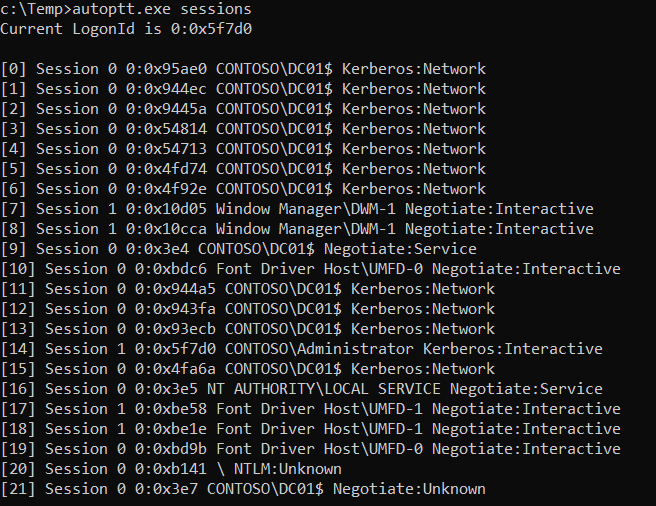
Automated Pass-the-Ticket (PtT) attack. Standalone alternative to Rubeus and Mimikatz for this attack. In C#, C++, Crystal, Python, Rust, Golang, Nim…
authenticationlateral-movementpost-exploitation+1
1571 month ago
ABC preview

ABC

GitHubhzachev/abc

CVE-2017-11882

command-and-controlexploitationpayload-generation+2
8 years ago
spraykatz preview

spraykatz

GitHubaas-n/spraykatz

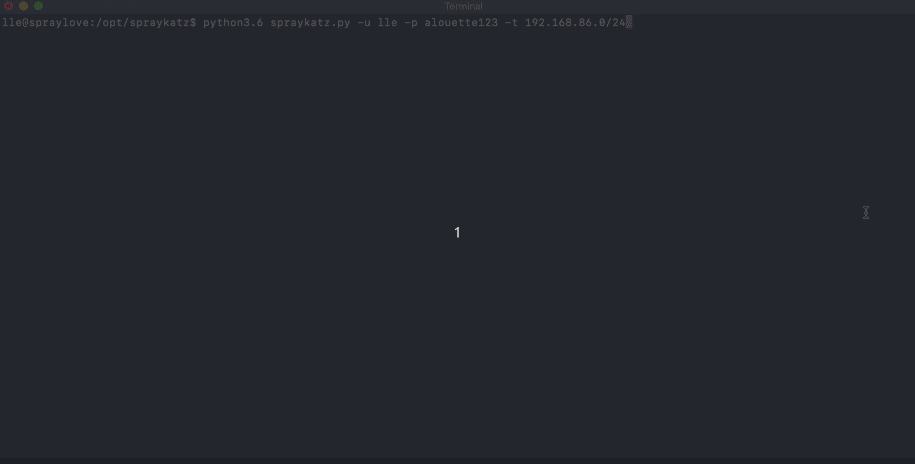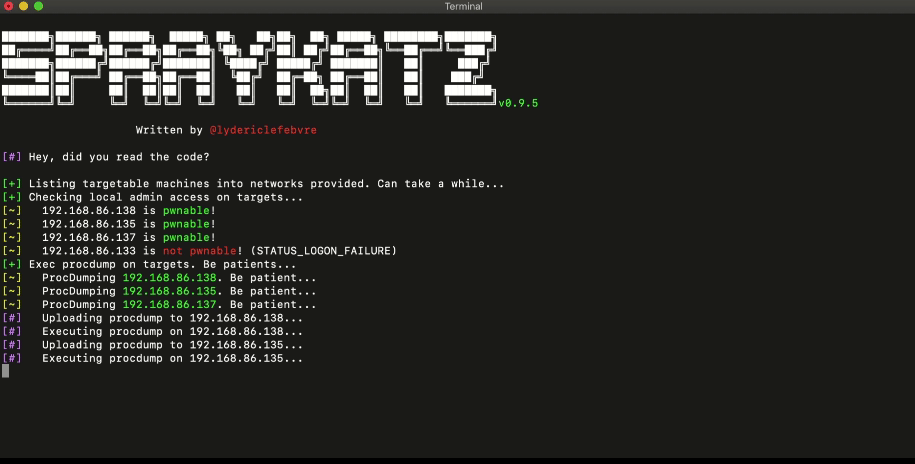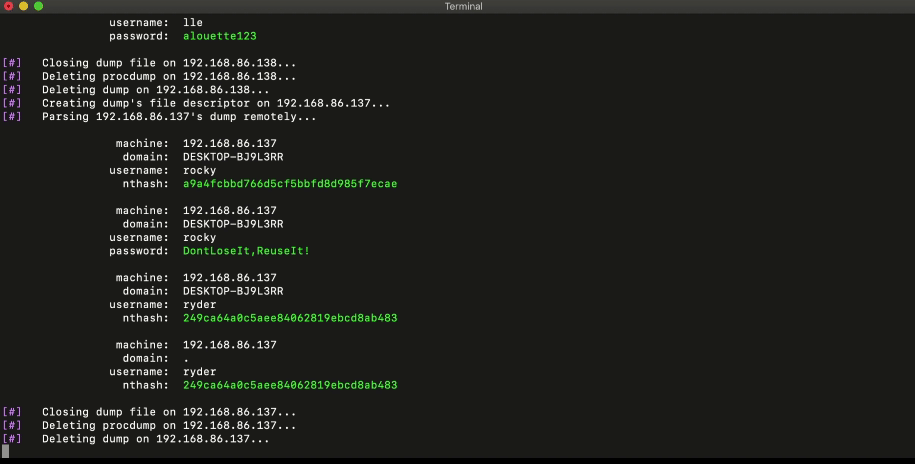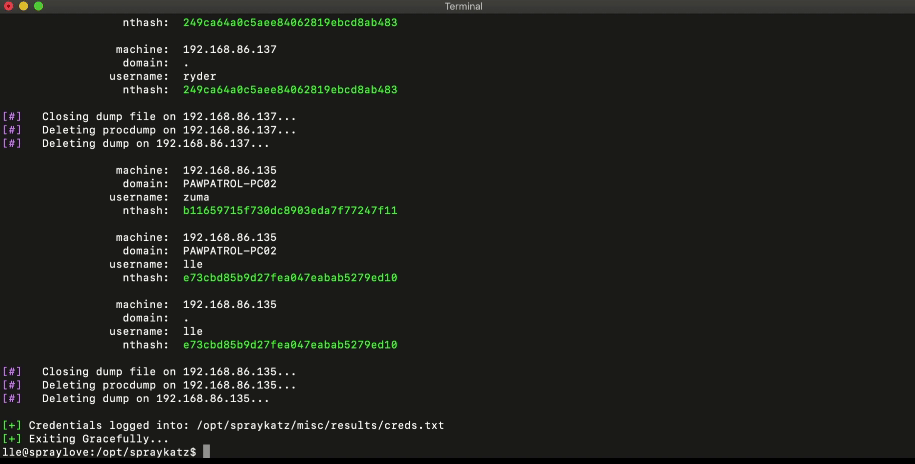
Credentials gathering tool automating remote procdump and parse of lsass process.
information-gatheringlateral-movementpenetration-testing+1
7846 years ago
BypassCredGuard preview

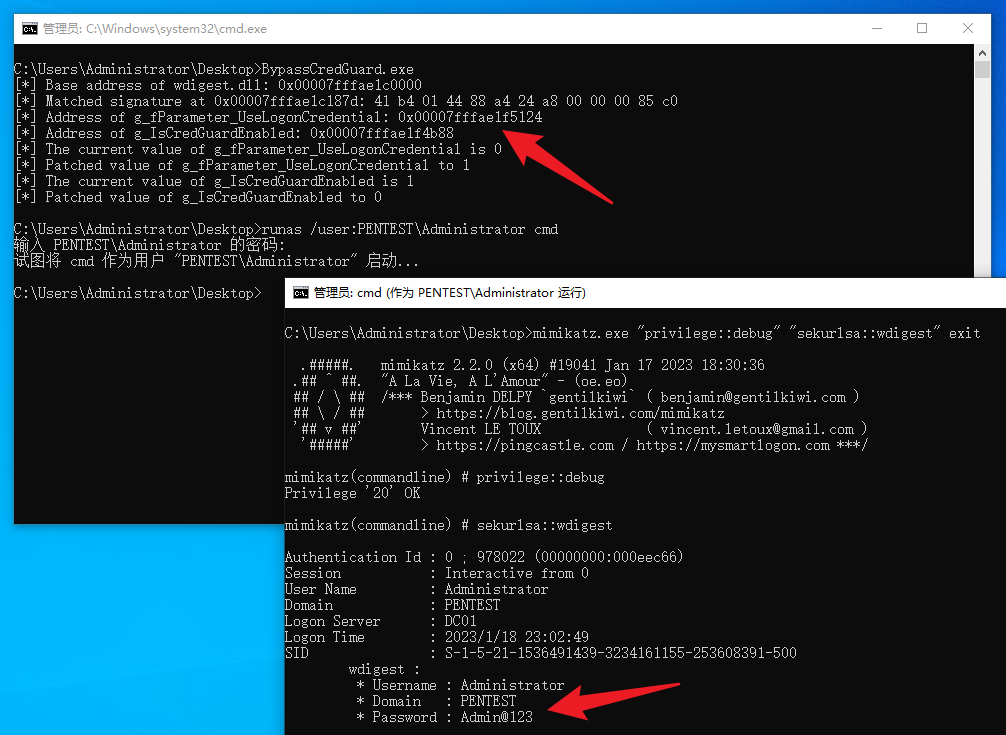
BypassCredGuard

GitHubwh0amitz/bypasscredguard

Credential Guard Bypass Via Patching Wdigest Memory
exploitationpassword-attackspenetration-testing+2
3393 years ago
bypass360mimikatz_x64 preview

bypass360mimikatz_x64

GitHubianxtianxt/bypass360mimikatz_x64

Modified mimikatz binary with resource modification and digital signature to evade 360 Antivirus detection for credential dumping in penetration…
exploitationids-ips-evasionpassword-attacks+3
187 years ago
LsassReflectDumping preview

LsassReflectDumping

GitHuboffensive-panda/lsassreflectdumping

This tool leverages the Process Forking technique using the RtlCreateProcessReflection API to clone the lsass.exe process. Once the clone is created,…
memory-forensicspassword-attackspost-exploitation+1
2182 years ago
pingcastle preview

pingcastle

GitHubnetwrix/pingcastle

Active Directory security risk assessment tool that evaluates vulnerabilities, misconfigurations, and maturity using a streamlined methodology,…

configuration-auditingvulnerability-scanners
3.0k11 days ago
VMkatz preview

VMkatz

GitHubnikaiw/vmkatz

Extract Windows credentials directly from VM memory snapshots and virtual disks

digital-forensicsexploitationforensics+7
1.6k22 days ago
Previous12Next