

Tiredful-API
 payatu/tiredful-api
An intentionally designed broken web application based on REST API.
api-security-testingeducationlabs-practice+2
payatu/tiredful-apiAn intentionally designed broken web application based on REST API.
 owasp/software-component-verification-standard
Software Component Verification Standard (SCVS)
 owasp/maswe
OWASP enumeration of common security and privacy weaknesses in mobile applications, serving as a reference bridging the MASVS verification standard…
 omar2535/graphqler
☸The first ever dependency-aware GraphQL API testing tool!
 owasp/railsgoat
A vulnerable version of Rails that follows the OWASP Top 10
 ethicalhackingplayground/tproxer
A Burp Suite extension made to automate the process of finding reverse proxy path based SSRF.
 santandersecurityresearch/corsair_scan
Automated CORS misconfiguration scanner that tests Origin header injection, wildcard reflection, and credential leakage across web applications and…
 secsys-fdu/cve-2025-51867
Demonstrates an Insecure Direct Object Reference (IDOR) vulnerability in Deepfiction AI's chat API, allowing attackers to consume other users'…
 mirfansulaiman/customheader
This Burp Suite extension allows you to customize header with put a new header into HTTP REQUEST BurpSuite (Scanner, Intruder, Repeater, Proxy…
 owasp/honeypot-project
Deploy web honeypots to capture emerging attack data, analyze ModSecurity audit logs via ELK, and share threat intelligence with MISP for…
 intelligencex/sdk
SDK for querying the Intelligence X search engine and data archive, supporting selectors like email, domain, IP, and phone. Includes API wrappers in…
 moopinger/smugglefuzz
A rapid HTTP downgrade smuggling scanner written in Go.
 dipjyotimetia/hybridtestframework
End to End testing of Web, API, Cloud, Events and Security
 owasp/wwwgrep
OWASP Foundation Web Respository
 syscallx-18113/apkx-hunter
C-based Android static analysis framework for decompilation, secret detection, endpoint discovery, permission analysis, and native library scanning…
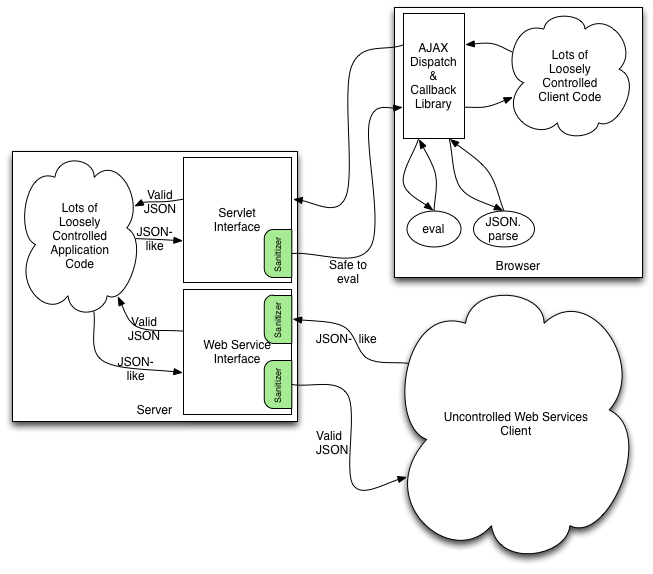 owasp/json-sanitizer
Given JSON-like content, The JSON Sanitizer converts it to valid JSON.
 owasp/donkai
DonkAI is a hands-on lab for the OWASP Top 10 for LLM Applications (2025) - no real LLM required.
 debajyoti0-0/cve-2026-60206
Technical analysis and Proof-of-Concept for CVE-2026-60206, a critical Oracle WebLogic Server SAML authentication bypass vulnerability.