
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

··Feeds·Contact·Privacy·© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
177 results
CVE-2021-26700 preview

CVE-2021-26700

GitHubjackadamson/cve-2021-26700

Proof-of-concept for CVE-2021-26700: remote code execution in the VSCode npm-script extension via malicious workspace settings.json, with detailed…

code-analysiseducationexploitation+3
20
5 years ago
vscode-frida preview

vscode-frida

GitHubchichou/vscode-frida

Unofficial frida extension for VSCode
android-securitybinary-analysisdebuggers+5
5942 months ago
SAMLRaider preview

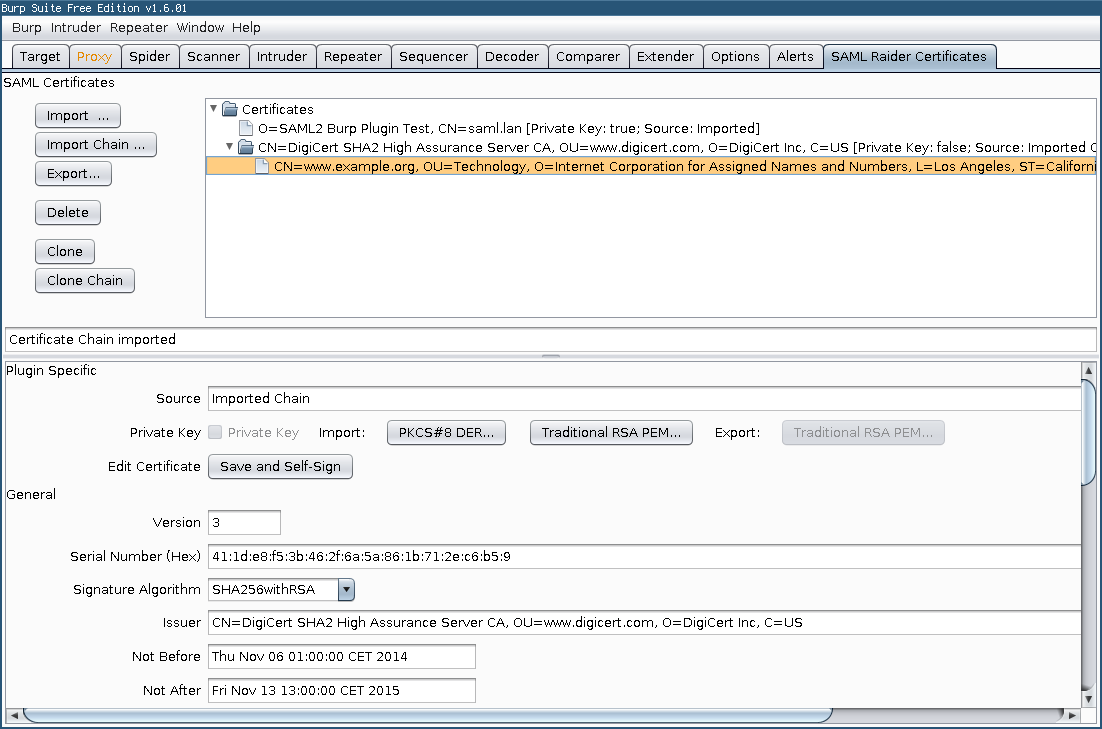
SAMLRaider

GitHublindi2/samlraider

SAML2 Burp Extension

authenticationcryptographyidentity-access-management+4
37 years ago
Next.js-RSC-RCE-Scanner-Burp-Suite-Extension preview

Next.js-RSC-RCE-Scanner-Burp-Suite-Extension

GitHubtobiasguta/next.js-rsc-rce-scanner-burp-suite-extension

Burp Suite extension to detect the Next.js / React Server Components (RSC) Remote Code Execution vulnerability (CVE-2025-55182 & CVE-2025-66478).
dynamic-analysis-sandboxingexploitationpenetration-testing+3
239 months ago
e-is-for-exploit-cve-2026-17543-php-pgsql-sql-injection-backslash-breakout preview

e-is-for-exploit-cve-2026-17543-php-pgsql-sql-injection-backslash-breakout

GitHubhunt-benito/e-is-for-exploit-cve-2026-17543-php-pgsql-sql-injection-backslash-breakout

PoC exploit for CVE-2026-17543: SQL injection in PHP ext/pgsql via backslash breakout, with data exfiltration and admin privilege-escalation payloads…

database-securityeducationexploitation+4
11 month ago
BurpBounty preview

BurpBounty

GitHubwagiro/burpbounty

Burp Bounty (Scan Check Builder in BApp Store) is a extension of Burp Suite that allows you, in a quick and simple way, to improve the active and…
penetration-testingvulnerability-scannersweb-security
1.8k3 years ago
turbo-intruder preview

turbo-intruder

GitHubportswigger/turbo-intruder

High-speed Burp Suite extension for sending large volumes of HTTP requests with a custom stack, Python-based attack configuration, and advanced…
fuzzingpenetration-testingvulnerability-analysis+1
1.8k2 days ago
Autorize preview

Autorize

GitHubquitten/autorize

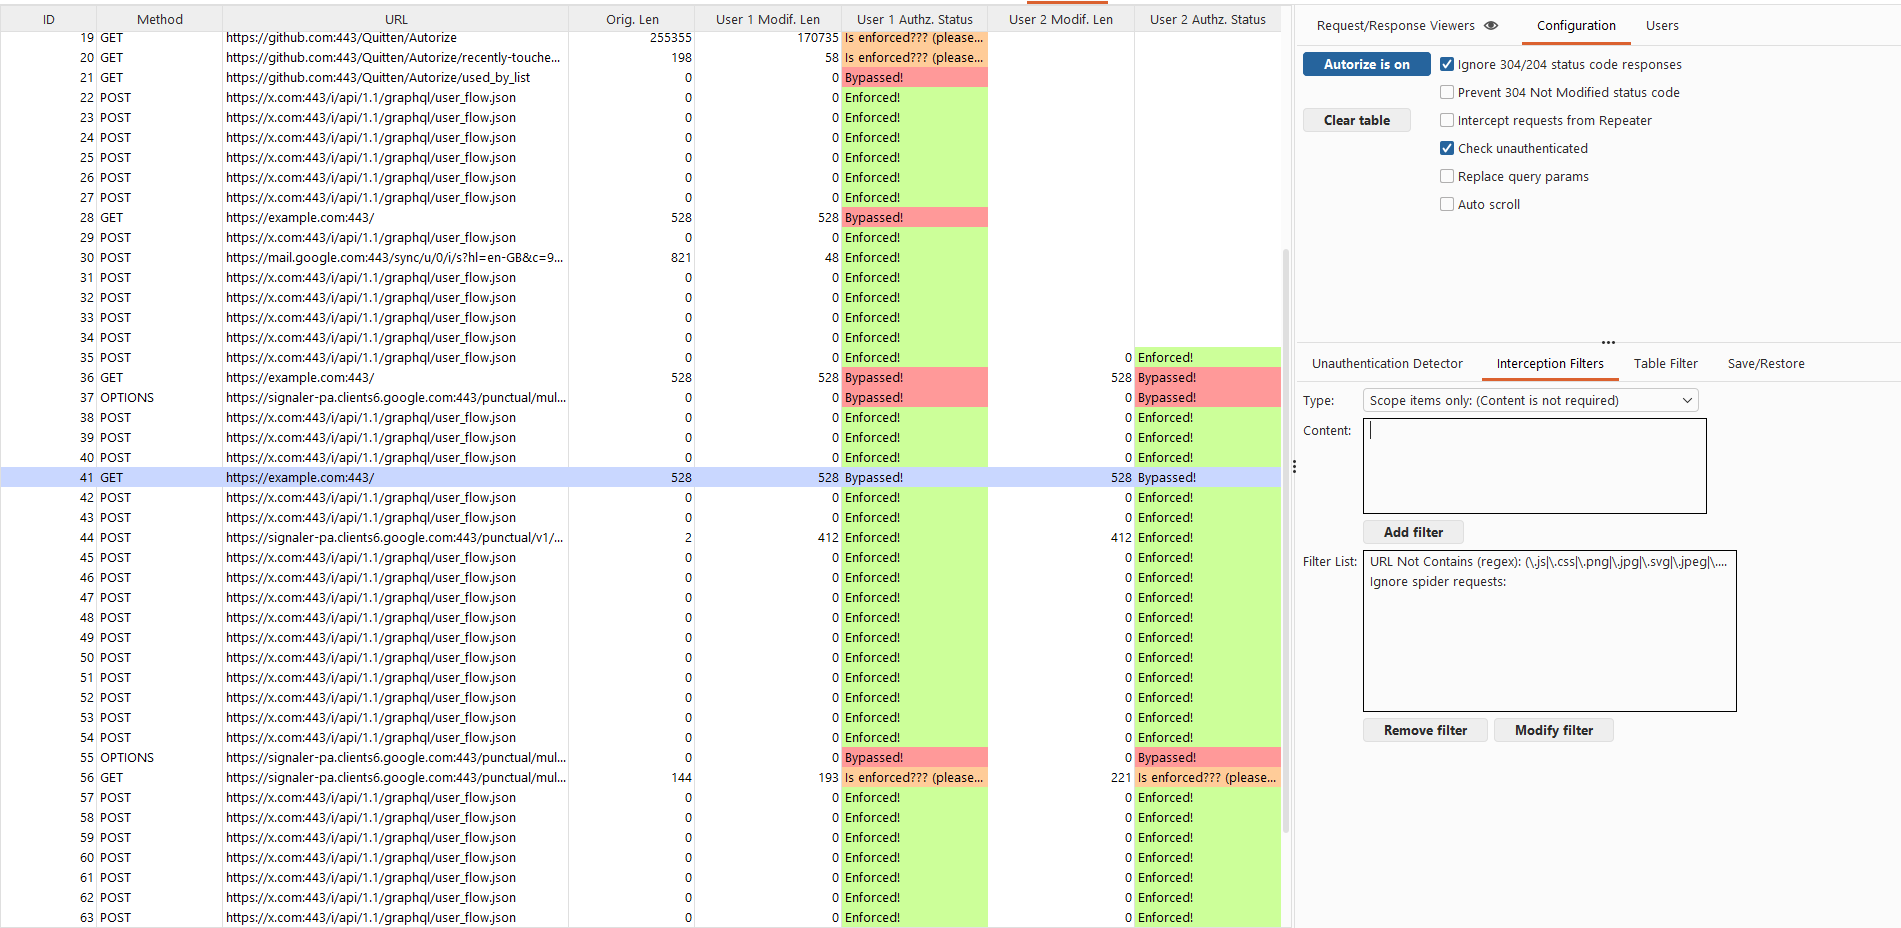
Automatic authorization enforcement detection extension for burp suite written in Jython developed by Barak Tawily in order to ease application…
api-security-testingauthentication-authorizationpenetration-testing+2
1.2k6 months ago
JS-Tap preview

JS-Tap

GitHubhoodoer/js-tap

JavaScript beacons and C2 to be used for XSS payload or post exploitation implants on webapp servers or desktop software to monitor users and…
command-and-controldata-exfiltrationinformation-gathering+8
4772 months ago
burp-vps-proxy preview

burp-vps-proxy

GitHubd3mondev/burp-vps-proxy

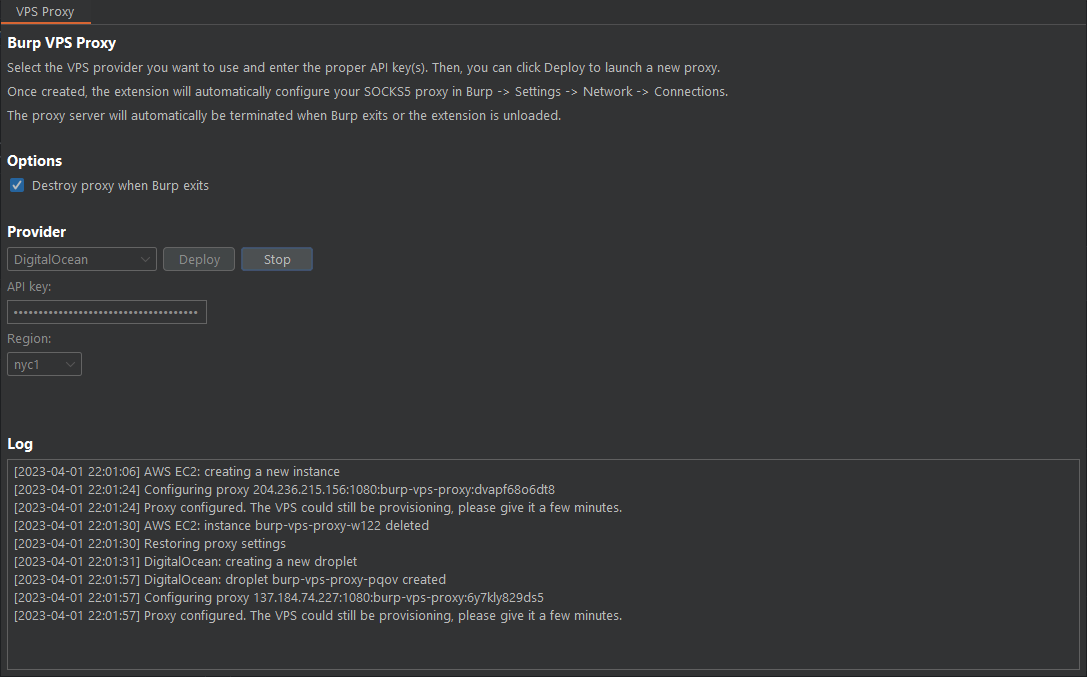
This Burp Suite extension allows for the automatic creation and deletion of an upstream SOCKS5 proxy on popular cloud services.

penetration-testingutilities-frameworkswaf-bypass+1
2491 year ago
OAUTHScan preview

OAUTHScan

GitHubakabe1/oauthscan

Burp Suite Extension useful to verify OAUTHv2 and OpenID security

api-securityapi-security-testingauthentication-authorization+6
1801 year ago
jsluicepp preview

jsluicepp

GitHub0x999-x/jsluicepp

jsluice++ is a Burp Suite extension designed for passive and active scanning of JavaScript traffic using the CLI tool jsluice
api-security-testinginformation-gatheringreconnaissance+3
3052 years ago
oauth-scan preview

oauth-scan

GitHubportswigger/oauth-scan

Burp Suite Extension useful to verify OAUTHv2 and OpenID security

authentication-authorizationconfiguration-auditinginformation-gathering+3
1921 year ago
reburp preview

reburp

GitHubforefy/reburp

A Burp Suite extension that exposes the full Montoya API as a local REST API, with Swagger UI

ai-securityapi-security-testingfuzzing+7
1033 days ago
CVE-2019-11358 preview

CVE-2019-11358

GitHubisacaya/cve-2019-11358

Proof-of-concept exploit for CVE-2019-11358, a prototype pollution vulnerability in jQuery's extend method (versions <3.4.0). Demonstrates the attack…

code-analysisexploitationvulnerability-analysis+2
13 years ago
CVE-2026-66492 preview

CVE-2026-66492

GitHubtoanln-cov/cve-2026-66492

The Joomla extension PhocaCommander is vulnerable to Path Traversal in the file upload action - CVSS 6.1

exploitationpenetration-testingvulnerability-analysis+2
1 month ago
HaE preview

HaE

GitHuboverspace-labs/hae

Modular Burp Suite extension for fine-grained highlighting and extraction of sensitive data from HTTP and WebSocket traffic, enabling efficient…
information-gatheringutilities-frameworksweb-security
4.4k5 days ago
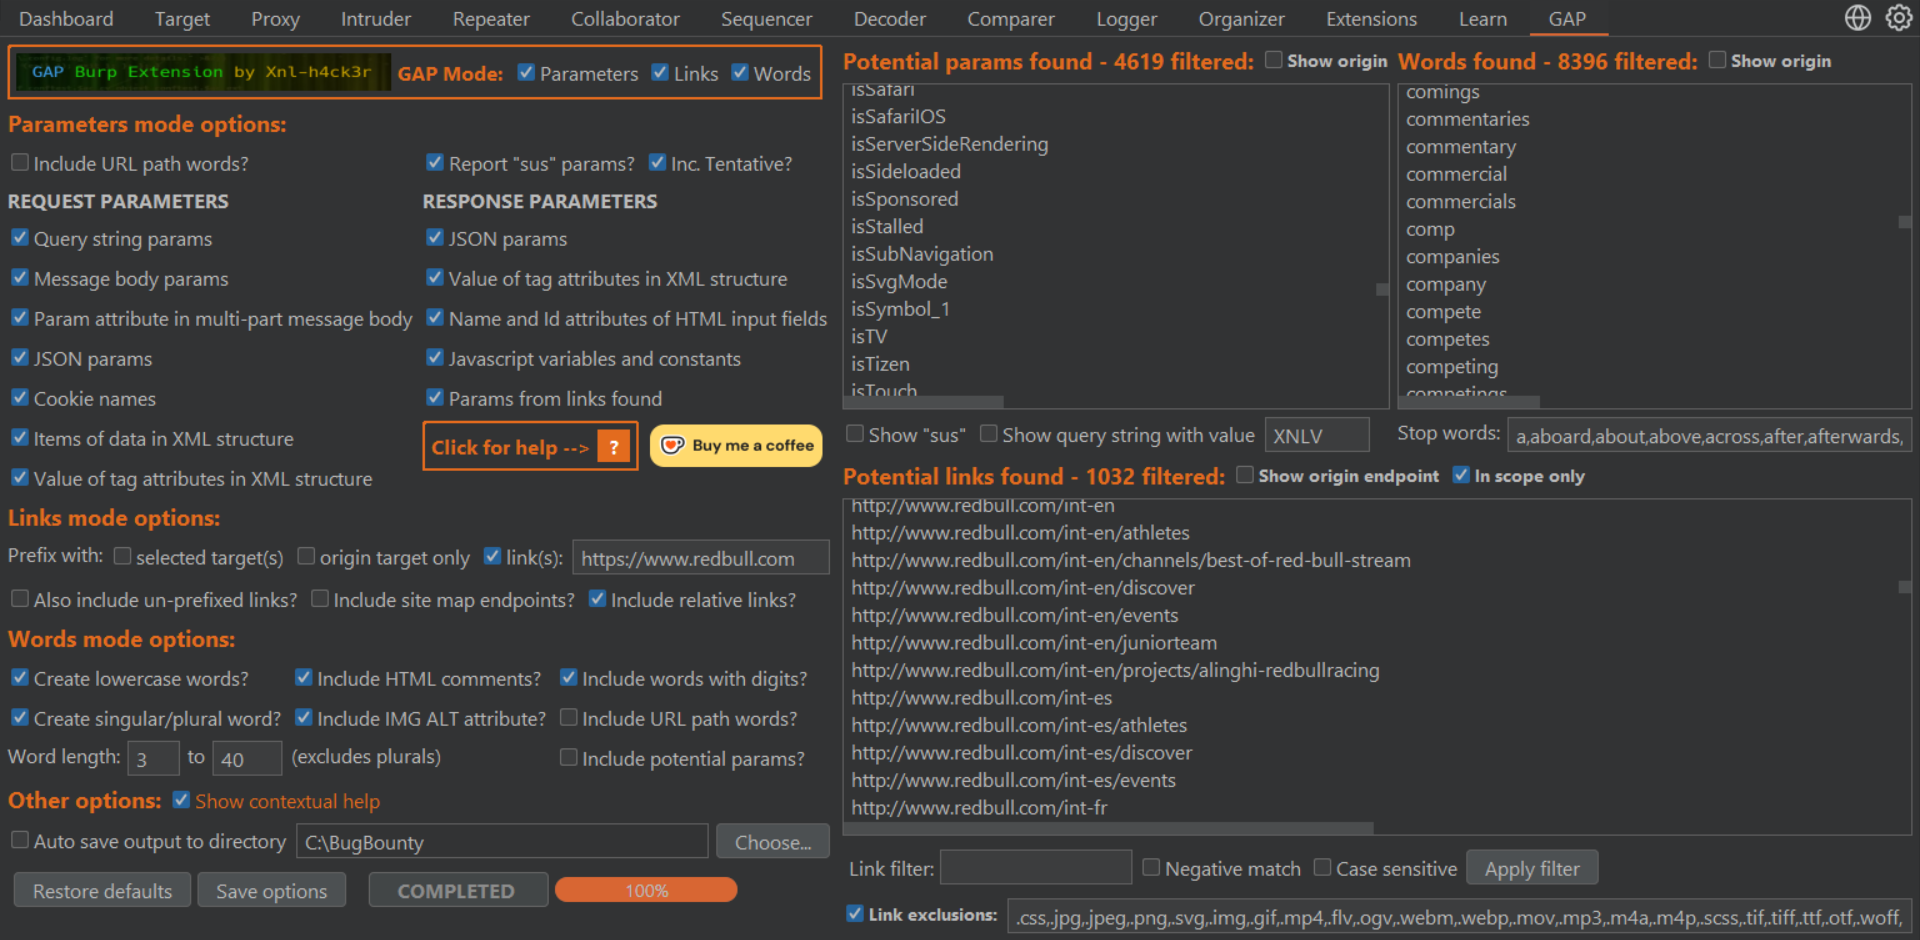
GAP-Burp-Extension preview

GAP-Burp-Extension

GitHubxnl-h4ck3r/gap-burp-extension

Burp Extension to find potential endpoints, parameters, and generate a custom target wordlist

fuzzinginformation-gatheringpenetration-testing+3
1.5k8 months ago
Previous1234…10Next