
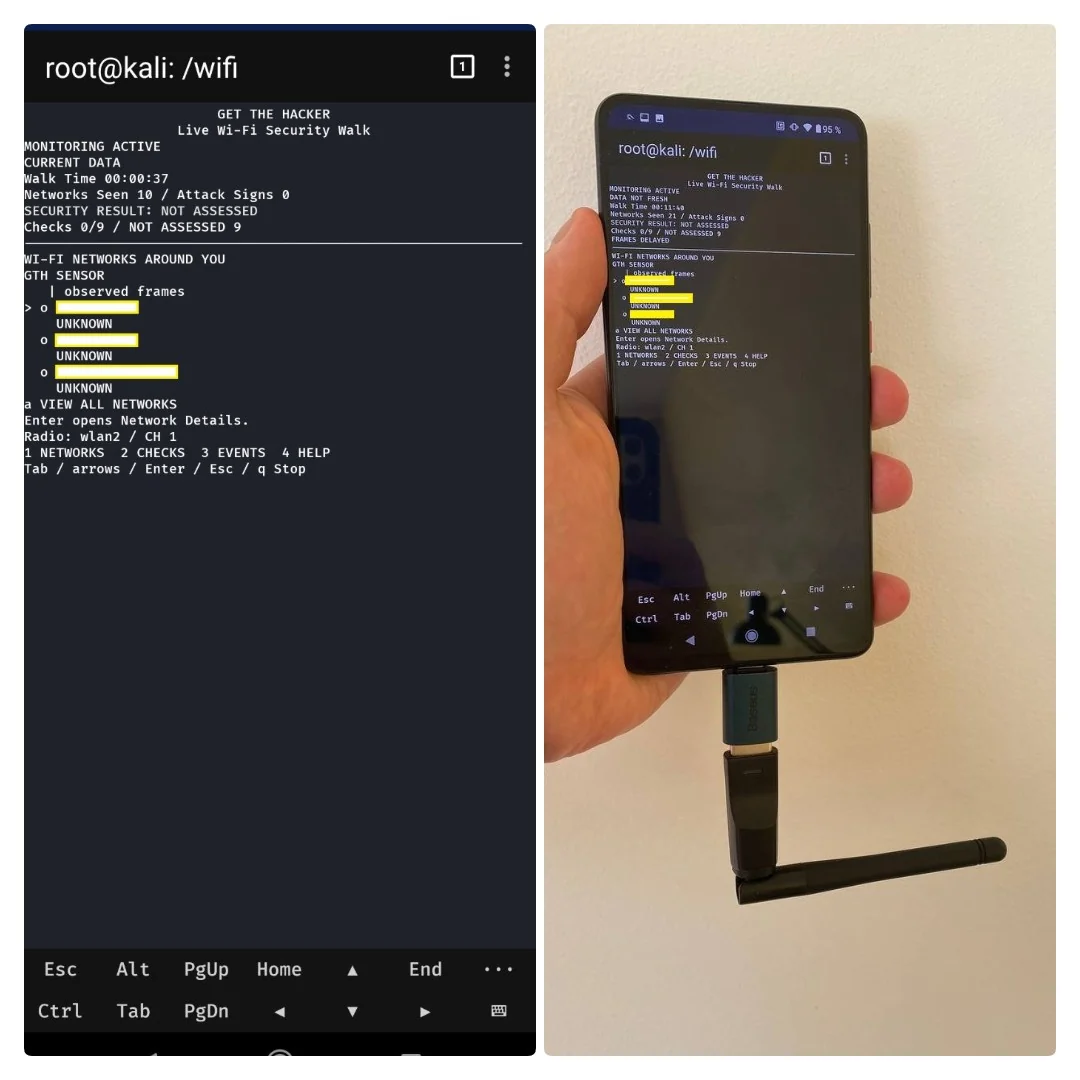
get-the-hacker
 buybitart/get-the-hacker
Hunt WiFi threats silently. Catch the hackers.
defensive-toolsincident-responseintrusion-detection+5
buybitart/get-the-hackerHunt WiFi threats silently. Catch the hackers.

 yashubitra/evil_twin_attack
Rogue access point attack and defense on Kali Linux: deauth with aireplay-ng, an airbase-ng evil twin with a captive portal, plus real-time…
 rianhanft/marauderbox
A fork of the marauder firmware with Nyan box capabilities
 phantom-brigade1/wifisting
GTK4 and CLI wireless security toolkit with 57 standalone modules for Wi-Fi, Bluetooth, 802.15.4, SDR/RF, NFC and router-side or network MITM testing…
 qkaiser/broadcom-wps
Tools to fingerprint WiFi Access Points running the Broadcom SDK and a list of known affected devices.
 buybitart/cyclepatrol
Bash tool for on-foot Wi-Fi security checks in a loop, with evidence reports. (re-invented wifi WarDriving)
 vanhoefm/krackattacks-scripts
Scripts to verify WPA2 clients and APs for KRACK key reinstallation vulnerabilities using modified hostapd and monitor-mode frame replay.
 vanhoefm/fragattacks
Automated vulnerability tester for Wi-Fi clients and access points, detecting FragAttacks fragmentation/aggregation flaws through frame injection,…
 ghostesp-revival/ghostesp
The open-source wireless research platform for ESP32.
 neternels/android_kernel_xiaomi_sunny
CAFest nethunter kernel based on LA.UM.9.1.r1-11900-SMXXX0.0 with latest upstream-f2fs-stable-linux-4.14.y merged, bb and perf focused. | Force push…
 seemoo-lab/nexmon
The C-based Firmware Patching Framework for Broadcom/Cypress WiFi Chips that enables Monitor Mode, Frame Injection and much more
 loukious/android_kernel_xiaomi_sm8150
Nethunter kernel for the POCO X3 Pro (vayu) based on crDroid's kernel.
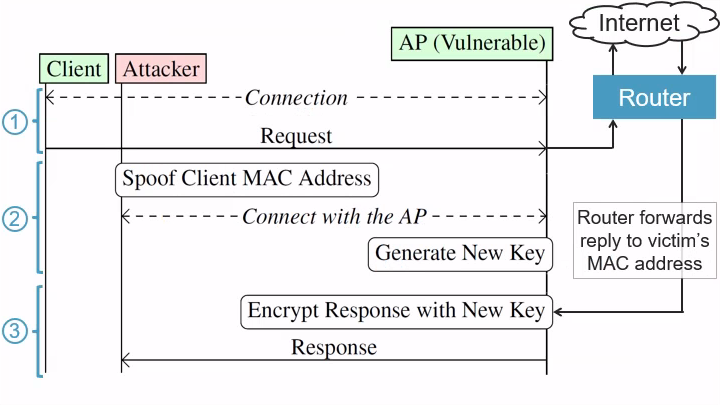 vanhoefm/macstealer
MacStealer: Wi-Fi Client Isolation Bypass
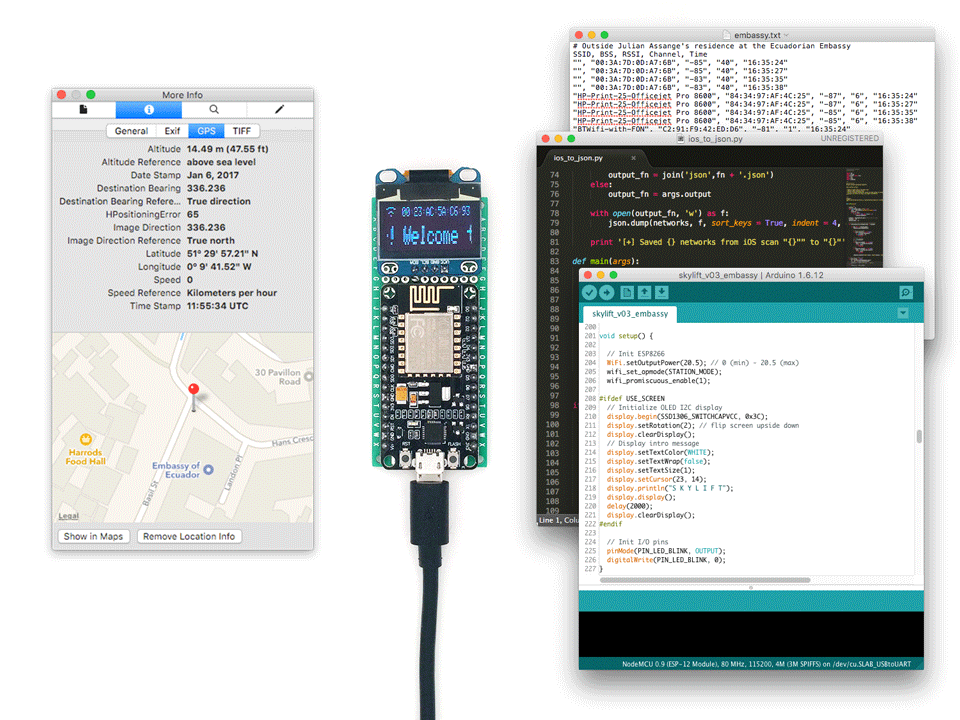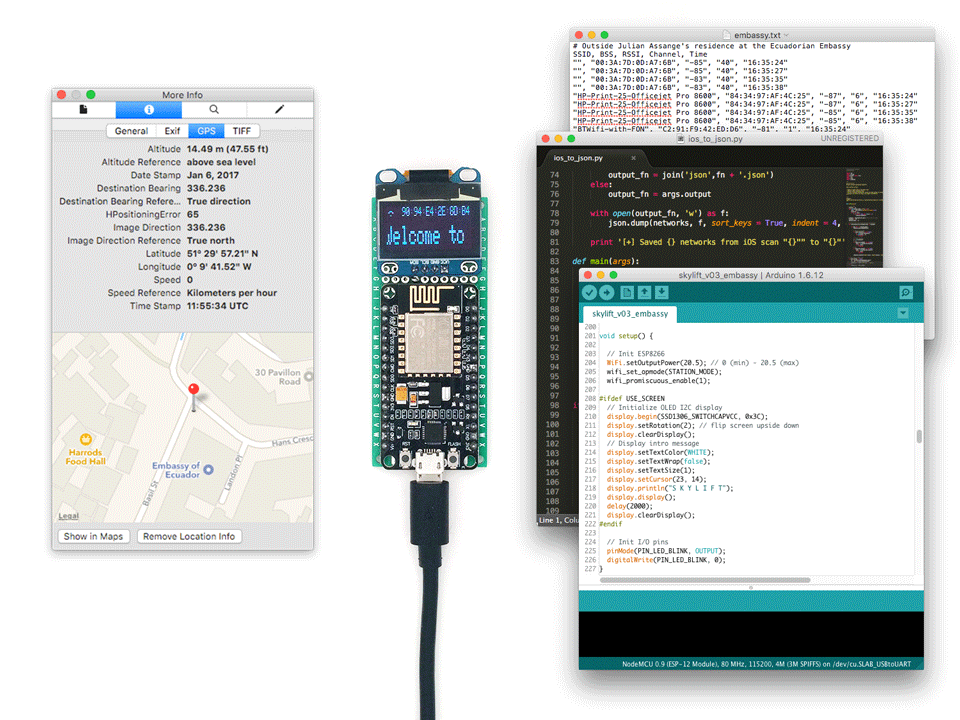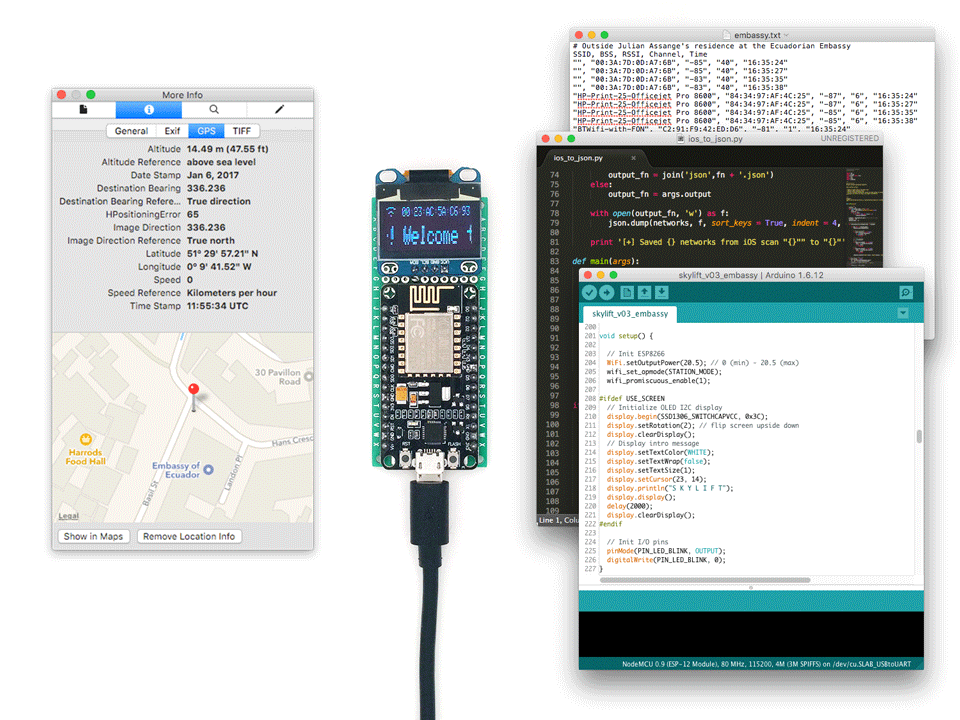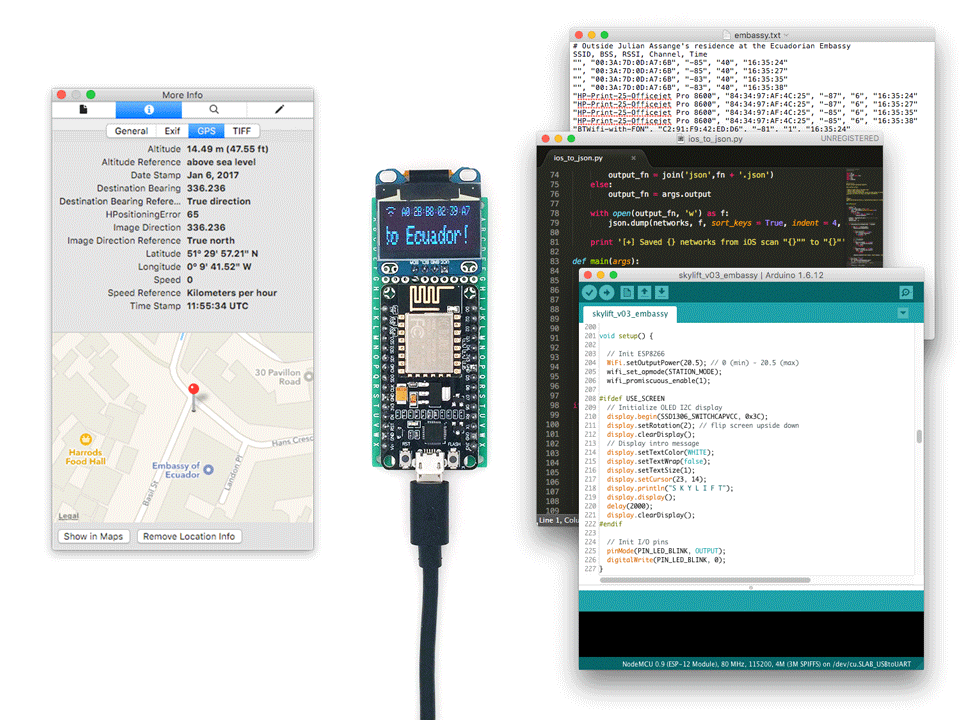 awesome-pentest-gadgets/skylift
WiFi Geolocation Spoofing with the ESP8266
 scramblr/rf-chaos
RF CHAOS is an Android App That Is Designed To Cause Chaos via All RF Adapters Possible - Enjoy!
 i-am-shodan/usbarmyknife
USB Army Knife – the ultimate close access tool for penetration testers and red teamers.
 satheesh575555/external_wpa_supplicant_8_aosp10_r33_cve-2021-0516
Proof-of-concept exploit for CVE-2021-0516 in wpa_supplicant on AOSP 10, demonstrating a buffer overflow vulnerability in Wi-Fi authentication.
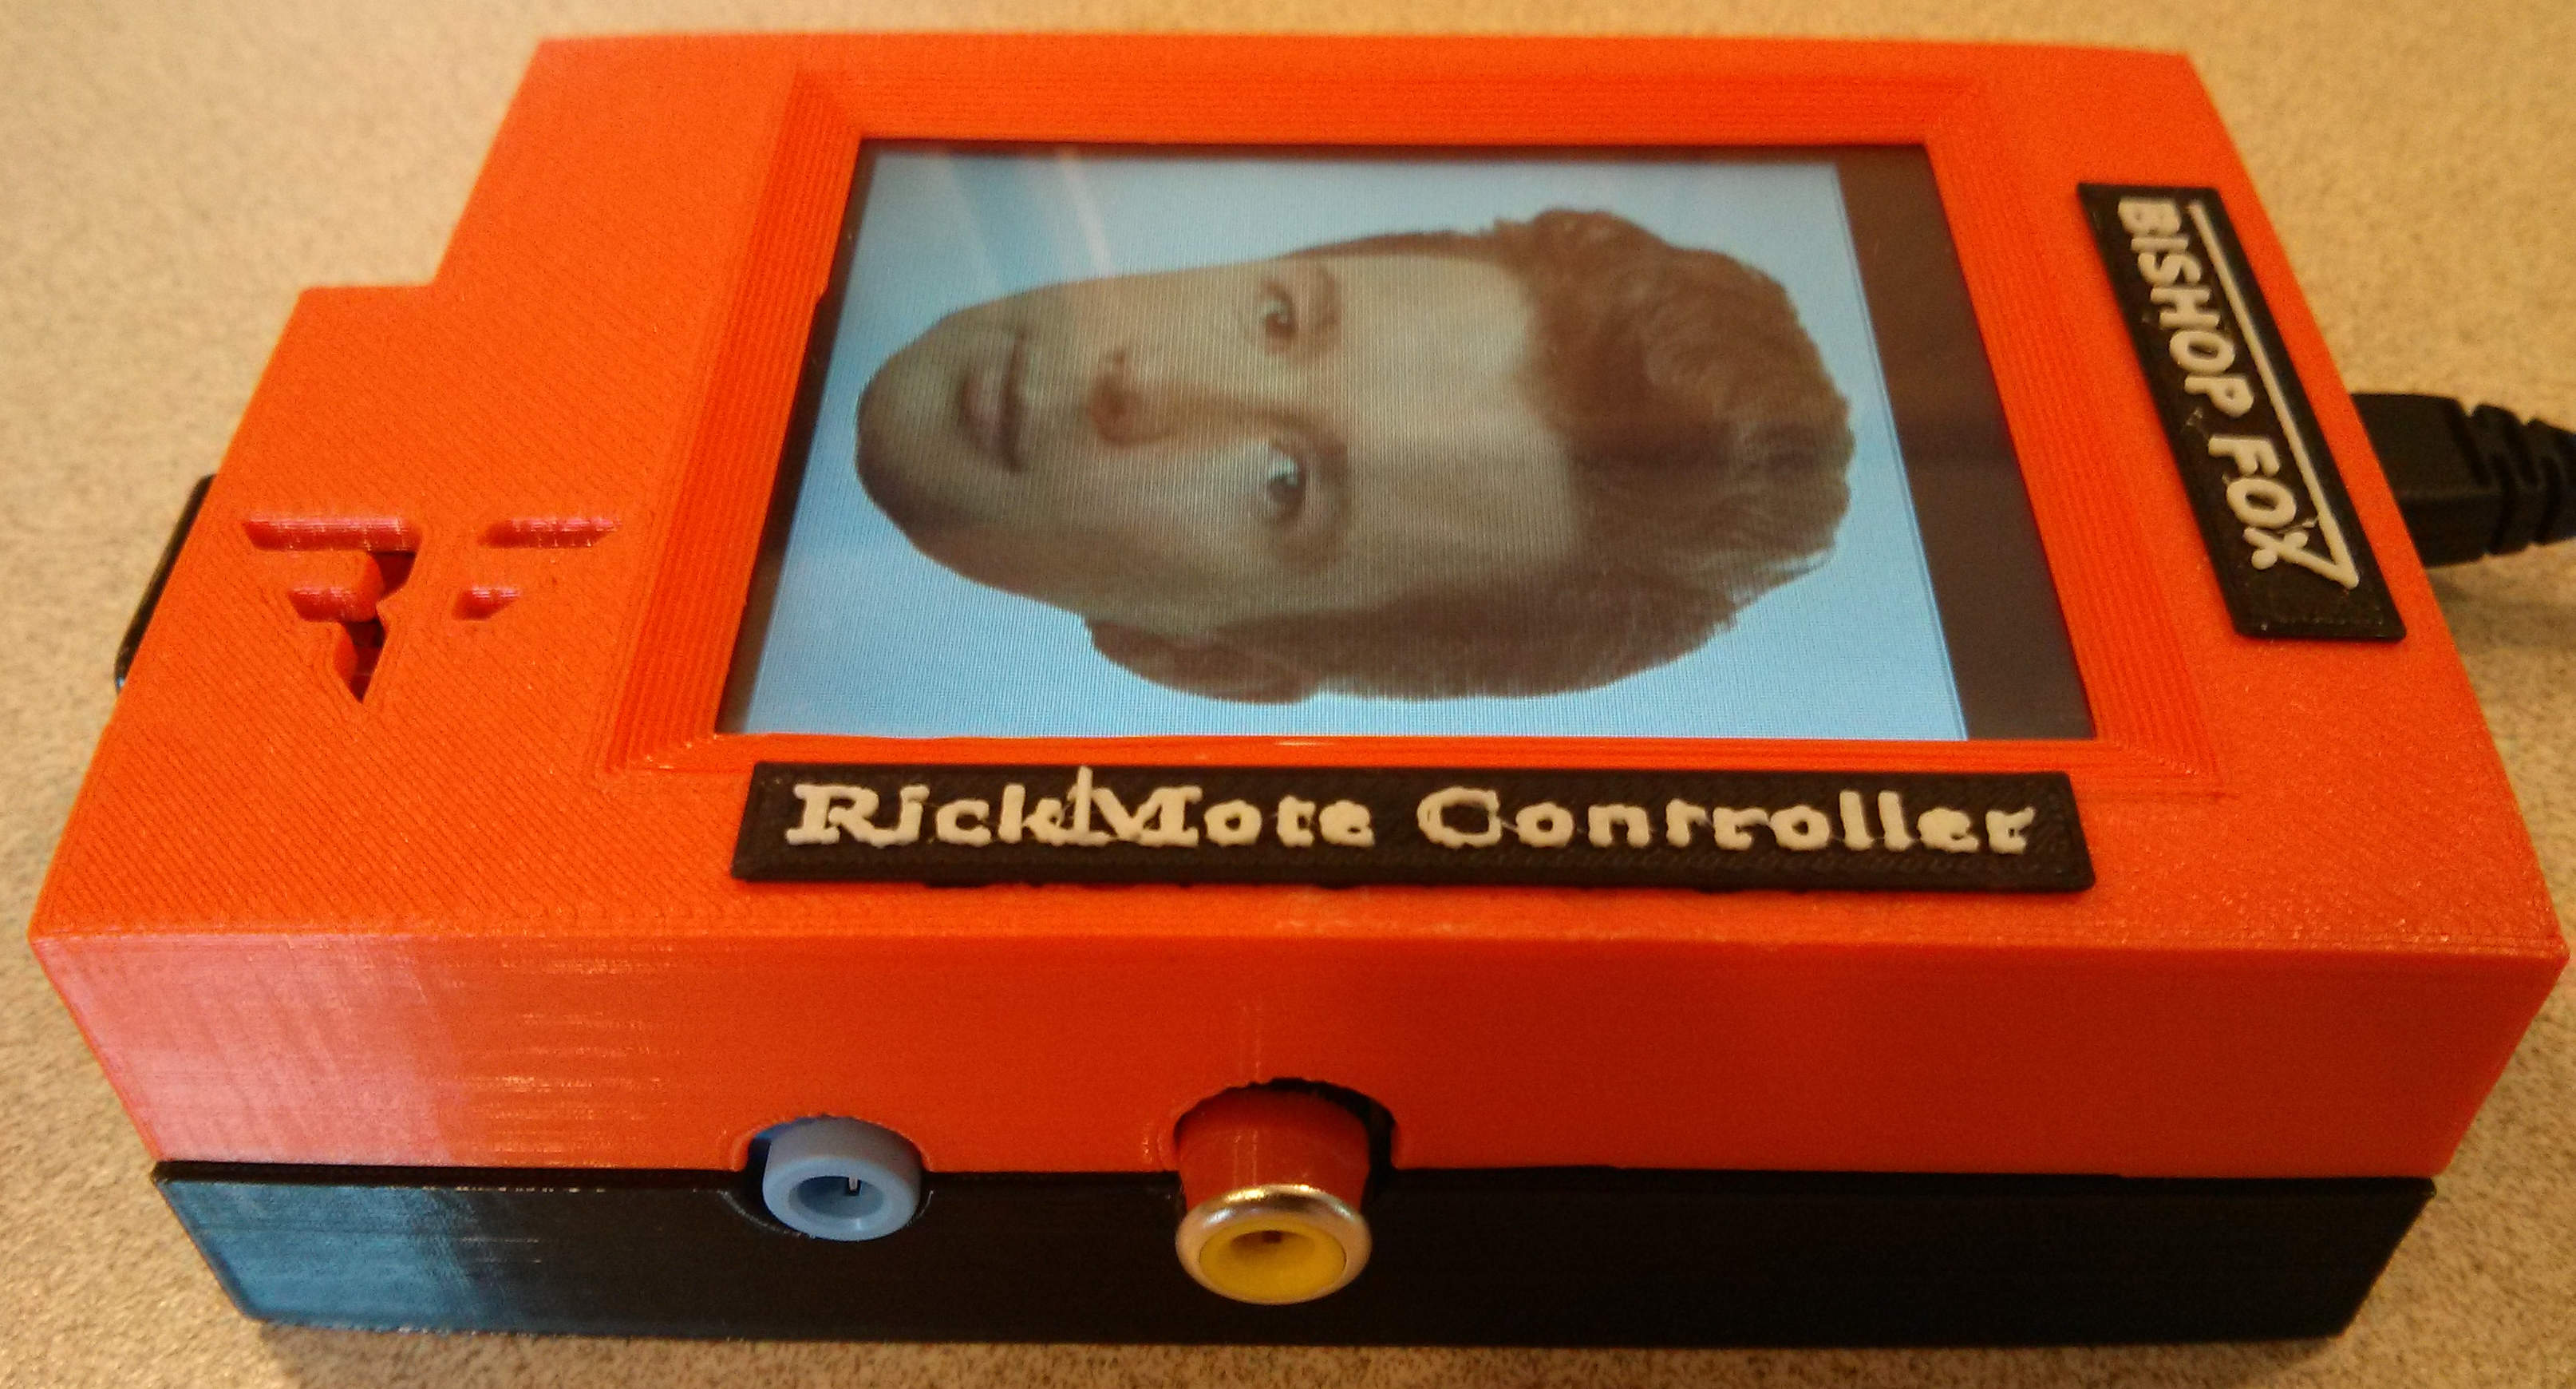 bishopfox/rickmote
The Rickmote Controller: Hijack TVs using Google Chromecast