

CVE-2026-114509
 nxploited/cve-2026-114509
Laravel TokenGuard authentication bypass through non-string API credentials
authenticationexploitationinformation-gathering+6
nxploited/cve-2026-114509Laravel TokenGuard authentication bypass through non-string API credentials
 kostas-pa/lfitester
Python3 tool that detects and exploits Local File Inclusion vulnerabilities, with crawling, path traversal and filter bypass payloads, and automated…
 hevnsnt/cvengine
AI-first external attack surface assessment with continuous discovery, evidence-based vulnerability validation, and developer-agent MCP integration.
 assetnote/node2shell-scanner
High fidelity detection mechanism for node2shell (CVE-2026-111497)
 affolter-engineering/hvt
Rust CLI that probes HTTP methods (including WebDAV and DeltaV verbs) against a target URL to surface verb tampering, access-control bypasses, and…
 d0rb/shellscope
Defensive exposure auditor for Plex2Shell and php2shell — find your own before they find you.
 yehia-mamdouh/xssya-v-2.0
Python XSS scanner that confirms reflected and encoded-payload injection, executes payloads to capture cookies, detects WAFs, and tests XST with a…
 assetnote/php2shell-scanner
High fidelity scanner for php2shell (CVE-2026-109618 and CVE-2026-109619)
 openai/php2shell-checker
CLI that checks a website's PHP version or a local PHP binary against embedded patch cutoffs to determine php2shell vulnerability status, with JSON…
 oscerd/cve-2026-85315
Runnable proof-of-concept reproducer for CVE-2026-85315, demonstrating camel-grpc consumer exception message disclosure (CWE-209) in Camel Spring…
 joasasantos/php2shell-scanner
Non-destructive scanner for CVE-2026-109618 / CVE-2026-109619 (PHP core RCE). Subdomain recon via crt.sh + subfinder, robust banner grabbing,…
 4rdr/proofs
Collection of CVE findings, proof-of-concept references, and vulnerability research notes, including ExploitDB entries and credited security…
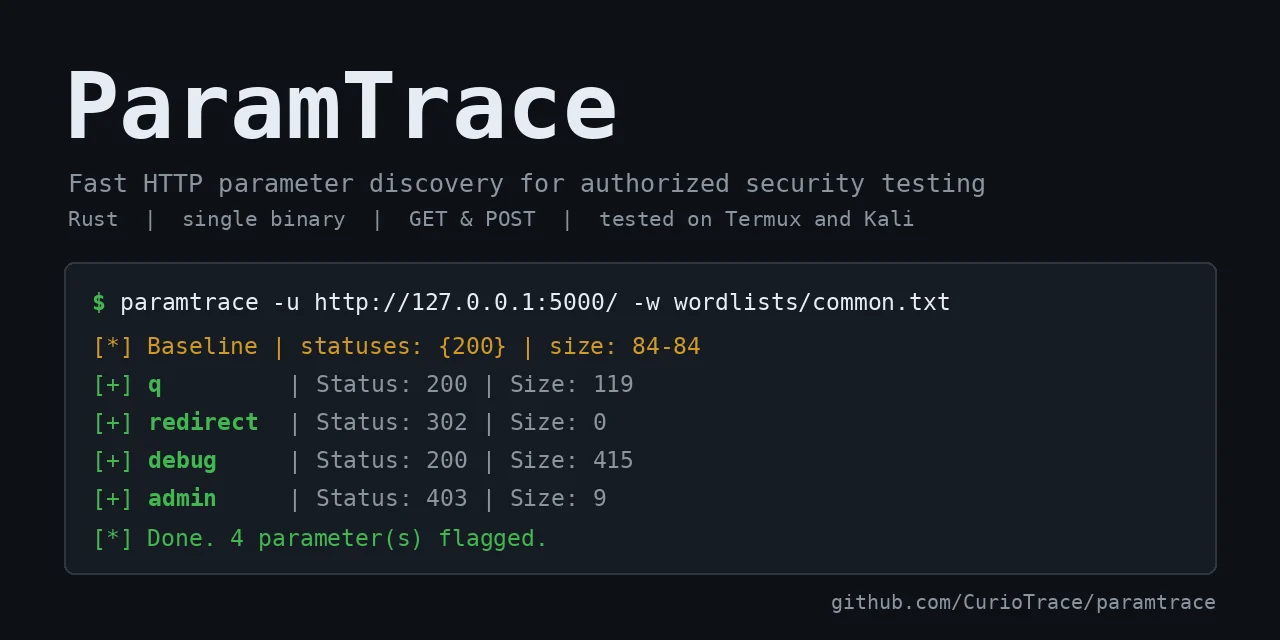 curiotrace/paramtrace
Fast HTTP parameter discovery for authorized security testing
 pennacle-security/summit
Open-source web security testing platform: proxy, scanner and fuzzer in one CLI. By Pennacle Security.
 affolter-engineering/xssearch
Rust-based XSS scanner with context-aware payload selection, WAF detection and bypass, crawling, blind XSS callbacks, and static DOM sink analysis.
 m14r41/scan4secrets
Find credentials and secret with 170+ rules covering across source code, Web URL, and CI/CD, verifies them against vendor APIs, and generates SARIF,…
 sleepingbag945/dddd
Batch asset collection and vulnerability scanning tool for red teams. Pulls targets from Hunter, Fofa, and Quake, performs fingerprinting, subdomain…
 watchtowrlabs/watchtowr-vs-atlassian-cve-2026-21589
Python detection artifact that checks Atlassian Jira, Confluence, and Bitbucket instances for the CVE-2026-21589 arbitrary file read vulnerability.